

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
11.1k
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 jaeles-project/jaeles-signatures
Default signature for Jaeles Scanner
 cckuailong/pocsploit
a lightweight, flexible and novel open source poc verification framework
 off-by-1-labs/flawed
Fix-Like Artifacts With Embedded Defects
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
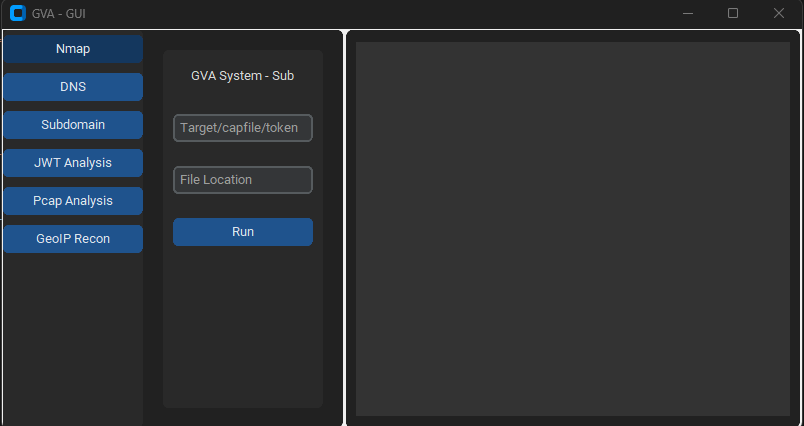 morpheuslord/gpt_vuln-analyzer
Uses ChatGPT API, Bard API, and Llama2, Python-Nmap, DNS Recon, PCAP and JWT recon modules and uses the GPT3 model to create vulnerability reports…
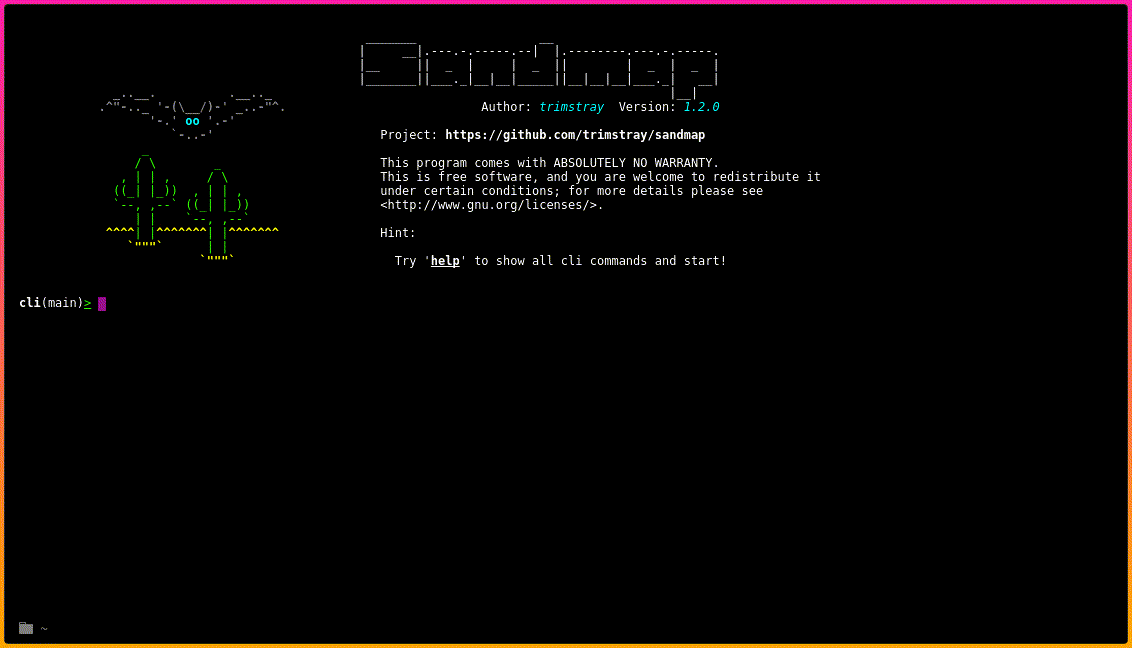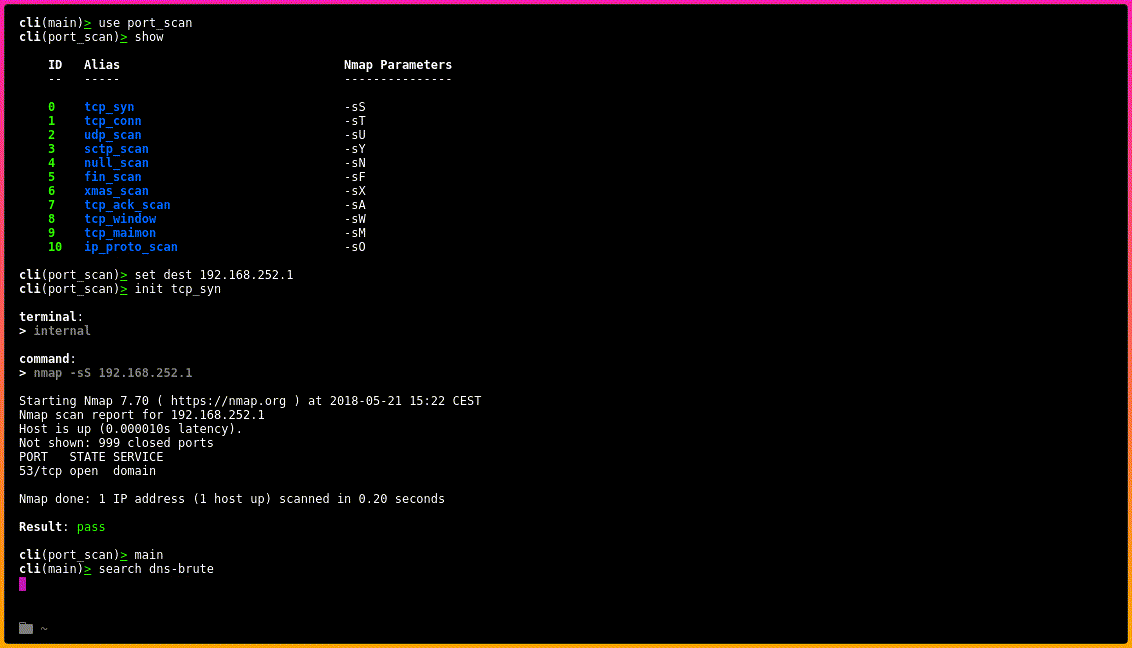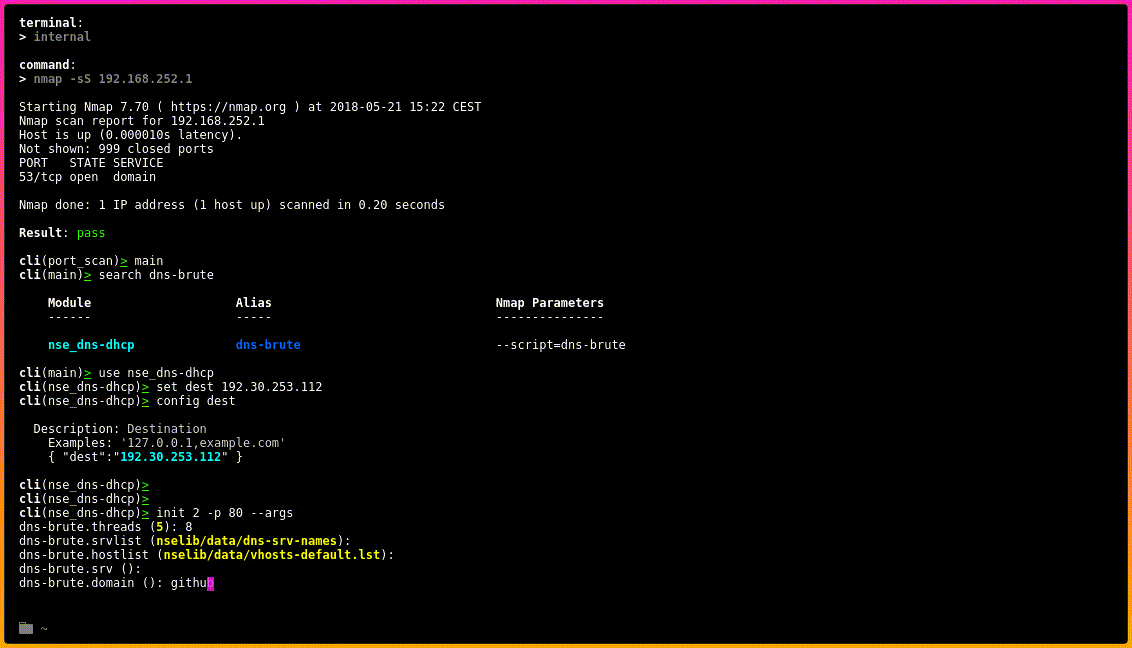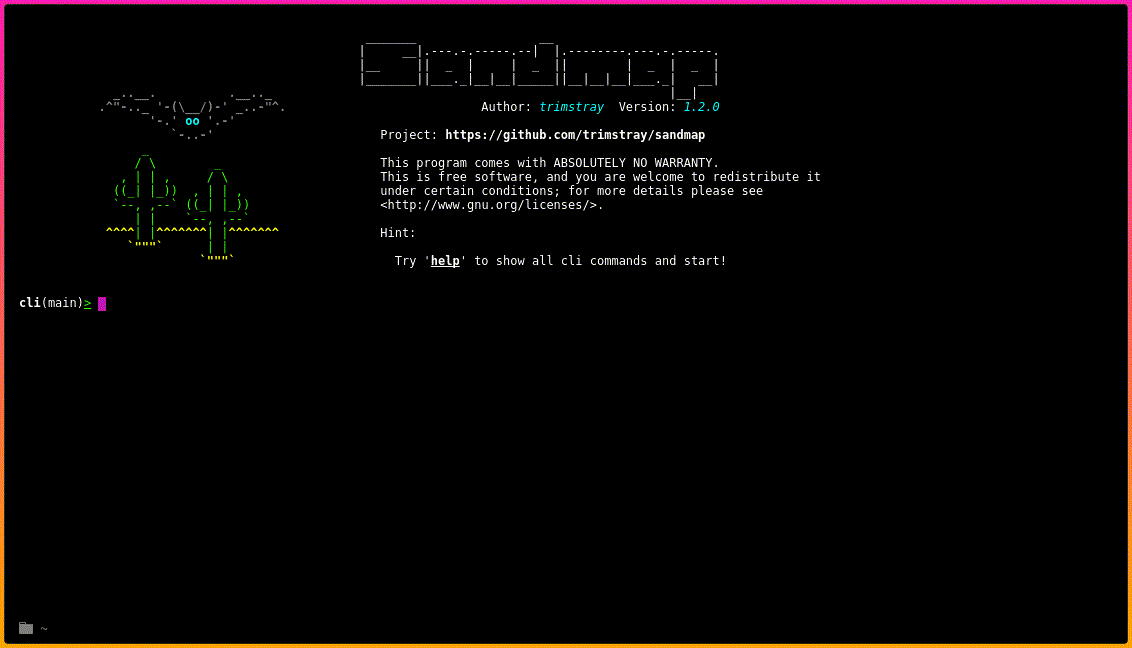 trimstray/sandmap
Nmap on steroids. Simple CLI with the ability to run pure Nmap engine, 31 modules with 459 scan profiles.
 mukul975/cve-mcp-server
Production-grade MCP server giving Claude 27 security intelligence tools across 21 APIs — CVE lookup, EPSS scoring, CISA KEV, MITRE ATT&CK, Shodan,…
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
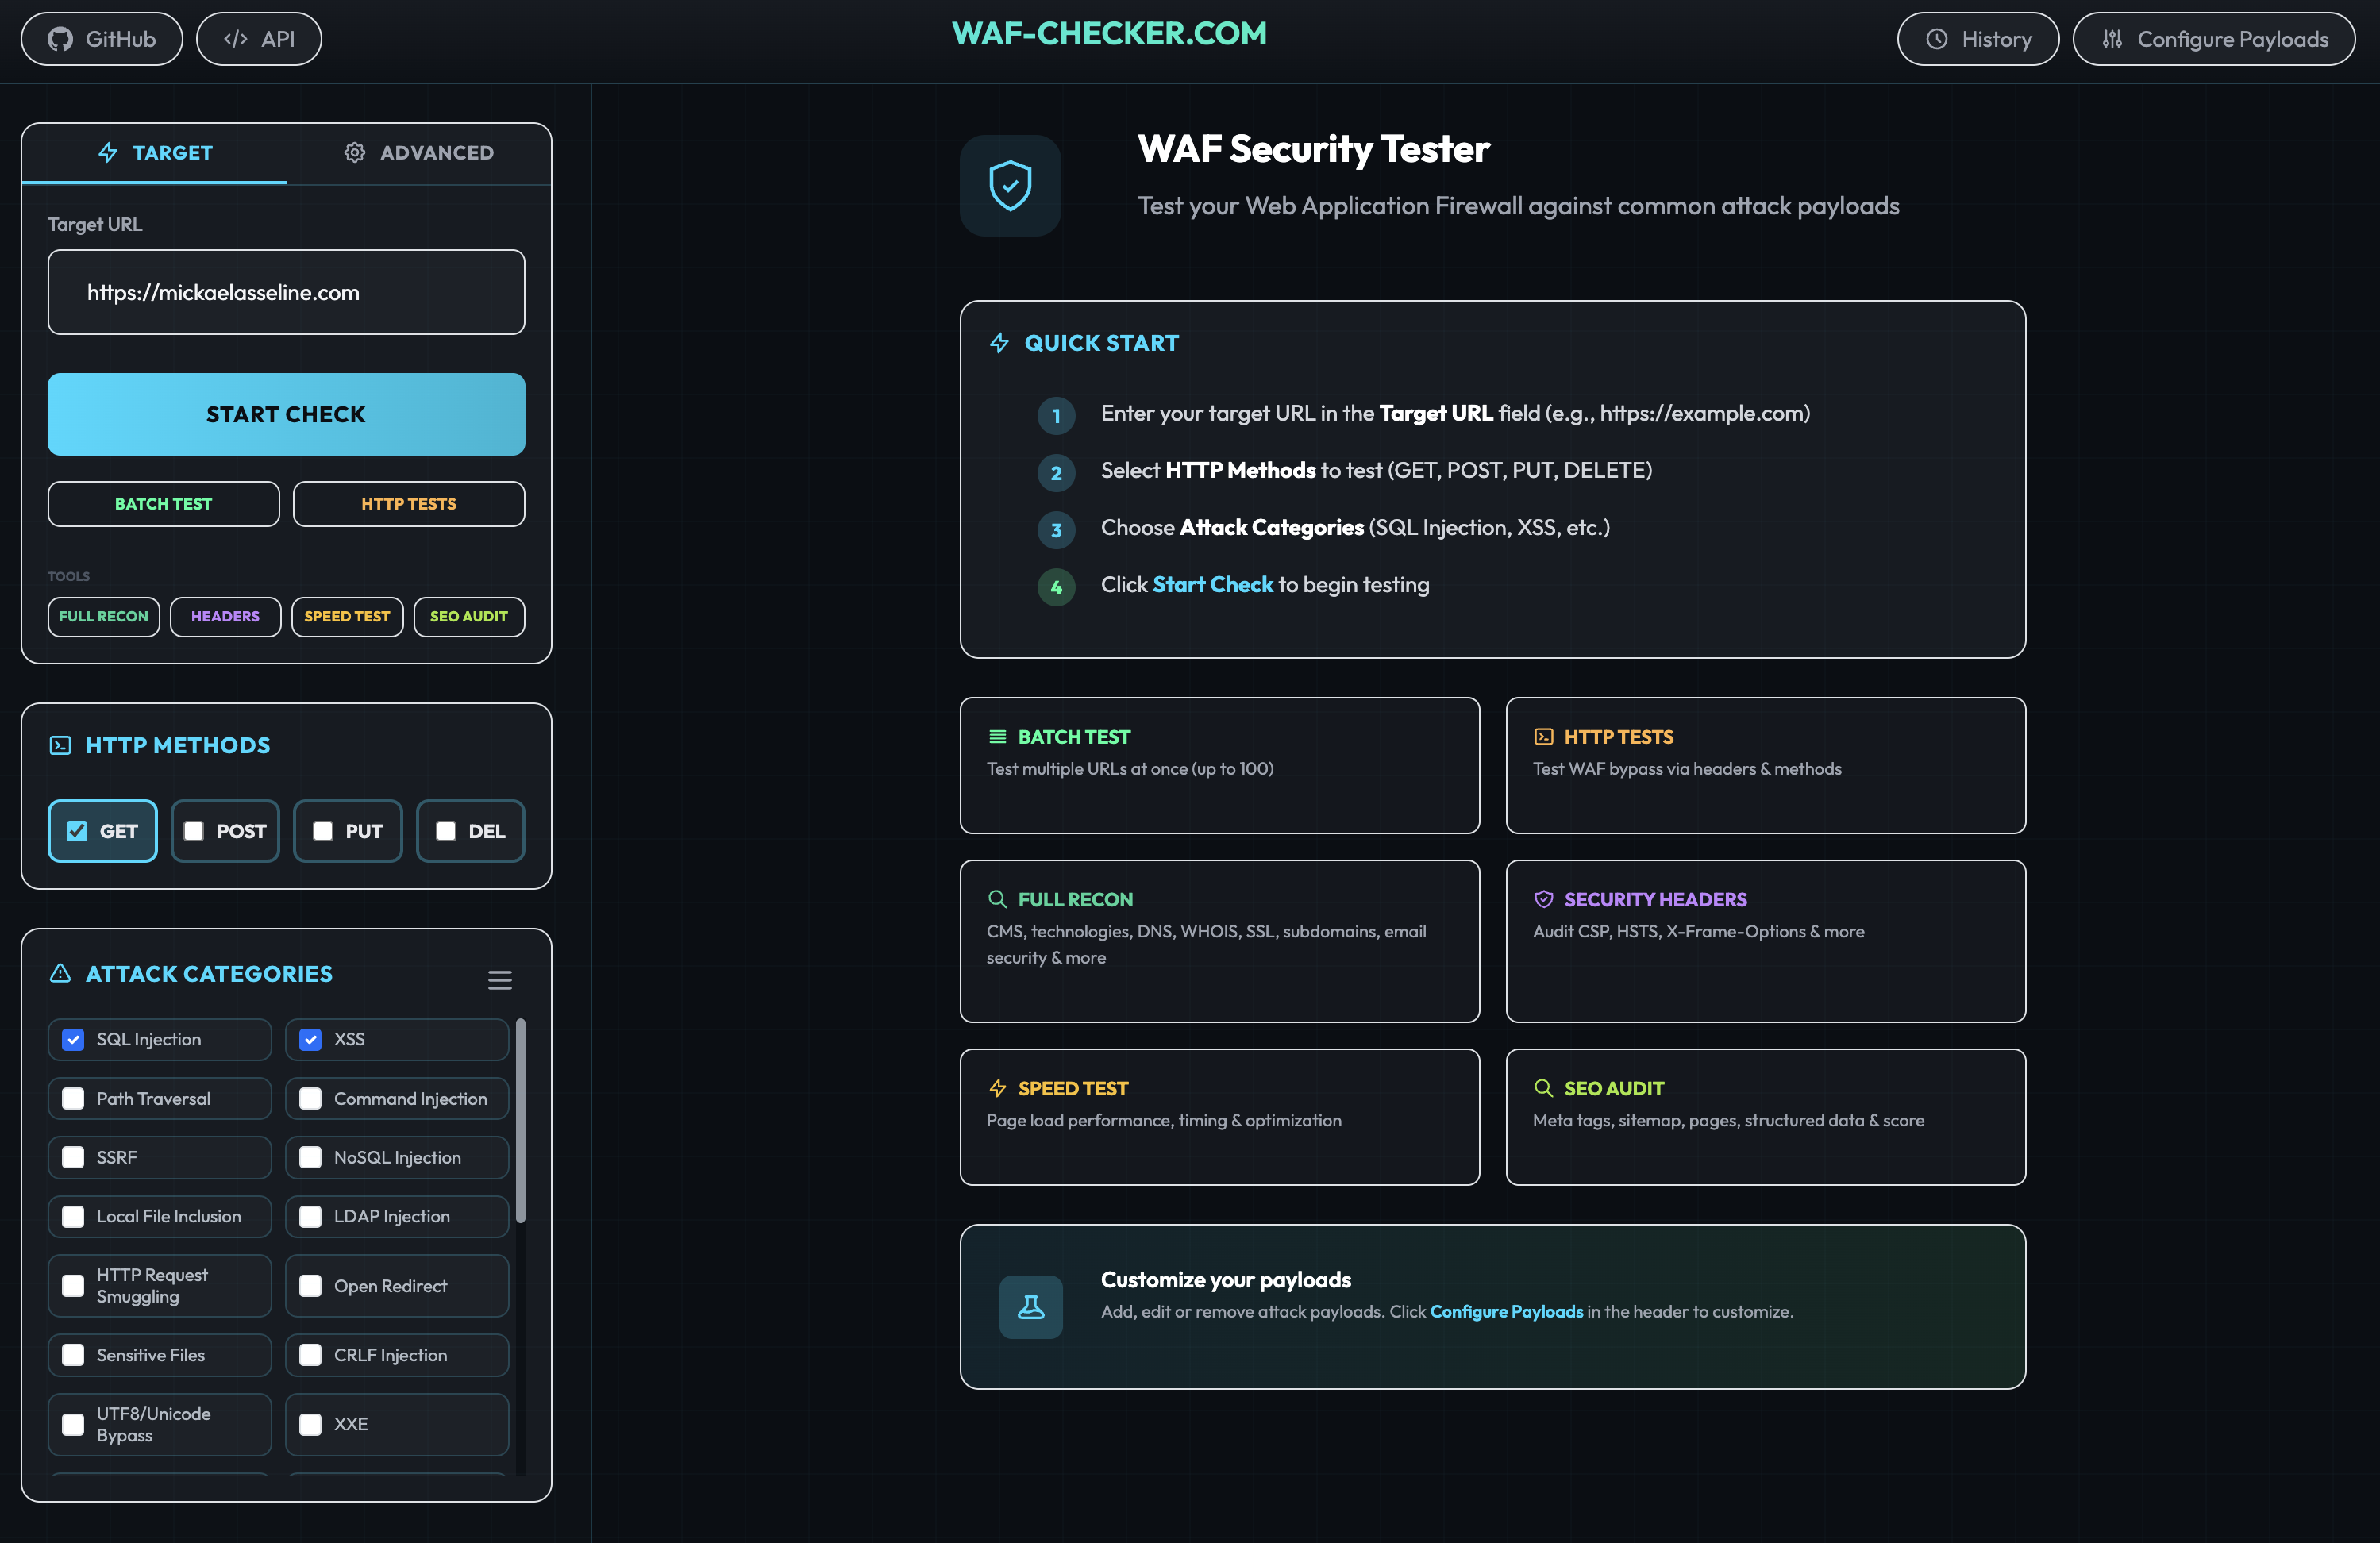 papamica/waf-checker
Tests your WAF with +160 payloads
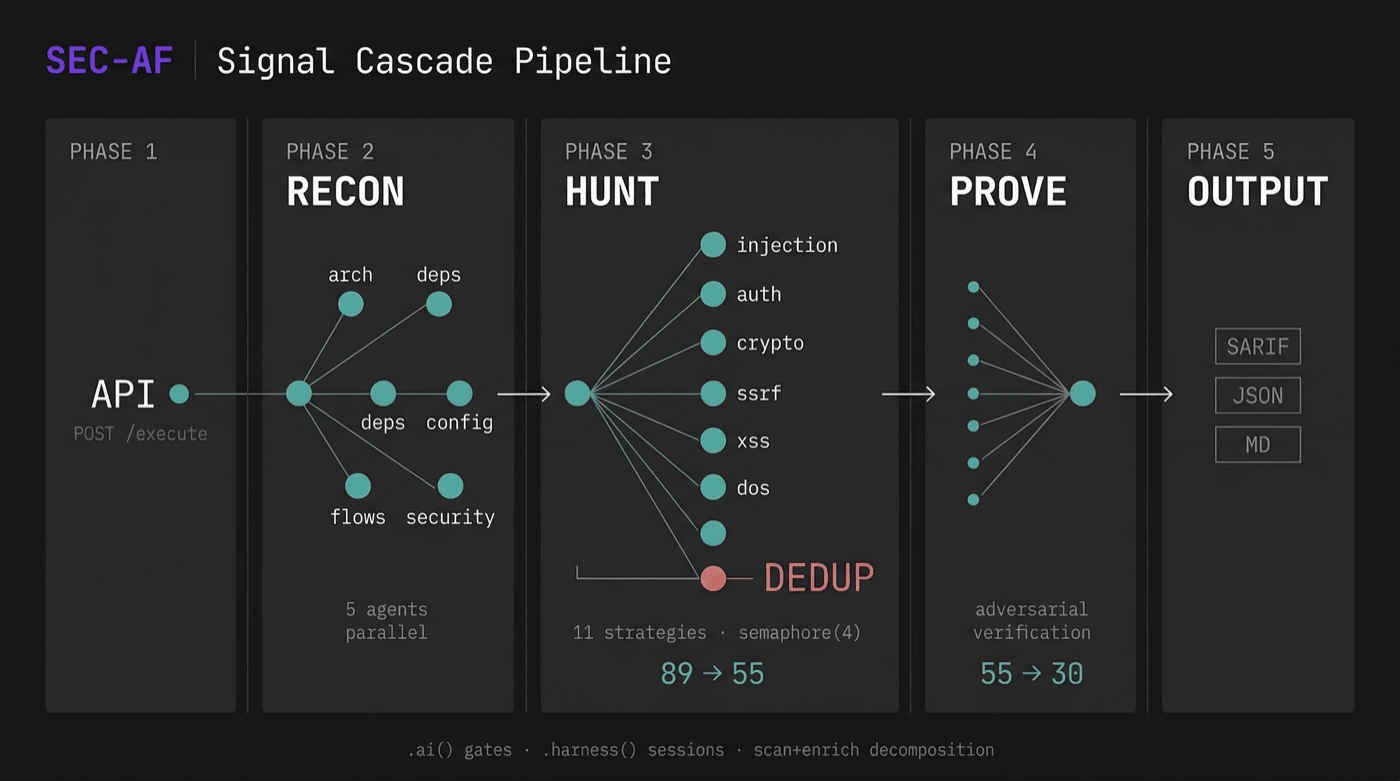 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 aron-tn/mega-bot
[NEW] : Mega Bot ☣ Scanner & Auto Exploiter
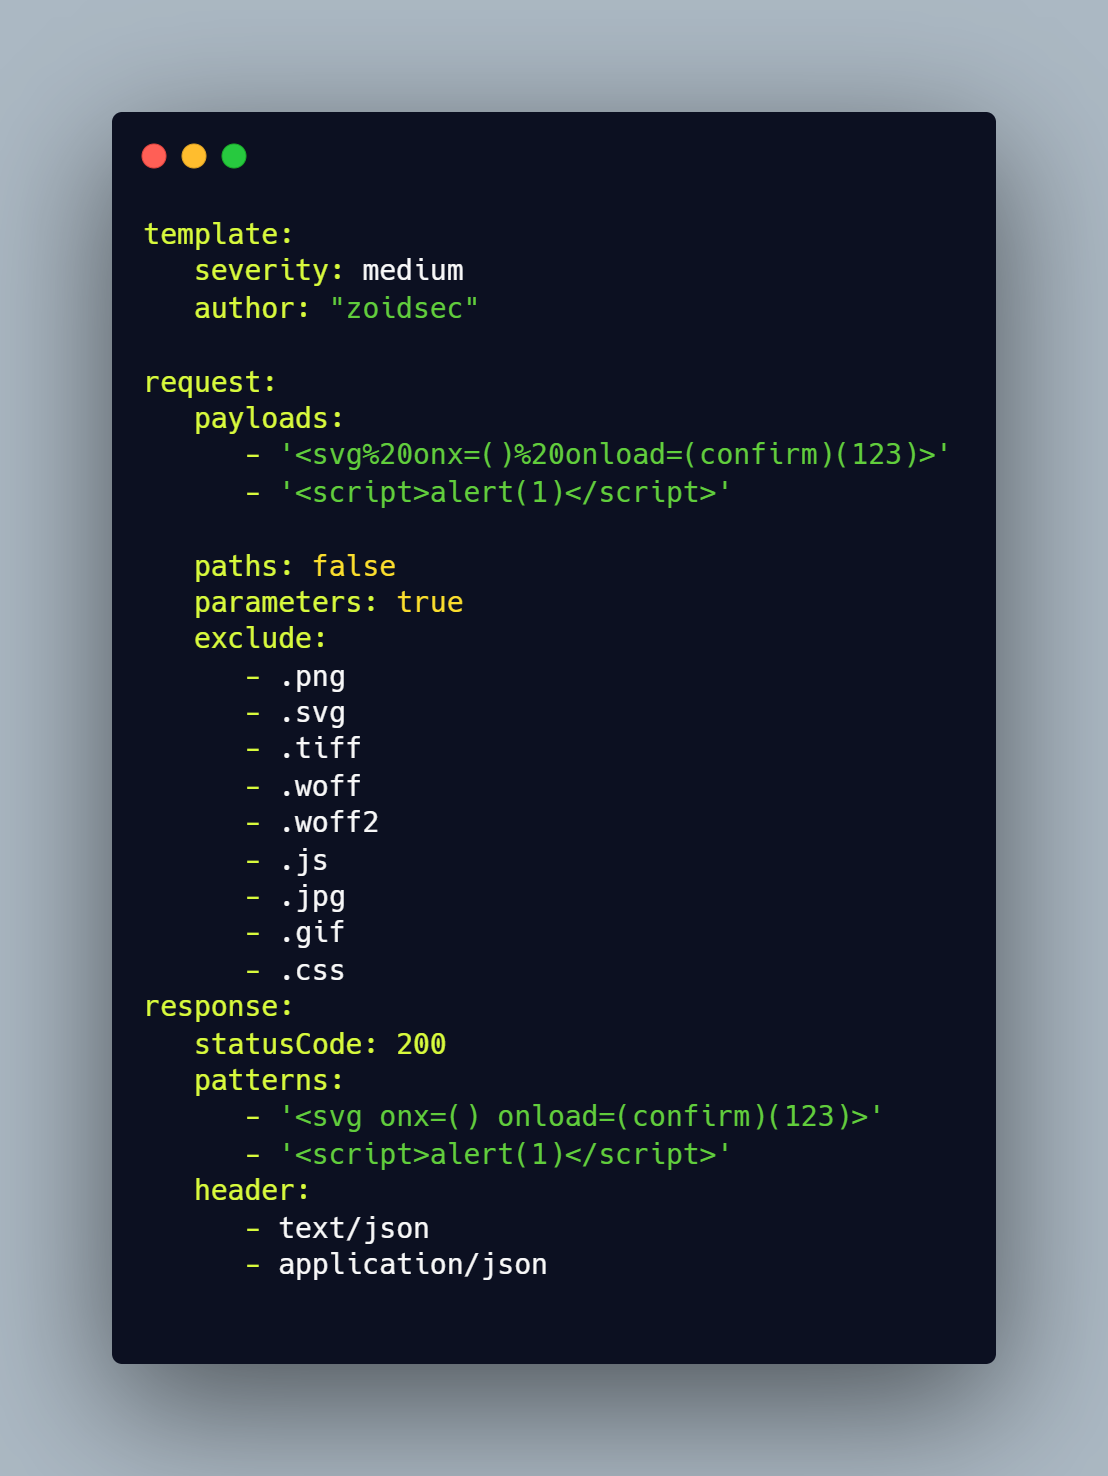 ethicalhackingplayground/erebus
Erebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.
 varchashva/vprioritizer
vPrioritizer enables us to understand the contextualized risk (vPRisk) on asset-vulnerability relationship level across the organization, for teams…
 dmonst3r/wordpressmassexploiter
[discontinued] Mass exploiter of CVE-2015-1579 for WordPress CMS
 gitlab-da/tutorials/security-and-governance/custom-scanner-integration/fern-pattern-scanner
Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…
 boostedchaos/fleet-cve-scanner
An open-source, single-script CVE scanner for RMM-managed fleets. Pure PowerShell 7 — joins your RMM software inventory against NVD, CISA KEV, EPSS…