
TIWAP
 tombstoneghost/tiwap
Deliberately vulnerable Flask web application with 22 security flaws across 3 difficulty levels for hands-on penetration testing and web security…
educationlabs-practicepenetration-testing+2
178
tombstoneghost/tiwapDeliberately vulnerable Flask web application with 22 security flaws across 3 difficulty levels for hands-on penetration testing and web security…
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 cream-sec/cve-2019-0708-msf--
CVE-2019-0708-Msf-验证
 ron190/jsql-injection
Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…
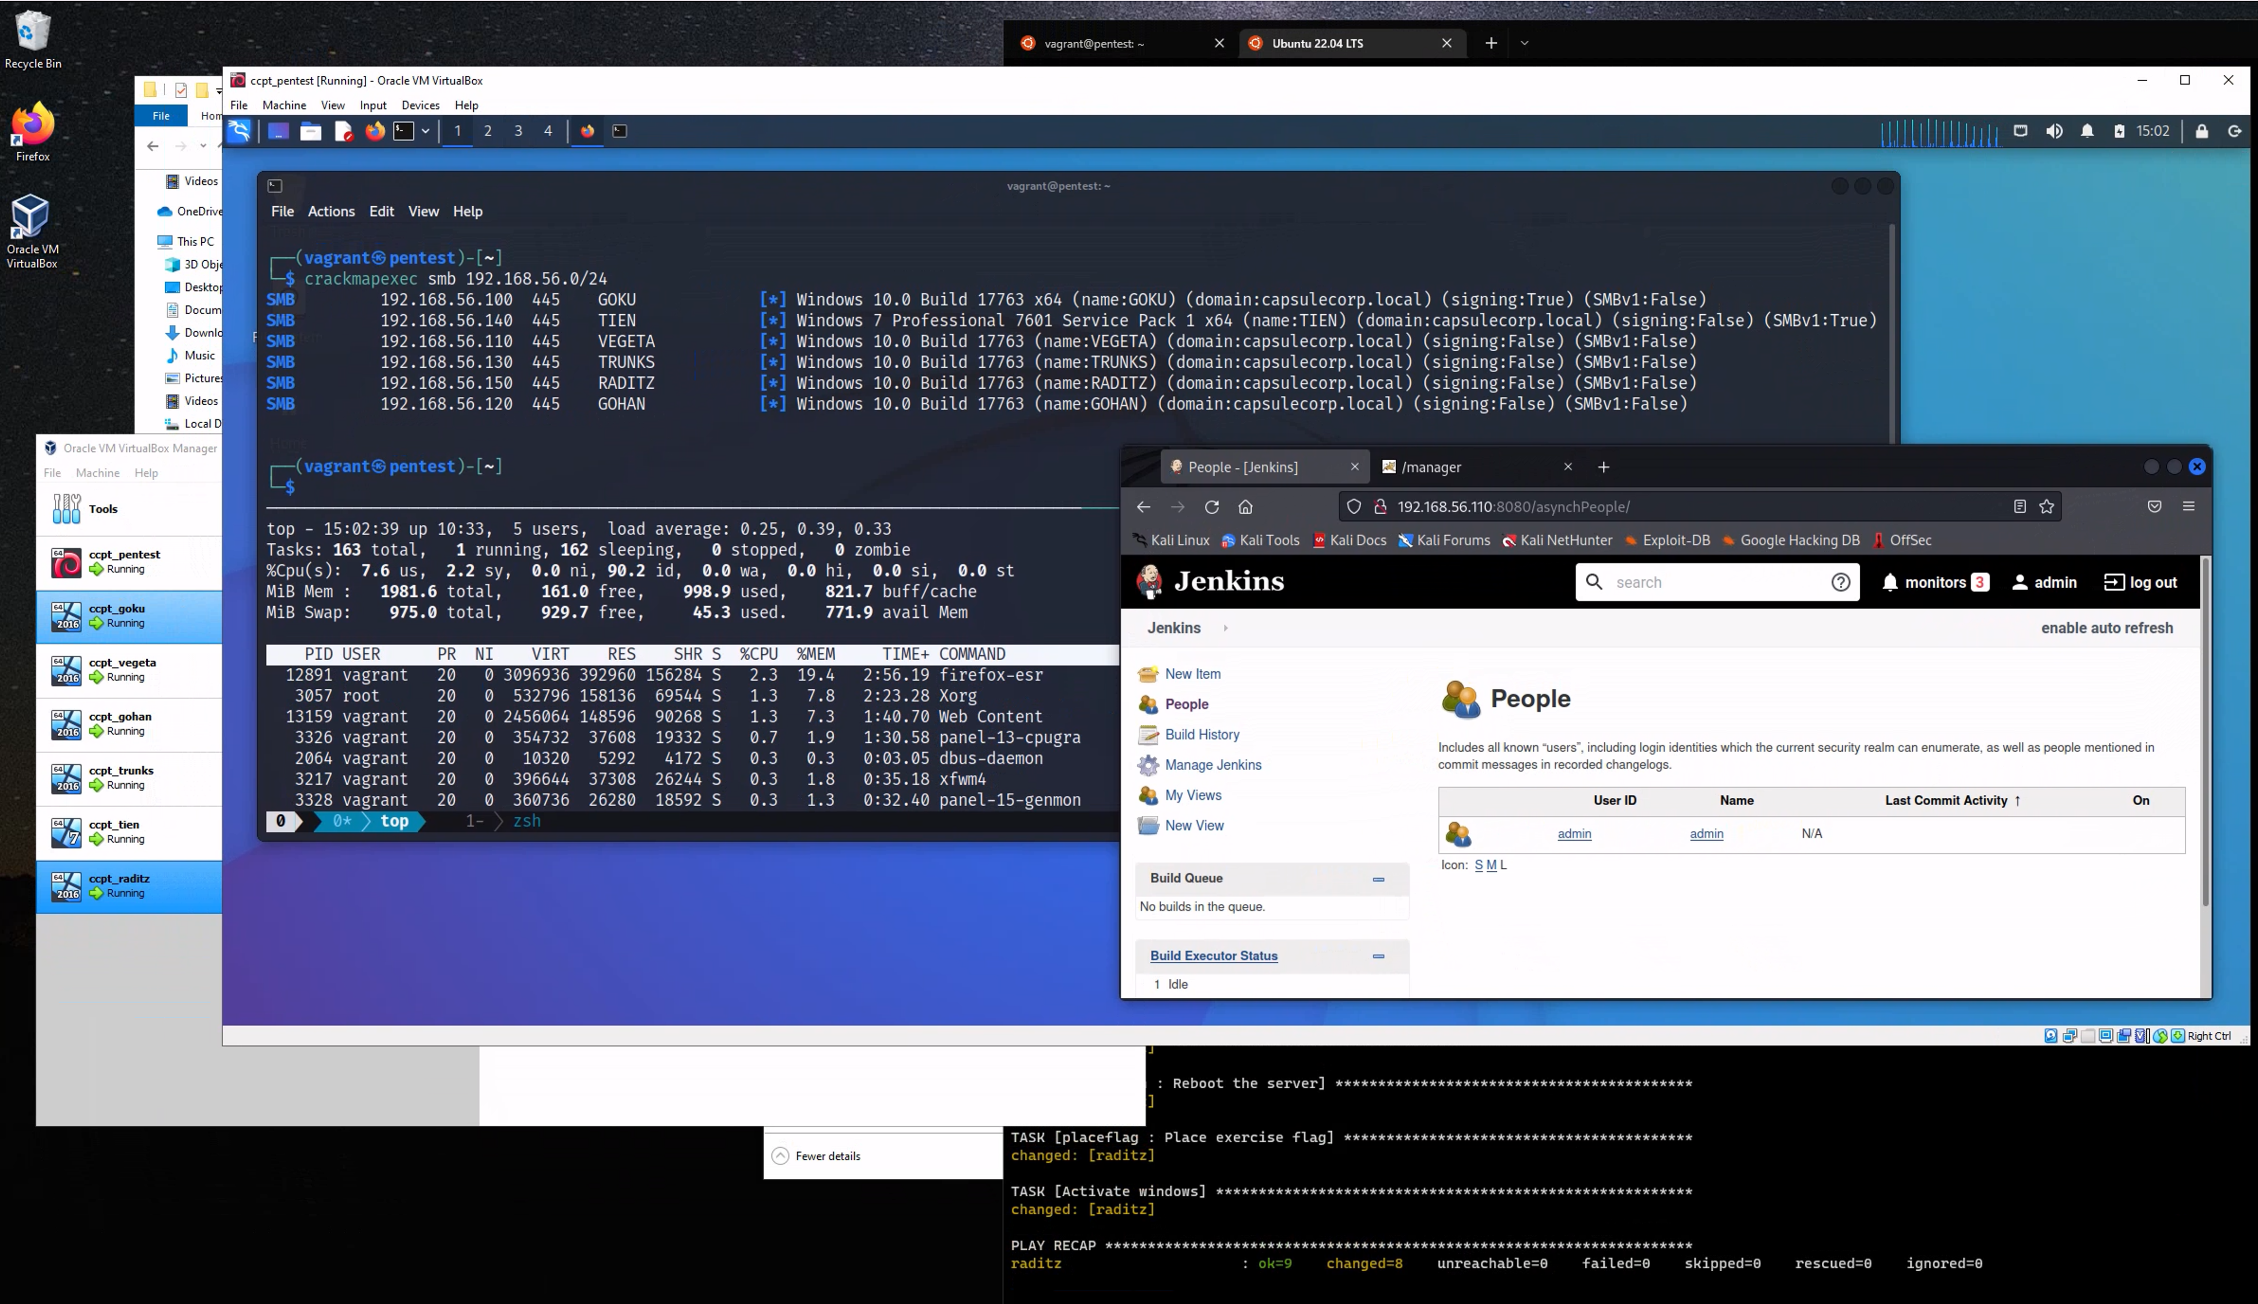 r3dy/capsulecorp-pentest
Vagrant VirtualBox environment for conducting an internal network penetration test
 webpwnized/mutillidae
OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
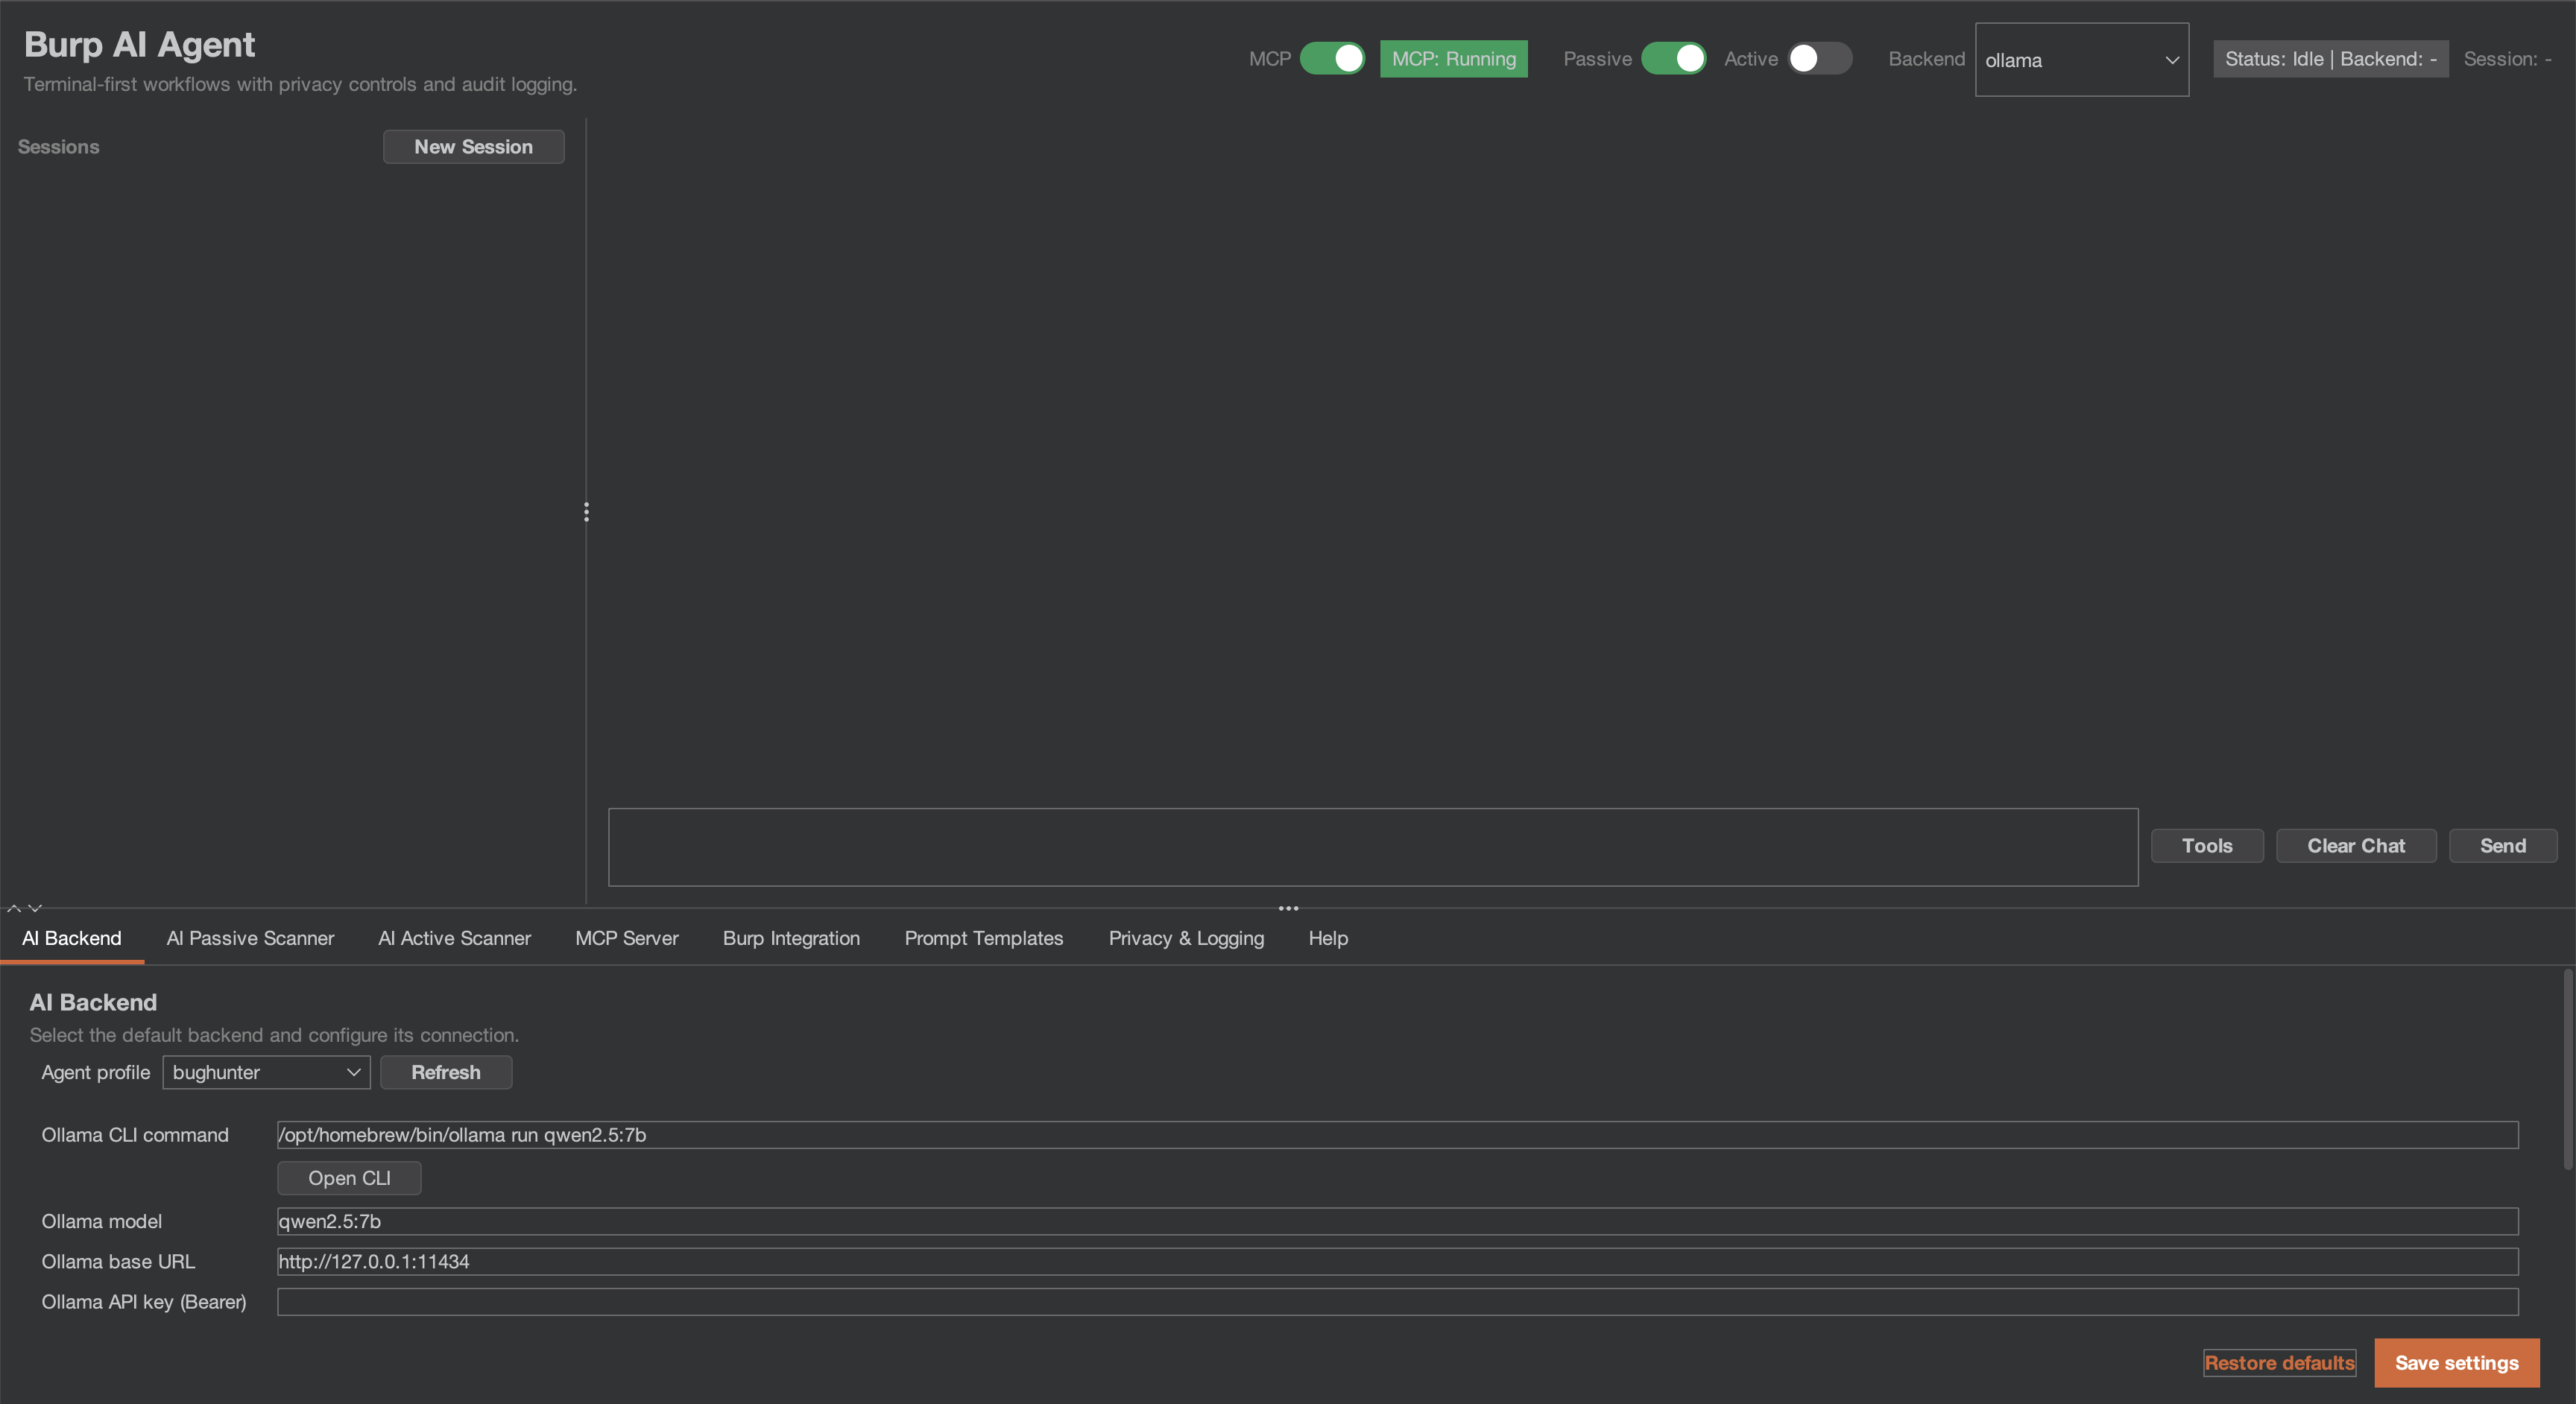 six2dez/burp-ai-agent
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
 owtf/owtf
Modular penetration testing framework integrating multiple tools for automated web application security assessment, aligned with OWASP Testing Guide,…
 lefayjey/linwinpwn
Bash script wrapping Active Directory tools for automated enumeration, vulnerability checks, exploitation, and password dumping via LDAP, RPC,…
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
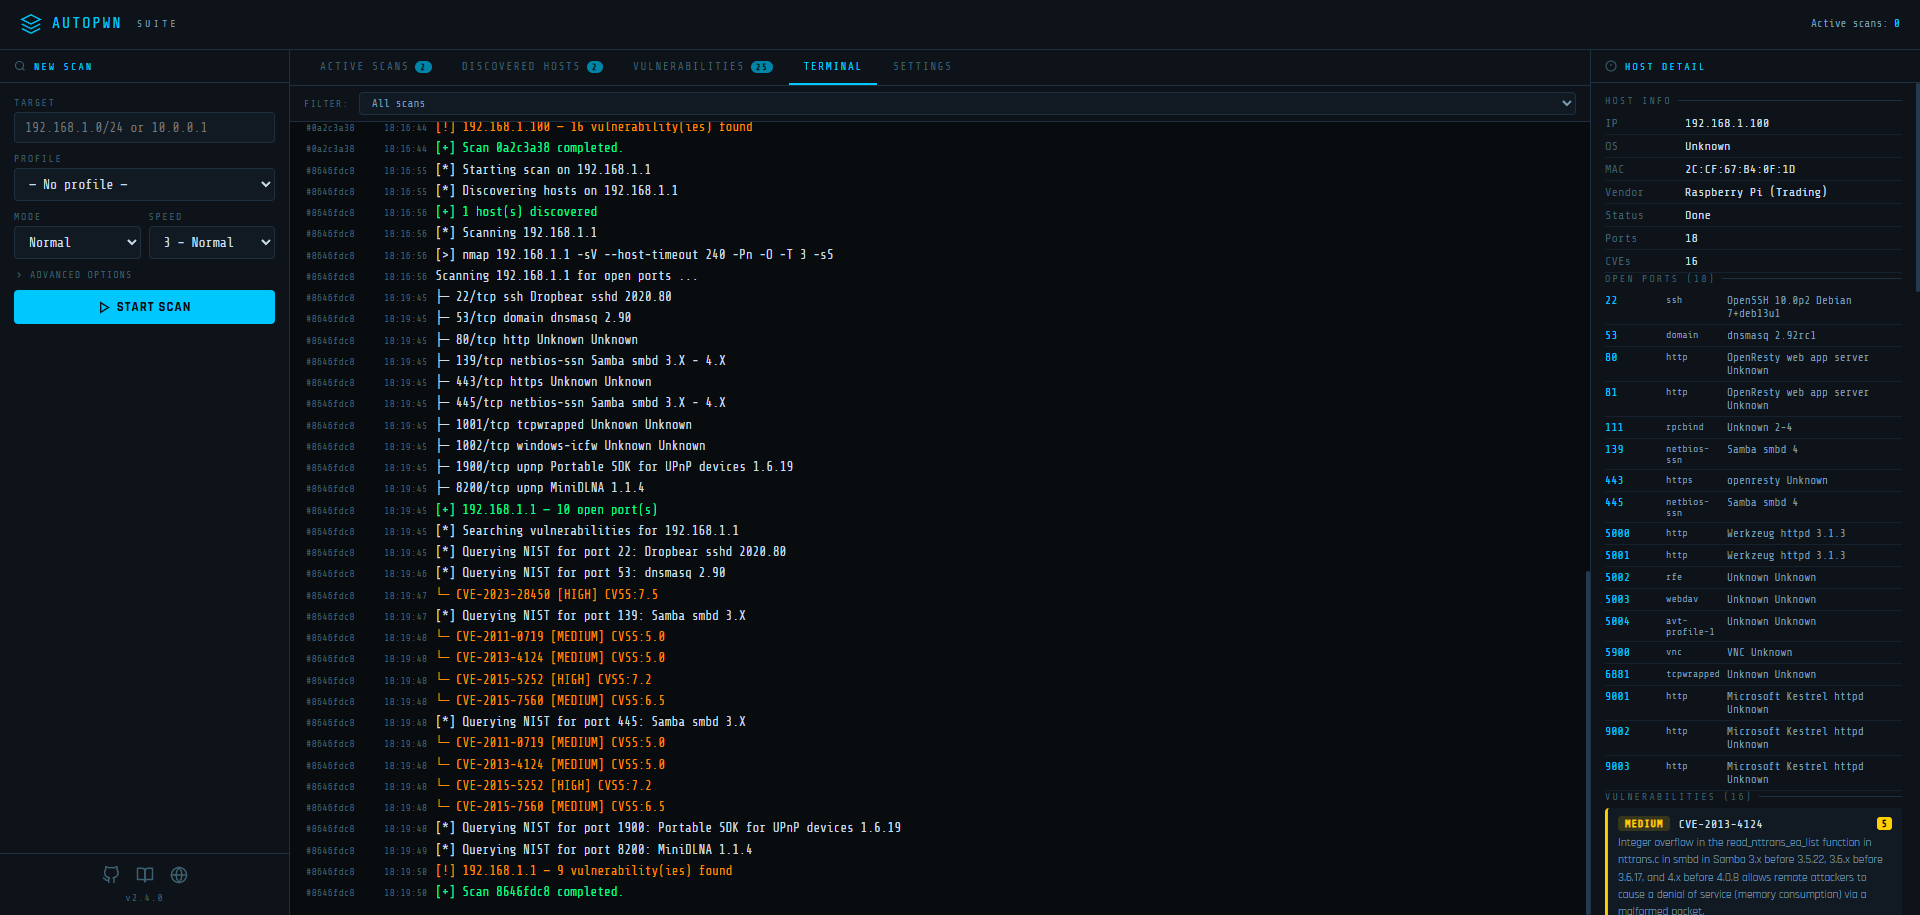 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 zeop-cybersec/apache_normalize_path
Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)
 spiritualmachines/buds-audit
No-dongle, no-root Bluetooth security assessment tool for wireless earbuds affected by the Airoha SDK vulnerability chain (CVE-2025-20700/20701/20702)
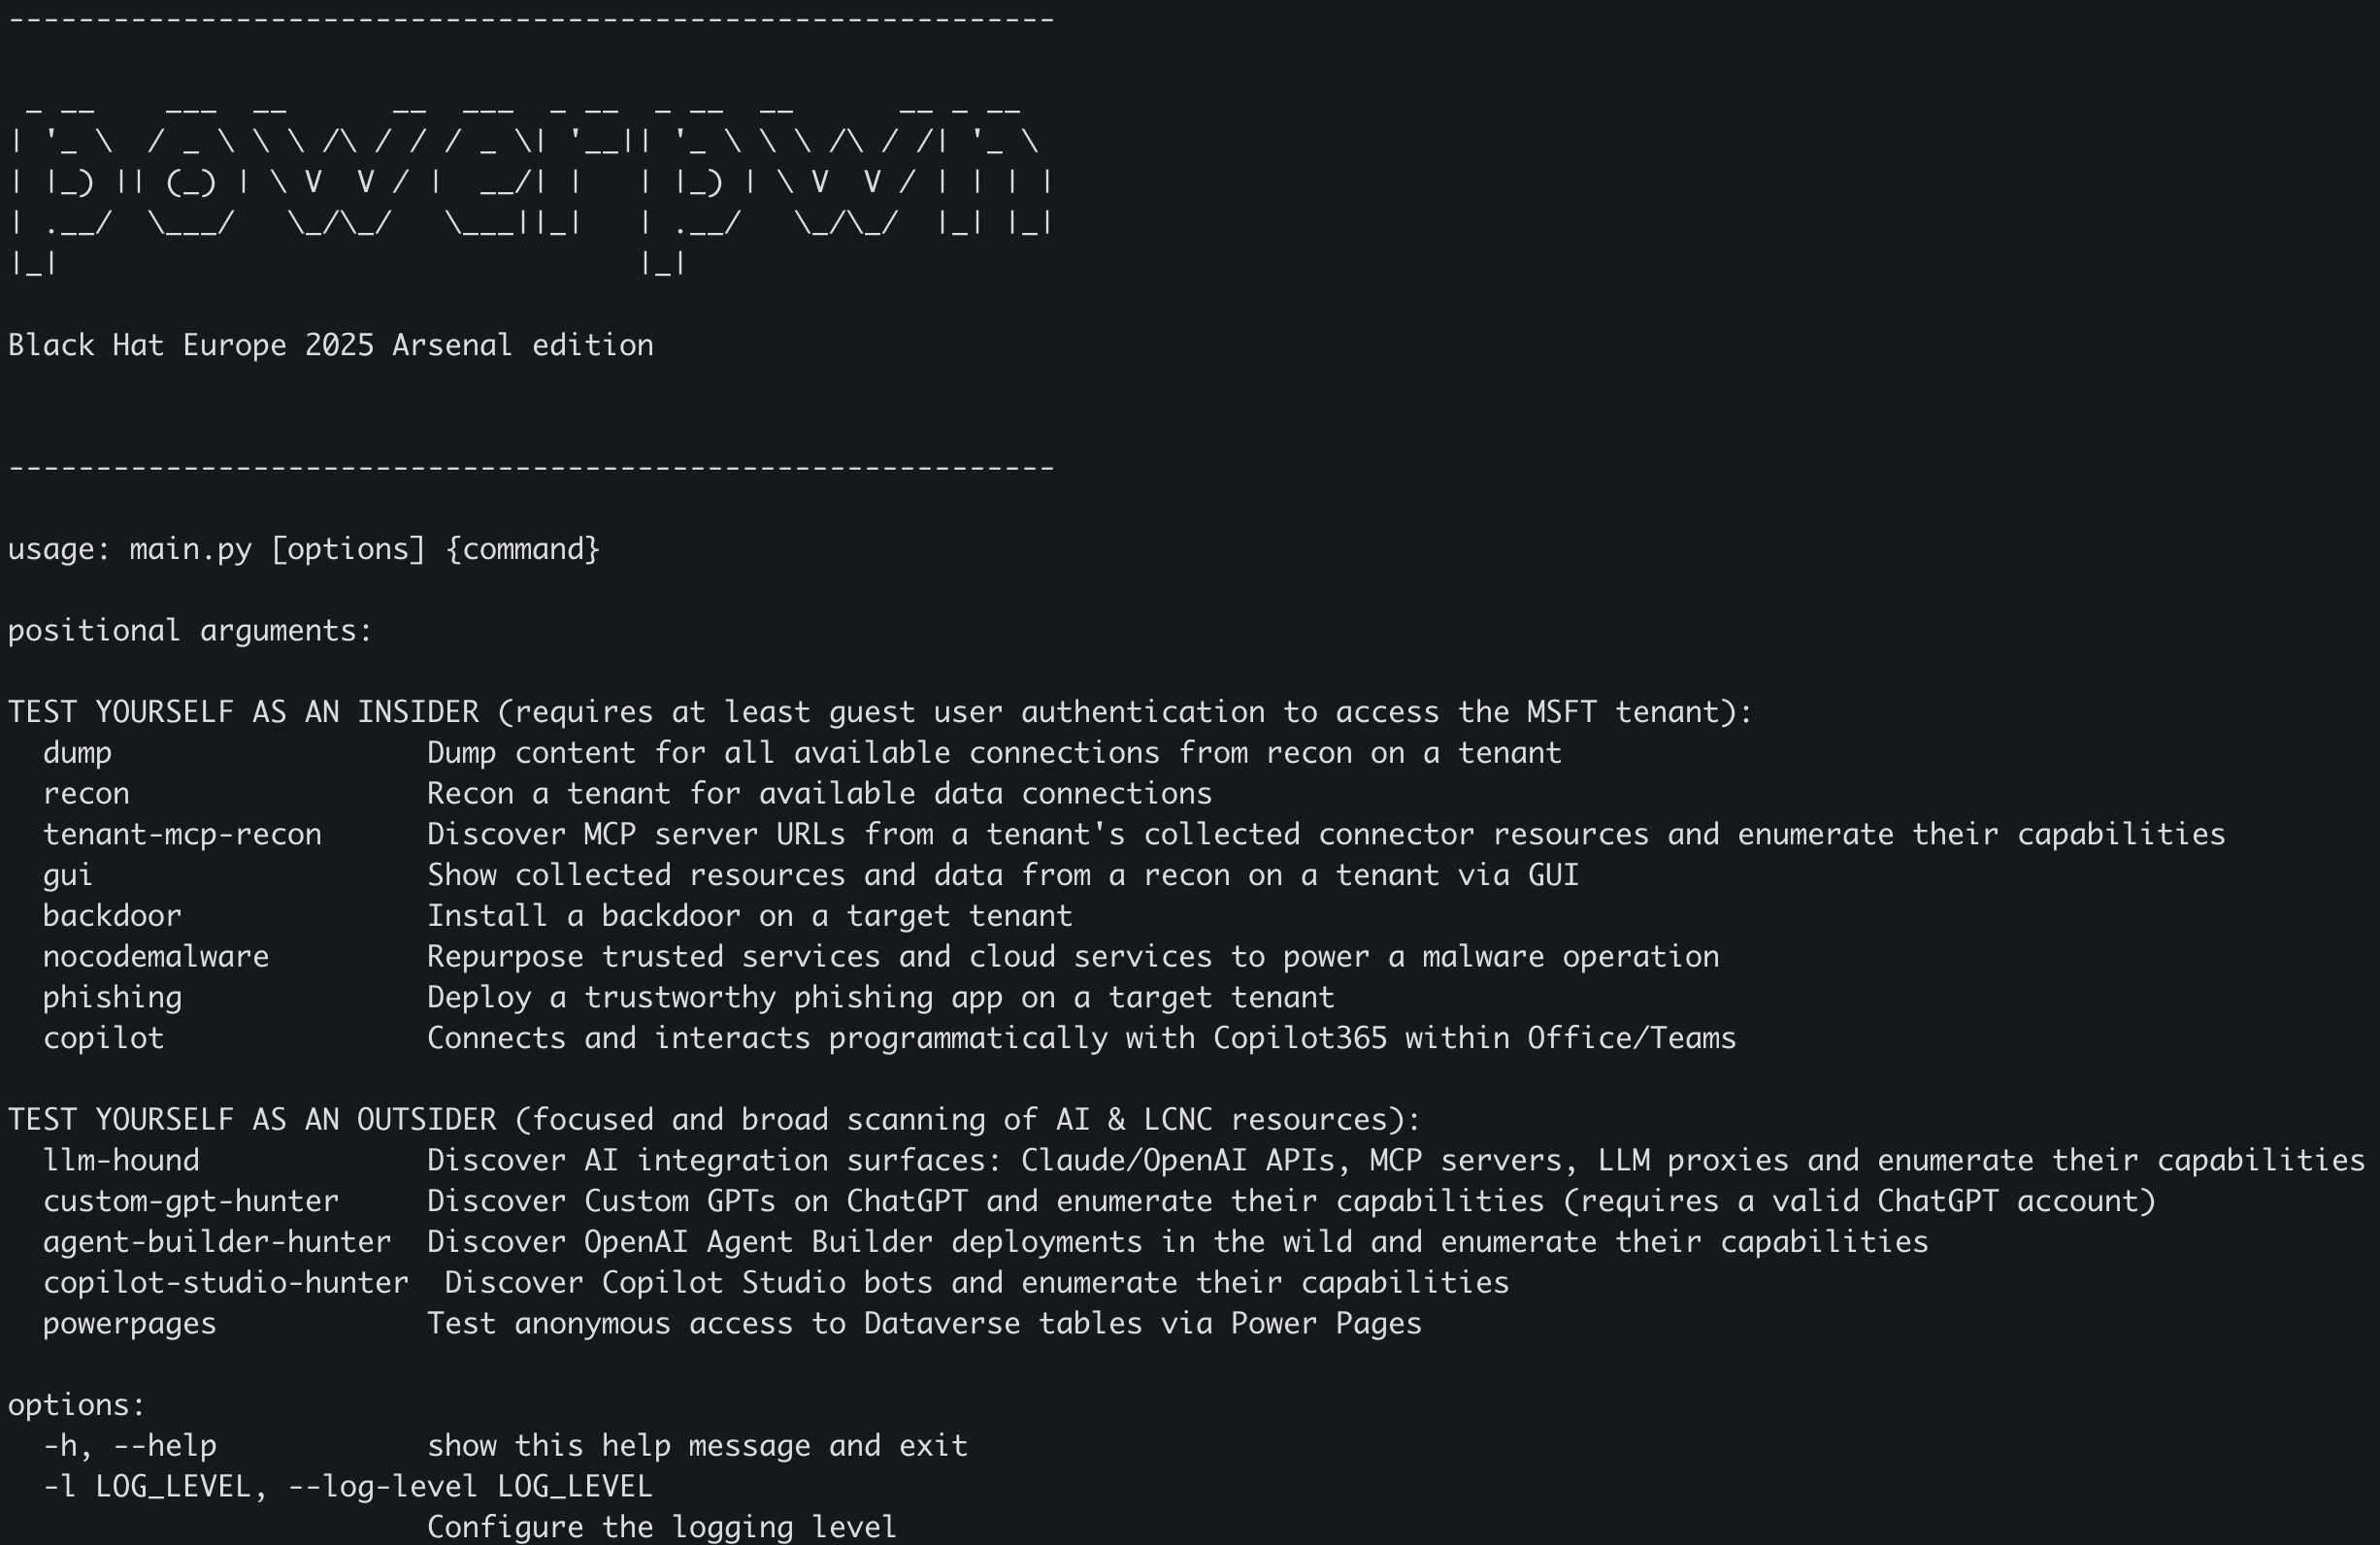 mbrg/power-pwn
An offensive/defense security toolset for discovery, recon and ethical assessment of AI Agents
 4shadoww/hakkuframework
Hakku Framework penetration testing
 machine1337/hackguard
FAST WEB APPLICATION VULNERABILITY SCANNER written in python3
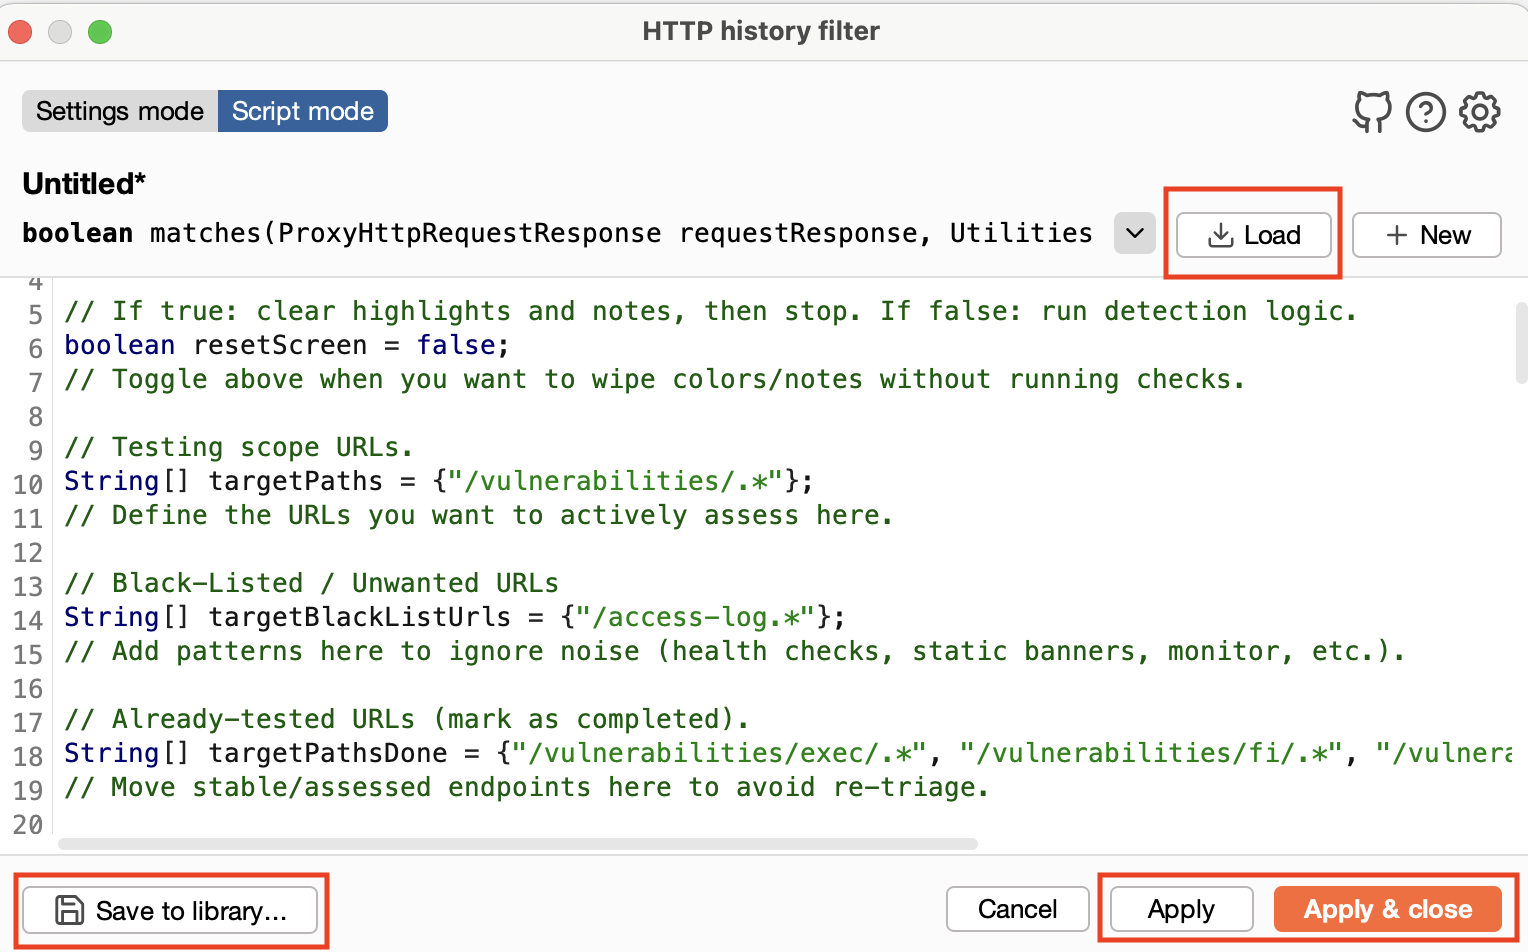 volkandindar/agartha
A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…