
CVE-2025-29824-Exploit
 afanpan/cve-2025-29824-exploit
Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.
binary-exploitationexploitationmalware-analysis+6
20
afanpan/cve-2025-29824-exploitUse after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
 justjeff211/conti-ransomware-writeup
Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…
 ionescu007/specucheck
Windows utility that queries kernel API to report software and hardware mitigation status against speculative execution vulnerabilities (Meltdown,…
 wiredpulse/invoke-hivenightmare
PoC for CVE-2021-36934, which enables a standard user to be able to retrieve the SAM, Security, and Software Registry hives in Windows 10 version…
 fortra/cve-2022-37969
Proof-of-concept exploit for CVE-2022-37969, a Windows Common Log File System driver local privilege escalation. Demonstrates heap spray, token…
 fortra/cve-2023-28252
Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…
 chandru-gunasekaran/log4j-fix-cve-2021-44228
Windows Batch Scrip to Fix the log4j-issue-CVE-2021-44228
 byt3n33dl3/clfs
it's a CVE-2023-28252 (Patched), but feel free to use it for check any outdated software or reseach
 mkultra6969/anysniff
AnySniff is a tool for monitoring TCP connections of processes like AnyDesk on Windows. It uses the CVE-2024-52940 vulnerability to track open…
 byt3n33dl3/crackkeyiso
it's a CVE-2023-28229 (Patched), but feel free to use it for check any outdated software or reseach
 mein-0/kaspermeow
Proof-of-concept that exploits a Kaspersky driver vulnerability to leak kernel pointers and bypass KASLR on Windows, enabling kernel exploit chain…
 boostedchaos/fleet-cve-scanner
An open-source, single-script CVE scanner for RMM-managed fleets. Pure PowerShell 7 — joins your RMM software inventory against NVD, CISA KEV, EPSS…
 dafthack/mfasweep
A tool for checking if MFA is enabled on multiple Microsoft Services
 technicaldada/hack-winrar
WinRar is a very widely known software for windows. Previous version of WinRaR was a vulnerability which has been patched in Feb-2019. Most of the…
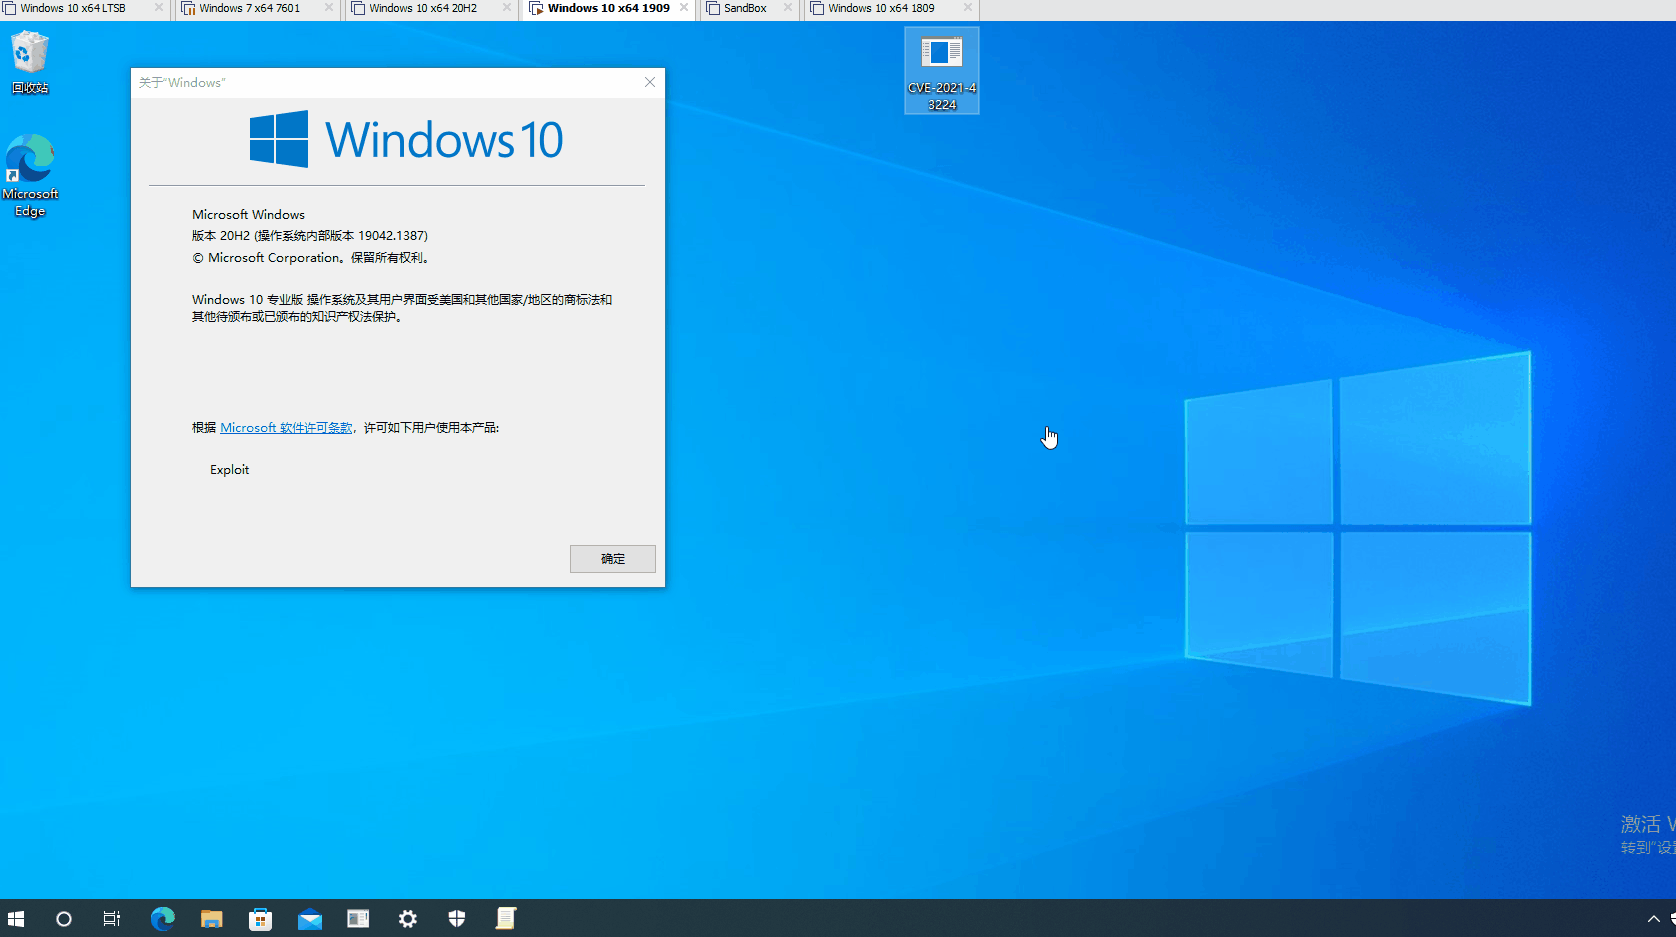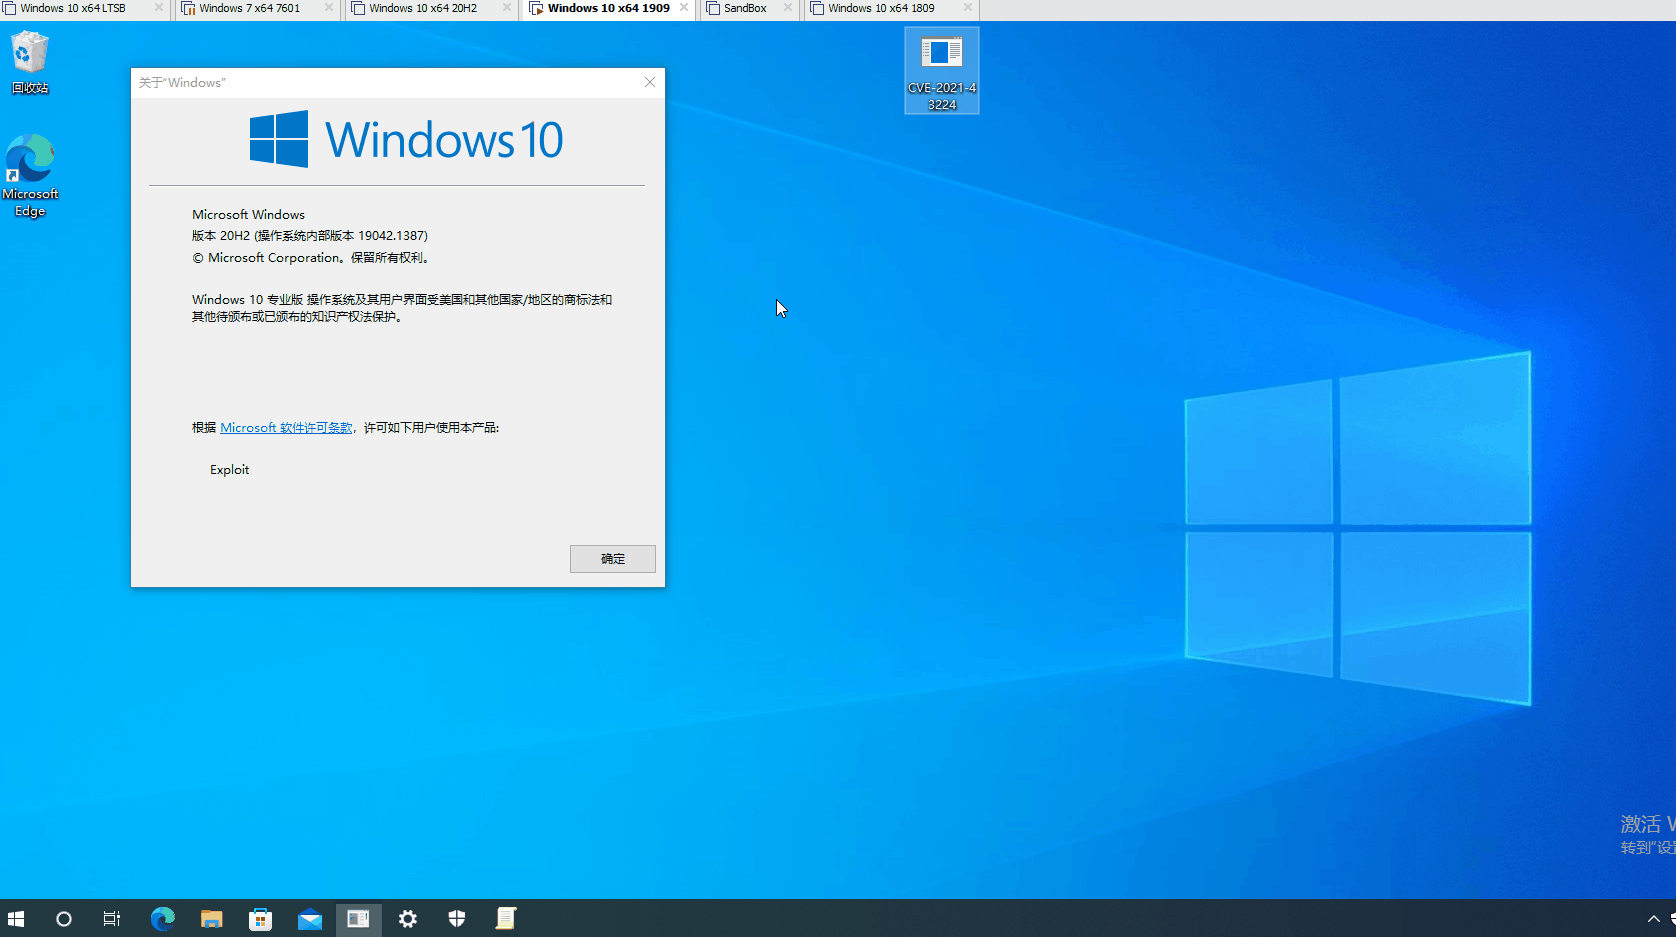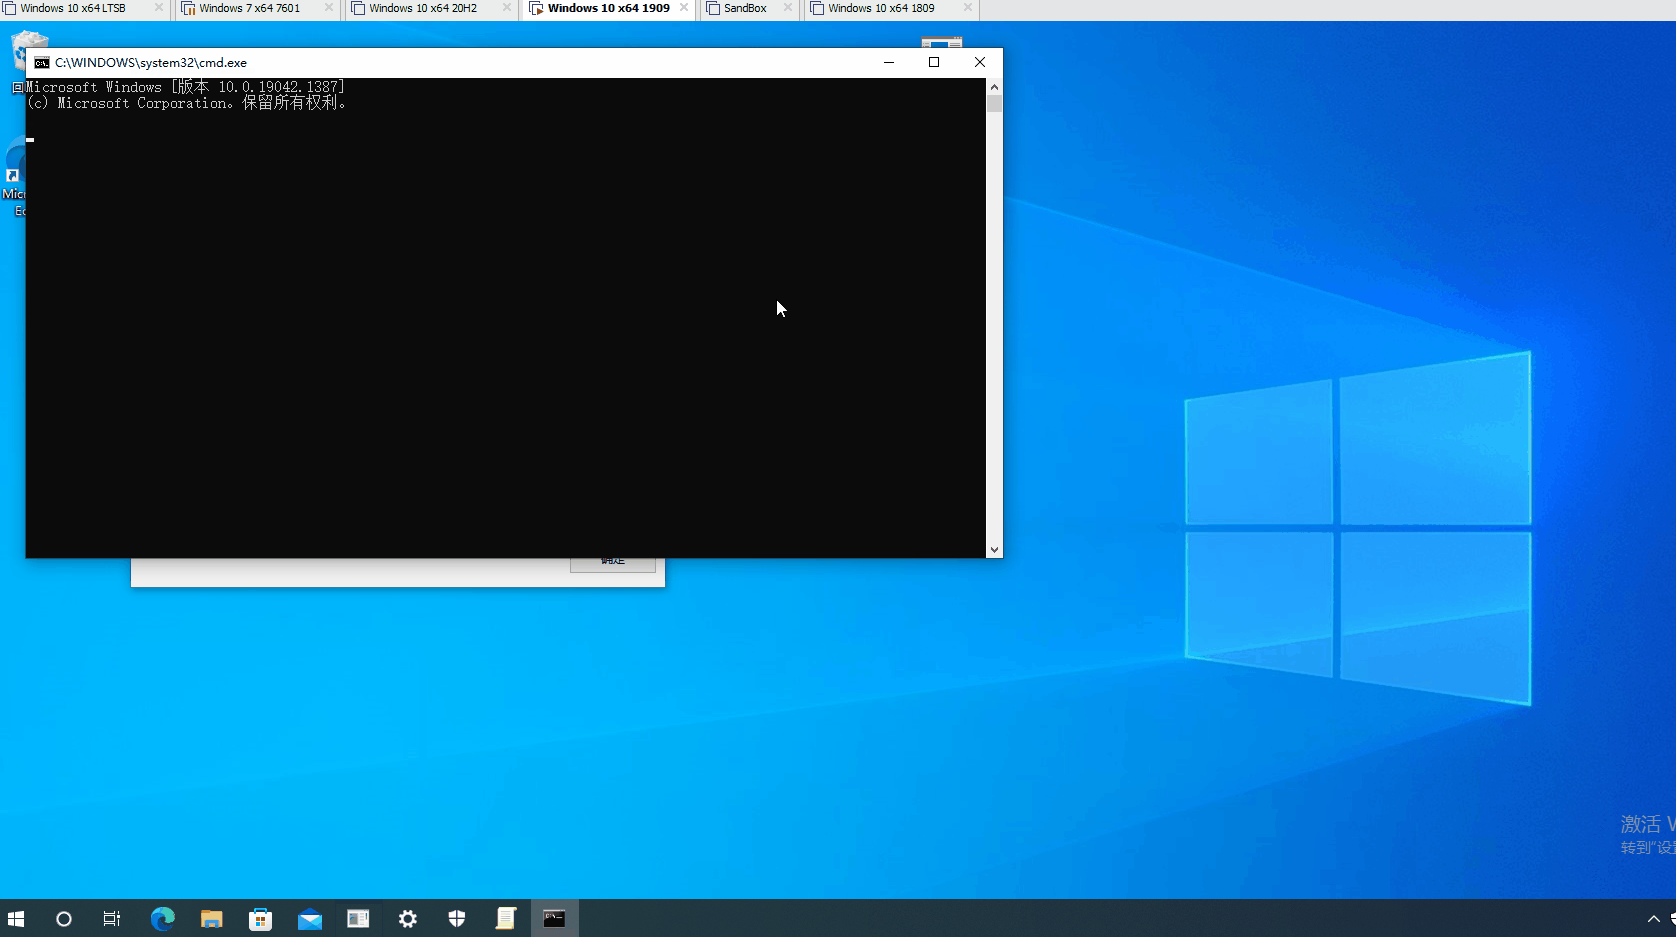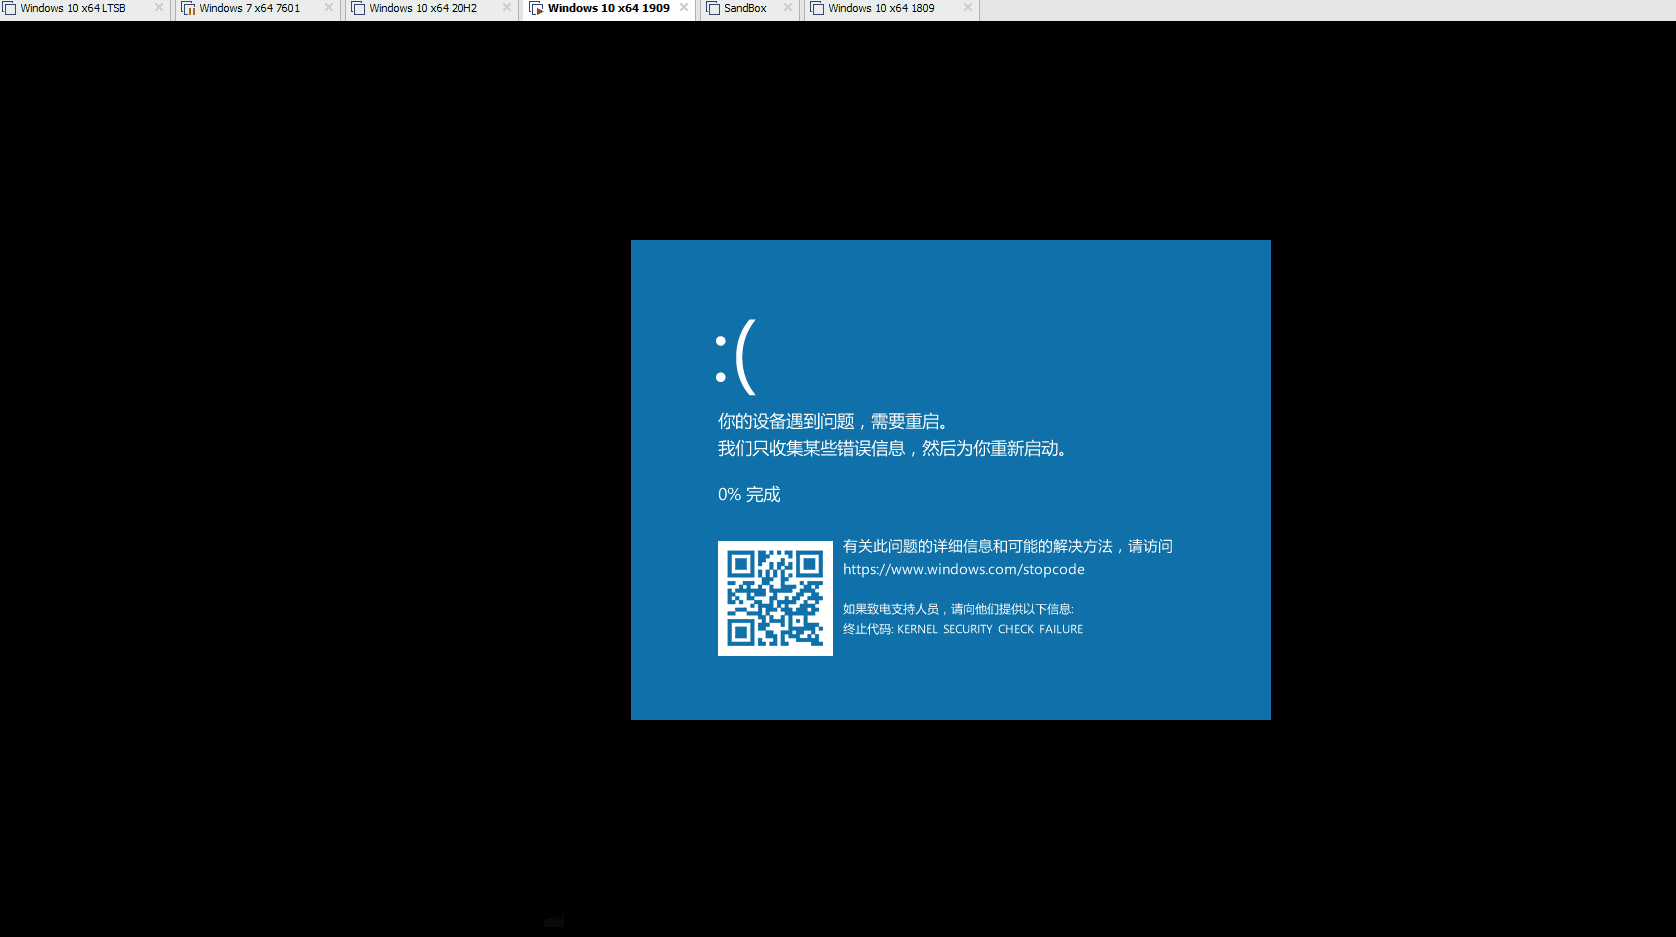 kalendsi/cve-2021-43224-poc
Windows Common Log File System Driver POC
 zmkeh/cve-2025-29824-clfs-local-privilege-escalation
Local privilege escalation exploit for CVE-2025-29824 targeting the Windows Common Log File System (CLFS) driver, providing proof-of-concept code for…
 kairo-one/cve-2023-26469-jorani
Proof-of-concept exploit for CVE-2023-26469 targeting Jorani 1.0.0. Combines path traversal and log injection to achieve remote code execution with…