
CVE-2025-5548
 raulsineiro/cve-2025-5548
Binary exploitation laboratory: Environment setup and step-by-step walkthrough for exploiting CVE-2025-5548 using Ghidra, Immunity Debugger, and…
binary-exploitationdebuggerseducation+6
raulsineiro/cve-2025-5548Binary exploitation laboratory: Environment setup and step-by-step walkthrough for exploiting CVE-2025-5548 using Ghidra, Immunity Debugger, and…
 kevin-mizu/werkzeug-cve-2022-29361-poc
Proof-of-concept exploit for CVE-2022-29361, demonstrating remote code execution via Werkzeug debugger console in Python web applications.
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 luisyapura/analisis-y-explotacion-de-cve-2025-5548
Educational lab for analyzing and exploiting CVE-2025-5548 (FreeFloat FTP Server buffer overflow) with step-by-step guides, debugger setup, and…
 rog3rsm1th/frelatage
Coverage-based fuzzer for python applications
 kartoffelpflanze/odis-project-explorer
Python dumper/explorer for MCD Runtime Projects used by ODIS
 nccgroup/umap2
Umap2 is the second revision of NCC Group's python based USB host security assessment tool.
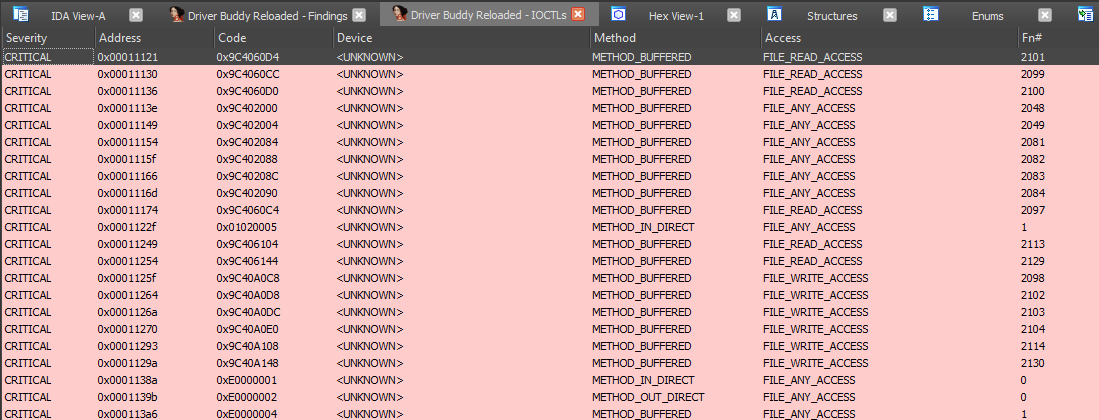 voidsec/driverbuddyreloaded
Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks
 gengstah/windbg-mcp
An MCP (Model Context Protocol) server that turns all pybag Windows debugger functions into native MCP tools. It lets MCP-compatible clients (Claude…
 nccgroup/libtalloc
libtalloc is a python script for use with GDB that can be used to analyse the "trivial allocator" (talloc)
 trailofbits/not-slithering-anywhere
The Python Version of our Not Go-ing Anywhere Vulnerable Application
 phantomn/virtualbox_cve-2019-2525-cve-2019-2548
Proof-of-concept exploits for VirtualBox guest-to-host escape vulnerabilities CVE-2019-2525 and CVE-2019-2548, with a Python library for HGCM…
 yezzfusl/cve_2023_38831_scanner
This Python application scans for the CVE-2023-38831 vulnerability in WinRAR.
 diego57709/cve-2025-5548
Structured lab for controlled exploitation of CVE-2025-5548 (FreeFloat FTP Server). Includes environment setup, fuzzing, EIP control, badchars…
 charlyrr/cve-2025-5548
Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…
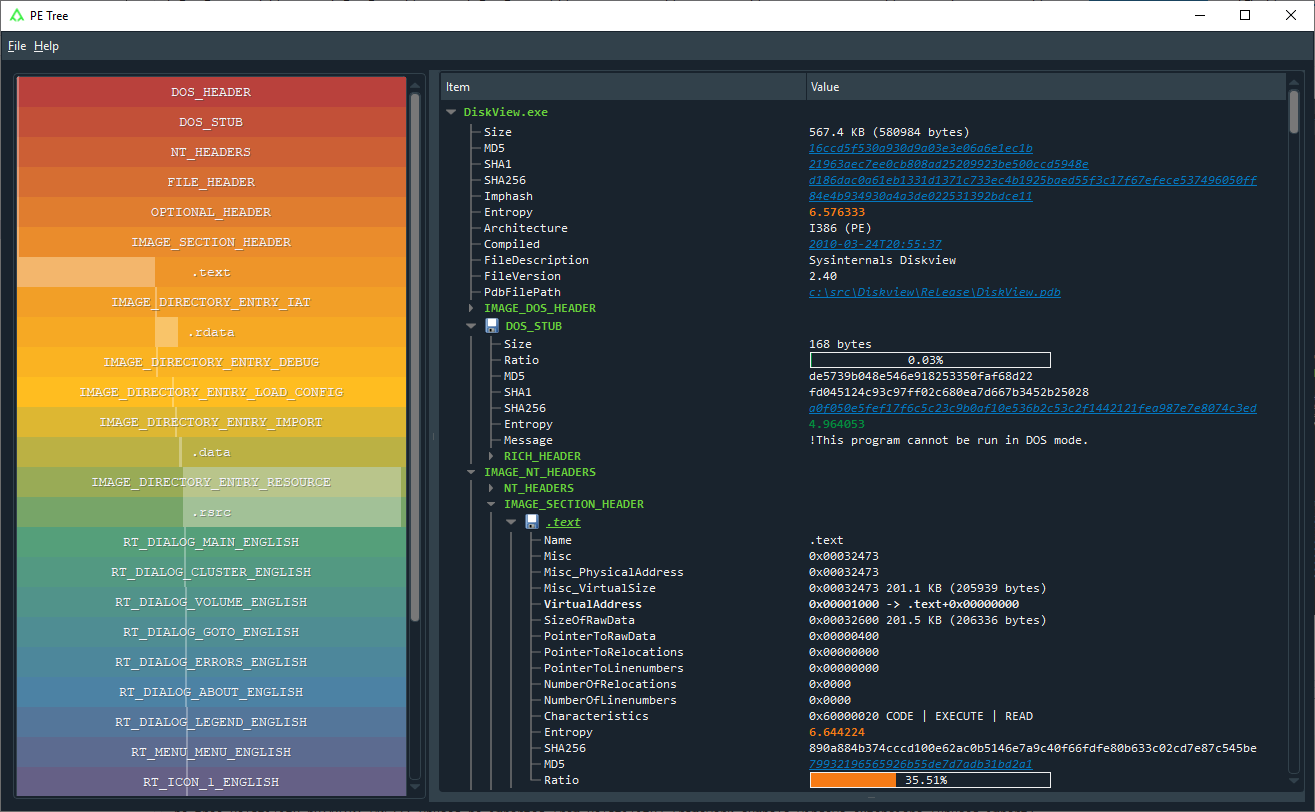 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 airbus-seclab/bincat
Binary code static analyser, with IDA integration. Performs value and taint analysis, type reconstruction, use-after-free and double-free detection