

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
65 results
summit preview

summit

GitHubpennacle-security/summit

Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
api-security-testingfuzzinginformation-gathering+9
4
8 days ago
CVE-2017-5638-Attack-and-Defense preview

CVE-2017-5638-Attack-and-Defense

GitHubacharaf06/cve-2017-5638-attack-and-defense

Docker-based security lab demonstrating Apache Struts2 S2-045 (CVE-2017-5638) exploitation and defense, featuring vulnerable and patched applications…
defensive-toolseducationlabs-practice+4
110 months ago
CVE-2026-87902 preview

CVE-2026-87902

GitHubbhideki/cve-2026-87902

Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
exploitationpayload-developmentpenetration-testing+6
21 month ago
ModSecurity preview

ModSecurity

GitHubowasp-modsecurity/modsecurity

ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…

anti-botapi-securitydefensive-tools+7
9.7k2 days ago
dalfox preview

dalfox

GitHubhahwul/dalfox

Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
devsecopsdynamic-code-analysispenetration-testing+5
5.2k2 days ago
collection-document preview

collection-document

GitHubtom0li/collection-document

Collection of quality safety articles. Awesome articles.
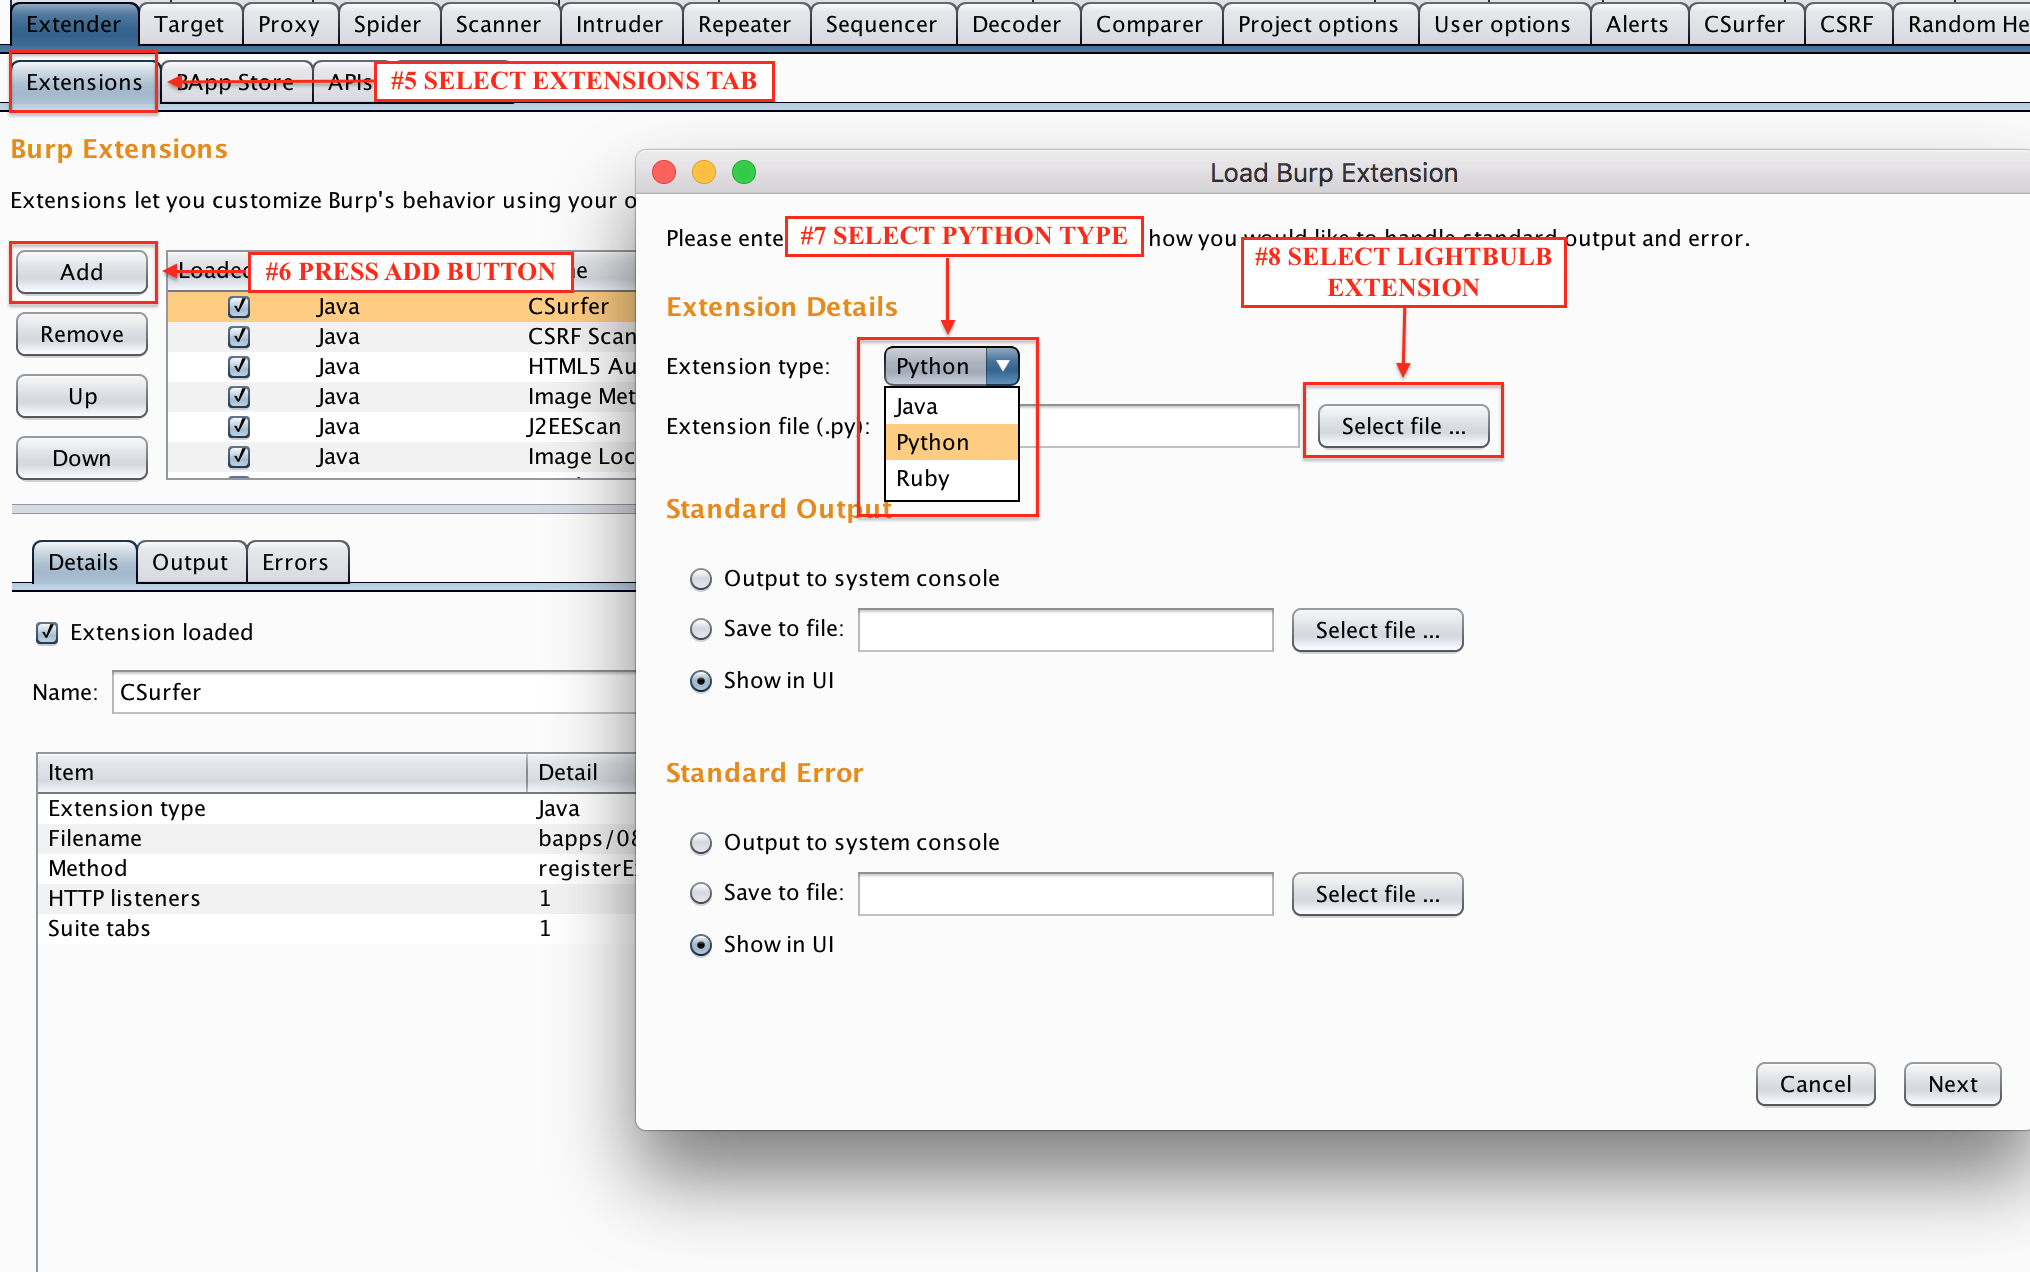
cloud-securitycurated-resourcesdevsecops+9
2.1k5 years ago
lightbulb-framework preview

lightbulb-framework

GitHublightbulb-framework/lightbulb-framework

Tools for auditing WAFS

fuzzingpenetration-testingvulnerability-analysis+2
4655 years ago
wafpass preview

wafpass

GitHubwafpassproject/wafpass

Analysing parameters with all payloads' bypass methods, aiming at benchmarking security solutions like WAF.

penetration-testingvulnerability-analysiswaf-bypass+2
2213 years ago
BurpSuiteHTTPSmuggler preview

BurpSuiteHTTPSmuggler

GitHubnccgroup/burpsuitehttpsmuggler

A Burp Suite extension to help pentesters to bypass WAFs or test their effectiveness using a number of techniques

ids-ips-evasionpenetration-testingvulnerability-analysis+3
7457 years ago
waf-dojo preview

waf-dojo

GitHubnishikawaakira/waf-dojo

Hands-on AWS WAF training game with tutorials, scored labs, and exams where players write Web ACL rules to block real attack shapes while avoiding…
cloud-securityctfdefensive-tools+7
182 days ago
cpanel-sessionscribe preview

cpanel-sessionscribe

GitHubrfxn/cpanel-sessionscribe

Detection, mitigation, and reverse-engineering tooling for CVE-2026-41940 (SessionScribe): the cPanel/WHM unauthenticated session-forgery…
defensive-toolsexploitationforensics+7
145 months ago
CVE-2024-34102 preview

CVE-2024-34102

GitHub11whoami99/cve-2024-34102

Proof-of-concept for CVE-2024-34102 exploiting unauthenticated Magento XXE and WAF bypass by sending a crafted request to the…
exploitationpenetration-testingvulnerability-analysis+2
32 years ago
Bypass-CVE-2025-58360 preview

Bypass-CVE-2025-58360

GitHubquyenheu/bypass-cve-2025-58360

A new way to exploit CVE-2025-58360 bypass WAF
exploitationpenetration-testingvulnerability-analysis+2
110 months ago
CVE-2026-21876 preview

CVE-2026-21876

GitHubmefhika120/cve-2026-21876

Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.

exploitationpenetration-testingvulnerability-analysis+2
9 months ago
CVE-2025-59342 preview
Archived

CVE-2025-59342

GitHubbytereaper77/cve-2025-59342

C exploit for CVE-2025-59342 path traversal in esm.sh CDN (v136 and earlier). Injects payloads via X-Zone-Id header with WAF bypass and cookie…

exploitationpenetration-testingvulnerability-analysis+2
11 year ago
CVE-2021-44228-PoC-log4j-bypass-words preview

CVE-2021-44228-PoC-log4j-bypass-words

GitHubpuliczek/cve-2021-44228-poc-log4j-bypass-words

🐱‍💻 ✂️ 🤬 CVE-2021-44228 - LOG4J Java exploit - WAF bypass tricks
educationexploitationids-ips-evasion+6
9504 years ago
Log4j2-CVE-2021-44228 preview

Log4j2-CVE-2021-44228

GitHubjas502n/log4j2-cve-2021-44228

CVE-2021-44228 Log4j2 remote code injection exploit with JNDI payload generation, WAF bypass techniques, and practical exploitation walkthrough for…
educationexploitationpayload-generation+4
4694 years ago
Imperva_gzip_WAF_Bypass preview

Imperva_gzip_WAF_Bypass

GitHubbishopfox/imperva_gzip_waf_bypass

Exploit for Imperva Cloud WAF bypass using gzip Content-Encoding header to evade WAF rules on HTTP POST requests. Includes detection script and…

ids-ips-evasionpenetration-testingvulnerability-analysis+2
1684 years ago
Previous1234Next