
CVE-2022-44268-pilgrimage
 katseyres2/cve-2022-44268-pilgrimage
Automated proof-of-concept exploit for CVE-2022-44268 (ImageMagick arbitrary file read) with PNG payload generation, designed for CTF challenges and…
ctfexploitationpenetration-testing+2
katseyres2/cve-2022-44268-pilgrimageAutomated proof-of-concept exploit for CVE-2022-44268 (ImageMagick arbitrary file read) with PNG payload generation, designed for CTF challenges and…
 h3x0v3rl0rd/cve-2019-5736
Go-based exploit for CVE-2019-5736 (Runc container escape) with a customizable reverse shell payload, designed for penetration testing and red team…
 cdedmondson/modified-cve-2019-15107
Modified exploit for CVE-2019-15107 with a Perl reverse shell payload. Designed for penetration testing of the targeted web application vulnerability.
 chessredoffsec/cve-2023-26208
Python script with GUI for automated payload testing against login endpoints, designed for educational exploitation simulation and vulnerability…
 chessredoffsec/cve-2023-26209
Python script with a Tkinter GUI for sending automated payloads of configurable size to a login endpoint, designed for educational testing of server…
 charlesbickel/cve-2021-38619
Proof-of-concept for CVE-2021-38619: unauthenticated stored XSS in openBaraza HCM HR Payroll v3.1.6, with payload examples for credential theft and…
 ersinerenler/cve-2023-46015-code-projects-blood-bank-1.0-reflected-cross-site-scripting-vulnerability
Proof-of-concept exploit for reflected cross-site scripting (XSS) in Code-Projects Blood Bank V1.0 via the 'msg' parameter in index.php, with payload…
 desultory/cve-2026-31431
Demonstrates CVE-2026-31431 by poisoning the cache for a target file with attacker-controlled payload bytes, illustrating a web cache poisoning…
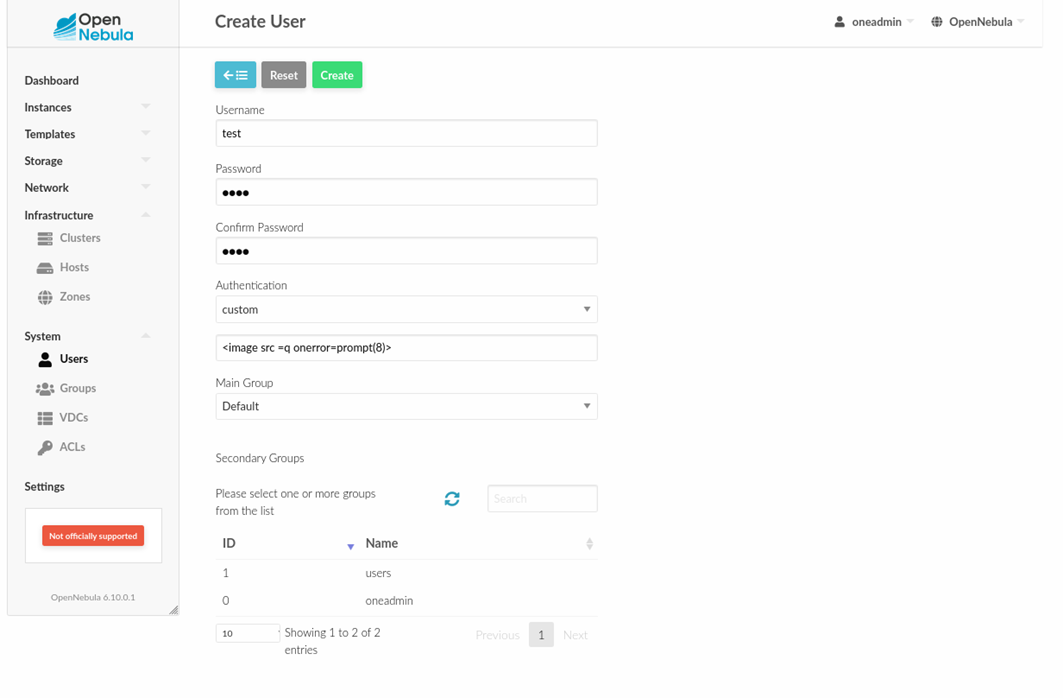 markartamonov/opennebula-cve-2025-56534
Stored XSS exploit for OpenNebula 6.10.0.1 via custom authenticator driver, with proof-of-concept payload and fix guidance for upgrading to version…
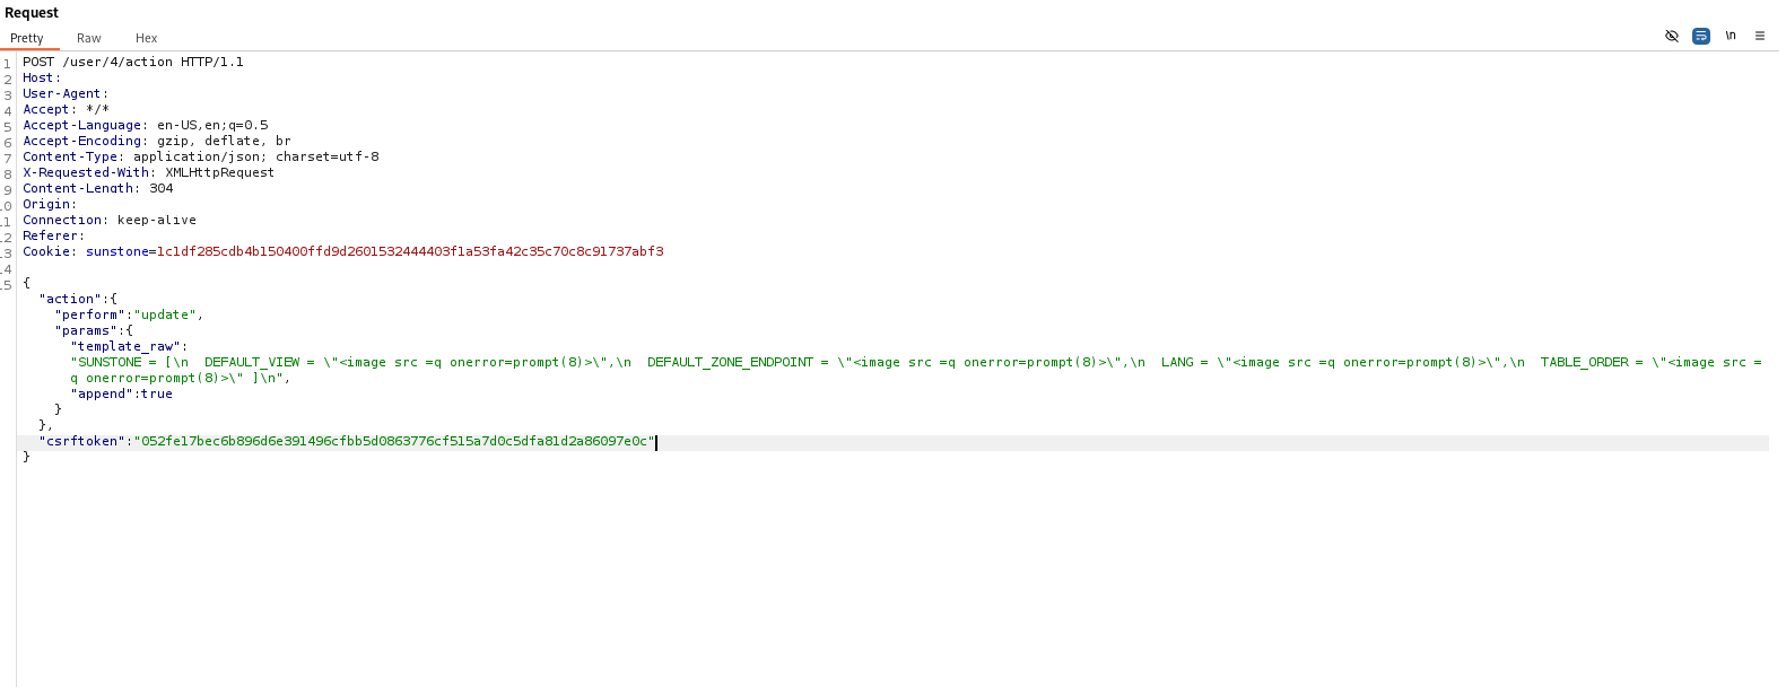 markartamonov/opennebula-cve-2025-56536
Stored XSS exploit for OpenNebula Sunstone (CVE-2025-56536) with proof-of-concept payload targeting user information parameter in versions < 7.0.
 jfriedli/cve-2025-11177
Time-based SQL injection exploit for CVE-2025-11177 targeting WordPress login with curl-based payload delivery and pg_sleep timing detection.
 falconz/cve-2019-12189
Proof-of-concept for a stored XSS vulnerability in Zoho ManageEngine ServiceDesk Plus 9.3, with a payload exploiting single quote and semicolon…
 ersinerenler/cve-2023-46016-code-projects-blood-bank-1.0-reflected-cross-site-scripting-vulnerability
Reflected XSS exploit for Code-Projects Blood Bank V1.0 via the 'search' parameter in abs.php, with PoC payload and CVE-2023-46016 documentation.
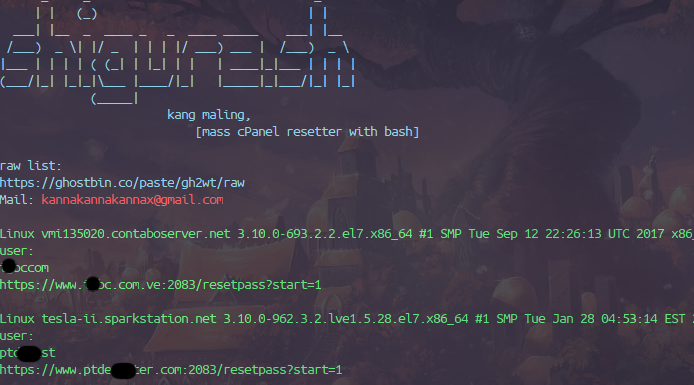 redsplit/shiguresh
CVE-2004-1769 // Mass cPanel Reset password
 bigzooooz/cve-2022-31298
Haraj Script 3.7 - Authenticated Stored XSS
 g0rx/drupal-sa-core-2019-003
Proof-of-concept exploit for CVE-2019-6340 targeting Drupal's RESTful web services module, with curl-based RCE payload and detailed reproduction…
 kac89/cve-2024-6050
Proof-of-concept exploit for reflected XSS vulnerability (CVE-2024-6050) in SOWA OPAC versions 4.0-4.9.10 and 5.0-6.2.12, with a working payload…
 ersinerenler/cve-2023-46019-code-projects-blood-bank-1.0-reflected-cross-site-scripting-vulnerability
Proof-of-concept exploit for reflected cross-site scripting (XSS) in Code-Projects Blood Bank V1.0 via the 'error' parameter in abs.php, with a…