CVE-2024-29943
 seadragnol/cve-2024-29943
Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943
binary-exploitationeducationexploitation+2
seadragnol/cve-2024-29943Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943
 dywhoami/cve-2021-34527-scanner-based-on-cube0x0-poc
Scanner for Windows Print Spooler service vulnerability CVE-2021-34527, based on cube0x0's PoC, enabling detection of exploitable targets.
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
 7bitsteam/exch_cve-2021-42321
Modified .NET deserialization payload for CVE-2021-42321, based on ysoserial.net, that writes files and bypasses Windows Defender to target Microsoft…
 vp777/windows-kernel-exploitation
Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…
 bitsadmin/wesng
Windows Exploit Suggester - Next Generation
 adenkiewicz/cve-2009-1330
Simple exploit for Easy RM to MP3 Converter 2.7.3.700 on Windows 7 32b.
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 lsw29475/cve-2020-17057
Windows kernel exploit for CVE-2020-17057 using palette objects with dangling data pointers, targeting type isolation bypass for privilege escalation.
 amlweems/gringotts
proof of concept for CVE-2020-0601
 horizon3ai/cve-2021-44077
Proof-of-concept exploit for PreAuth RCE in ManageEngine ServiceDesk Plus (CVE-2021-44077). Uploads and executes arbitrary Windows executables on…
 rt1252/cve-2021-34427
Windows POC for CVE-2021-34427 affecting Birt Viewer
 rvn0xsy/cve_2020_0796_cna
Cobalt Strike AggressorScripts CVE-2020-0796
 joaoaugustom/adobe_coldfusion_rce_unauthenticated
This exploit is based on CVE-2023-26360 (https://nvd.nist.gov/vuln/detail/CVE-2023-26360) and was built on top of the Metasploit module and the…
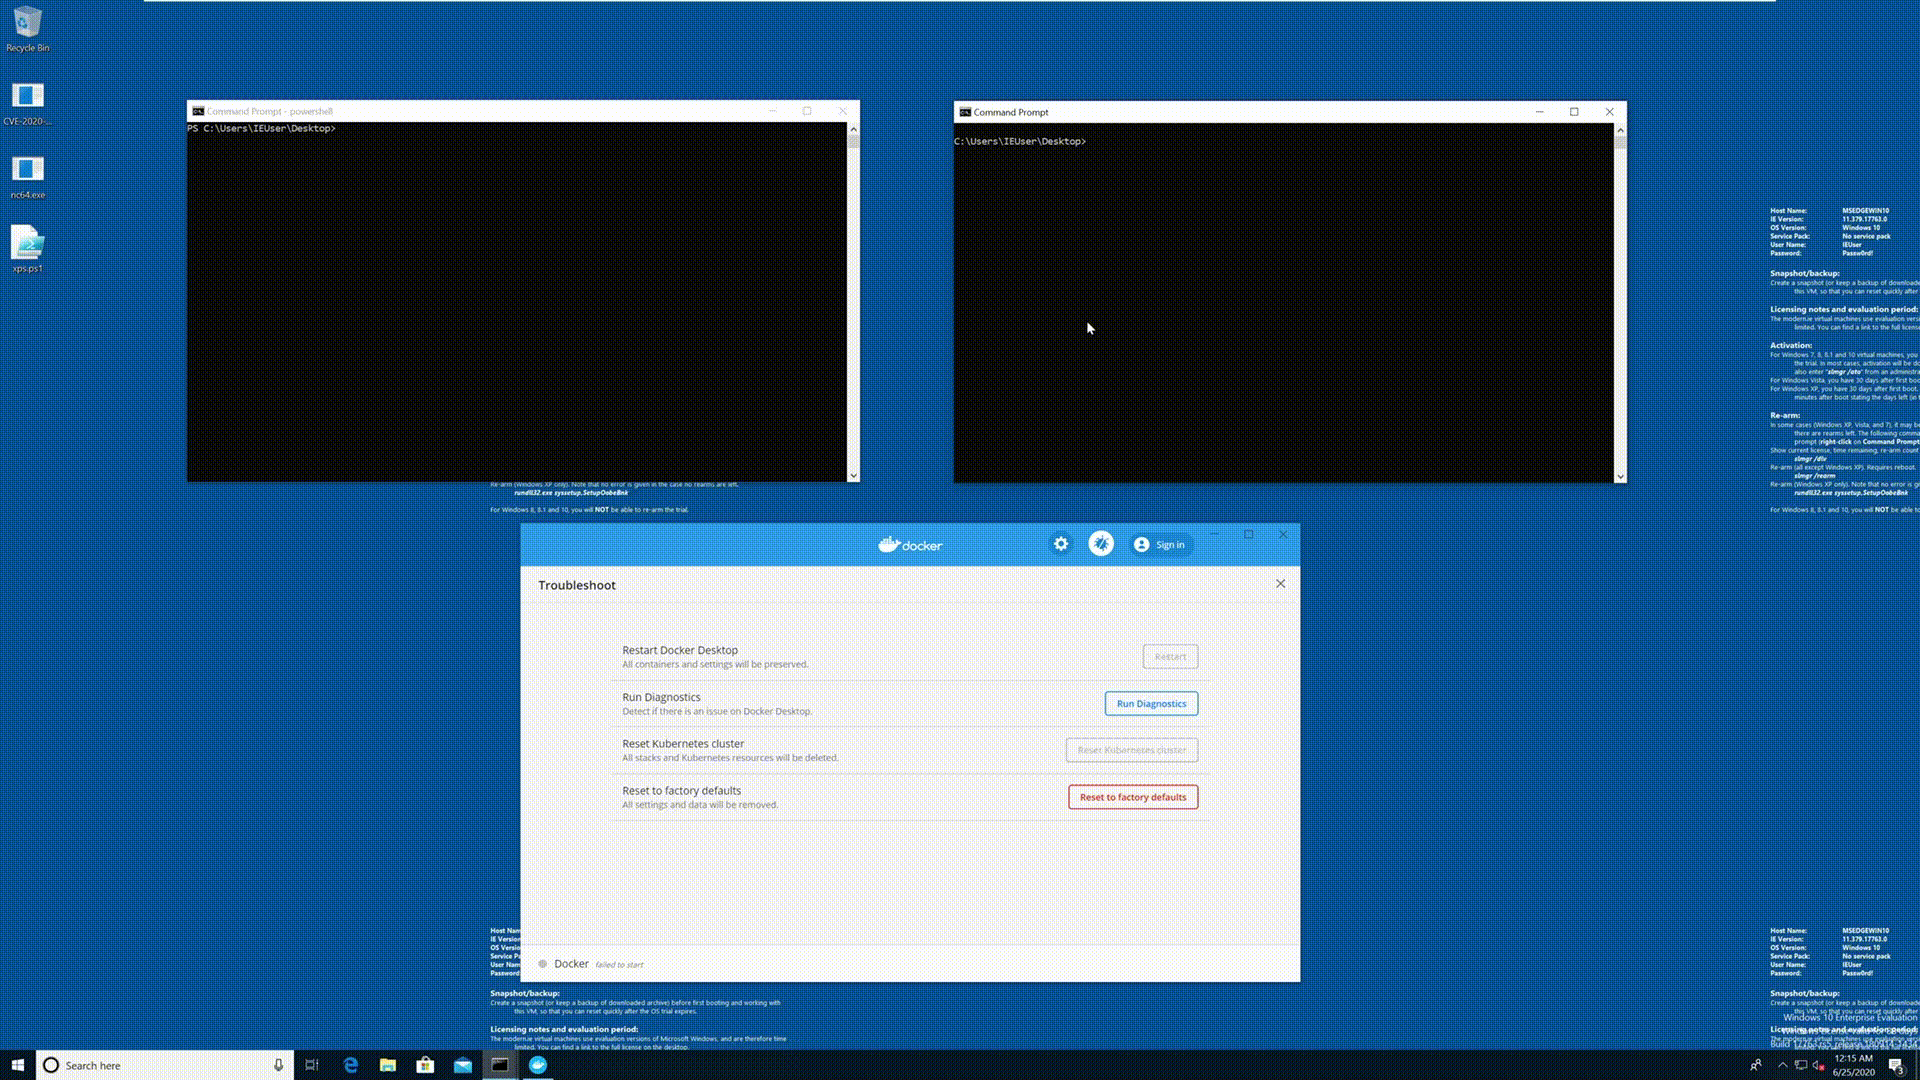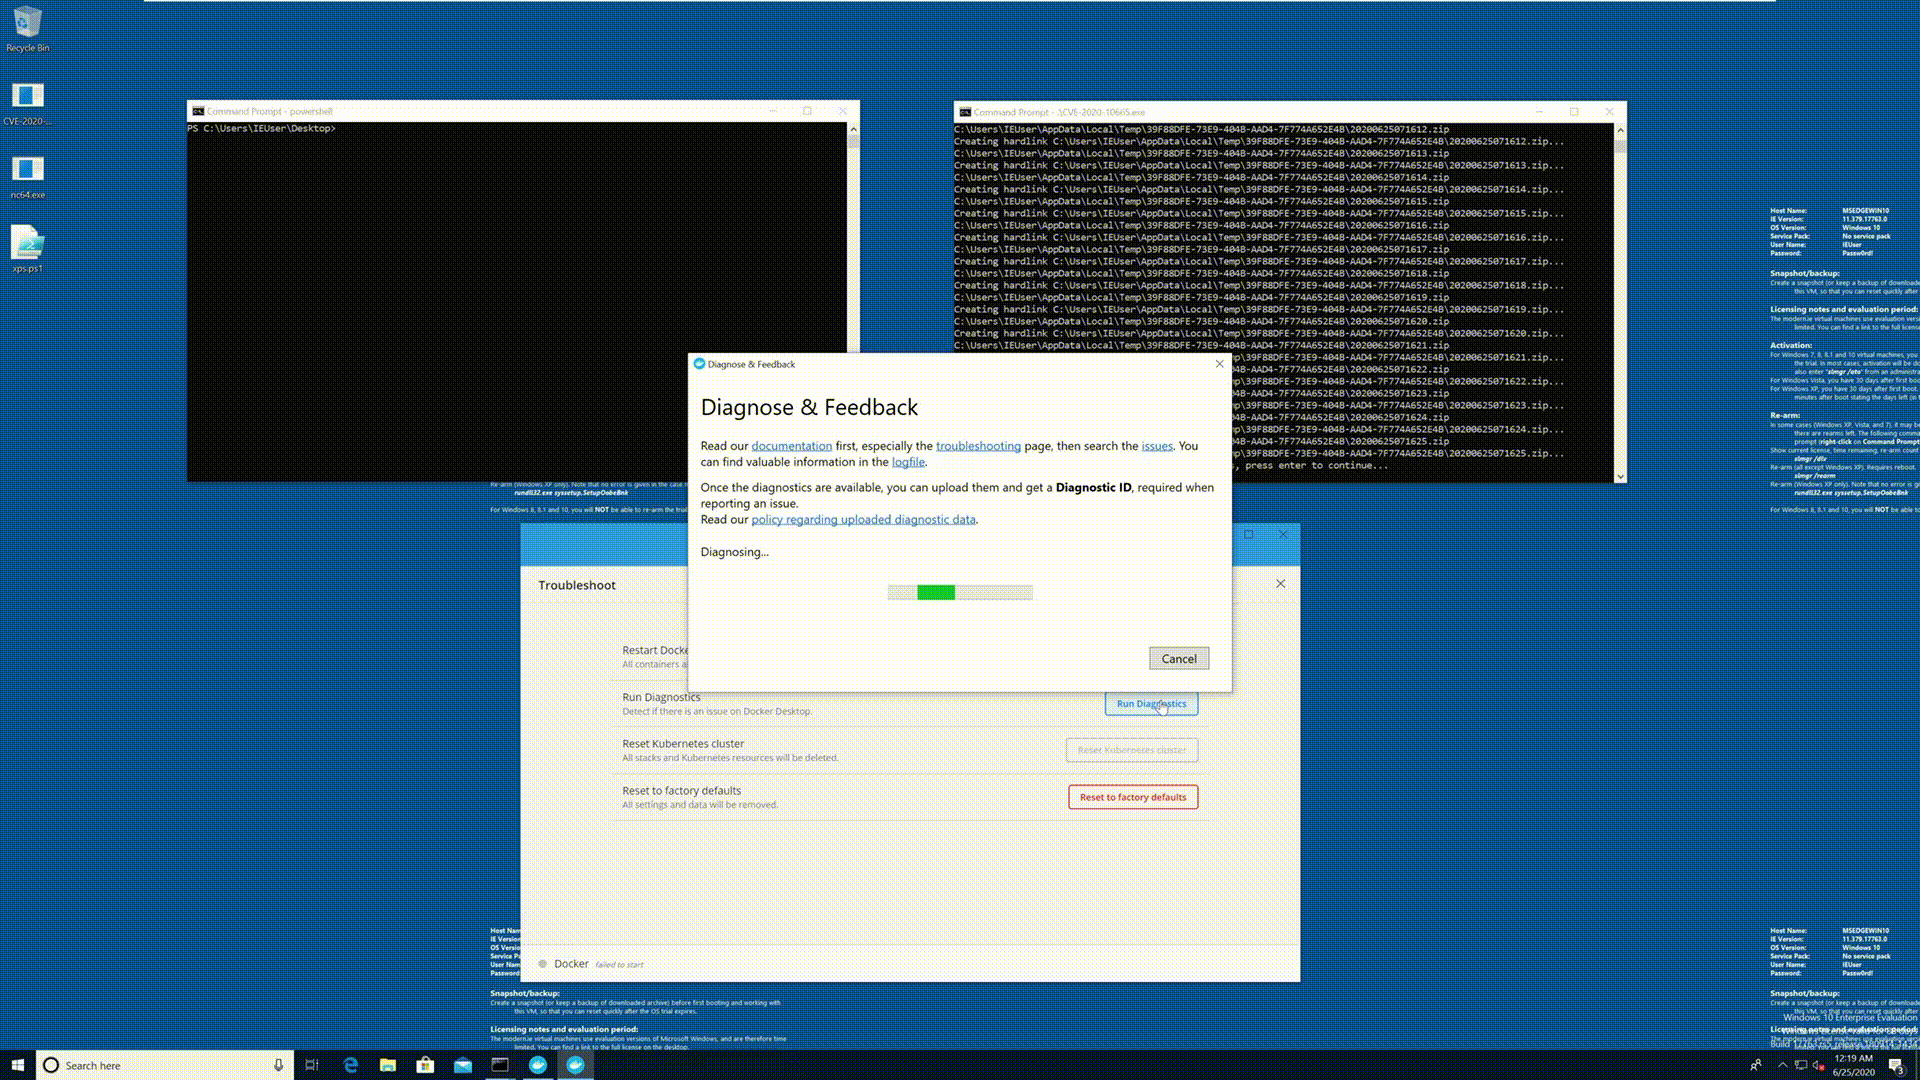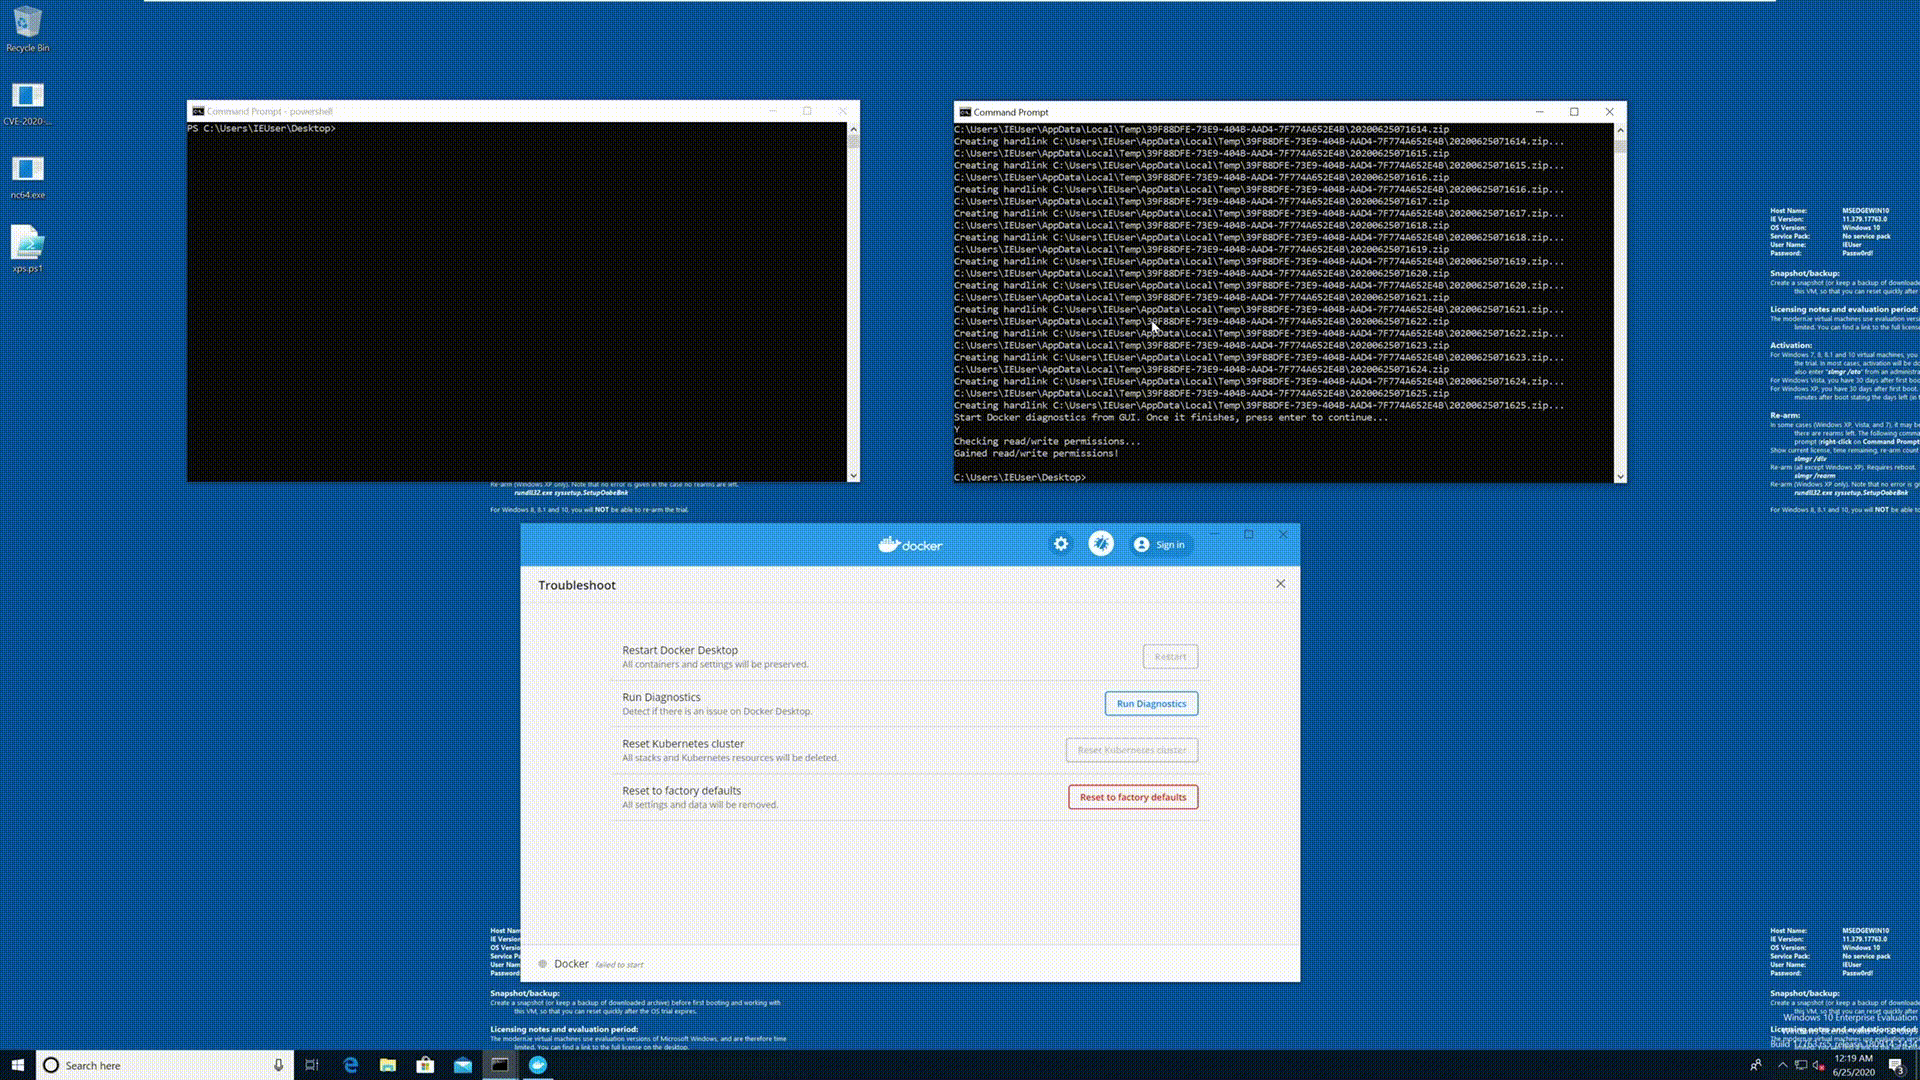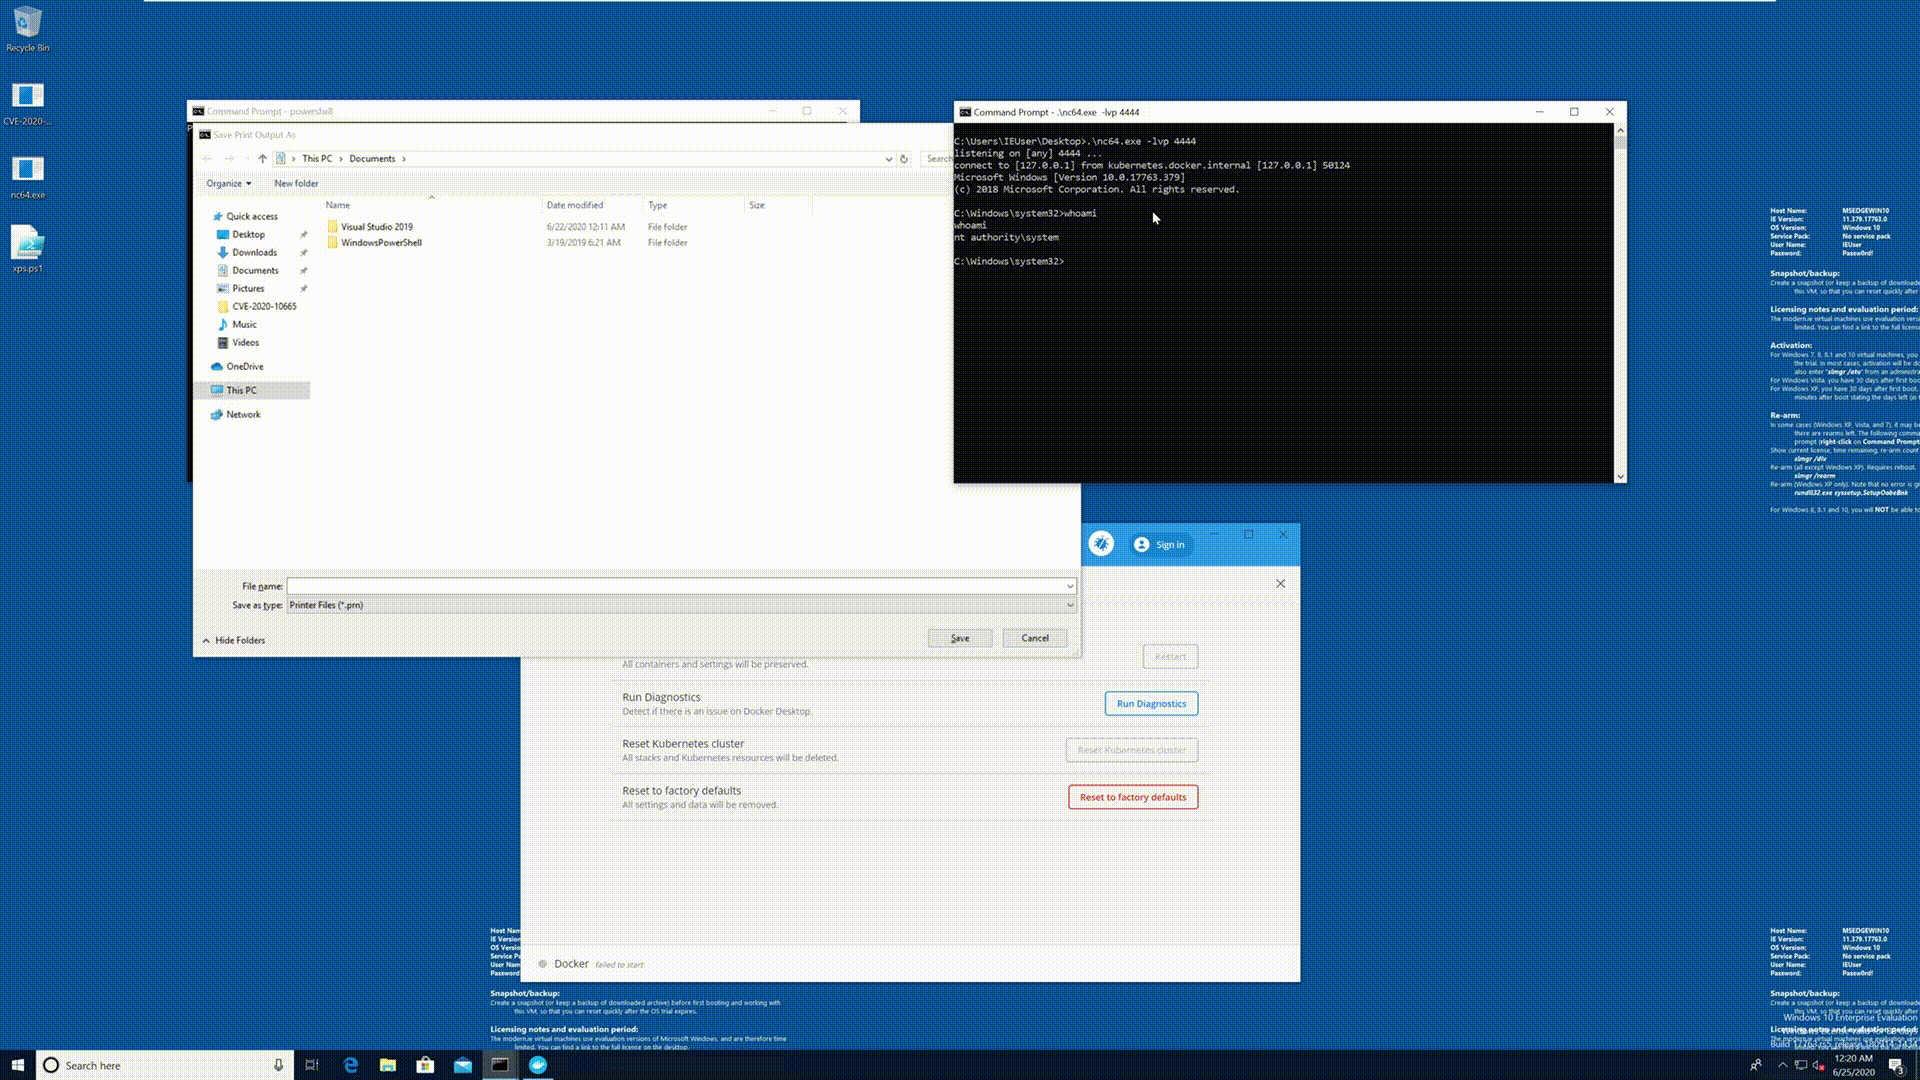 spaceraccoon/cve-2020-10665
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation
 h4xl0r/winrar_ace_exploit_cve-2018-20250
This program is an script developed in Python which exploit the ACE vulnerability on WinRar - Vulnerability CVE-2018-20250
 chuzoux/cve-2025-32433-exploit-edited
Based on the original version:https://github.com/vulhub/vulhub/blob/master/erlang/CVE-2025-32433/exploit.py Replace Unicode checkmark with ASCII…