

Archived
volatility
 volatilityfoundation/volatility
An advanced memory forensics framework
digital-forensicsforensicsincident-response+4
volatilityfoundation/volatilityAn advanced memory forensics framework
 splintersfury/autopiff
Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 colton1skees/dna
LLVM based static binary analysis framework
 pascal-lab/tai-e
An easy-to-learn/use static analysis framework for Java and Android
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
 morpheuslord/quadrainspect
Modular Android APK security analysis framework integrating static, dynamic, and reverse engineering tools for comprehensive vulnerability assessment…
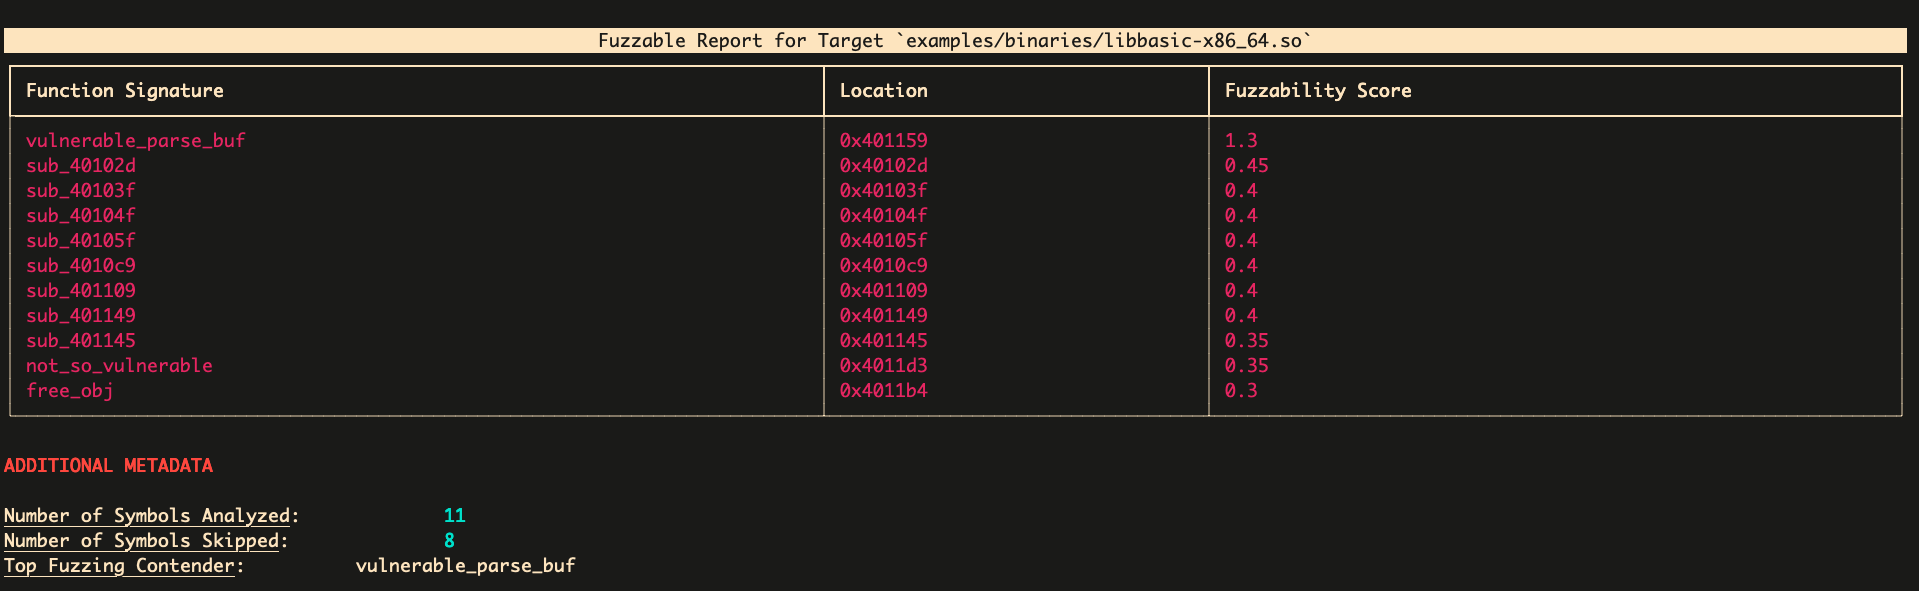 ex0dus-0x/fuzzable
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 purs3lab/argus
Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…
 angr/angr
A powerful and user-friendly binary analysis platform!
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
 crytic/slither
Static Analyzer for Solidity and Vyper
 crytic/caracal
Static Analyzer for Starknet smart contracts
 pr0v3rbs/firmae
Towards Large-Scale Emulation of IoT Firmware for Dynamic Analysis
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…