burp-alfresco-referer-proxy-cve-2014-9301

Burp Suite extension exploiting CVE-2014-9301 in Alfresco Referer Proxy for targeted web application penetration testing.

Burp Suite extension exploiting CVE-2014-9301 in Alfresco Referer Proxy for targeted web application penetration testing.

Proof-of-concept exploit for CVE-2024-2054, demonstrating insecure deserialization RCE in Artica-Proxy administrative web application. Includes…

Interactive demo of CVE-2022-45059 Varnish Cache request smuggling vulnerability. Includes Spring Boot web app, vulnerable proxy, automated victim…

Python-based proof-of-concept exploit for CVE-2021-3019 targeting Lanproxy, enabling remote code execution via directory traversal in the web proxy…

Python-based web crawler and SQL injection vulnerability scanner using dork queries. Supports proxy and automated scanning for security testing.

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

Proof-of-concept exploit for CVE-2018-11759 demonstrating Apache mod_jk access bypass via specially crafted requests to bypass reverse proxy…

Generates reproducible CORE network topologies from XML scenario files for cybersecurity training and experimentation. Provides Web GUI and CLI for…

A lightweight caching proxy for package registries.

Hackable HTTP proxy for resiliency testing and simulated network conditions

A firewall reverse proxy for preventing Log4J (Log4Shell aka CVE-2021-44228) attacks.

Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.

Exploitability PoC for CVE-2026-49352 (9router Hardcoded JWT Secret Authentication Bypass)

CVE-2015-3224

Chrome extension and Shodan scanner for detecting and demonstrating RCE vulnerabilities in React Server Components (RSC) and Next.js applications,…

Go-based MITM exploit demo for OpenSSL CVE-2014-0224 (CCS Injection) targeting RC4-SHA cipher, with server/client proxy setup for testing TLS…

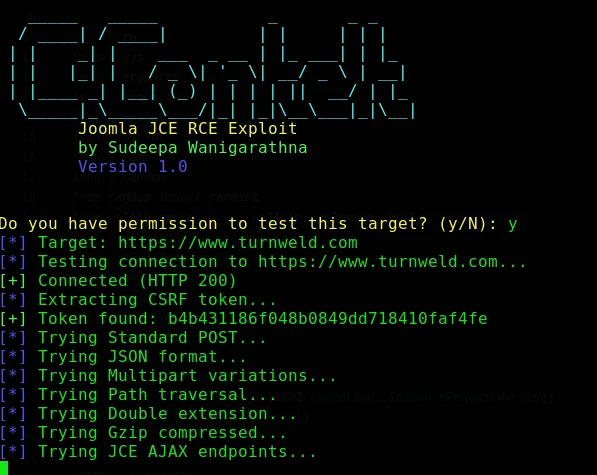
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…

Go-based proof-of-concept for CVE-2025-55182, a critical RCE in React Server Components. Features vulnerability checking, command execution, memory…