

systeminformer
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
16.4k
winsiderss/systeminformerReal-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 vortexcry-organization/vortexcry-ransomware-release
Advanced ransomware using process injection and kernel driver loading via CVE-2019-16098 to encrypt files, disable recovery, and demand ransom. For…
 shoucheng3/asf__nifi_cve-2023-34468_1-21-00
Exploit for Apache NiFi CVE-2023-34468, targeting a vulnerability in versions 1.21.0 and earlier to demonstrate data access and system compromise.
 tdonaworth/firefox-cve-2024-9680
Educational analysis of CVE-2024-9680, a use-after-free vulnerability in Firefox's CSS Animation Timeline, with detailed exploit mechanics and…
 xaitax/sploitscan
Aggregates CVE details, exploit databases, and EPSS scores with AI risk assessment and vulnerability scanner import for prioritized patching.
 iveresk/cve-2022-21907-http.sys
An unauthenticated attacker can send an HTTP request with an "Accept-Encoding" HTTP request header triggering a double free in the unknown…
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
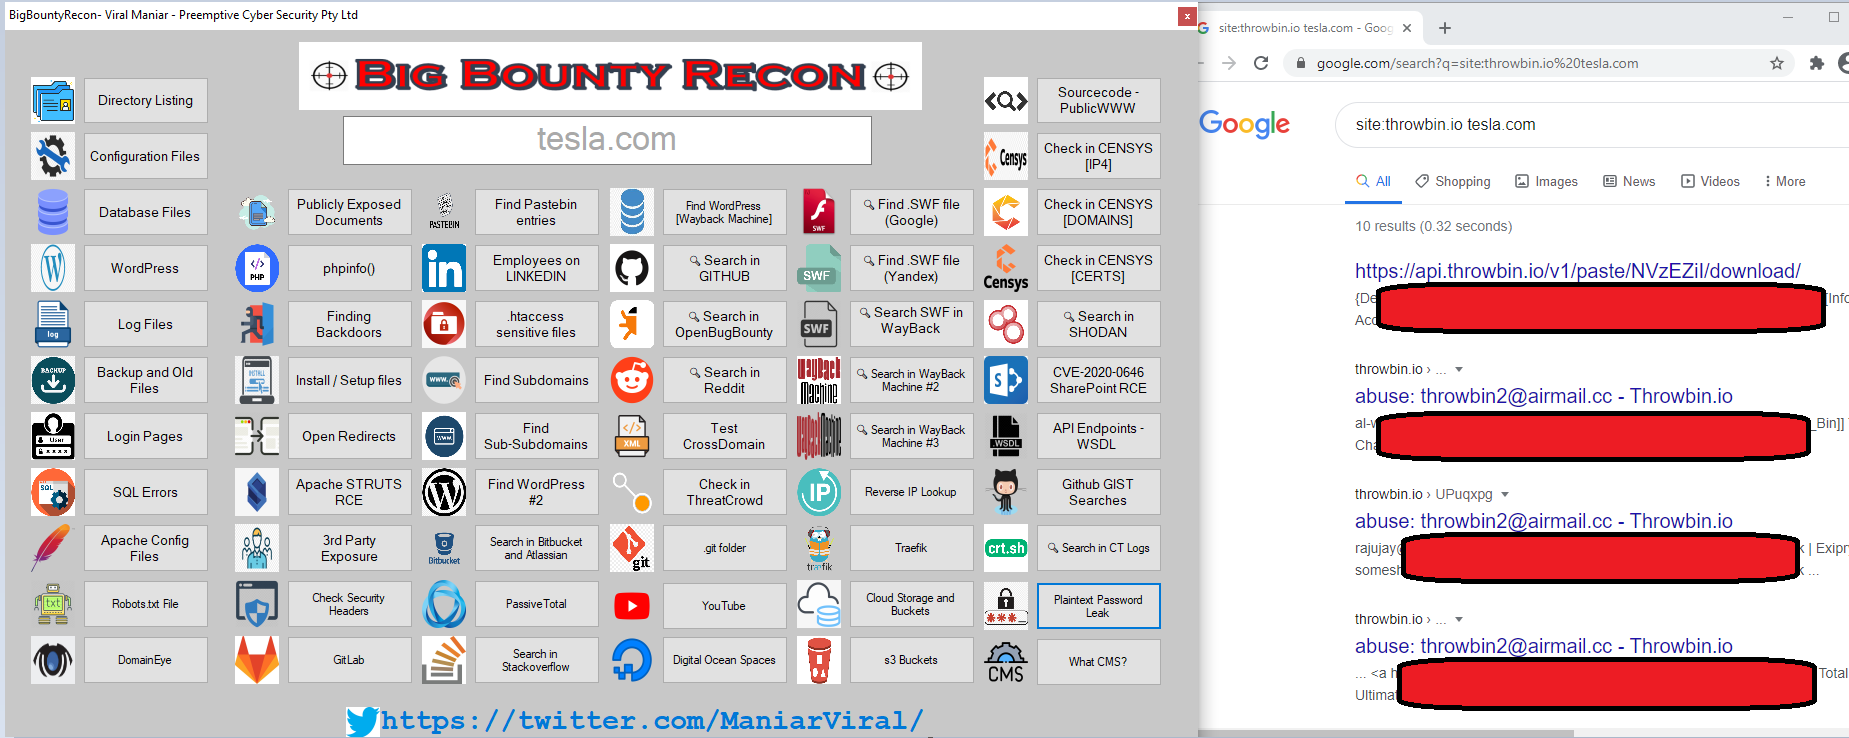 viralmaniar/bigbountyrecon
BigBountyRecon tool utilises 58 different techniques using various Google dorks and open source tools to expedite the process of initial…
 chompie1337/windows_lpe_afd_cve-2023-21768
Local privilege escalation exploit for CVE-2023-21768 targeting Windows AFD driver. Elevates arbitrary process to SYSTEM using I/O Ring read/write…
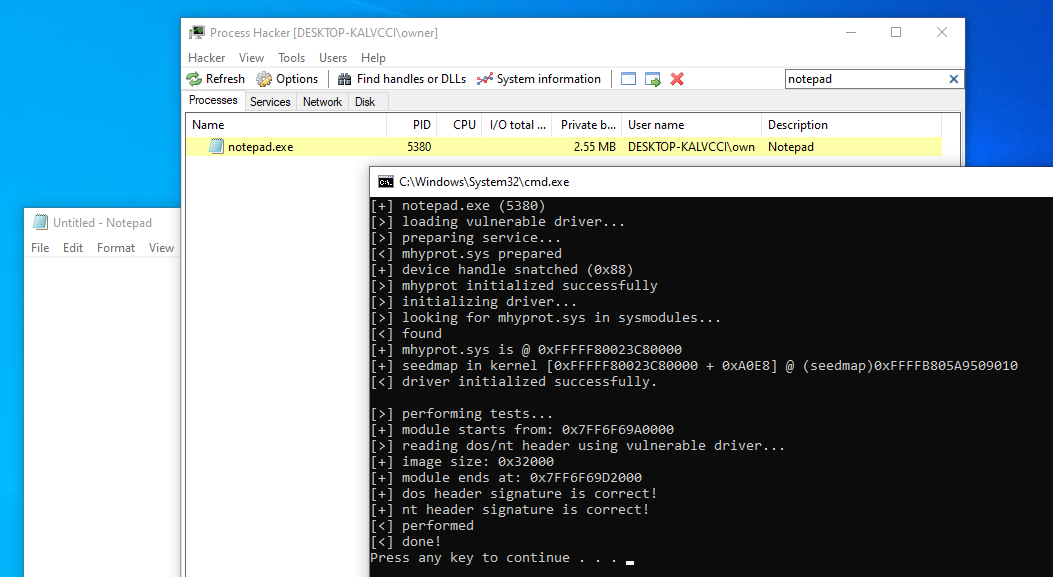 kkent030315/evil-mhyprot-cli
A PoC for Mhyprot2.sys vulnerable driver that allowing read/write memory in kernel/user via unprivileged user process.
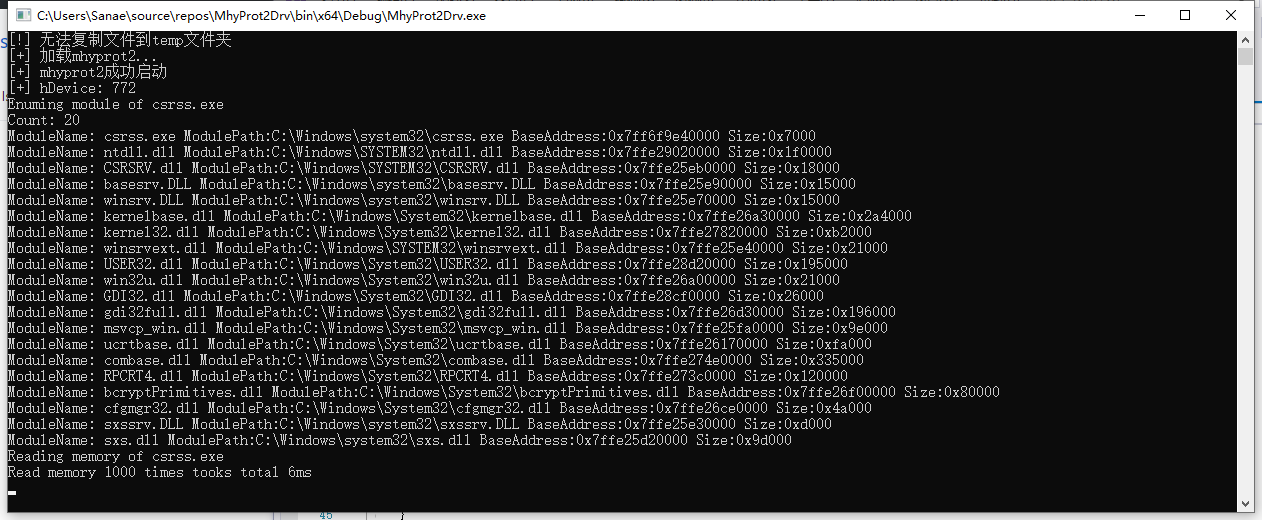 kagurazakasanae/mhyprot2drvcontrol
A lib that allows using mhyprot2 driver for enum process modules, r/w process memory and kill process.
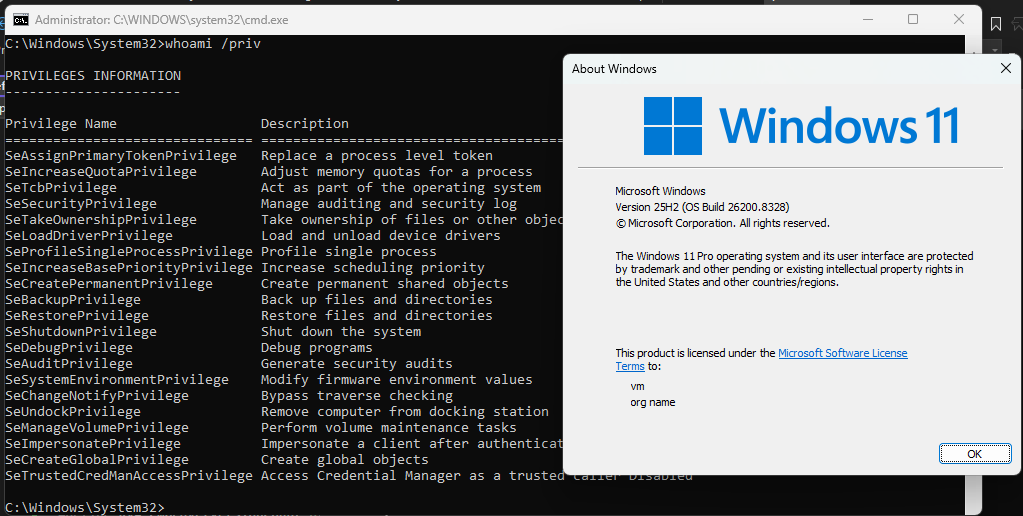 orinimron123/cve-2026-40369-exploit
Full exploit code for CVE-2026-40369 - A Windows kernel arbitrary write vulnerability that allows browser sandbox escape from all browsers render…
 mzfr/slicer
A tool to automate the boring process of APK recon
 po6ix/poc-for-cve-2023-41993
Proof-of-concept exploit for CVE-2023-41993, a WebKit JIT type confusion in Safari. Provides addrof/fakeobj primitives via heap manipulation and…
 ethicalhackingplayground/tproxer
A Burp Suite extension made to automate the process of finding reverse proxy path based SSRF.