

OWASPBugBounty
 owasp/owaspbugbounty
This is a container of web applications that work with OWASP Bug Bounty for Projects
ctfeducationlabs-practice+3
owasp/owaspbugbountyThis is a container of web applications that work with OWASP Bug Bounty for Projects
 scriptingxss/iotgoat
IoTGoat is a deliberately insecure firmware based on OpenWrt.
 owasp/iotgoat
Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 waburig/open-worldwide-application-security-project-owasp-
Automated Web Vulnerability Assessment of DVWA using OWASP ZAP to identify and analyze critical security flaws like Remote Code Execution…
 owasp/owaspwebgoatphp
A deliberately vulnerable web application for learning web application security.
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 owasp/nodegoat
The OWASP NodeGoat project provides an environment to learn how OWASP Top 10 security risks apply to web applications developed using Node.js and how…
 owasp/benchmark
The OWASP Benchmark GitHub repo has moved to: https://github.com/OWASP-Benchmark/BenchmarkJava
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
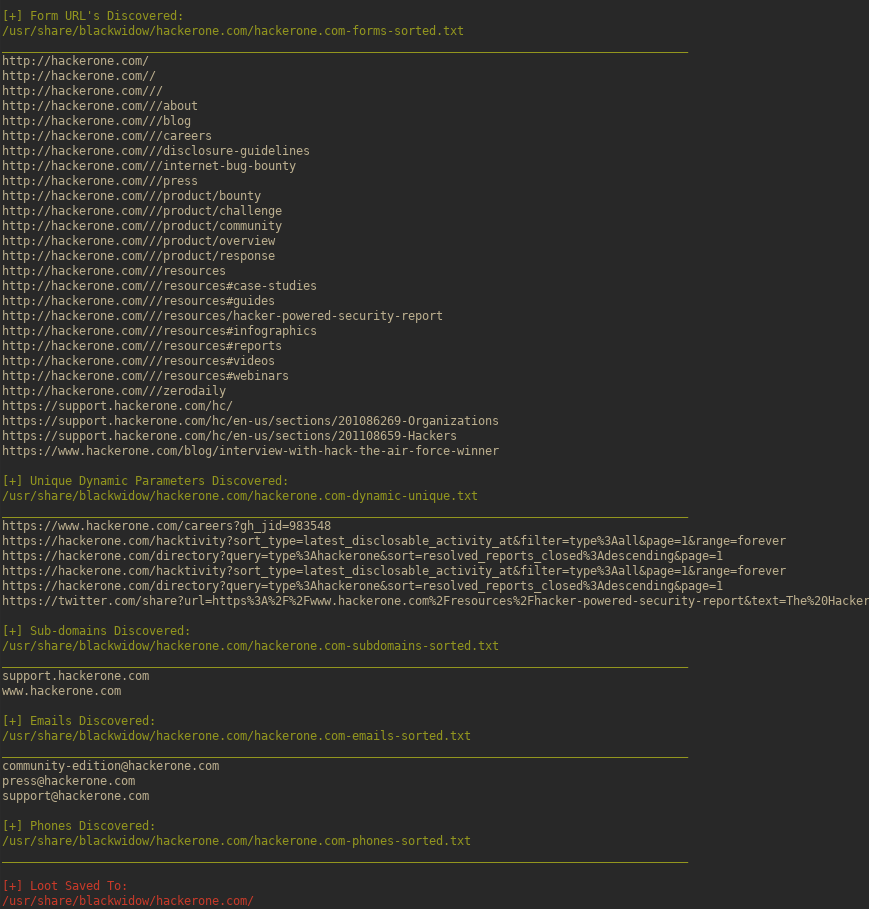 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 canpilayda/n8n-rce-cve-2025-68613
Lab report analyzing CVE-2025-68613 expression injection in n8n, demonstrating sandbox escape via crafted payloads to access sensitive server files,…
 jeremylong/dependencycheck
The dependency-check repository has moved:
 jacobideji/aiiroverlay
AI IR Overlay™ — practical incident response framework for AI agents in production. Built on NIST SP 800-61 r3, mapped to NIST AI RMF, NIST CSF 2.0,…
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 ine-labs/azuregoat
AzureGoat : A Damn Vulnerable Azure Infrastructure
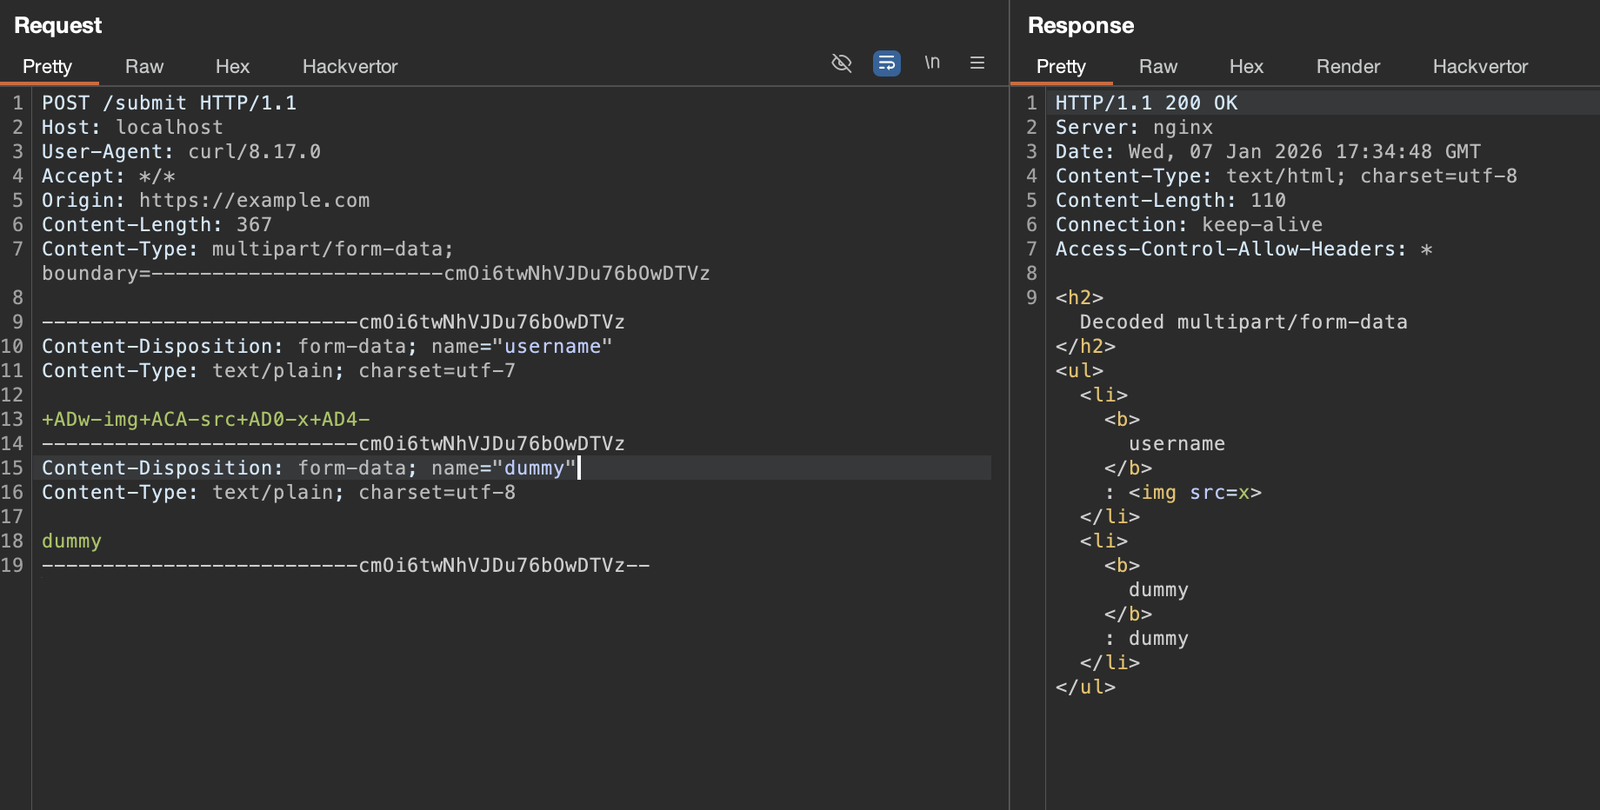 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.