

PCAPdroid
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
android-securitydns-analysiseducation+8
emanuele-f/pcapdroidNo-root network monitor, firewall and PCAP dumper for Android
 reverseclabs/drozer
The Leading Security Assessment Framework for Android.
 pascal-lab/tai-e
An easy-to-learn/use static analysis framework for Java and Android
 bytedance/appshark
Static taint analysis platform for Android apps that detects vulnerabilities and compliance issues using customizable rule-based scanning and…
 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
 1n3/reverseapk
Quickly analyze and reverse engineer Android packages
 joinchang/ghostlock-oneplus
GhostLock (CVE-2026-43499) kernel exploit for Android devices with locked bootloader
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
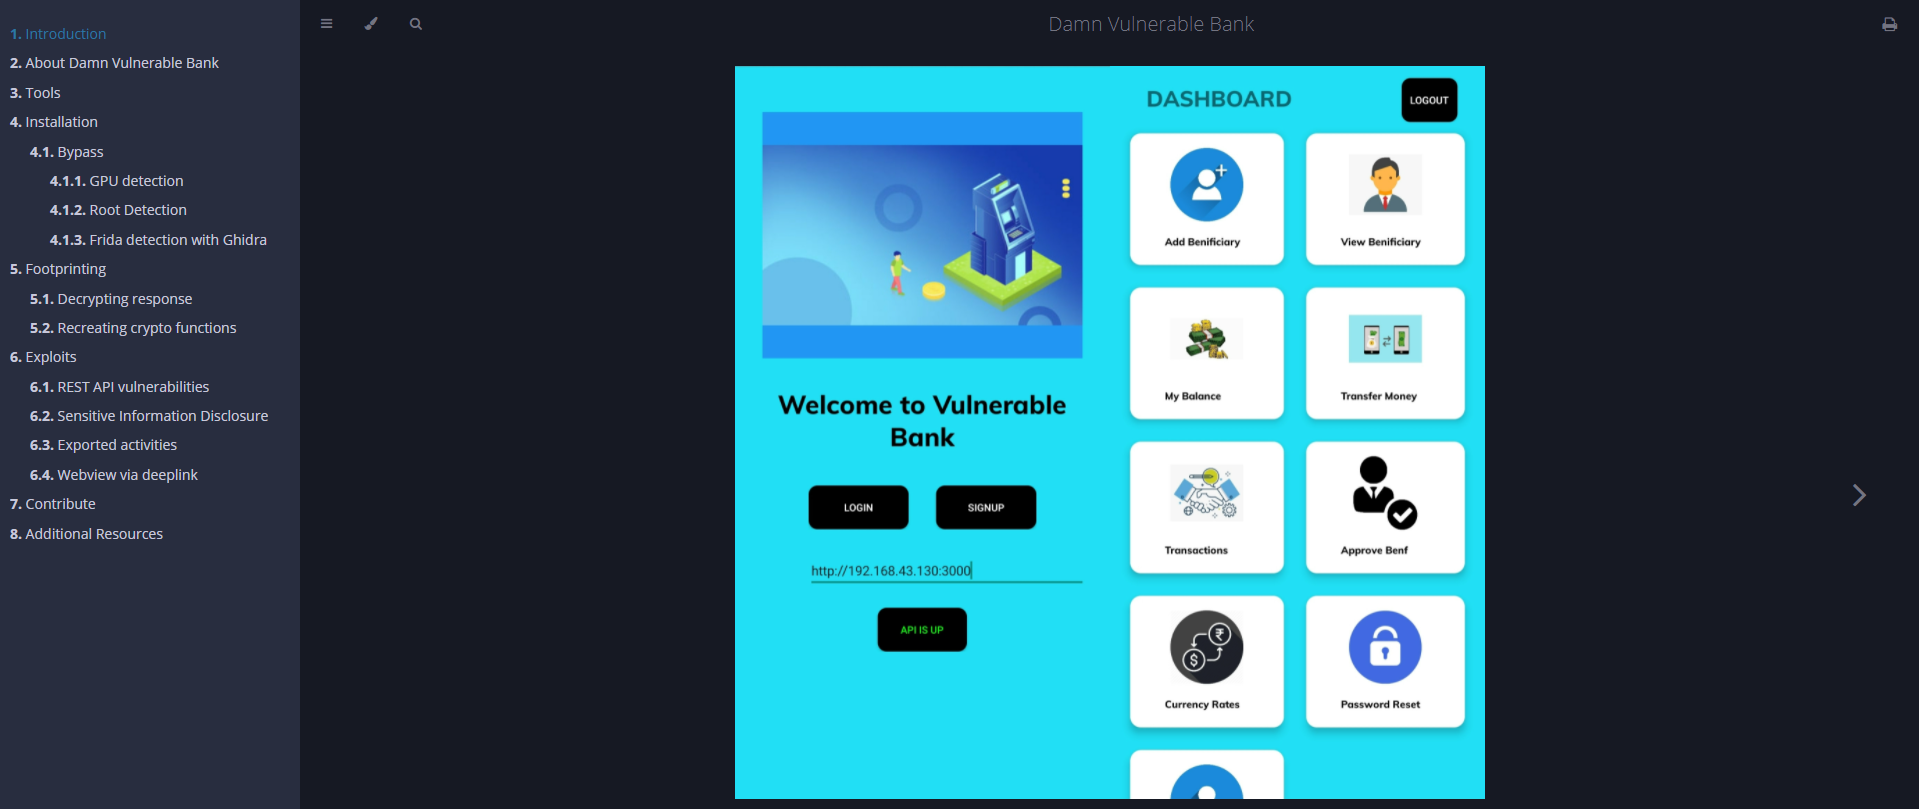 rewanthtammana/damn-vulnerable-bank
Intentionally vulnerable Android banking app for practicing mobile security testing, featuring root detection, anti-debugging, SSL pinning, and…
 morpheuslord/quadrainspect
Modular Android APK security analysis framework integrating static, dynamic, and reverse engineering tools for comprehensive vulnerability assessment…
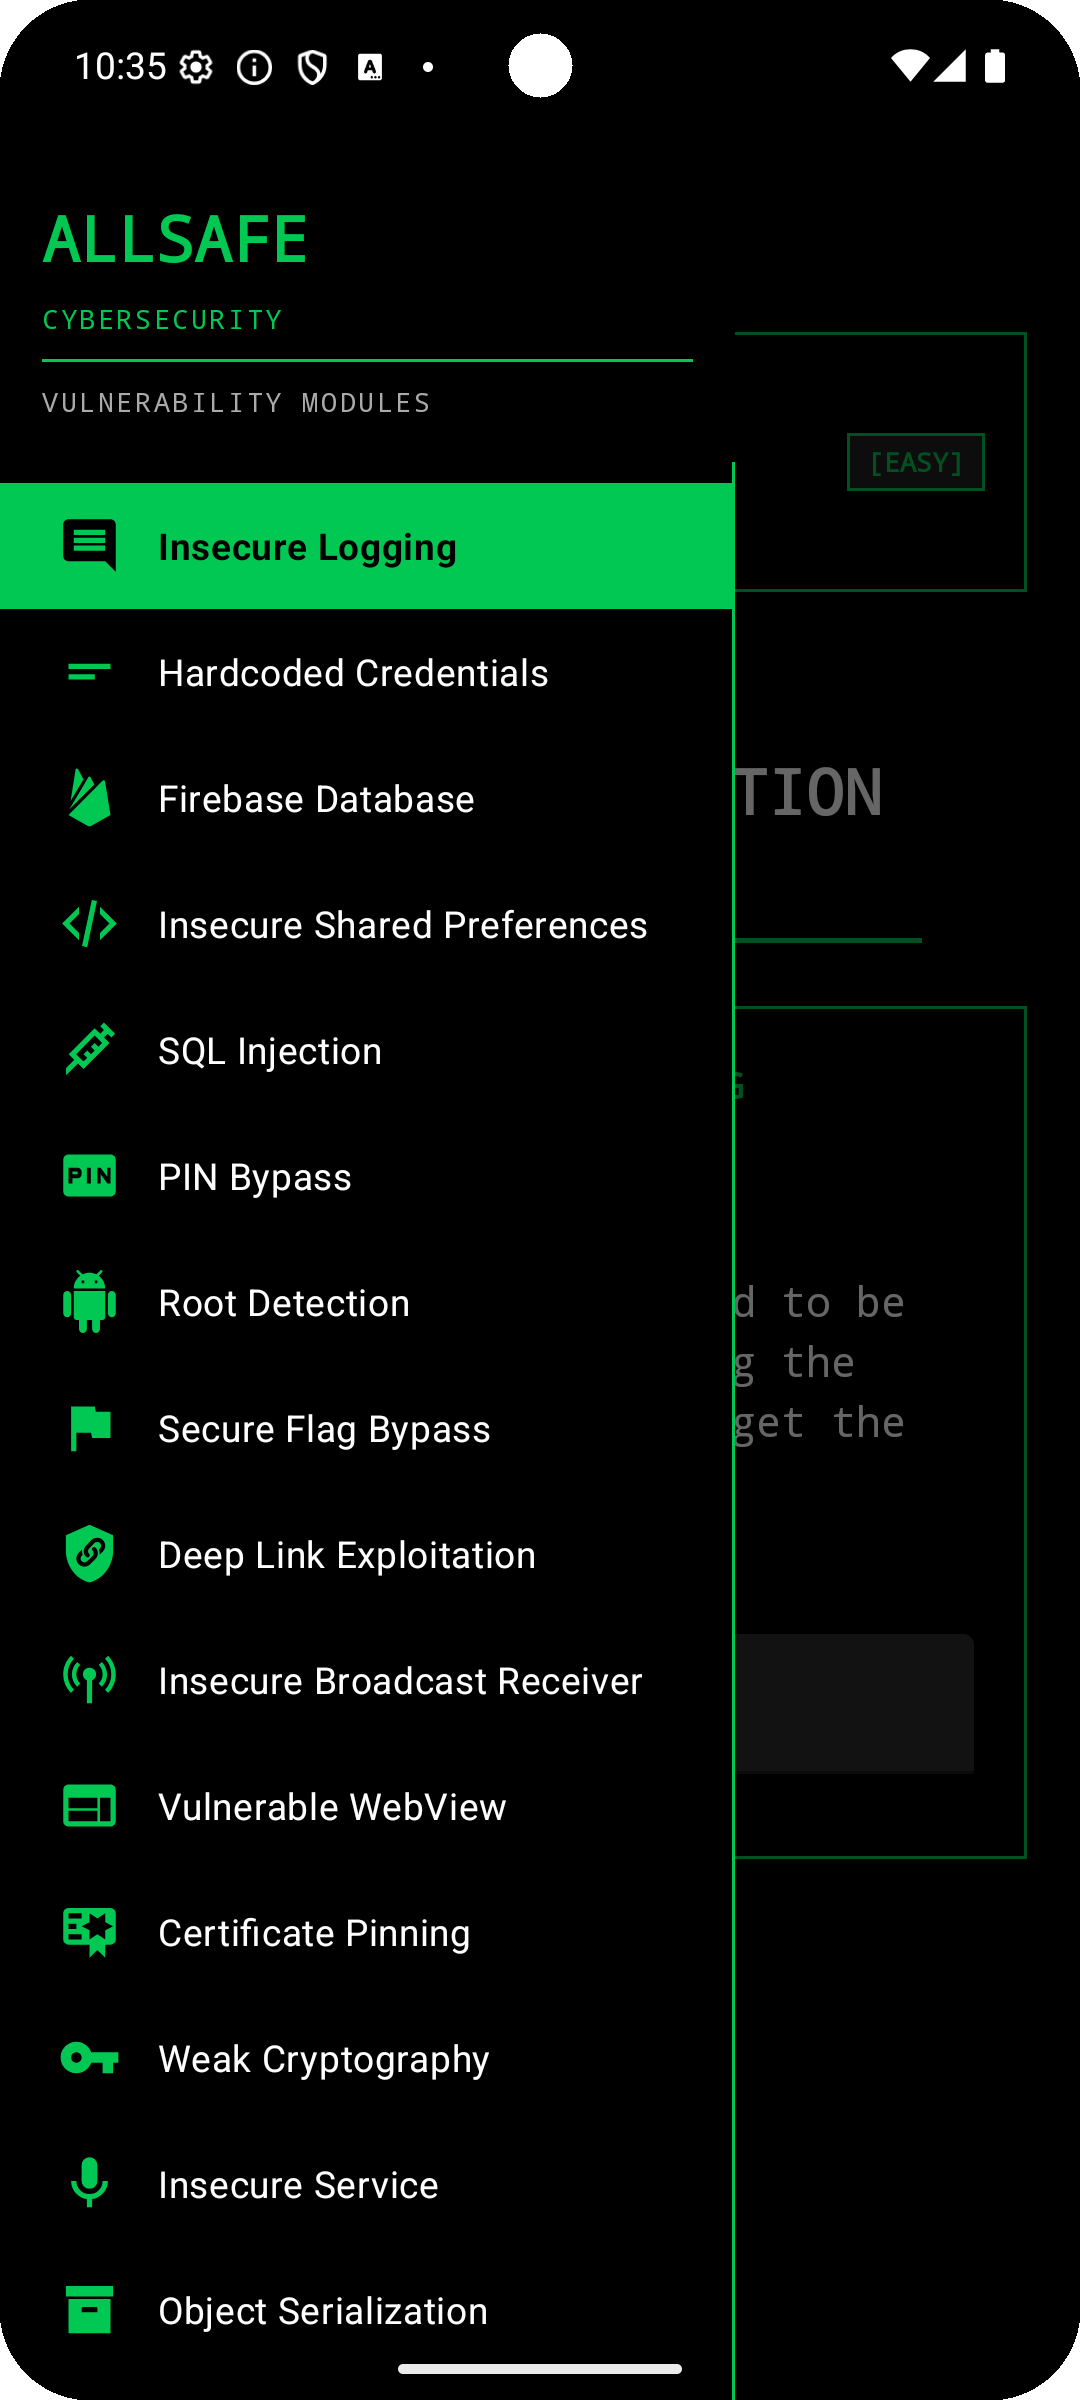 t0thkr1s/allsafe-android
Intentionally vulnerable Android application.
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 logicalhacking/dvhma
Intentionally vulnerable hybrid Android app for security professionals to test tools and techniques, and for developers to learn common hybrid mobile…
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 user1342/obfu-de-scate
Fuzzy comparison tool for deobfuscating Android APKs by identifying renamed functions across versions, generating mapping files and interactive HTML…
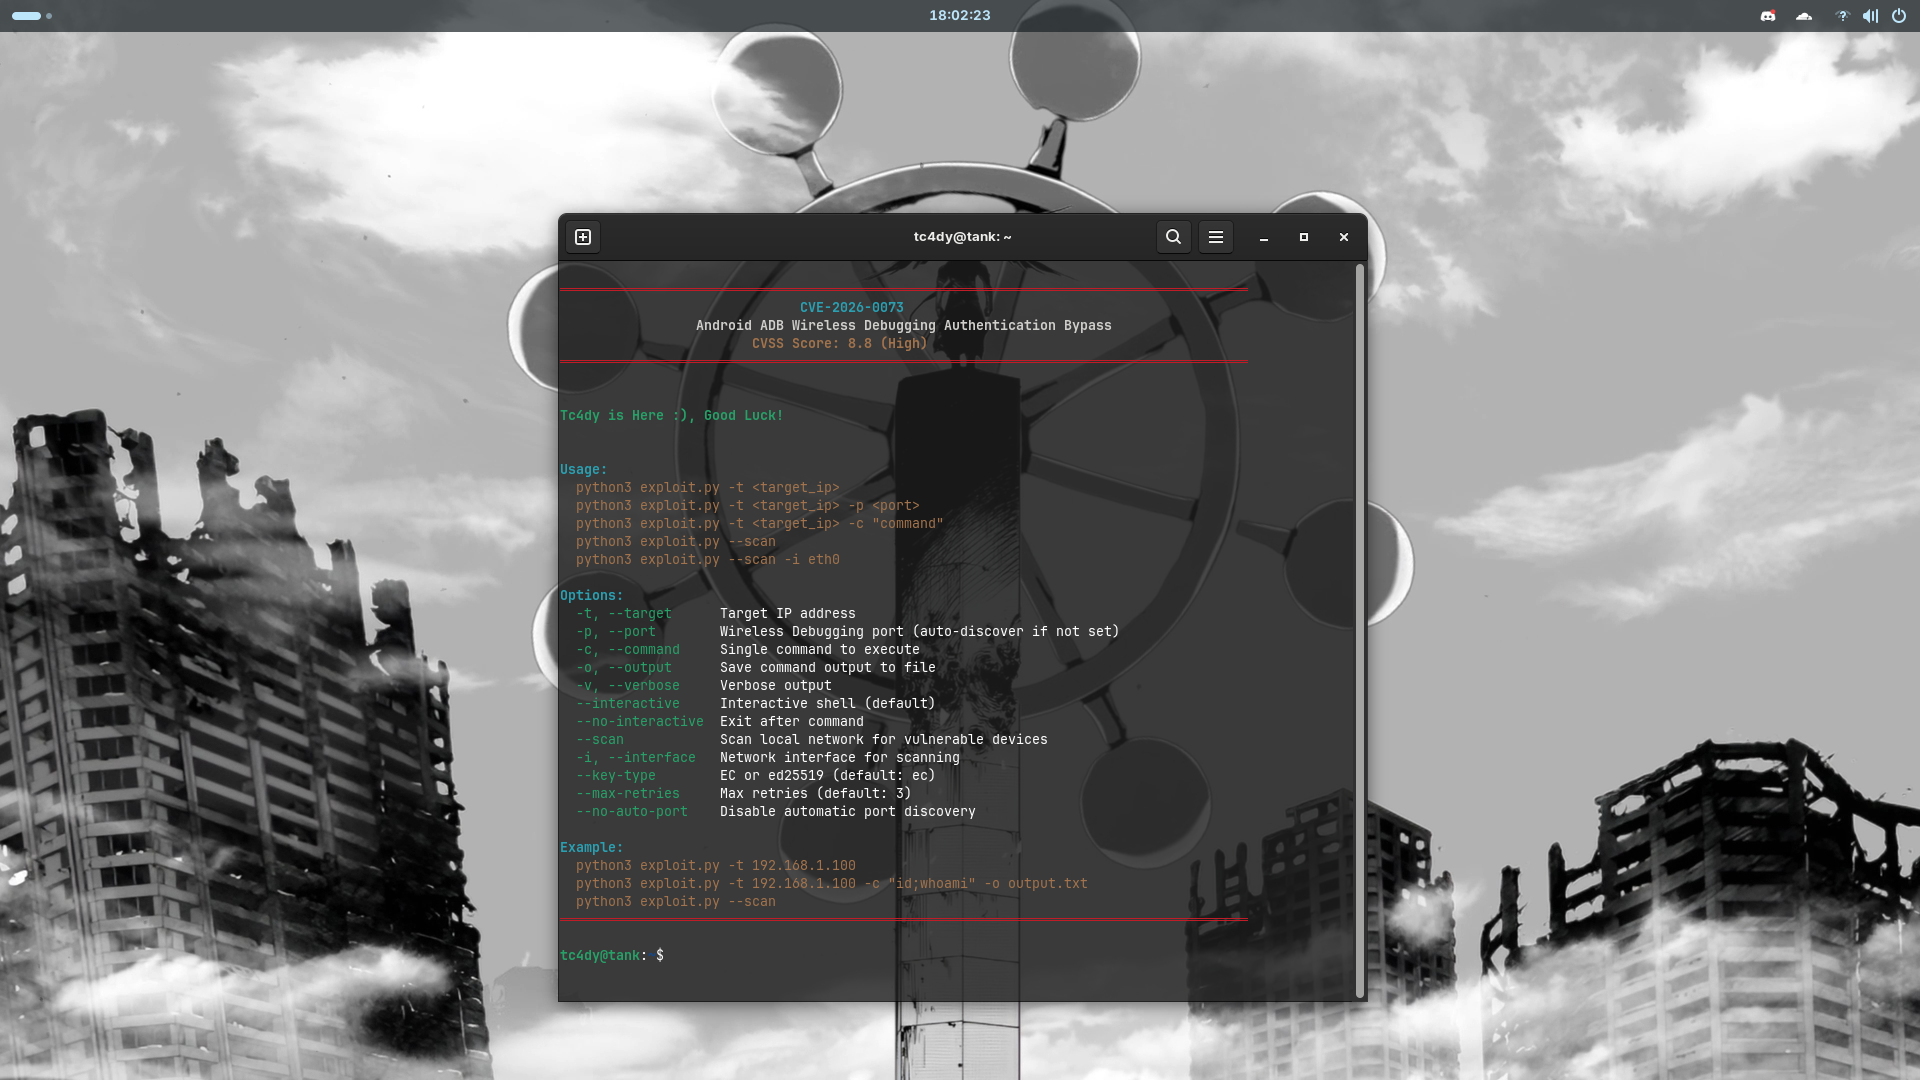 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…