gitlab-cve-2026-85706-ioc

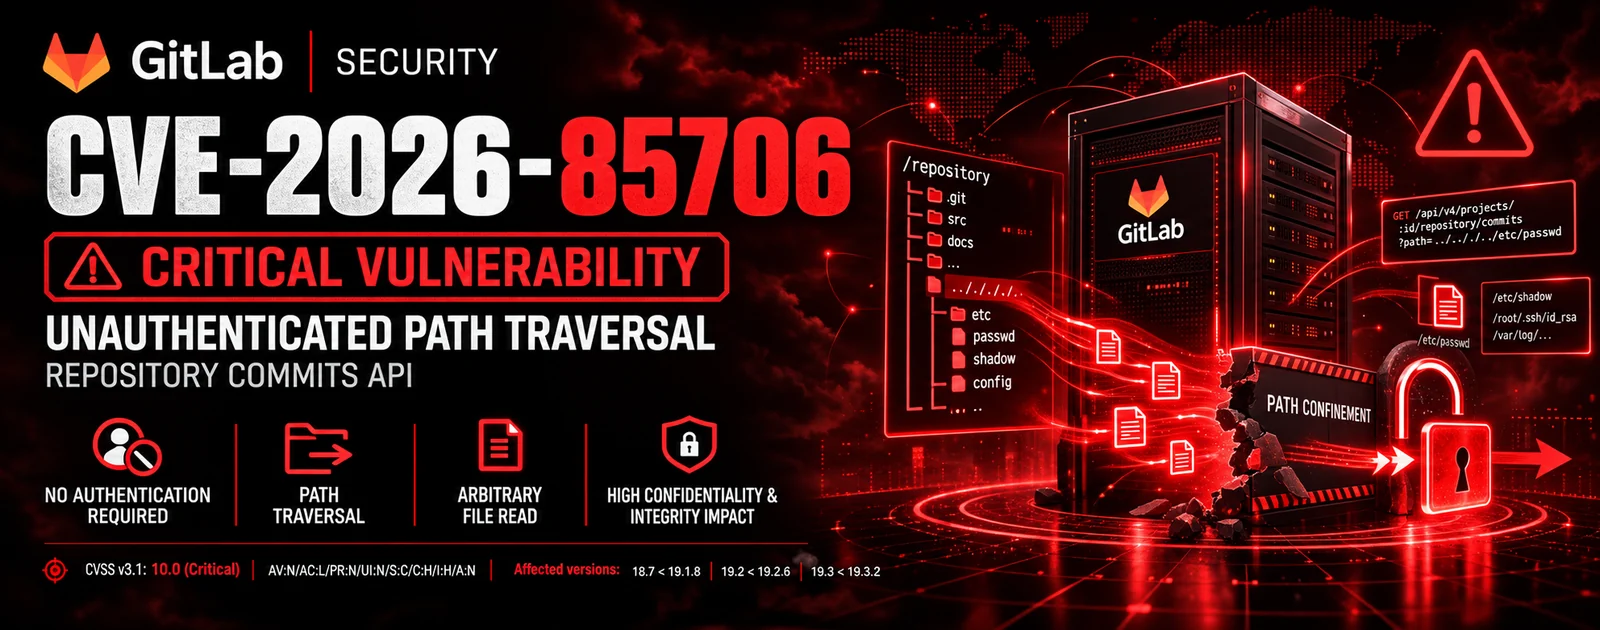
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…

CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…

Find open databases - Powered by Binaryedge.io

CVE-2024-0402 exploit for GitLab Workspaces using a malicious Devfile Registry with path-traversal archive to overwrite authorized_keys and gain SSH…

Reproducible A/B lab + safe PoC for GitLab CVE-2026-19478 / CVE-2026-19650 (GraphQL @gl_introduced)

Exploit for GitLab CVE-2021-22205 Unauthenticated Remote Code Execution

Exploit for "GitLab Instance" Arbitrary server file read vulnerability

Exploit for GitLab account takeover via CVE-2023-7028, demonstrating password reset bypass by injecting attacker email to receive reset token.

Exploit for GitLab CVE-2023-7028: password reset bypass via dual email verification, allowing unauthorized account takeover. Includes affected…

Unauthenticated remote code execution exploit for GitLab 13.10.2 targeting CVE-2021-22205, enabling arbitrary command execution on vulnerable…

Proof-of-concept exploit for GitLab stored XSS (CVE-2022-1175) enabling personal access token theft and account takeover via malicious issue comments.

authenticated arbitrary file read for Gitlab (CVE-2020-10977)

Unauthenticated remote code execution exploit for GitLab versions < 13.10.3, leveraging ExifTool DjVu annotation parsing to execute arbitrary…

Curated Semgrep rule repository for GitLab SAST, providing static analysis patterns to detect security vulnerabilities across multiple programming…

Generates reverse shell payloads targeting the GitLab-shell vulnerability CVE-2024-32002 for exploitation testing.

PoC in single line bash

Python exploit script for CVE-2021-22205 (GitLab RCE) with command execution and reverse shell capabilities. Supports one-click getshell for…

Python toolkit for CVE-2026-85706 GitLab unauth file read: weaponized exploit with loot, shell, mass scan, plus non-intrusive SafeChecker audit and…

Provides PoC exploits and root-cause analysis for two GitLab GraphQL `@gl_introduced` directive vulnerabilities: unauthenticated method execution and…