

PCAPdroid
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
android-securitydns-analysiseducation+8
emanuele-f/pcapdroidNo-root network monitor, firewall and PCAP dumper for Android
 bardlaudian/cve-2018-9276
CVE-2018-9276 — PRTG Network Monitor < 18.2.39 Authenticated RCE. For educational purposes and authorized penetration testing only.
 ch-rigu/cve-2020-11547--prtg-network-monitor-information-disclosure
Exploit for CVE-2020-11547: unauthenticated information disclosure in PRTG Network Monitor via crafted HTTP requests to /public/login.htm or…
 cves-labs/cve-2026-21877
Dockerized vulnerable lab environment with a Python-based network monitor and dedicated exploit script, enabling hands-on exploitation, privilege…
 h0j3n/cve-2020-23934
Python exploit script for CVE-2020-23934, achieving authenticated remote code execution on PRTG Network Monitor via crafted multipart form-data…
 andyfeili/cve-2018-9276
Exploit code for CVE-2018-9276, a privilege escalation vulnerability in PRTG Network Monitor, providing proof-of-concept implementation.
 alperenugurlu/network_assessment
With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
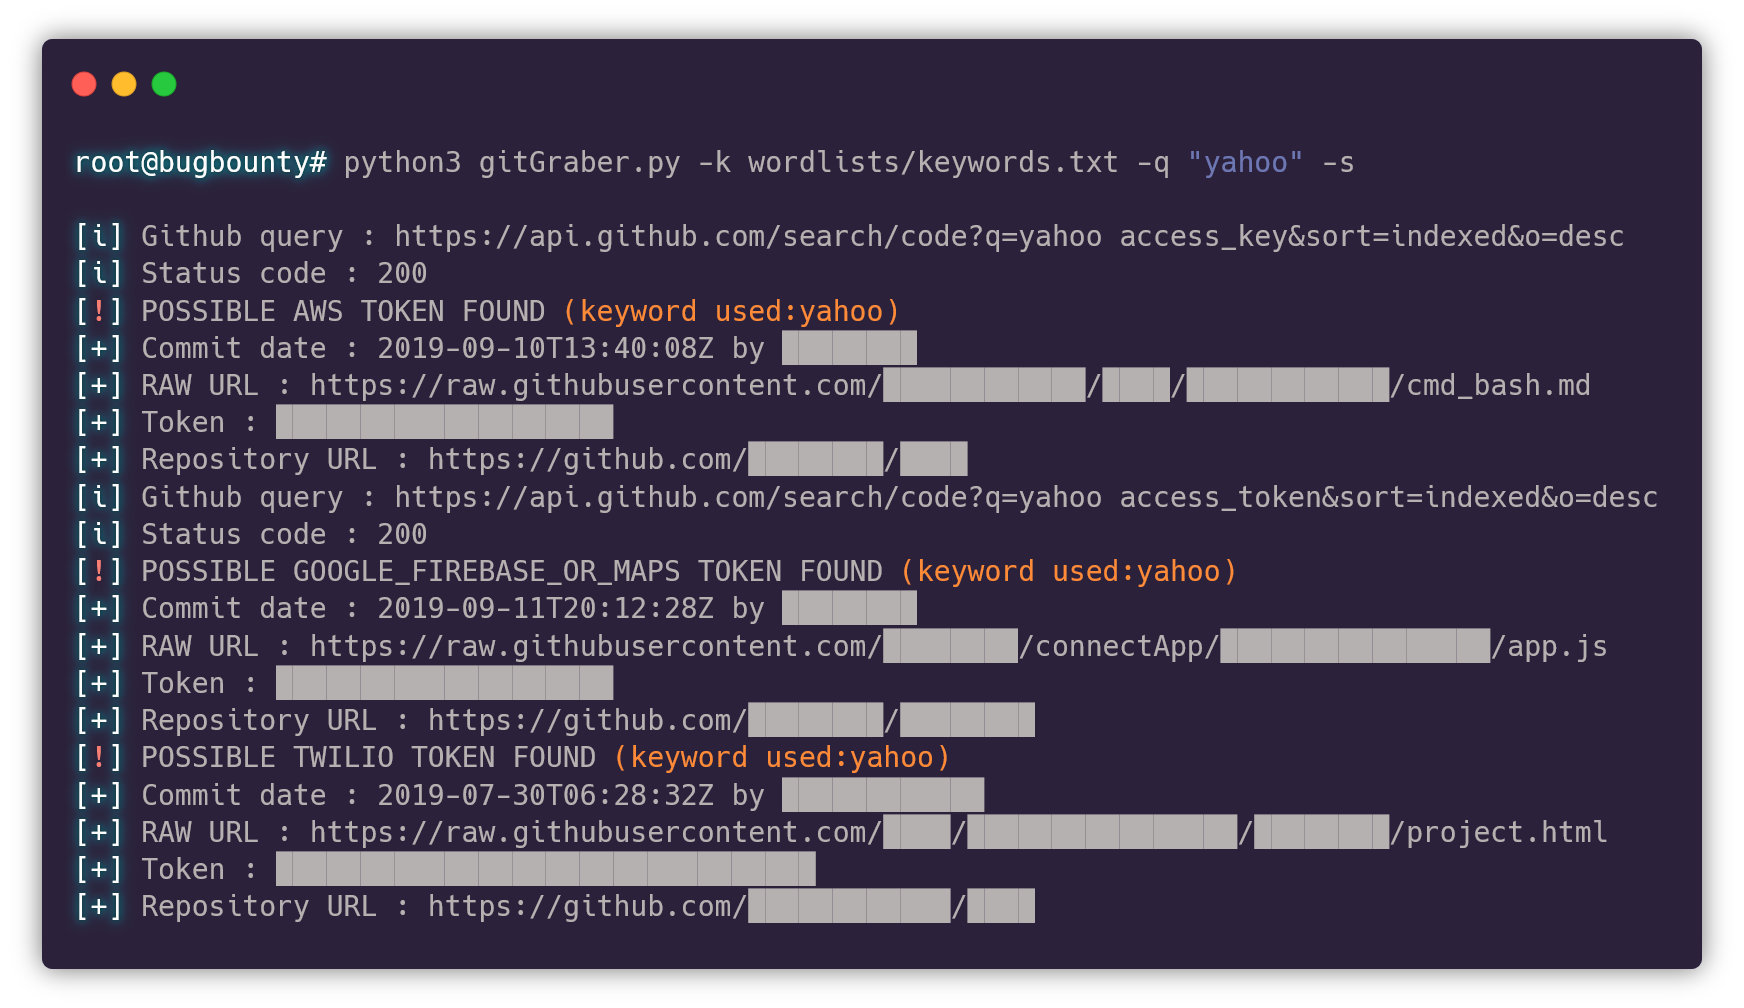 hisxo/gitgraber
gitGraber: monitor GitHub to search and find sensitive data in real time for different online services such as: Google, Amazon, Paypal, Github,…
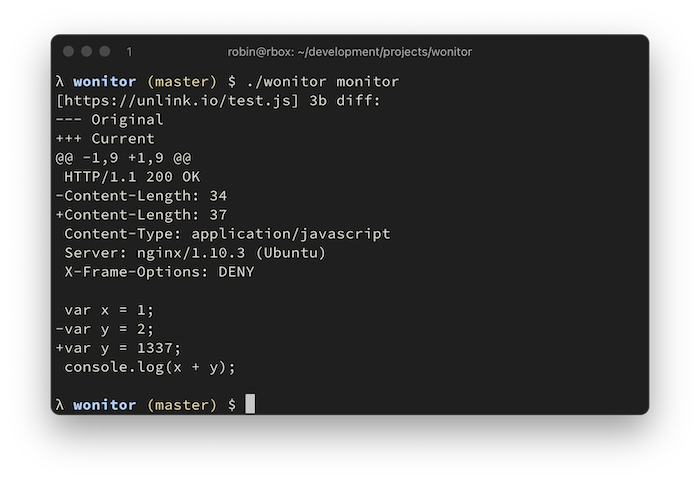 rverton/wonitor
fast, zero config web endpoint change monitor
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 asvorg/cve-2026-105030-poc
A python3 PoC for CVE-2026-105030 Kener 4.0.0 before 4.1.6 Hidden Monitor Data Disclosure via Dashboard API
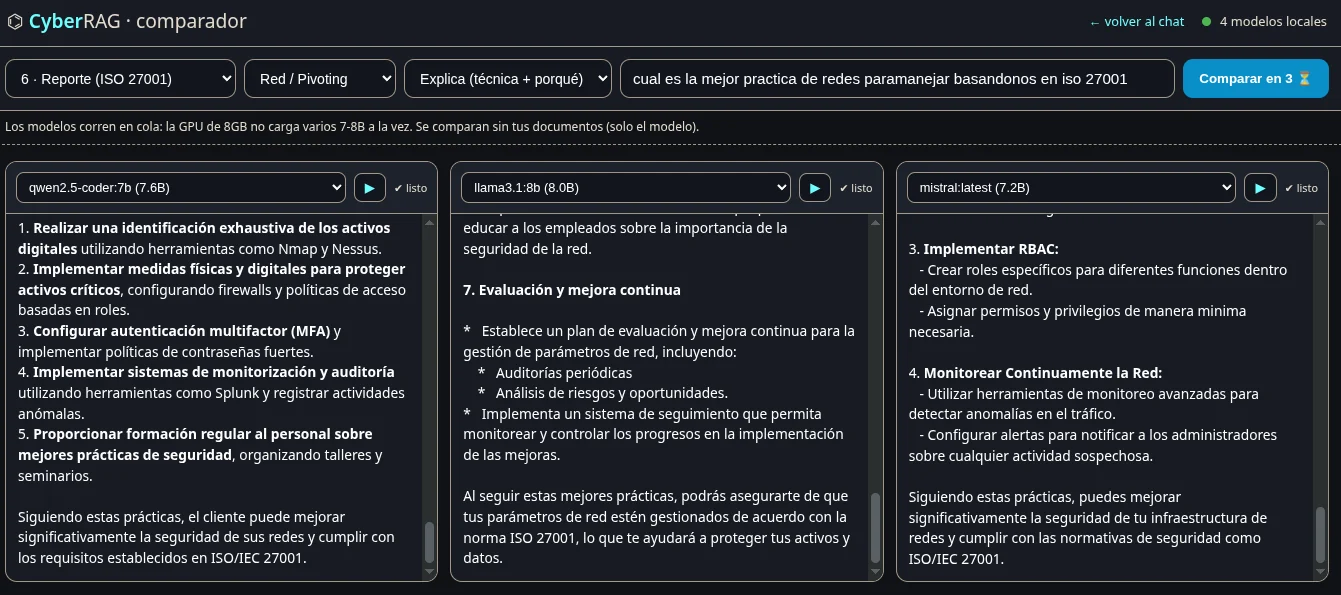
 rdelasierra-uy/rag-seguridad
CyberRAG — RAG 100% local (Ollama) sobre apuntes y libros de ciberseguridad: recuperación híbrida, respuestas con citas, asistente de pentest por…
 pry0cc/bluekeeptracker
My bot (badly written) to search and monitor cve-2019-0708 repositories
 jcarabantes/cve-2024-54820
Proof-of-concept for an unauthenticated SQL injection vulnerability in XOne Web Monitor that allows credential dumping and data extraction via…
 mr-r3b00t/cve-2026-0300
Deceptive honeypot designed to simulate and monitor exploitation attempts targeting CVE-2026-0300, capturing attacker behavior for analysis and…
 griisemine/cve-2024-56331
Proof-of-concept exploit for CVE-2024-56331, demonstrating Local File Inclusion in Uptime Kuma via improper URL handling in the real-browser monitor.…
 randomrobbiebf/cve-2022-45354
Download Monitor <= 4.7.60 - Sensitive Information Exposure via REST API