
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
23 results
ParrotNG preview

ParrotNG

GitHubikkisoft/parrotng

Java-based tool to detect Adobe Flex SWF files vulnerable to CVE-2011-2461, usable as a command-line utility or Burp Suite passive scanner plugin.
exploitationpenetration-testingstatic-analysis+3
48
11 years ago
BlackWidow preview

BlackWidow

GitHub1n3/blackwidow

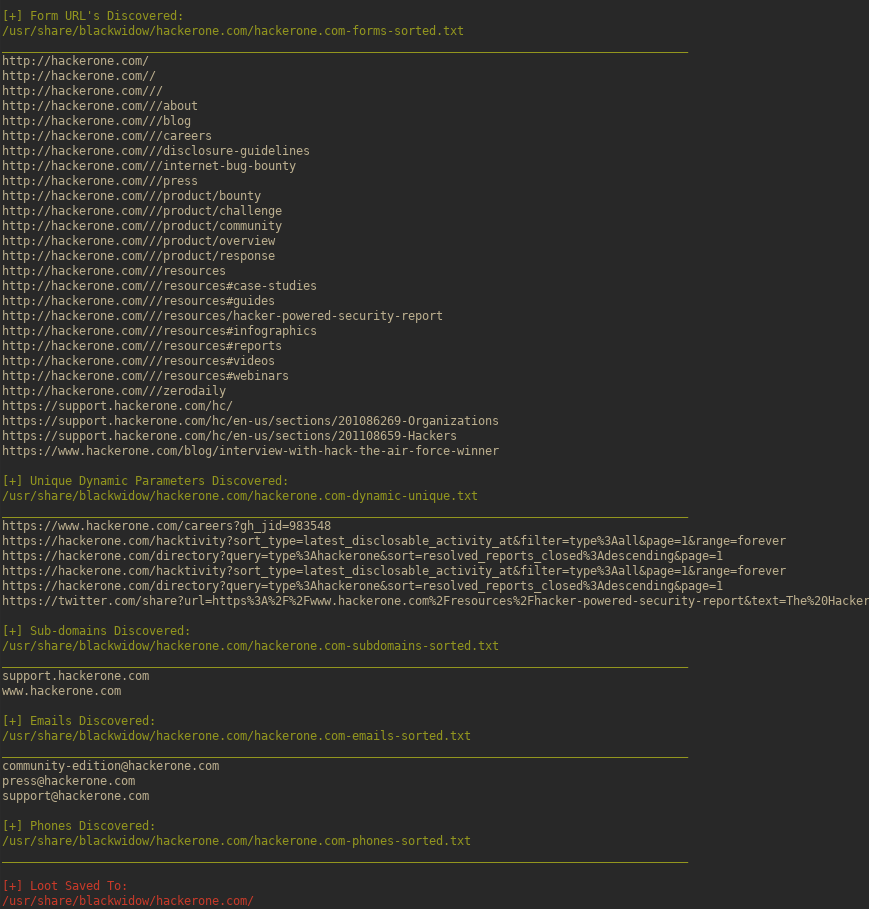
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
fuzzinginformation-gatheringosint+3
1.8k5 months ago
cve-2026-1731-scanner preview

cve-2026-1731-scanner

GitHubcybrdude/cve-2026-1731-scanner

Passive vulnerability scanner for CVE-2026-1731 — BeyondTrust RS/PRA pre-auth RCE (CVSS 9.9). Educational & defensive use only.
defensive-toolseducationinformation-gathering+5
47 months ago
CVE-2026-103752-Authorizer-Privilege-Escalation preview

CVE-2026-103752-Authorizer-Privilege-Escalation

GitHubanoxhunterdump-ctrl/cve-2026-103752-authorizer-privilege-escalation

Defensive analysis, patch breakdown, and passive detection scanner for CVE-2026-103752 (WordPress Authorizer Plugin <= 3.15.3).
defensive-toolsincident-responsepenetration-testing+3
4 days ago
livewire-vuln-scanner preview

livewire-vuln-scanner

GitHubjenderal92/livewire-vuln-scanner

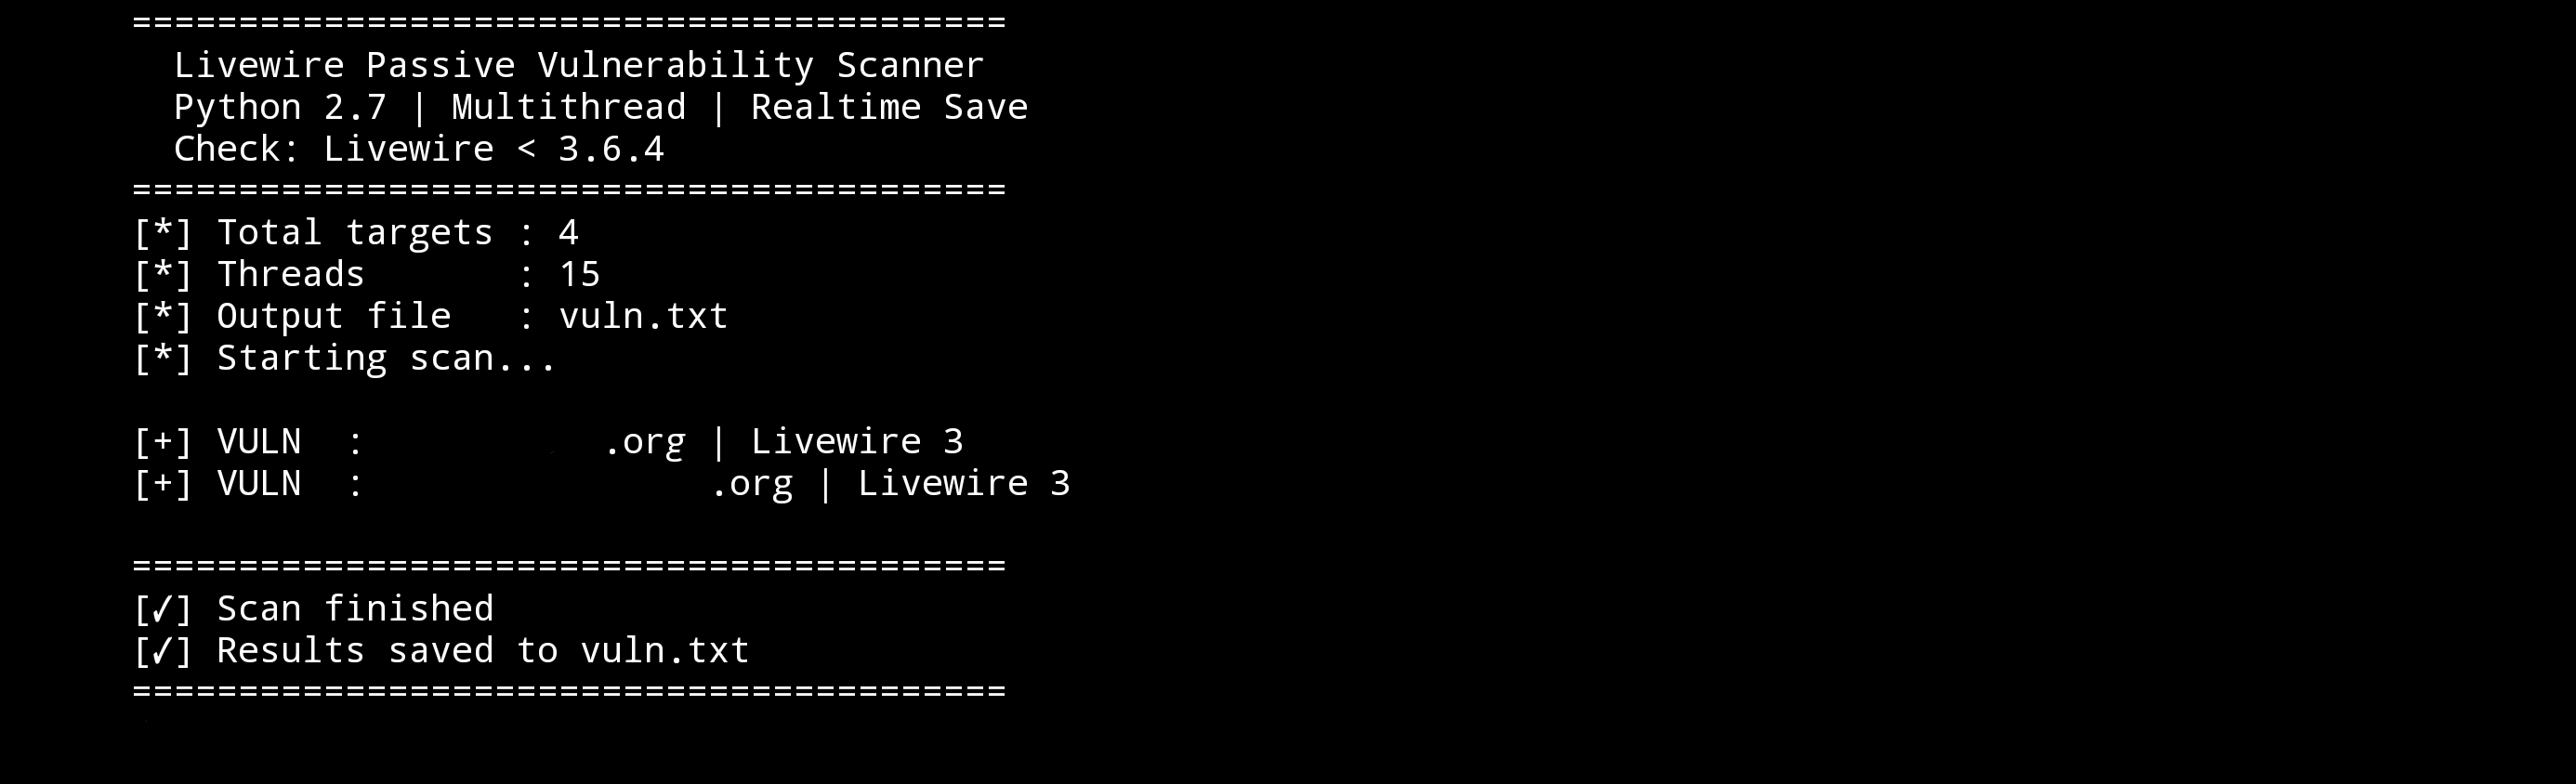
Simple scanner to detect vulnerable Livewire installations.
information-gatheringreconnaissancevulnerability-analysis+3
4 months ago
Recon-Scan preview

Recon-Scan

GitHubaarocy/recon-scan

Recon-Scan: open‑source passive reconnaissance with AI‑powered security analysis. Zero‑touch, developer‑first, and privacy‑focused.

ai-securitydns-analysisdns-subdomain-enumeration+6
78 days ago
CVE-2025-2294 preview

CVE-2025-2294

GitHubromanedutov/cve-2025-2294

YAML-based vulnerability scanner for CVE-2025-2294 with active and passive detection templates, enabling automated exploitation checks against Kubio…

exploitationpenetration-testingvulnerability-analysis+2
1 year ago
Securiscan preview

Securiscan

GitHubvighnesh91/securiscan

Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
ai-securityapi-securityapi-security-testing+8
6 days ago
CVE-2021-40113 preview

CVE-2021-40113

GitHubkarammahmad/cve-2021-40113

CVE documentation repository detailing unauthenticated remote vulnerabilities in Cisco Catalyst PON Series Switches ONT, including default credential…
authenticationconfiguration-auditingexploitation+3
3 years ago
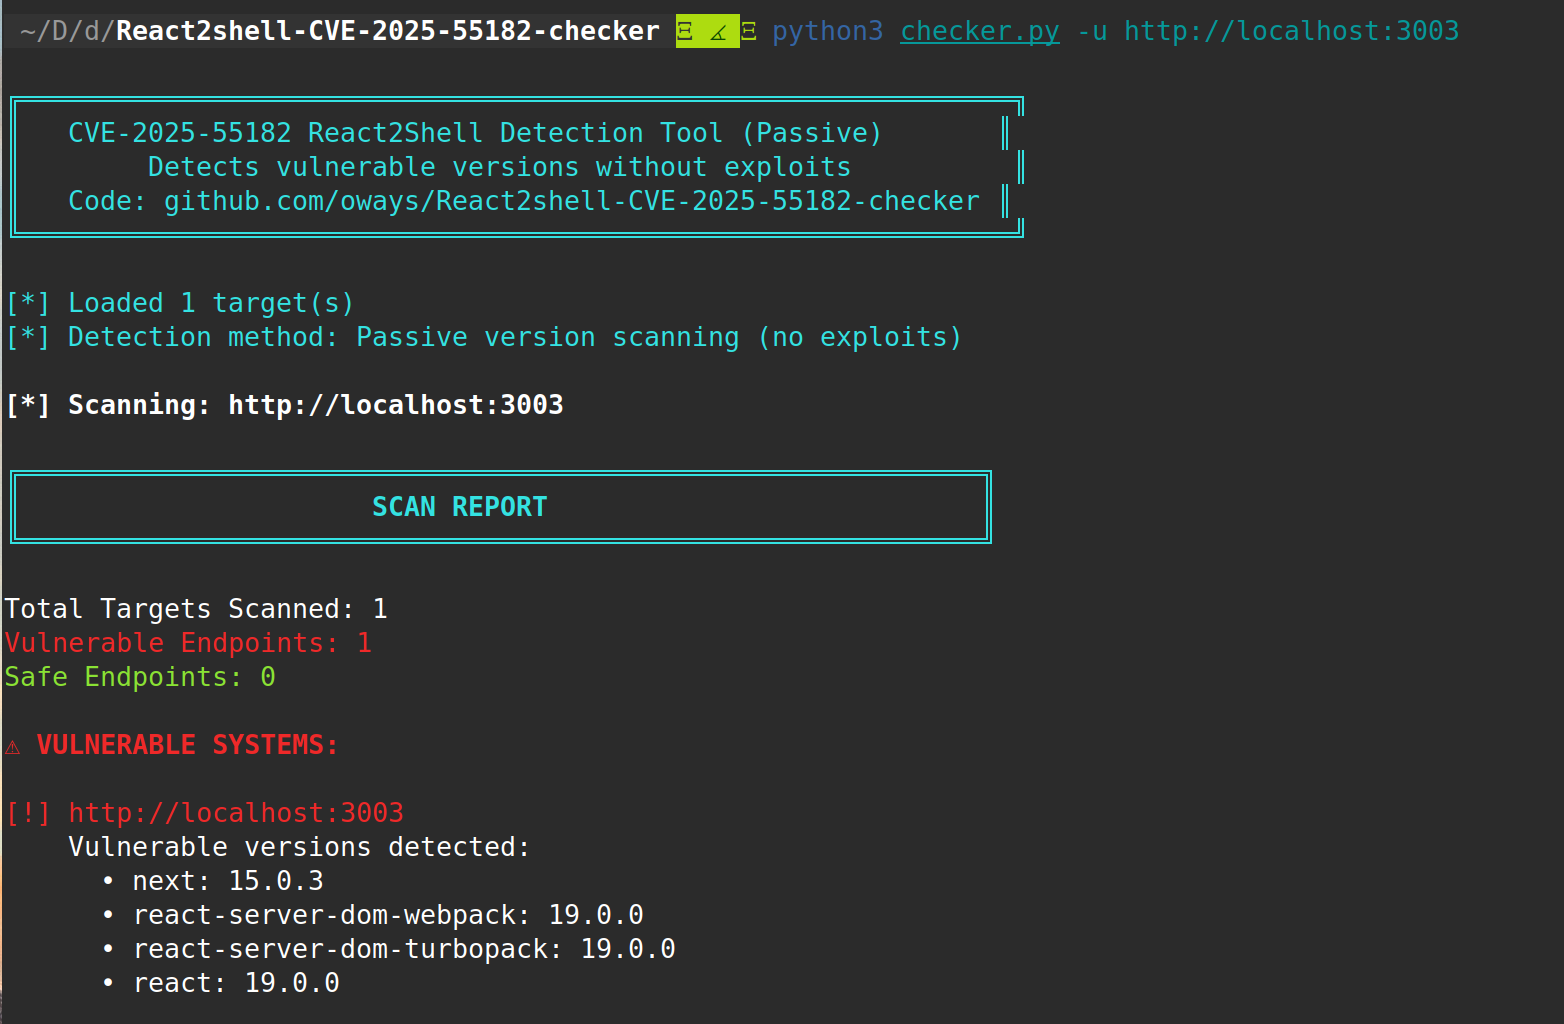
React2shell-CVE-2025-55182-checker preview

React2shell-CVE-2025-55182-checker

GitHuboways/react2shell-cve-2025-55182-checker

Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…
code-analysisdevsecopssupply-chain-security+3
210 months ago
pagodo preview

pagodo

GitHubopsdisk/pagodo

pagodo (Passive Google Dork) - Automate Google Hacking Database scraping and searching
information-gatheringosintreconnaissance+2
3.4k1 year ago
HUNT preview

HUNT

GitHubbugcrowd/hunt

Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
curated-resourcespenetration-testingvulnerability-analysis+3
2.3k1 month ago
karma_v2 preview

karma_v2

GitHubdheerajmadhukar/karma_v2

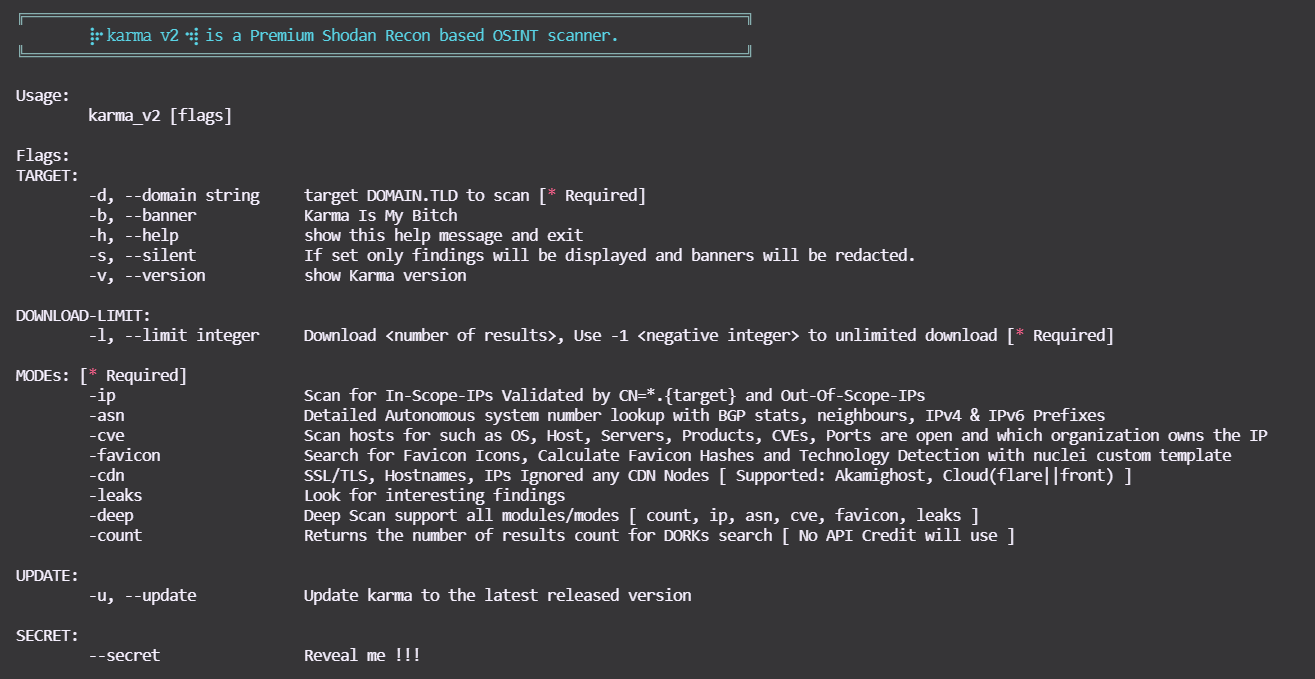
⡷⠂𝚔𝚊𝚛𝚖𝚊 𝚟𝟸⠐⢾ is a Passive Open Source Intelligence (OSINT) Automated Reconnaissance (framework)

crawlerdns-subdomain-enumerationinformation-gathering+4
1.0k2 years ago
ripple20 preview

ripple20

GitHubcorelight/ripple20

A Zeek package for the passive detection of "Ripple20" vulnerabilities in the Treck TCP/IP stack.
anomaly-detectionintrusion-detectioniot-security+3
324 years ago
CVE-2026-18322 preview

CVE-2026-18322

GitHubi3it/cve-2026-18322

Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
exploitationlabs-practicepapers-research+7
1 month ago
CVE-2026-0257-PoC preview

CVE-2026-0257-PoC

GitHubakashsingh0454/cve-2026-0257-poc

Passive, read-only remote detection tool for CVE-2026-0257, an authentication bypass in Palo Alto Networks PAN-OS GlobalProtect. Fingerprints PAN-OS…
information-gatheringnetwork-securitypenetration-testing+3
24 months ago
CVE-2025-58360 preview

CVE-2025-58360

GitHubrxerium/cve-2025-58360

Passive detection for CVE-2025-58360
exploitationpenetration-testingvulnerability-analysis+3
9 months ago
CVE-2021-44228-Apache-Log4j-Rce preview

CVE-2021-44228-Apache-Log4j-Rce

GitHubkannthu/cve-2021-44228-apache-log4j-rce

Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection payloads, WAF bypass techniques, and passive scanning integration for…

exploitationpayload-developmentpenetration-testing+3
4 years ago
Previous12Next