

DeepZero
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
ai-assisted-reversingbinary-analysisfuzzing+3
730
416rehman/deepzeroFind zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 splintersfury/autopiff
Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
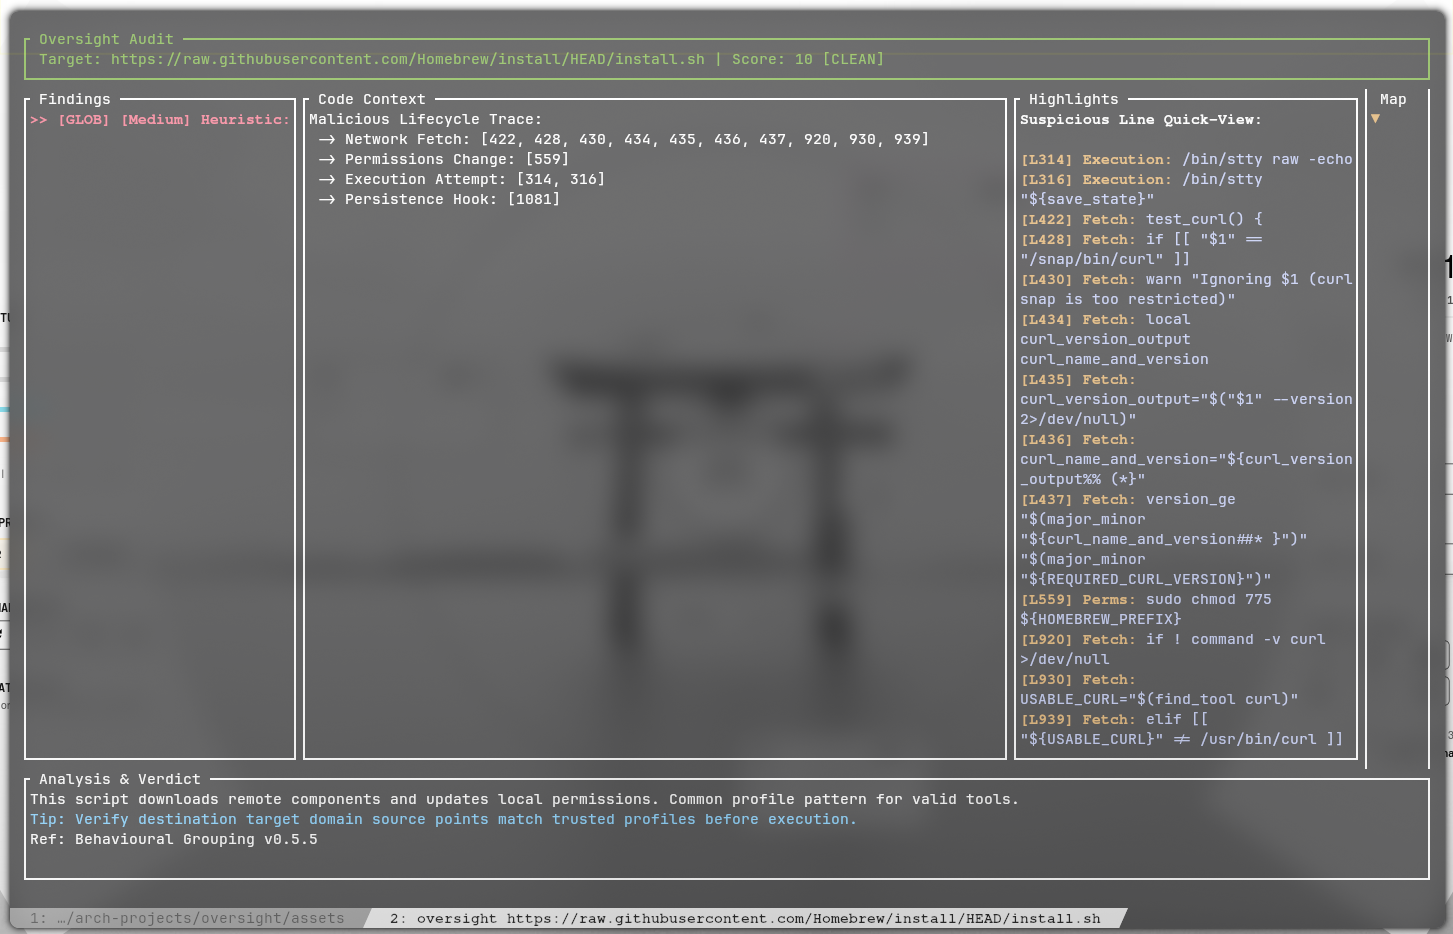 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
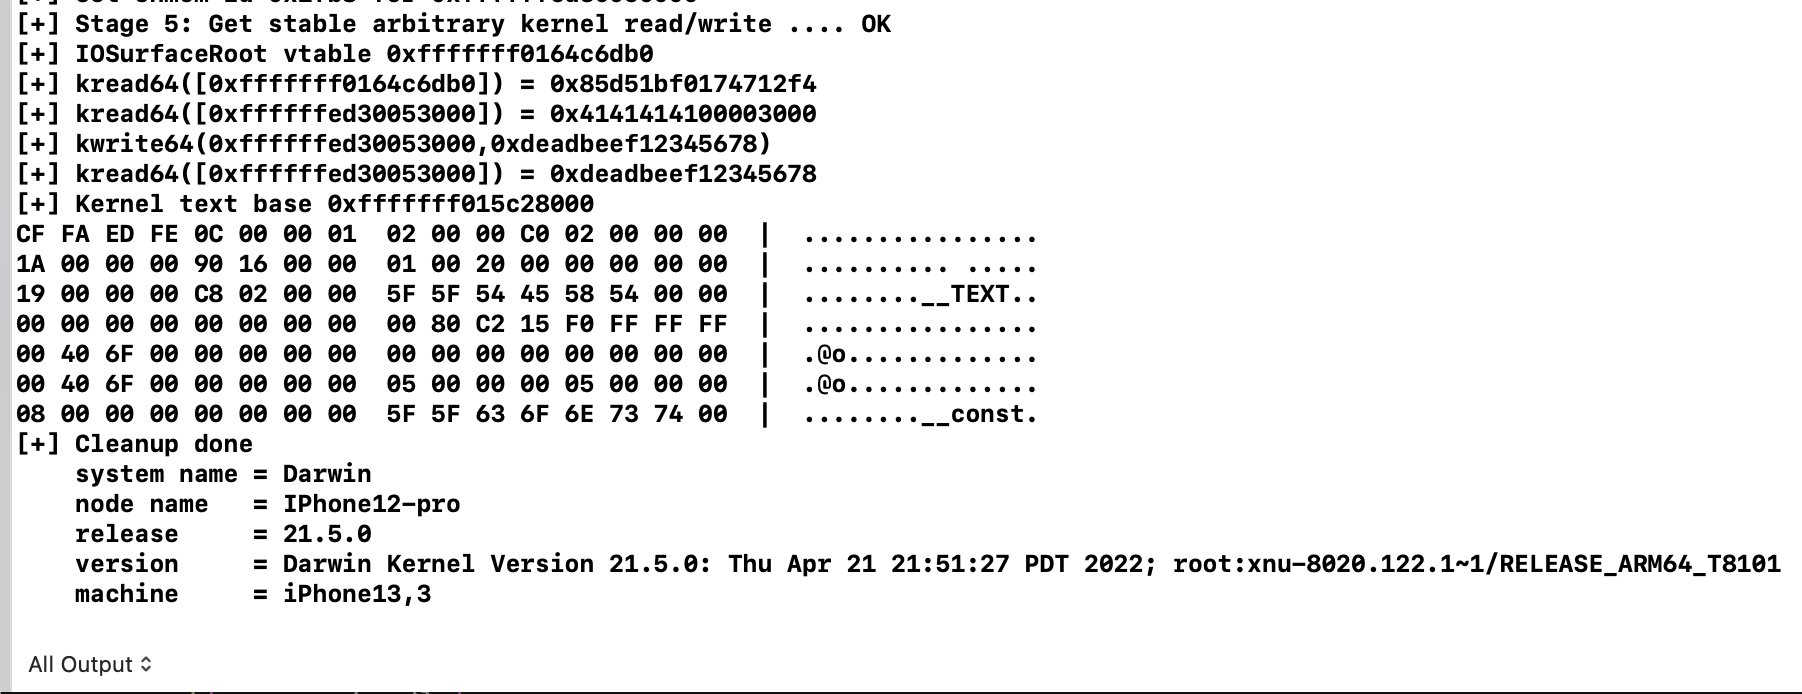 ox1111/cve-2022-32898
Technical analysis and exploit demonstration of CVE-2022-32898, a kernel memory corruption vulnerability in Apple Neural Engine driver, with detailed…
 egkritsis/cve-2025-61303
Critical Vulnerability (9.8) - RecordedFuture Triage dynamic analysis engine can fail to record malicious behavior when samples produce very…
 martinastarone/cve-2026-2441
Detailed proof-of-concept and technical analysis for CVE-2026-2441, a Chrome CSS use-after-free vulnerability enabling sandboxed renderer RCE via…
 prox0959/trueverdict
Zero-dependency Windows PE provenance and false-positive reduction engine (Embedded Authenticode + OS Security Catalogs, Rich Header ROL32…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 day6reak/cve-2014-1773
Technical analysis of CVE-2014-1773, a heap corruption vulnerability in Internet Explorer's MSHTML engine, with detailed crash callstack,…
 day6reak/cve-2014-4109
Proof-of-concept exploit for a use-after-free vulnerability in Internet Explorer's MSHTML engine, triggered via a crafted URL and documented with…
 misterdengi/cve-2026-1801c
Static reverse-engineering analysis of movement input heuristics in Source 2 engine, identifying structural edge cases in input automation and jump…
 openrce/sulley
A pure-python fully automated and unattended fuzzing framework.
 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…

 runreveal/sigmalite
Go library for parsing and executing Sigma detection rules against log entries, supporting field modifiers, CIDR matching, and custom field resolvers…