
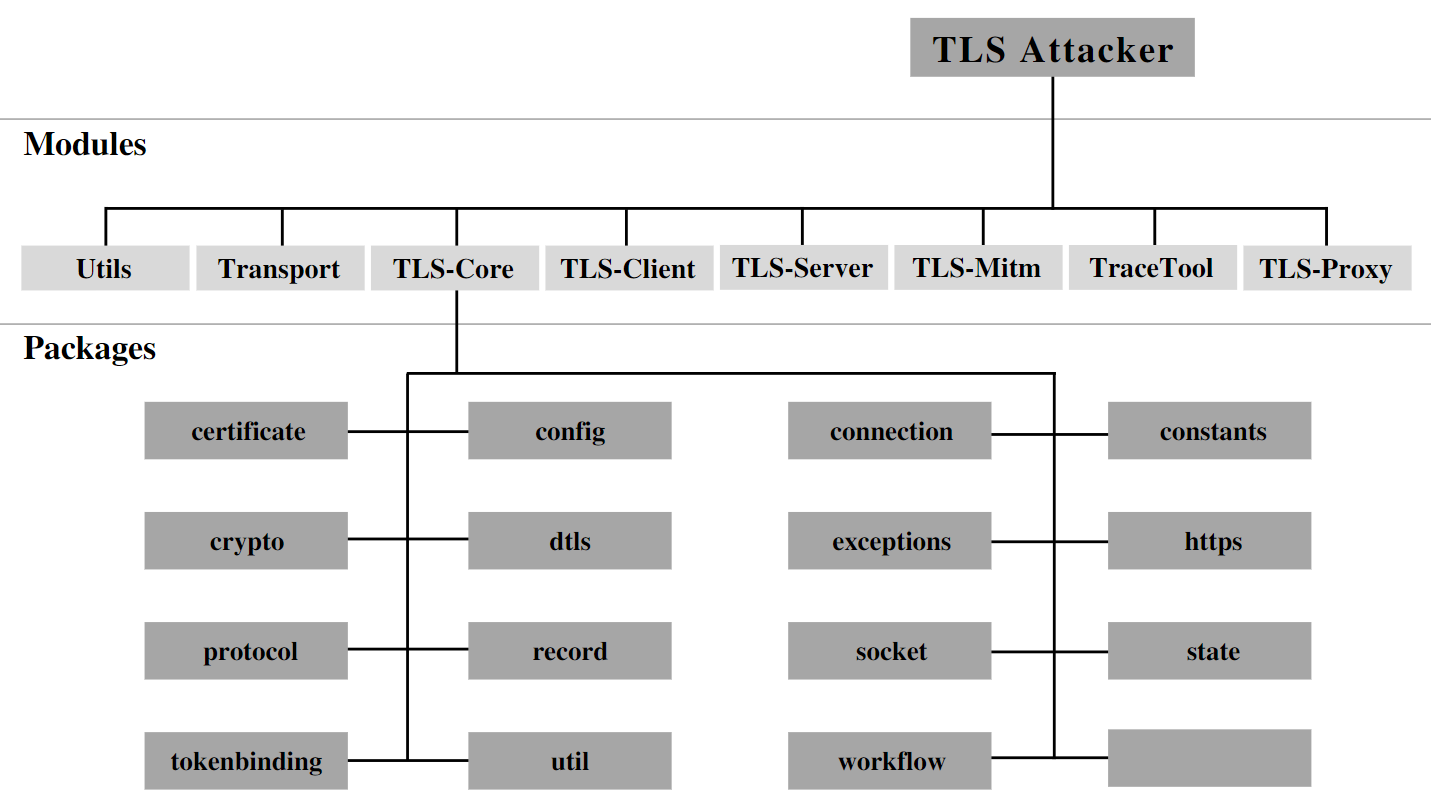
TLS-Attacker
 tls-attacker/tls-attacker
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
cryptographyfuzzingnetwork-security+2
879
tls-attacker/tls-attackerJava-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
 purs3lab/argus
Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
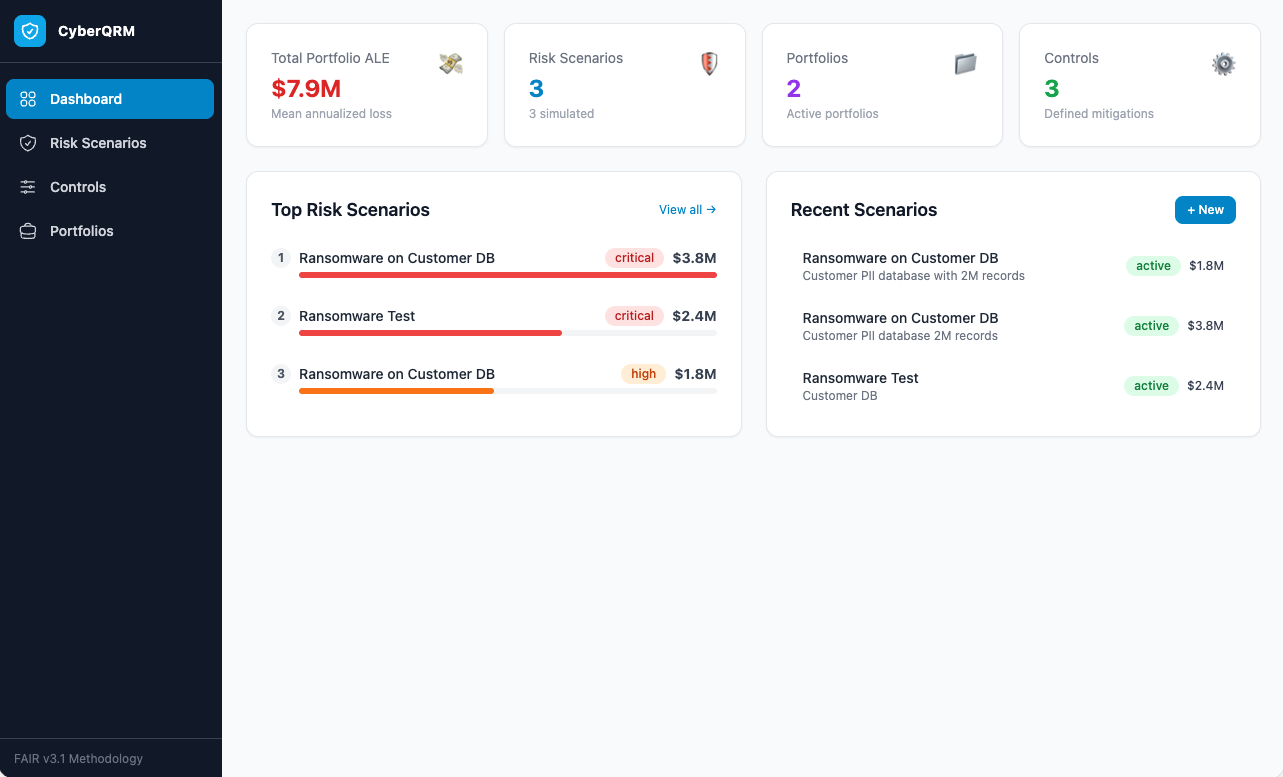 iiamit/cyberqrm
An implementation of the FAIR CRQ Framework
 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
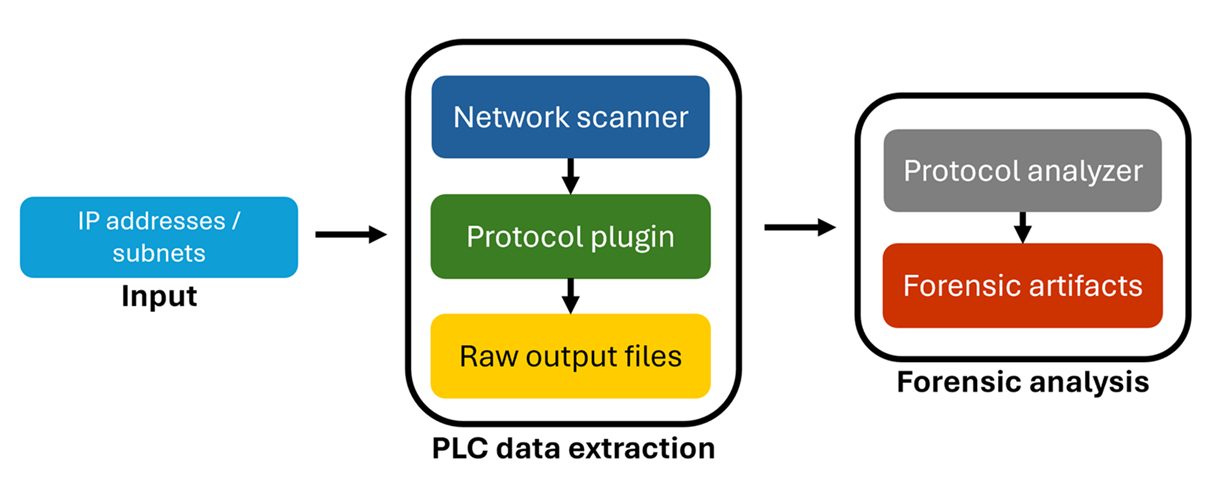 microsoft/ics-forensics-tools
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
 epicosy/jooby
Exploit toolkit targeting CVE-2019-15477 in the Jooby micro web framework, enabling vulnerability analysis and exploitation of Java/Kotlin web…
 pr0v3rbs/firmae
Towards Large-Scale Emulation of IoT Firmware for Dynamic Analysis
 morpheuslord/quadrainspect
Modular Android APK security analysis framework integrating static, dynamic, and reverse engineering tools for comprehensive vulnerability assessment…
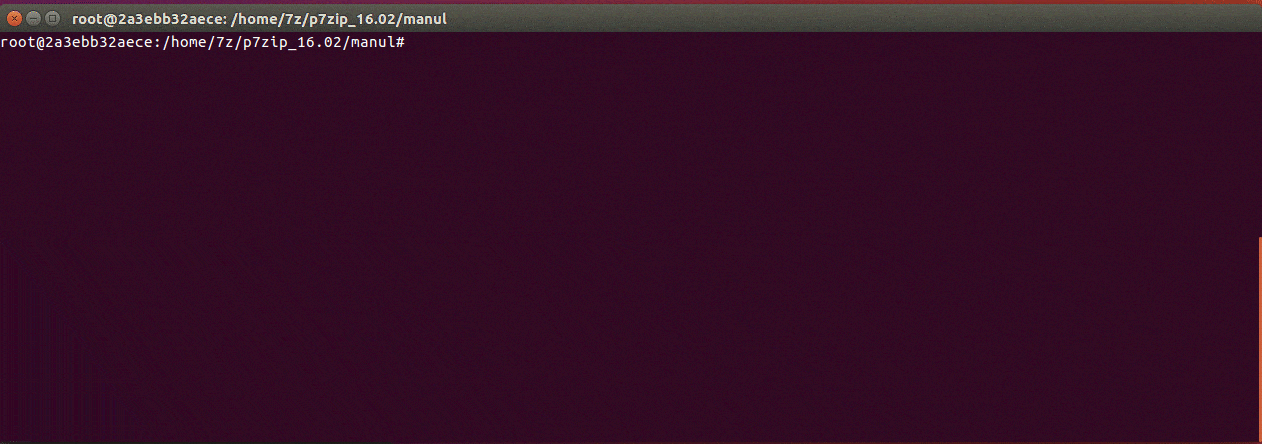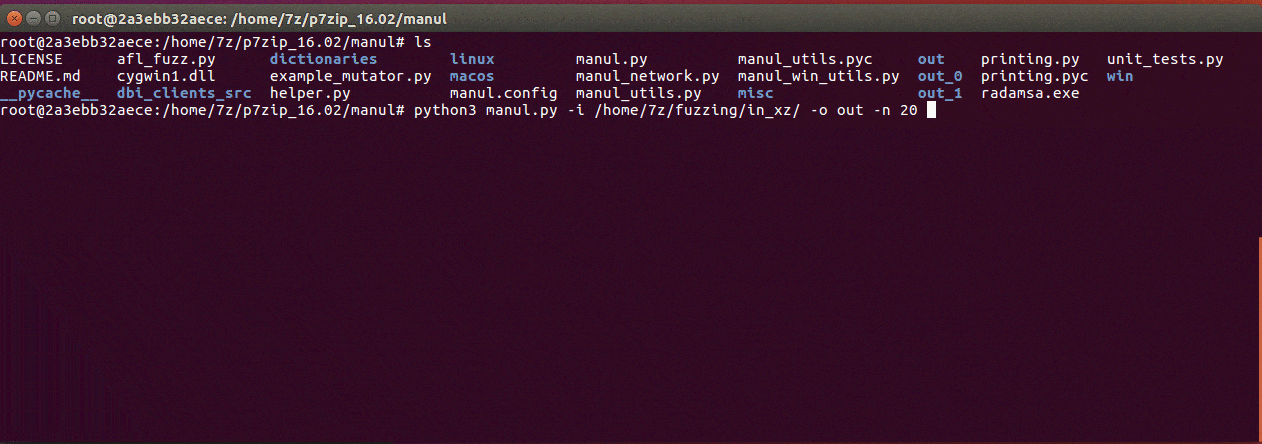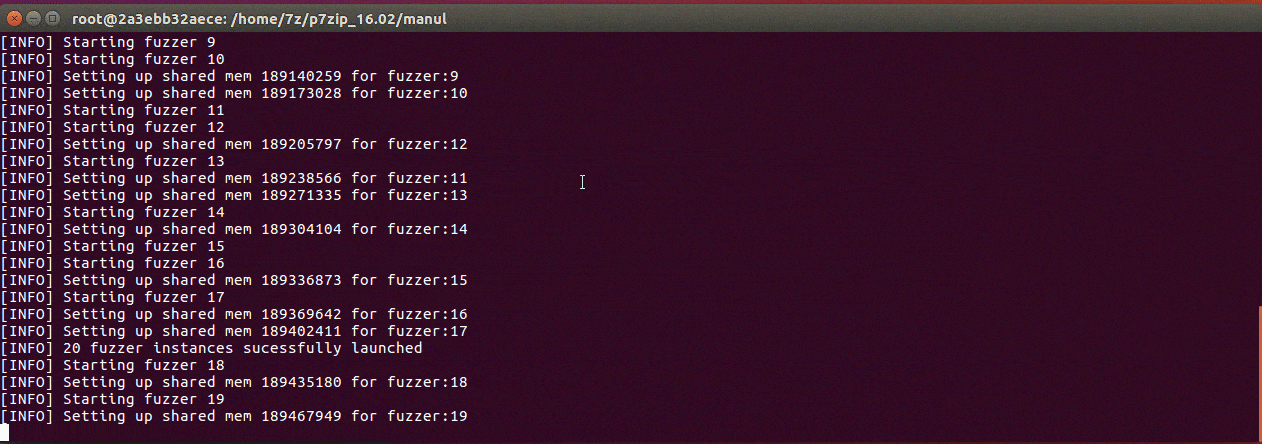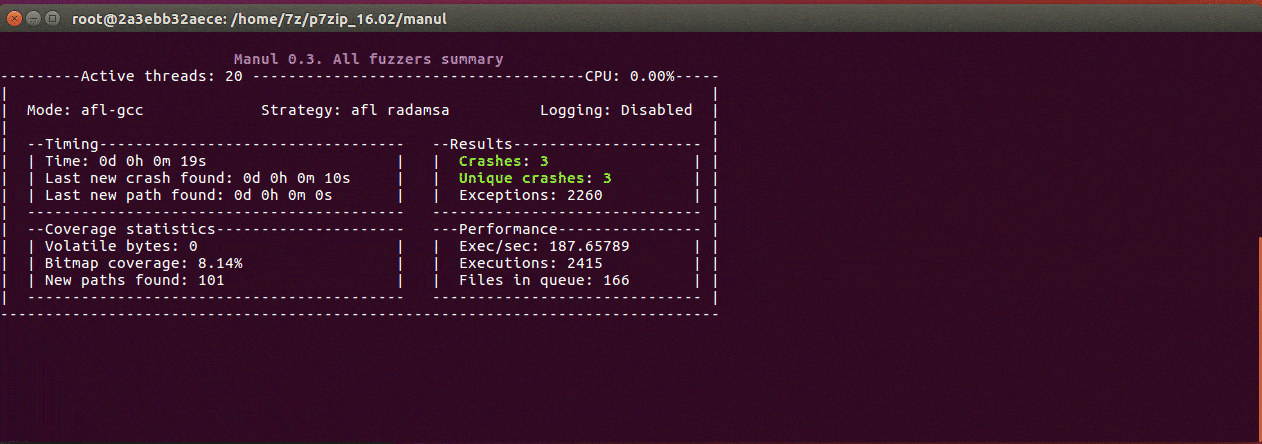 mxmssh/manul
Manul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
 cved-sources/cve-2018-15473
Docker-based vulnerable environment for CVE-2018-15473 exploitation, part of the Cved framework for managing and testing against known…
 cved-sources/cve-2018-15961
Docker container for CVE-2018-15961, part of the Cved framework for managing and testing vulnerable Docker environments in security labs.
 cved-sources/cve-2018-7600
Docker container for CVE-2018-7600 (Drupalgeddon2) vulnerability exploitation, part of the Cved framework for managing vulnerable Docker environments…
 cved-sources/cve-2018-9208
Docker container exploit for CVE-2018-9208, part of the Cved framework for managing and testing vulnerable containers in security labs.
 cved-sources/cve-2016-6515
Docker container providing a vulnerable environment for CVE-2016-6515 exploitation, part of the Cved framework for managing and testing against known…