
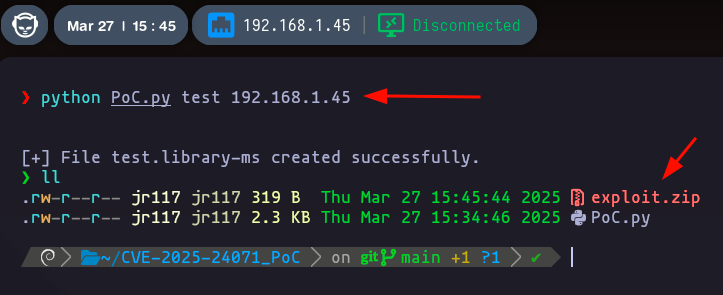
CVE-2025-24071_PoC
 marcejr117/cve-2025-24071_poc
A PoC of CVE-2025-24071 / CVE-2025-24054, A windows vulnerability that allow get NTMLv2 hashes
exploitationinformation-gatheringpassword-cracking+2
25
marcejr117/cve-2025-24071_pocA PoC of CVE-2025-24071 / CVE-2025-24054, A windows vulnerability that allow get NTMLv2 hashes
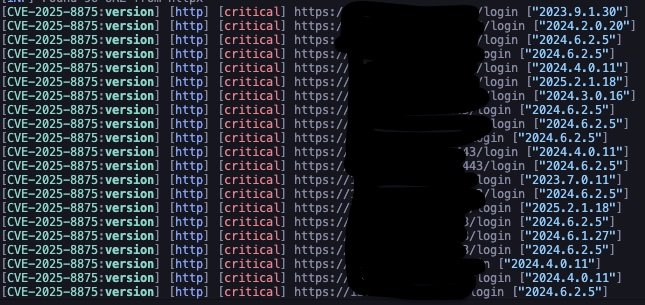 rxerium/cve-2025-8875-cve-2025-8876
Detection for CVE-2025-8875 & CVE-2025-8876
 rxerium/cve-2025-52691
Detection for CVE-2025-52691
 demining/bluetooth-attacks-cve-2025-27840
Bitcoin Cryptanalysis: CVE-2025-27840 Vulnerability in ESP32 Microcontrollers Puts Billions of IoT Devices at Risk via Wi-Fi & Bluetooth
 stackoverflowexcept1on/cve-2021-36393
Error-based blind SQL injection with bit-shifting approach for Moodle 3.10.4
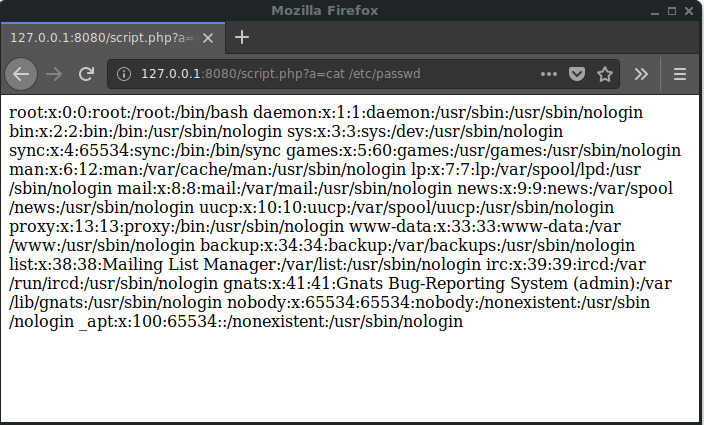 ypereirareis/docker-cve-2019-11043
Docker image and commands to check CVE-2019-11043 vulnerability on nginx/php-fpm applications.
 candisexterior171/cve-2026-57827
Demonstrate the unauthenticated remote code execution vulnerability in the RSFiles! Joomla component through an arbitrary file upload.
 kh4sh3i/cve-2023-22515
CVE-2023-22515 - Broken Access Control Vulnerability in Confluence Data Center and Server
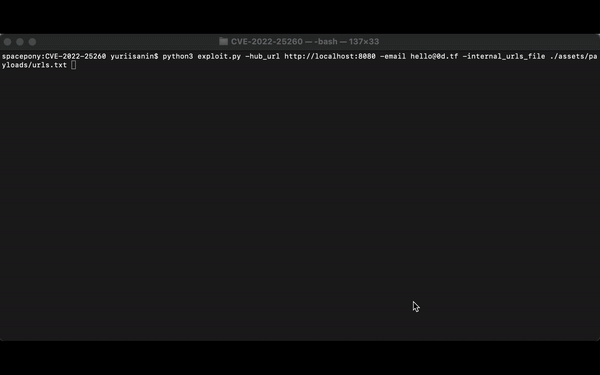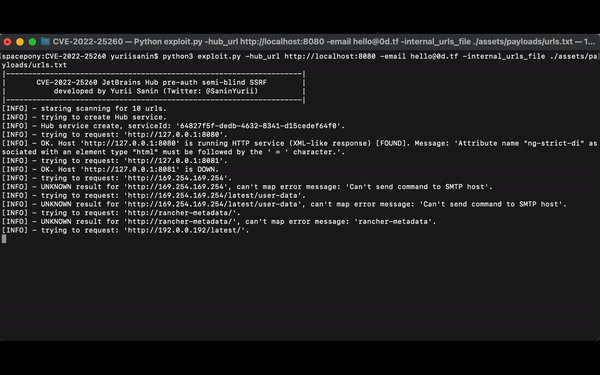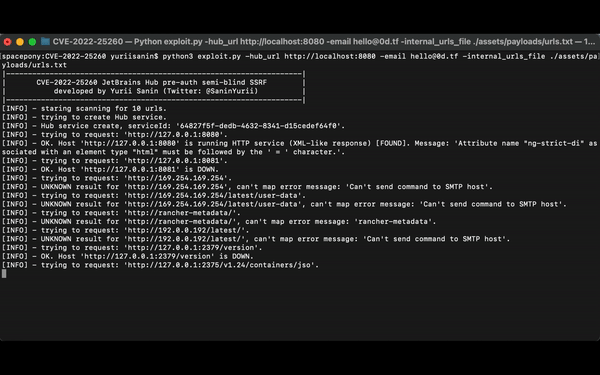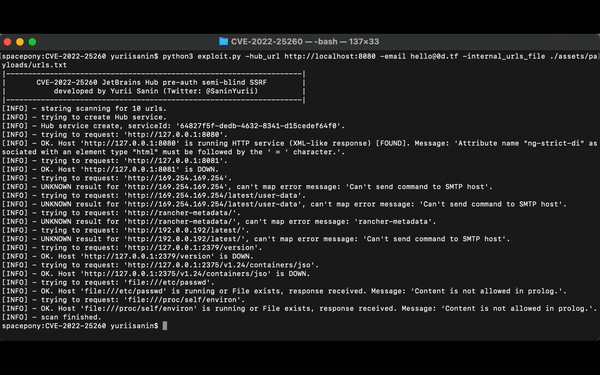 yuriisanin/cve-2022-25260
PoC for CVE-2022-25260: pre-auth semi-blind SSRF in JetBrains Hub
 xiaoqimikko/spring-cvss-check
Scans Java artifacts and source for Spring/Tomcat CVEs, compares vendor vs NVD CVSS scores, verifies exploitability conditions, and checks if fix…
 rxerium/cve-2023-40000
LiteSpeed Cache plugin for WordPress that could enable unauthenticated users to escalate their privileges
 jenderal92/cve-2026-48908
CVE-2026-48908 — PoC exploit for unauthenticated RCE in SP Page Builder (Joomla) via arbitrary file upload. Multi‑threaded, case‑bypass, shell…
 ricardojoserf/cve-2019-19033
CVE-2019-19033 description and scripts to check the vulnerability in Jalios JCMS 10 (Authentication Bypass)
 oscerd/cve-2026-64640
Reproducer for CVE-2026-64640 — Apache Polaris Iceberg REST register/register-view vends storage credentials and reads an attacker-chosen metadata…
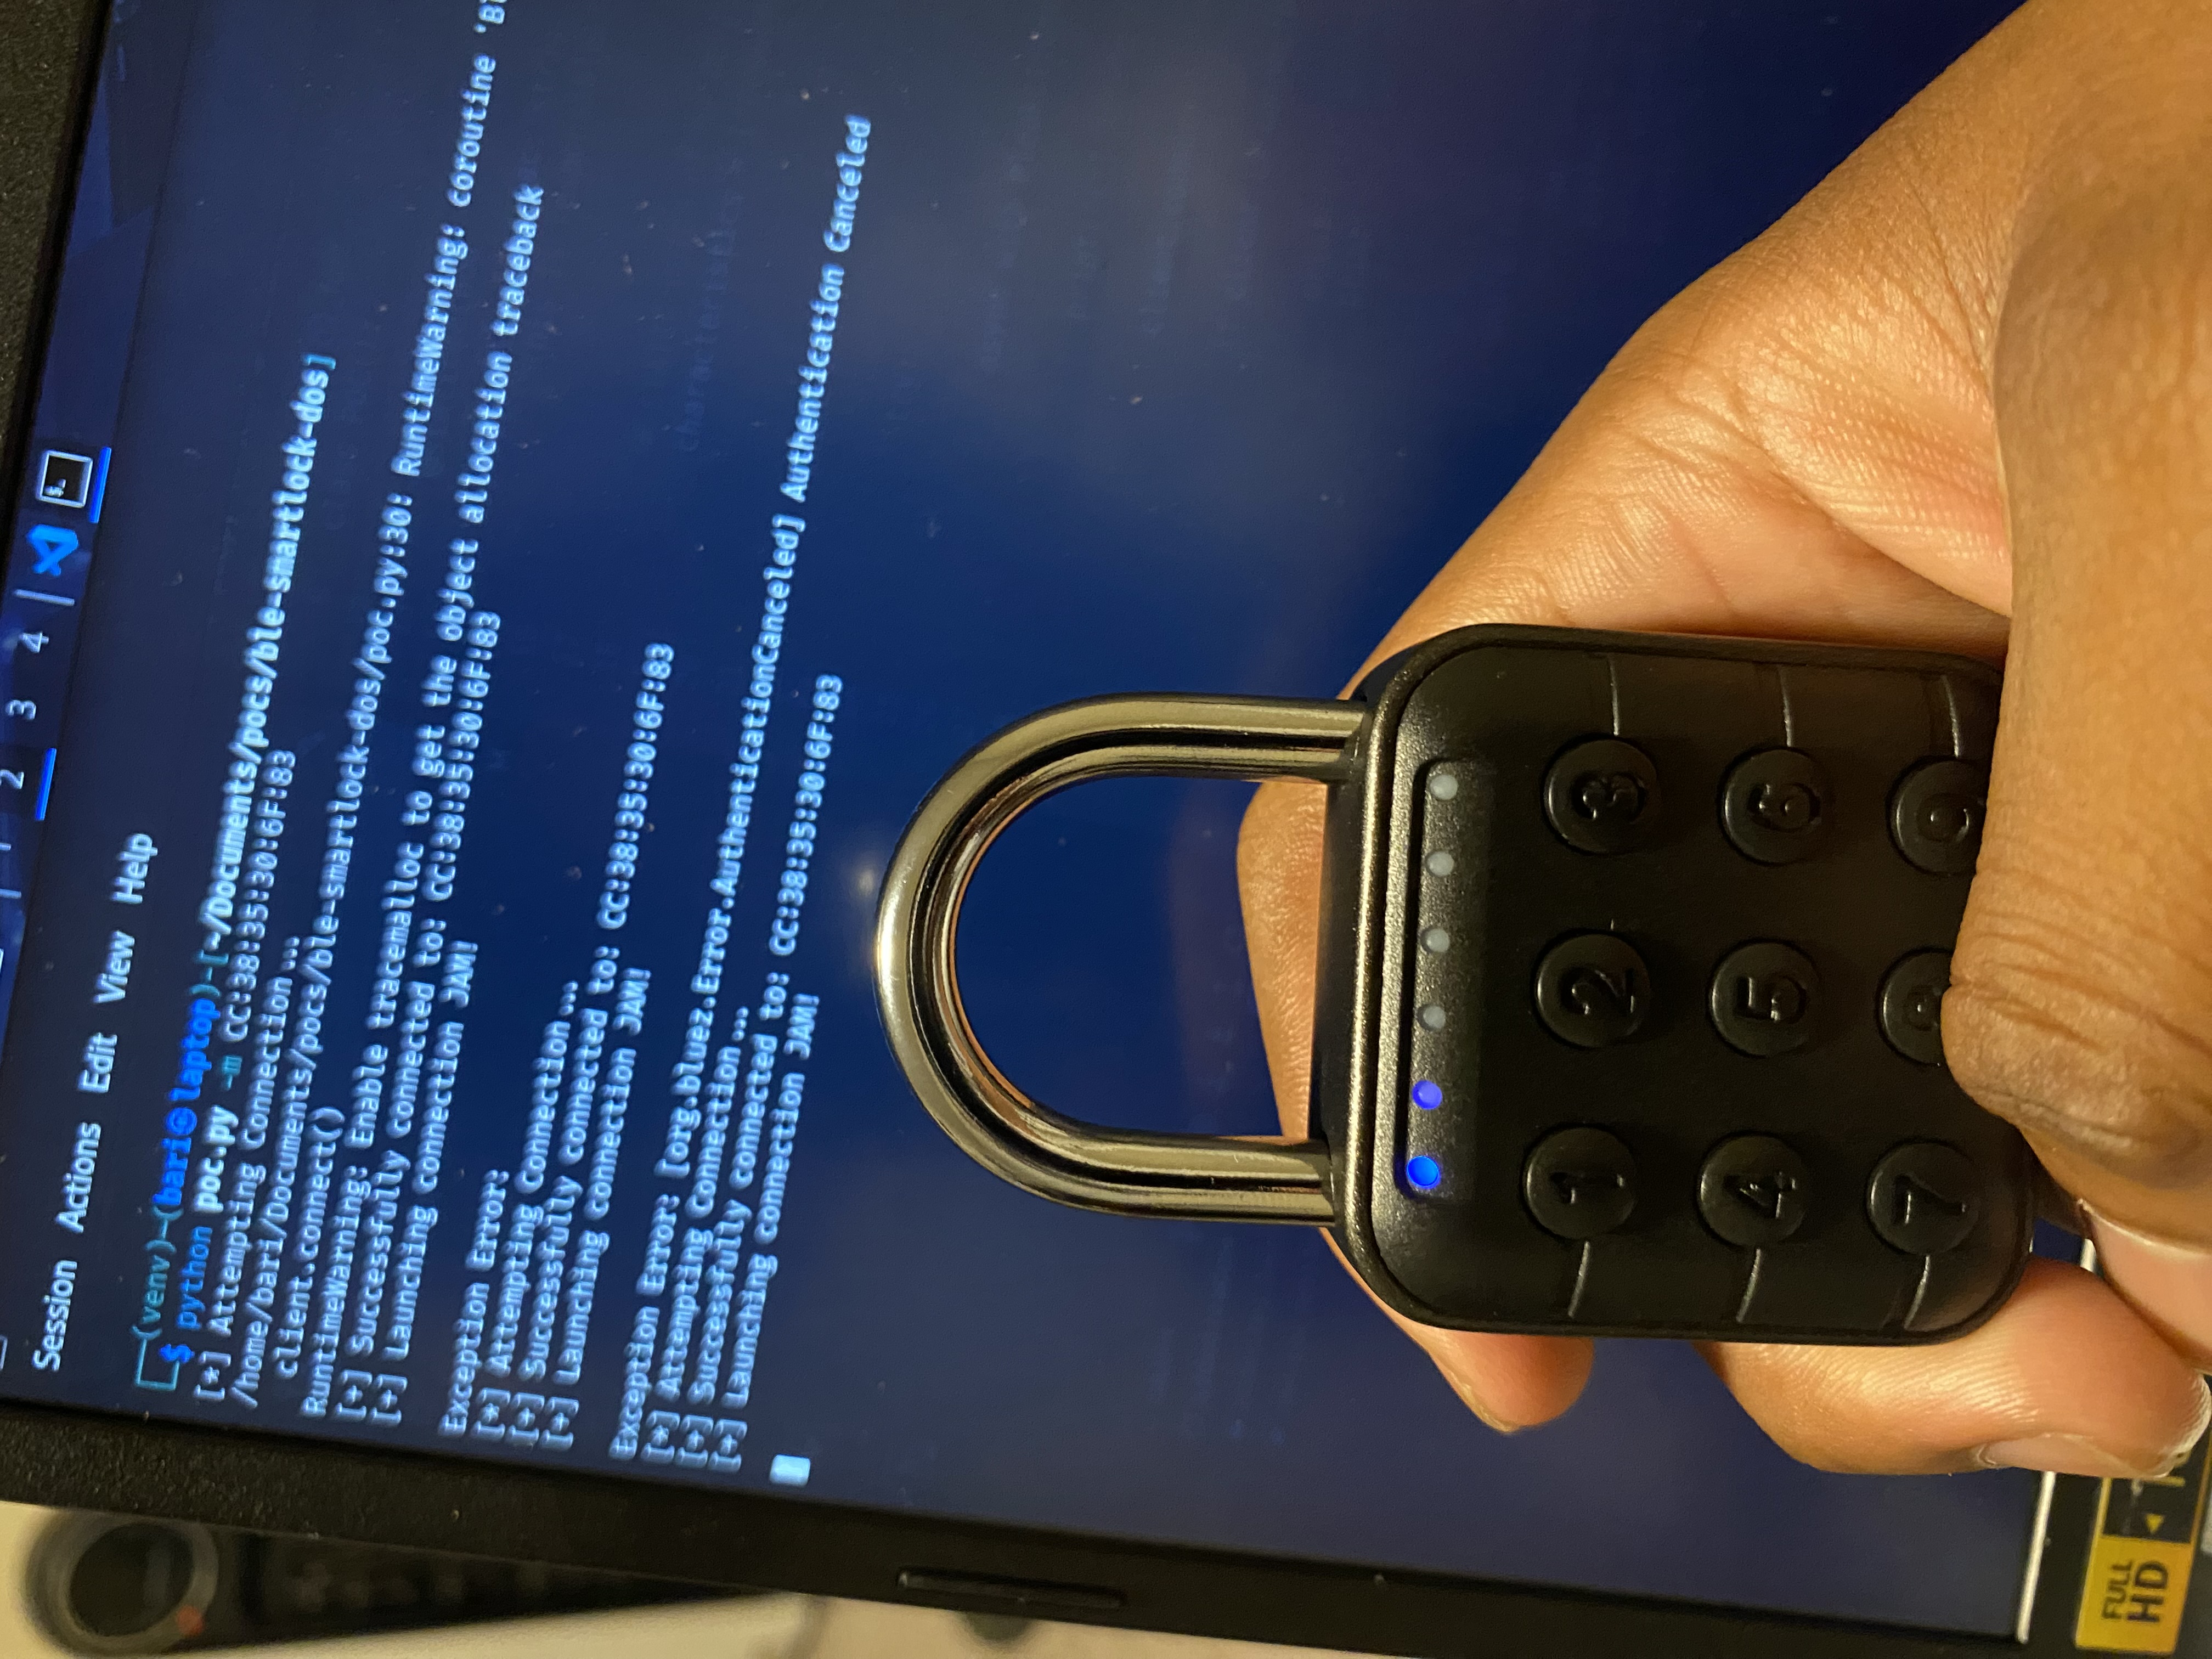 nsm-barii/cve-2025-15474
A denial-of-service vulnerability in the AuntyFey BLE smart padlock allows unauthenticated connection floods to lock out legitimate users. …
 d-maggipinto/cve-2026-72898-metabase-sqli
Detector + root-cause analysis for CVE-2026-72898 (Metabase unauthenticated SQLi via reset_password)
 choudai/gpon-loader
Exploit loader for Remote Code Execution w/ Payload on GPON Home Gateway devices (CVE-2018-10562) written in Python.
 jenderal92/cve-2024-8856
Scans WordPress sites for WP Time Capsule plugin CVE-2024-8856, detecting versions below 1.22.22 and logging vulnerable targets to a file.