leaflet-cve-2025-69993

Proof-of-concept for CVE-2025-69993: Cross-Site Scripting in Leaflet's bindPopup() method. Includes advisory, impact analysis, and a demo Angular…

Proof-of-concept for CVE-2025-69993: Cross-Site Scripting in Leaflet's bindPopup() method. Includes advisory, impact analysis, and a demo Angular…

Technical analysis of CVE-2026-28858, a critical buffer overflow in Apple iOS/iPadOS kernel, including exploit flow, mitigation, and defensive coding…

Security research & exploitation analysis of CVE-2025-55182 (React) — CVSS + OWASP Top 10 mapping

Security advisory detailing CVE-2026-28363, a critical RCE in OpenClaw, including technical analysis, CVSS metrics, and mitigation steps for…

Detailed analysis of CVE-2025-61686, a path traversal vulnerability in React Router's file session storage, including root cause, attack scenarios,…

Technical investigation and host containment of a Critical-severity Zero-Click RCE exploit (CVE-2025-21298) using EDR telemetry and static malware…

Proof of concept for CVE-2022-22629, a heap buffer overflow in Safari's WebGL multi-draw extension, with vulnerability analysis and crash…

Documentation of CVE-2017-11499: a hash flooding remote DoS vulnerability in Node.js caused by constant HashTable seeds, with analysis of the attack…

Research implementation demonstrating interaction with Linux eBPF subsystem related to CVE-2021-3490. Includes BPF map creation, syscall wrappers,…

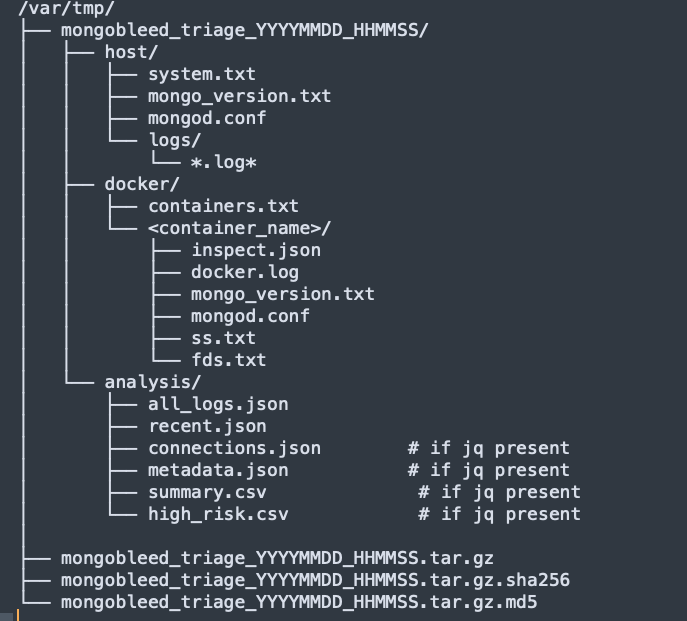
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…

Proof-of-concept exploit for CVE-2025-11832, demonstrating the vulnerability and providing a technical reference for security testing and analysis.

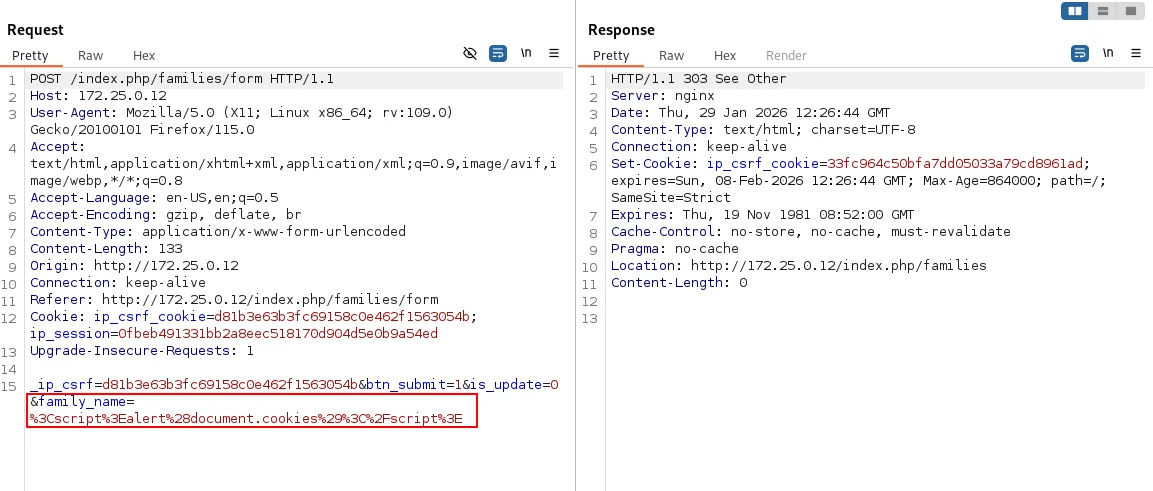
Stored XSS proof-of-concept for InvoicePlane 1.7.0 via the family name field, including payload, request, and impact analysis for defensive research.

Proof-of-concept exploit for CVE-2024-48510, a .NET Zip vulnerability. Includes reproduction steps and technical analysis via accompanying blog post.

Technical analysis and documentation of CVE-2024-6387, a critical remote code execution vulnerability in OpenSSH, detailing exploitation vectors and…

Technical analysis and writeup of CVE-2024-3094, the XZ Utils backdoor. Explores the supply-chain attack, exploitation mechanics, and detection…

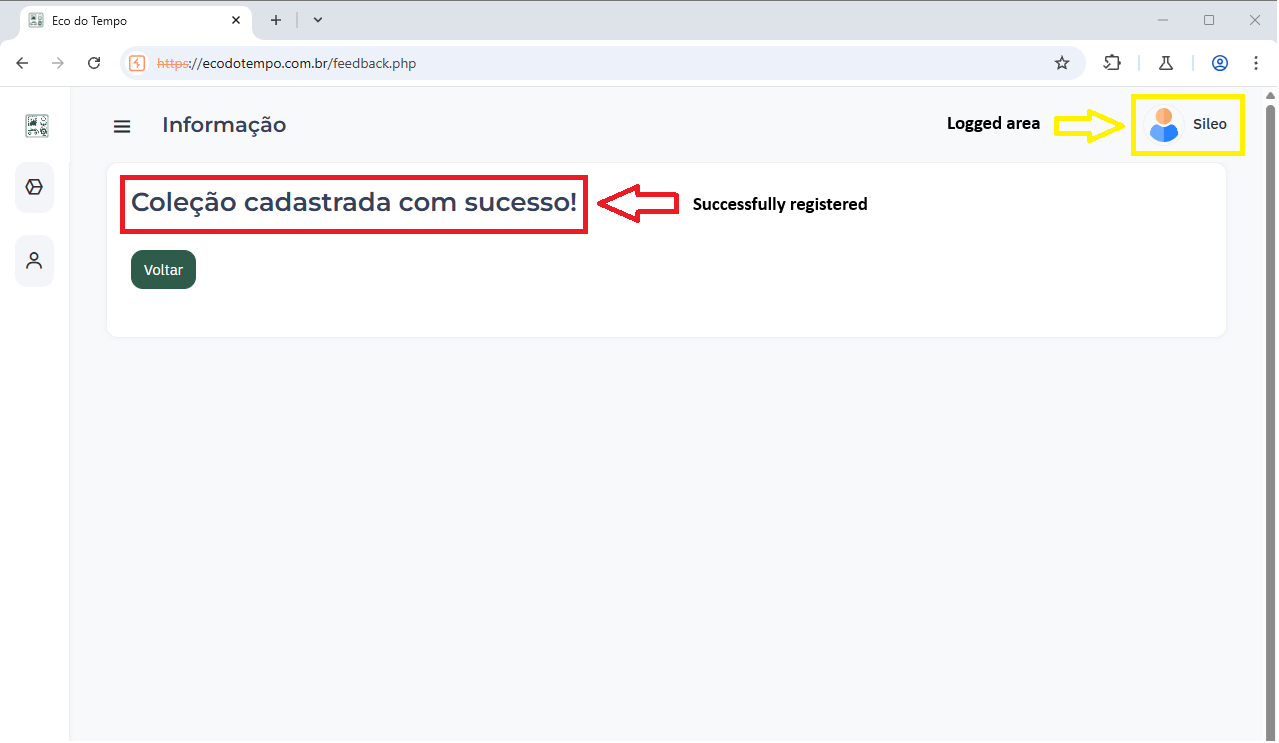
During the analysis of the website ecodotempo.com.br, a Stored Cross-Site Scripting (XSS) vulnerability was discovered. This vulnerability allows an…

Reflected XSS vulnerability disclosure with PoC script and remediation guidance for an online appointment booking system. Includes vulnerable…

Methodology for vulnerability analysis and exploit development, covering static/dynamic analysis, fuzzing, patch diffing, and 0-day research with…