
msiscan
 sec-consult/msiscan
Scanning tool for identifying local privilege escalation issues in vulnerable MSI installers
configuration-auditingpenetration-testingprivilege-escalation+2
129
sec-consult/msiscanScanning tool for identifying local privilege escalation issues in vulnerable MSI installers
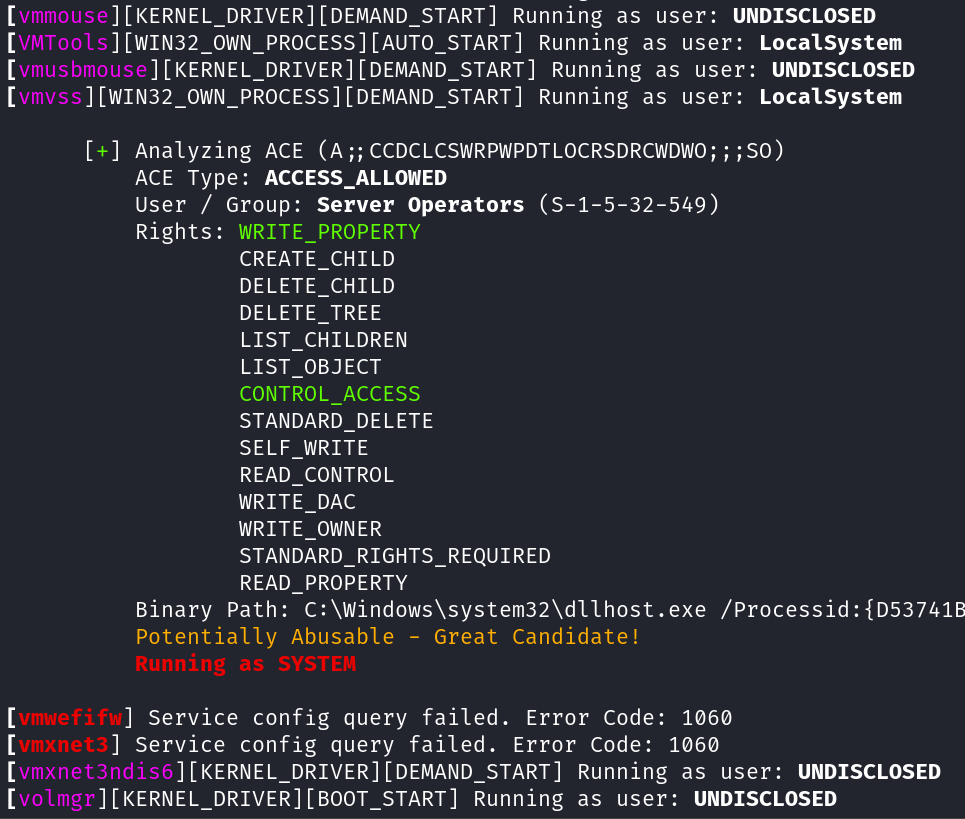 t3l3machus/aceshark
ACEshark is a utility designed for rapid extraction and analysis of Windows service configurations and Access Control Entries, eliminating the need…
 mthbernardes/heimdall_webserver
It's a tool to manage vulnerables packages in your *nix server, in a centralized way
 mubix/find-wsus
Helps defenders find their WSUS configurations in the wake of CVE-2025-59287
 d3sre/intelligentprocesslifecycle
The Intelligent Process Lifecycle of Active Cyber Defenders
 maxwitat/cve-2023-36884-scripts-for-intune-remediation-sccm-compliance-baseline
The remediation script should set the reg entries described in https://msrc.microsoft.com/update-guide/vulnerability/CVE-2023-36884 . The detection…
 ozergoker/cve-2021-40444
Microsoft MSHTML Remote Code Execution Vulnerability CVE-2021-40444
 synacktiv/cve-2020-9289
Decrypt reversible secrets encrypted using the default hardcoded key related to CVE-2020-9289 on FortiAnalyzer/FortiManager (the only difference with…
 technion/disablesmbcompression
CVE-2020-0796 Flaw Mitigation - Active Directory Administrative Templates
 ajf8729/blacklotus
BlackLotus aka CVE-2023-24932 Detection/Remediation Scripts for Intune, ConfigMgr, and generic use
 baba01hacker666/cve-2026-33032
Python proof-of-concept for CVE-2026-33032 that inspects nginx status and configs, then demonstrates unauthorized config write with reload to deploy…
 sofire/polkit-0.96-cve-2021-4034
centos 6.10 rpm for fix polkit CVE-2021-4034; centos 6.10的rpm包,修复CVE-2021-4034 漏洞
 cynepmyx/nginx-rift-check
Detects the CVE-2026-42945 rewrite pattern in nginx configs: rewrite with ? in the replacement plus an unnamed capture consumed in the same location
 gduma-phdata/patch-cve-2026-09881
Patch: Template injection RCE (Atlassian Confluence)
 execution-py/cve-2026-9055
Defensive analysis of CVE-2026-9055, an unauthenticated privilege escalation in Amelia WordPress booking plugin. Provides root cause breakdown,…
 nvansluis/test_cve-2023-46747
Python script to test F5 BIG-IP for CVE-2023-46747 and add an administrator account if vulnerable.
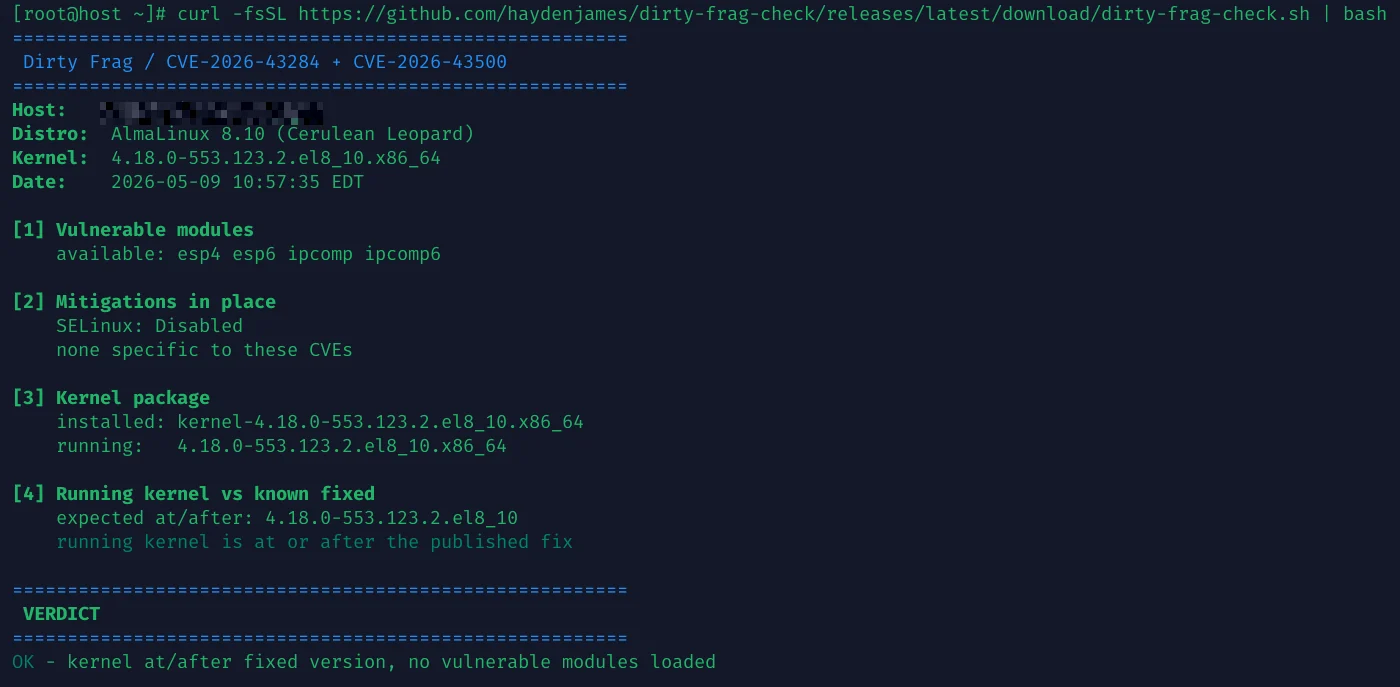 haydenjames/dirty-frag-check
Read-only checker for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) Linux kernel local-root vulns
 imxur/wordpress-cve-2026-63030-analysis
Technical analysis, root cause breakdown, and non-destructive detection methodology for CVE-2026-63030.