

CVE-2015-7547
 fjserna/cve-2015-7547
Proof of concept for CVE-2015-7547
binary-exploitationdns-analysisexploitation+2
fjserna/cve-2015-7547Proof of concept for CVE-2015-7547
 riverloopsec/killerbee
IEEE 802.15.4/ZigBee Security Research Toolkit
 quarkslab/conf-presentations
Quarkslab conference talks
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
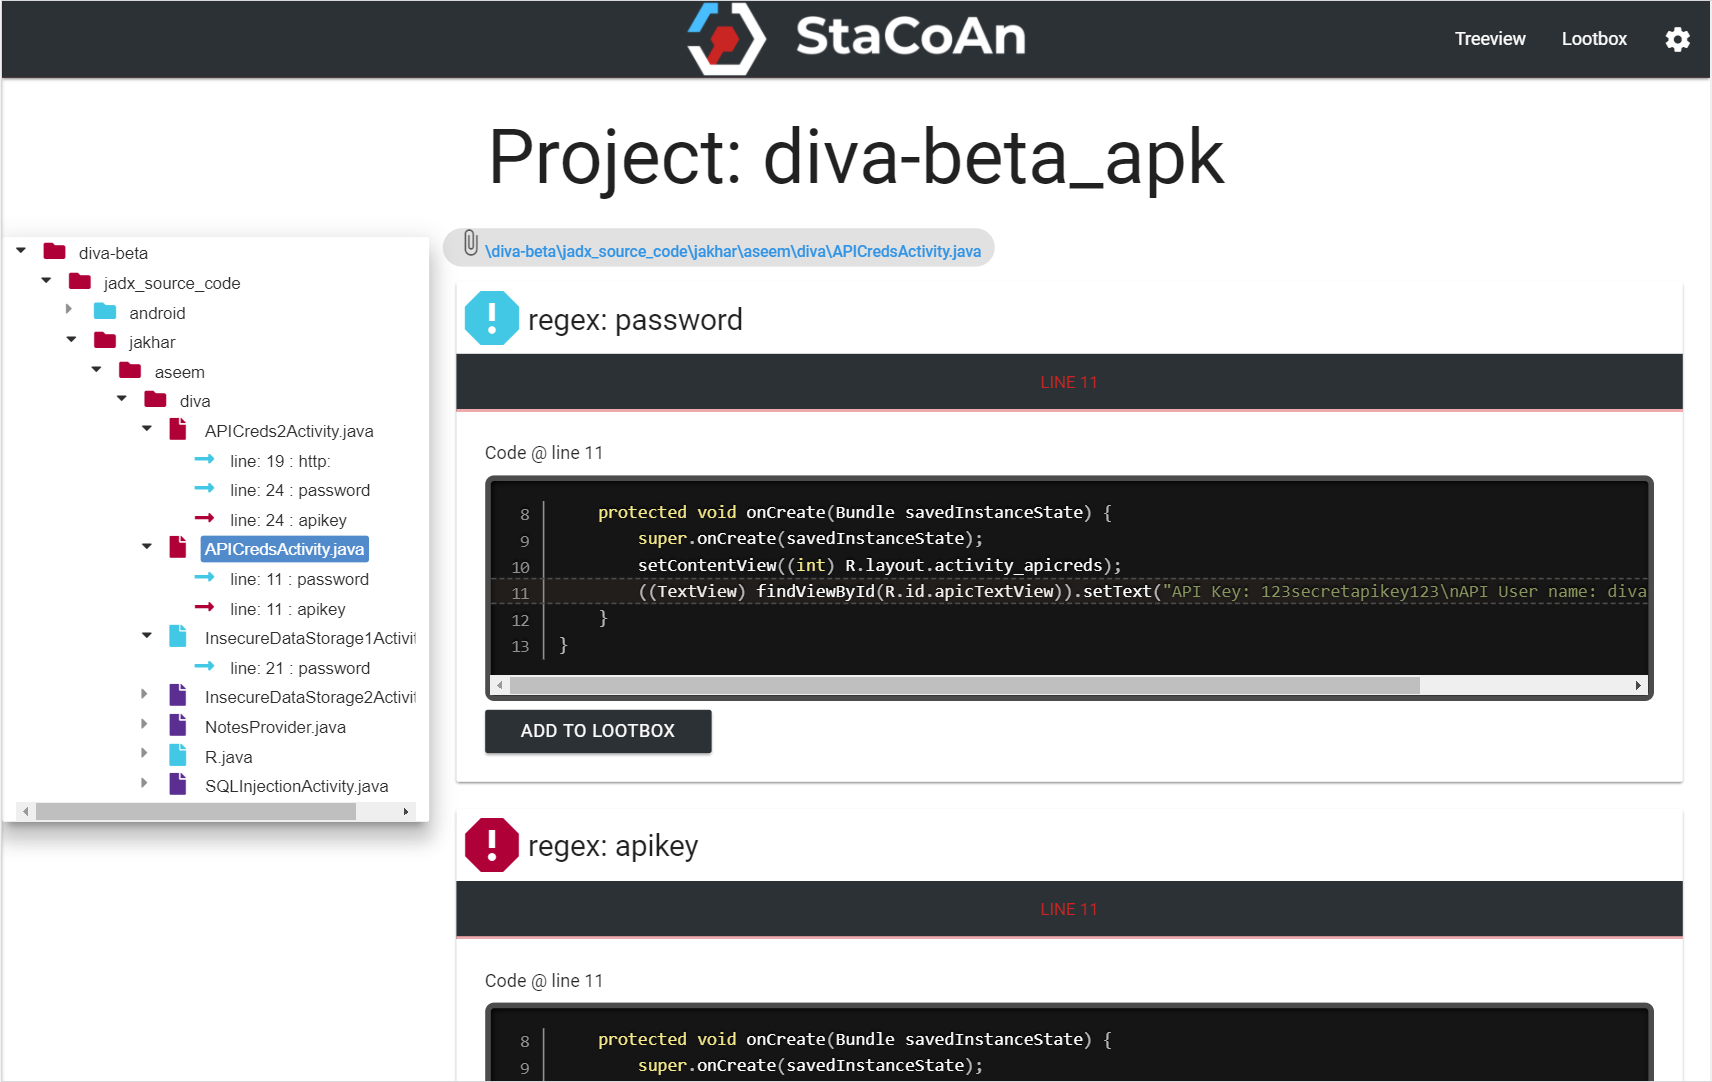 vincentcox/stacoan
StaCoAn is a crossplatform tool which aids developers, bugbounty hunters and ethical hackers performing static code analysis on mobile applications.

 silverpoision/rock-on
Rock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.
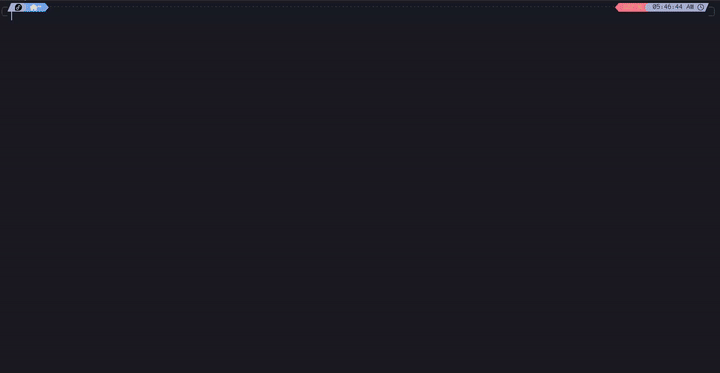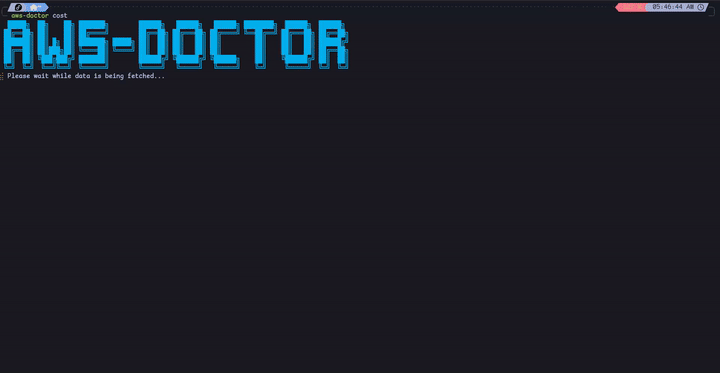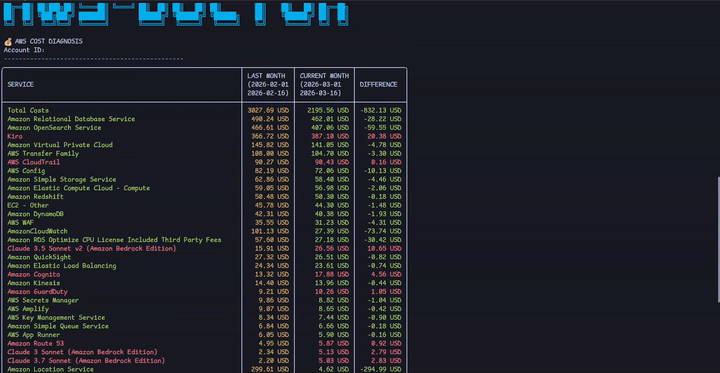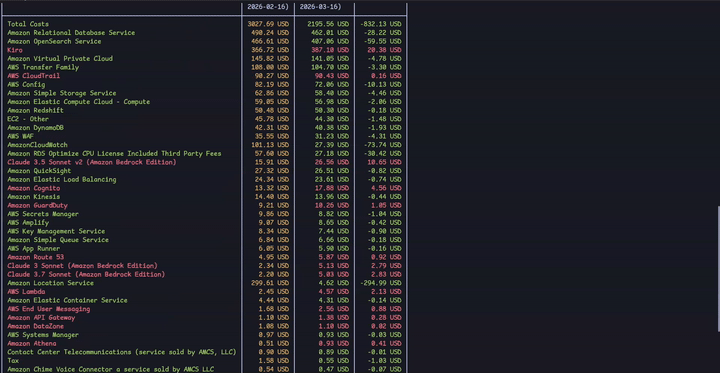 elc0mpa/aws-doctor
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️
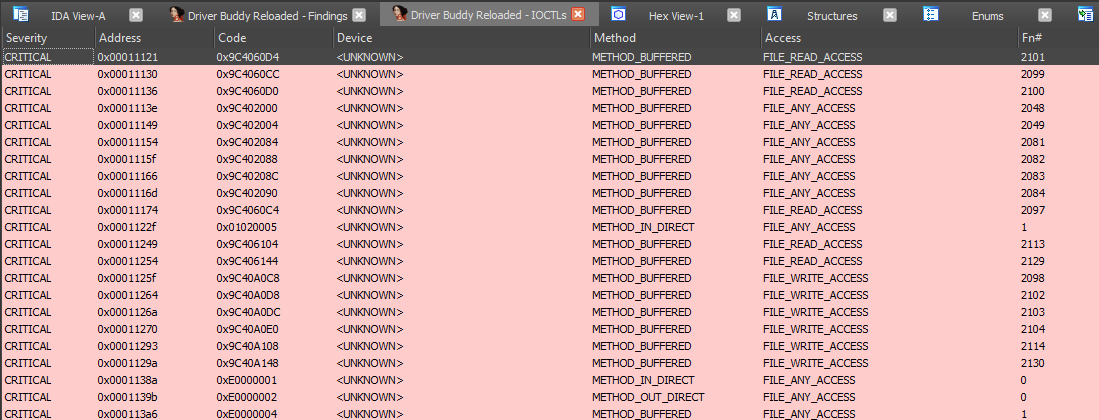 voidsec/driverbuddyreloaded
Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks
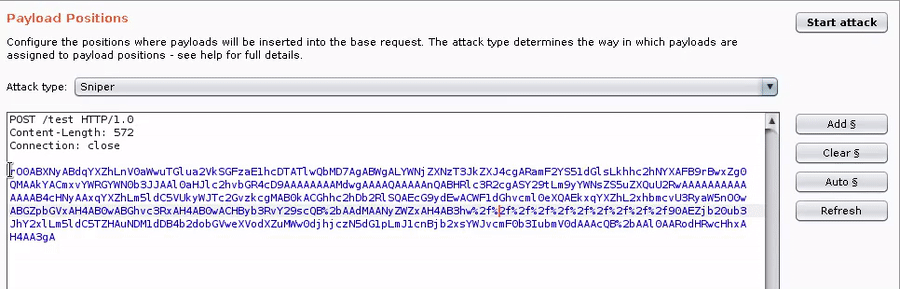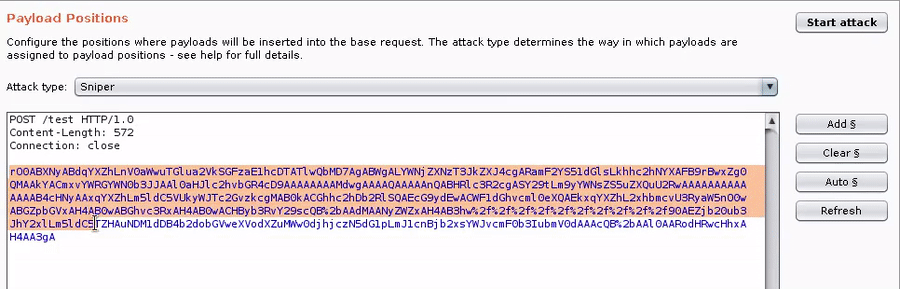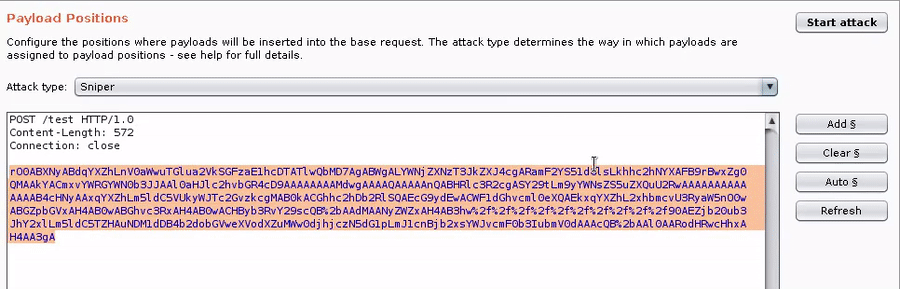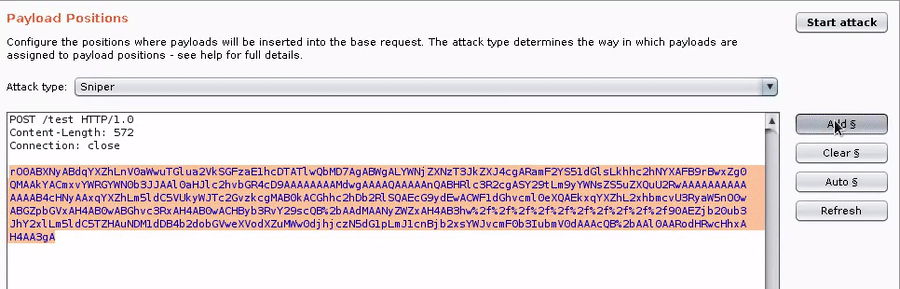 bishopfox/gadgetprobe
Probe endpoints consuming Java serialized objects to identify classes, libraries, and library versions on remote Java classpaths.
 its-arun/cve-2022-39197
Proof-of-concept exploit for CVE-2022-39197, enabling remote code execution against CobaltStrike <= 4.7.1 via malicious SVG payload served over HTTP.
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 yt1g3r/cve-2019-3396_exp
CVE-2019-3396 confluence SSTI RCE
 medpaf/hawk
Network, recon and offensive-security tool for Linux.
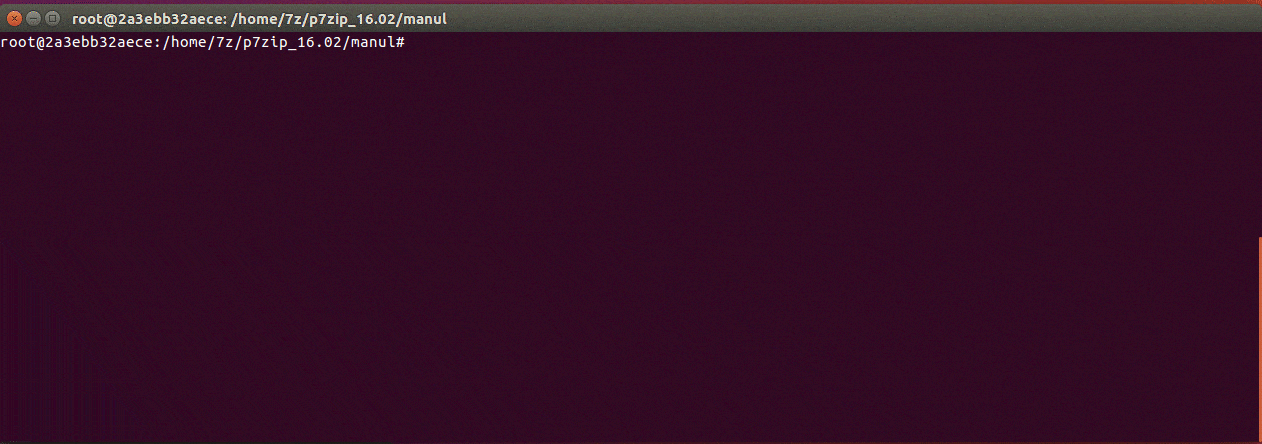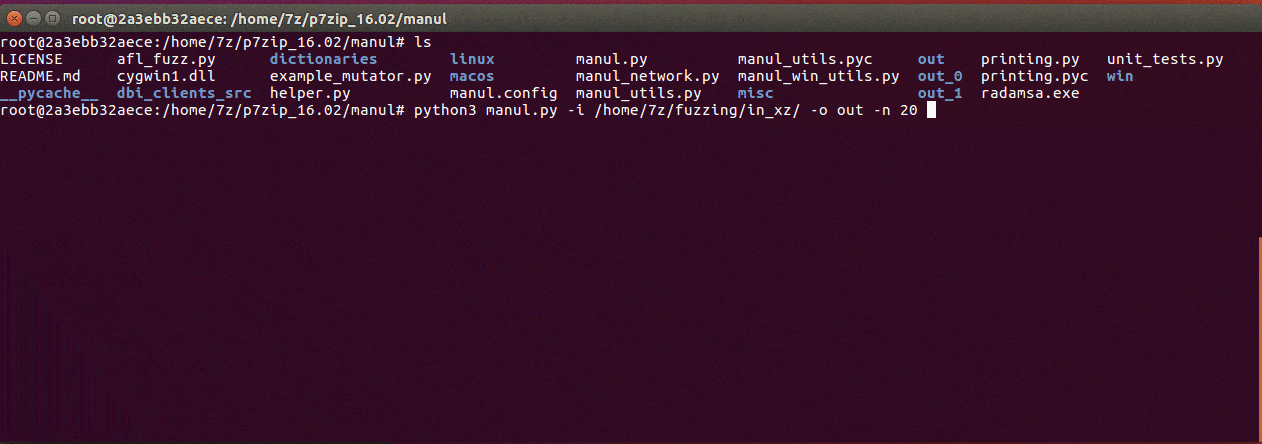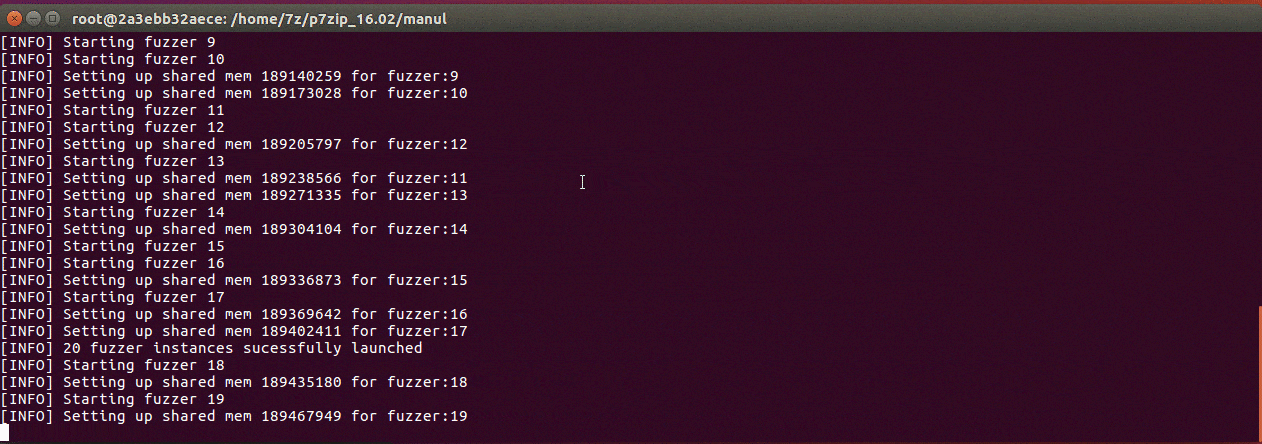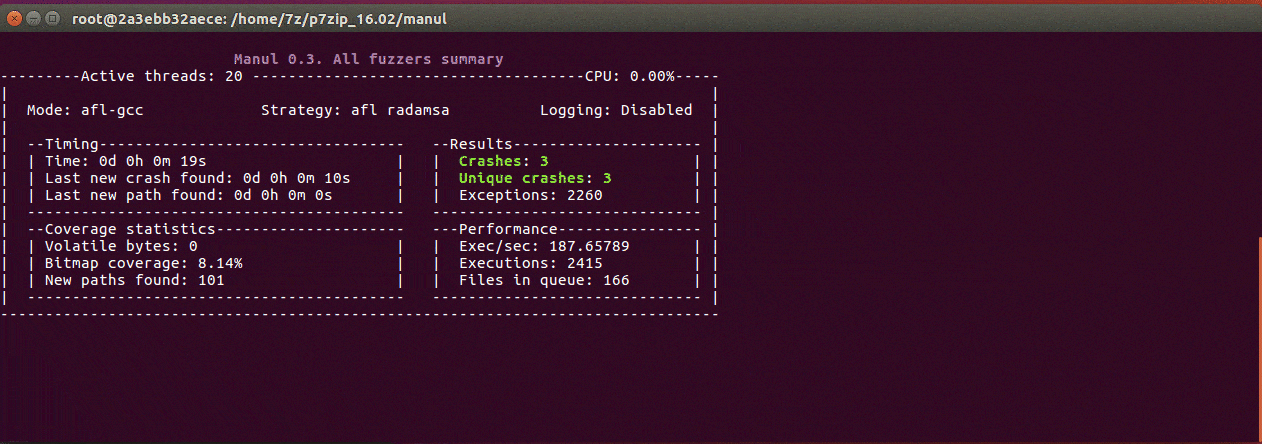 mxmssh/manul
Manul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 breenmachine/javaunserializeexploits
Exploit Java deserialization vulnerabilities in WebLogic, WebSphere, JBoss, Jenkins, and OpenNMS using Python PoC scripts and crafted HTTP requests.
 nu11secur1ty/cve-mitre
https://cve.mitre.org/