
SNet
 hrmtz/snet
AI-guided CTF - Break into a real server with Claude Code as your trainer
ctfeducationexploitation+8
hrmtz/snetAI-guided CTF - Break into a real server with Claude Code as your trainer
 devianntsec/cve-2024-51324
Master's Thesis research on CVE-2024-51324 (BYOVD). Advanced exploit with 4 operational modes (SCANNER, LOADER, KILLER, CLEANUP), SHA-256 driver…
 horkimhab/cve-2026-0001
CVE-2026-0001. Do with your own risk
 rishipatidar/cve-2023-30212-poc-docker-file
This repository provides a Docker container for simulating the CVE-2023-30212 vulnerability, allowing you to practice and understand its impact. It…
 sibersan/web-server-audit_cve-2026-42945
Trigger-aware web server CVE audit for nginx and Apache. Goes beyond version matching by checking whether the vulnerable code path is actually…
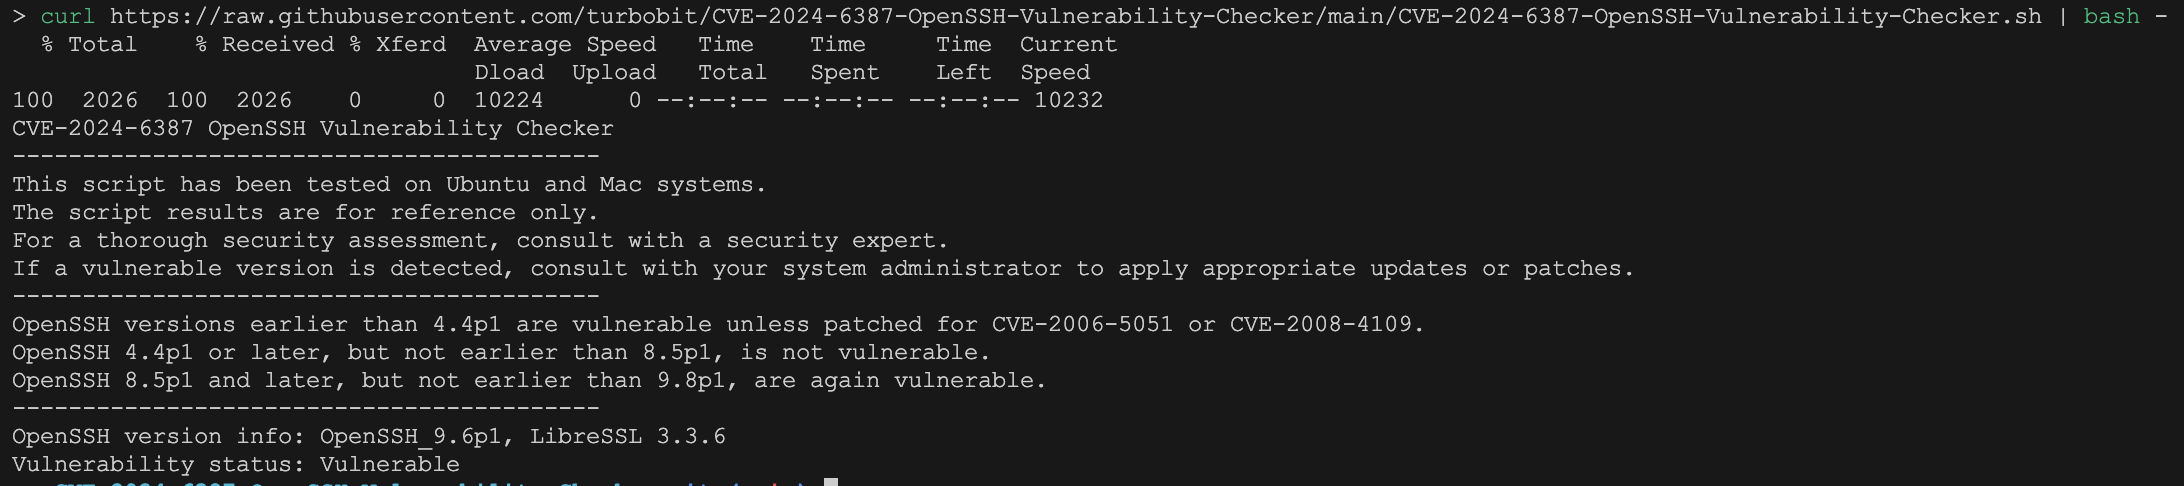 turbobit/cve-2024-6387-openssh-vulnerability-checker
Welcome to the CVE-2024-6387 OpenSSH Vulnerability Checker repository! This project offers multiple scripts to check the installed version of…
 pescada-dev/-cve-2025-8088
POWERSHEL script to check if your device is affected or no
 tulhan/commons-text-goat
An intentionally vulnerable webapp to get your hands dirty with CVE-2022-42889.
 retr02332/cve-2020-7115
Create your malicious engine in seconds
 tumikoto/exploit-fortinetmagicbackdoor
PoC for CVE-2018-13382, never successfully tested so swim at your own risk
 dedsec-47/metasploit-exploits-cve-2023-6710
Welcome to the Metasploit Exploits Repository, your go-to resource for a comprehensive collection of cutting-edge exploits designed for penetration…
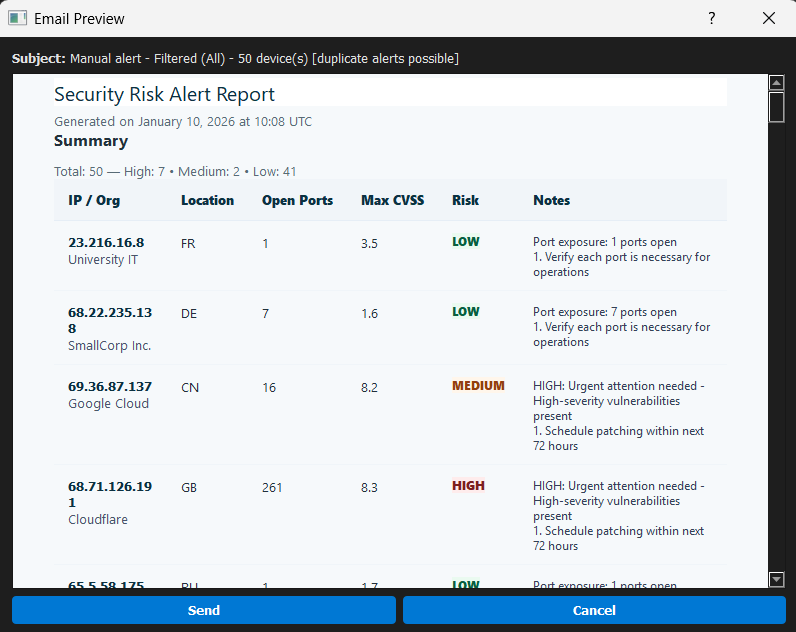 eclipsemanic/threatsentry-ai
ThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…
 darabium/gombruc
This vulnerability is related to CVE-2025-0401, which affects all Linux systems. With the help of this bash script, you can give your user any level…
 arnaudluti/ps-cve-2021-21551
Script to patch your domain computers about the CVE-2021-21551. Privesc on machines that have the driver dbutil_2_3.sys, installed by some DELL tools…
 ryo-soikutsu/heartbleed
Demonstration of the Heartbleed CVE (CVE-2014-0160), including lab setup instructions and source code to build your own Heartbleed lab for…
 praiseimafidon/version_vulnerability_scanner
A vulnerability scanner for Firefox and Thunderbird that checks if your versions are out of date and susceptible to CVE-2024-9680.
 tinopreter/docviewerexploitapp
This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…
 mrk336/cve-2025-27480-the-silent-gateway-risk
Letting attackers run malicious code without needing a cracked password, user interaction, or even a foothold in your network. That’s CVE-2025-27480