

CVE-2025-44137
 mheranco/cve-2025-44137
Proof-of-concept exploit for CVE-2025-44137: unauthenticated directory traversal in MapTiler Tileserver-php v2.0, enabling arbitrary file read via…
exploitationinformation-gatheringpenetration-testing+2
mheranco/cve-2025-44137Proof-of-concept exploit for CVE-2025-44137: unauthenticated directory traversal in MapTiler Tileserver-php v2.0, enabling arbitrary file read via…
 mheranco/cve-2025-44136
Proof-of-concept exploit for unauthenticated reflected XSS in MapTiler Tileserver-php v2.0 via the 'layer' GET parameter, enabling arbitrary HTML/JS…
 jfs-jfs/cve-2026-37070
Proof-of-concept exploit for CVE-2026-37070: an authenticated attacker can read arbitrary uploaded files in Veno File Manager 4.4.9 via a crafted GET…
 jacopoaugelli/cve-2025-60574
Proof-of-concept exploit for CVE-2025-60574, a Local File Inclusion vulnerability in tQuadra CMS 4.2.1117, enabling arbitrary file retrieval via…
 ethancunt/cve-2022-45600
Proof-of-concept exploit for command injection vulnerability in Aztech WMB250AC routers, enabling authenticated privilege escalation to root shell…
 s4fv4n/cve-2024-57784
Exploit for CVE-2024-57784: authenticated directory traversal in Zenitel AlphaWeb XE 11.2.3.10. Enables remote file reading via HTTP GET requests…
 20matan/cve-2018-6574-poc
Proof-of-concept exploit for CVE-2018-6574, demonstrating arbitrary command execution via crafted import paths in Go's go get command.
 mandiant/threatpursuit-vm
Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…
 rickgeex/proxylogon
ProxyLogon is the formally generic name for CVE-2021-26855, a vulnerability on Microsoft Exchange Server that allows an attacker bypassing the…
 soltanali0/cve-2025-4476-exploit
Python test client that sends HTTP GET requests with oversized Authorization headers to trigger header-parsing bugs like CVE-2025-4476. For…
 te-k/harpoon
CLI tool for open source and threat intelligence
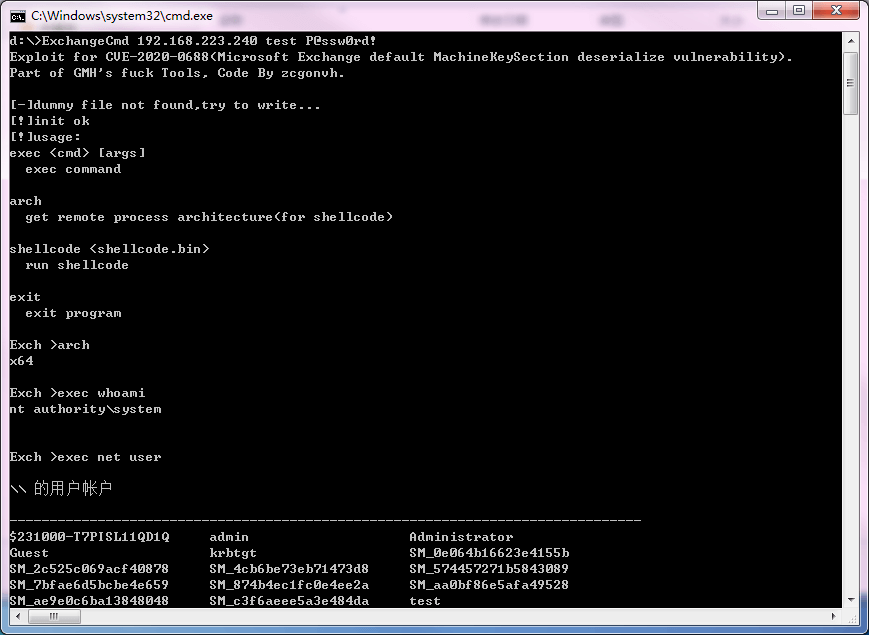 zcgonvh/cve-2020-0688
Exploit and detect tools for CVE-2020-0688
 malwaretech/log4jtools
Tools for investigating Log4j CVE-2021-44228
 34zy/microsoft-office-word-mshtml-remote-code-execution-exploit
Exploits CVE-2021-40444 in Microsoft Office Word to achieve remote code execution through the MSHTML engine by injecting malicious content into a…
 adversarial-detection-engineering/adversarial-detection-engineering-framework
A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…
 egebalci/ticketbleed
This is a tool for exploiting Ticketbleed (CVE-2016-9244) vulnerability.
 cyberheartmi9/cve-2017-8295
Proof-of-concept exploit for CVE-2017-8295, a WordPress password reset vulnerability allowing attackers to obtain reset links without authentication,…