
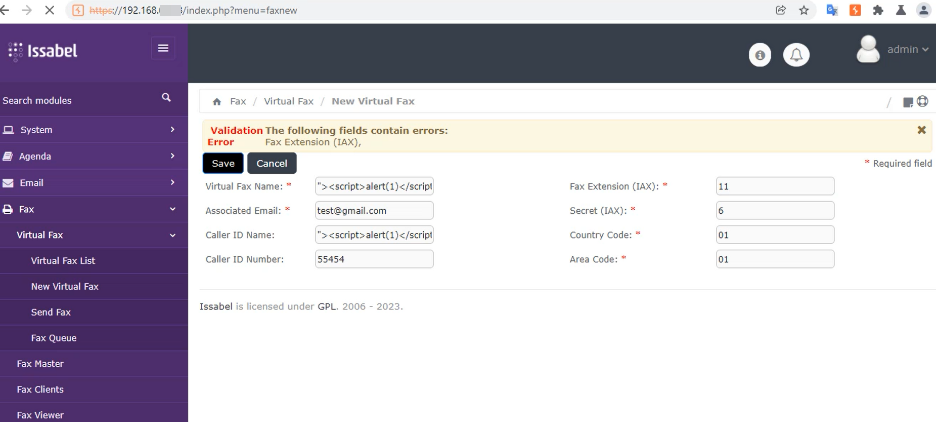
CVE-2023-37190
 sahiloj/cve-2023-37190
A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel-PBX version 4.0.0-6. The application fails to properly sanitize and encode…
educationexploitationpapers-research+3
1
sahiloj/cve-2023-37190A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel-PBX version 4.0.0-6. The application fails to properly sanitize and encode…
 anandjogawade/cve-2026-48849-roundcube-webmail-stored-xss
This repository documents CVE-2026-48849, a Stored Cross-Site Scripting (XSS), HTML Injection, and CSS Injection vulnerability discovered in…
 lightningspeed221/winrar-exploit-cve-2023-38831
C# utility demonstrating CVE-2023-38831 archive-structure exploitation technique for WinRAR versions below 6.23. Builds proof-of-concept binaries for…
 aykhan32/cve-2026-51788
Detailed CVE-2026-51788 advisory for a DoS vulnerability in cleverange_auth v0.1.10, with technical analysis, CVSS scoring, and mitigation guidance…
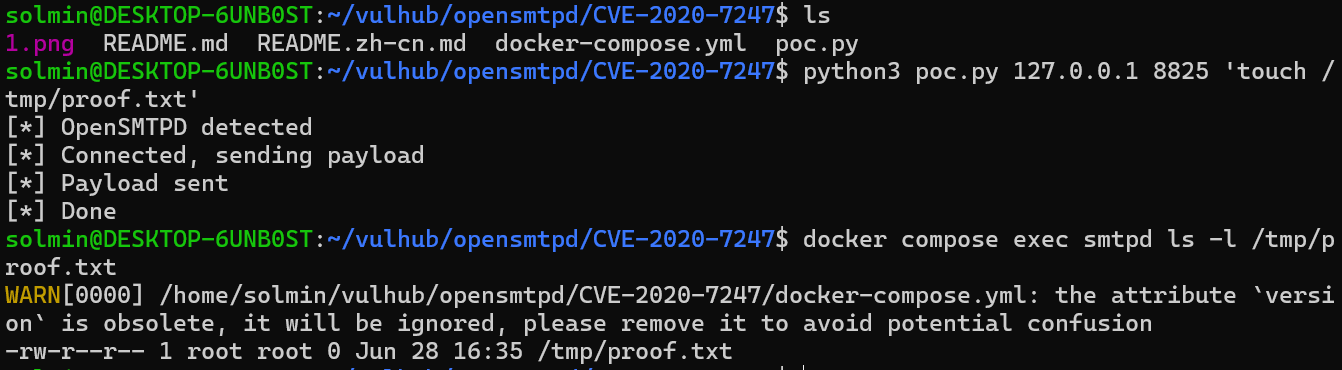 solmin111/opensmtpd-cve-2020-7247-
Docker-based lab demonstrating CVE-2020-7247 remote code execution in OpenSMTPD 6.6.1p1 with a Python PoC for educational security testing.
 yoguicr/cve-2024-21413-outlook-assessment
Detailed vulnerability assessment and exploitation report for CVE-2024-21413 (Moniker Link) in Microsoft Outlook, including attack path, NetNTLMv2…
 cmadhushanka/wordpress-rce-vapt-cve-2020-25213
Educational cybersecurity project demonstrating exploitation and mitigation of CVE-2020-25213 (WordPress File Manager Plugin RCE). Includes malware…
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 c-g-creator/letsdefend-soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
LetsDefend SOC336 case study on CVE-2025-21298
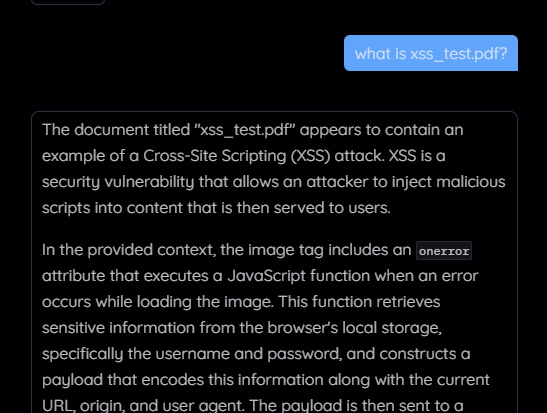 hantul/kotaemon-cve-2025-56526-56527-disclosure
Public disclosure for CVE-2025-56526 and CVE-2025-56527 — Stored XSS via unsanitized PDF content rendering and plaintext credential exposure in…
 pescada-dev/cve-2025-22381
Discovering CVE-2025-22381: Host Header Injection in the Aggie Open-Source Project
 nxploited/cve-2025-25101
WordPress Munk Sites plugin <= 1.0.7 - CSRF to Arbitrary Plugin Installation vulnerability
 ronixxcybsec0101/cve-2025-25460
Cross Site Scripting Vulnerability in Flatpress CMS
 theethat-thamwasin/cve-2025-63307
An authenticated Stored Cross-site Scripting (XSS) vulnerability in laravel-file-manager v3.3.1 and below allows attackers with access to the file…
 fdzdev/cve-2024-50964
Documentation of CVE-2024-50964: critical DMARC policy bypass in DonWeb MX server allowing email spoofing, with low attack complexity and no required…
 polarisxsec/cve-2024-21413
Educational lab demonstrating CVE-2024-21413 exploitation in Outlook to leak NTLM hashes via malicious UNC links, with custom SMTP/POP3…
 hackwidmaddy/cve-2024-57522
CVE-2024-57522 - Stored XSS Vulnerability in Users.php - SourceCodester Packers and Movers Management System 1.0
 nuky-alt/cve-2025-8088
Proof-of-concept exploit and technical analysis for a WinRAR path traversal vulnerability enabling code execution via crafted archives with binary…