
CVE-2026-20516
 dingo97/cve-2026-20516
Write-up and ADB proof of concept for CVE-2026-20516, a confused deputy flaw in MediaTek Android TV MiracastService allowing local Wi-Fi Direct state…
android-securityeducationexploitation+5
dingo97/cve-2026-20516Write-up and ADB proof of concept for CVE-2026-20516, a confused deputy flaw in MediaTek Android TV MiracastService allowing local Wi-Fi Direct state…
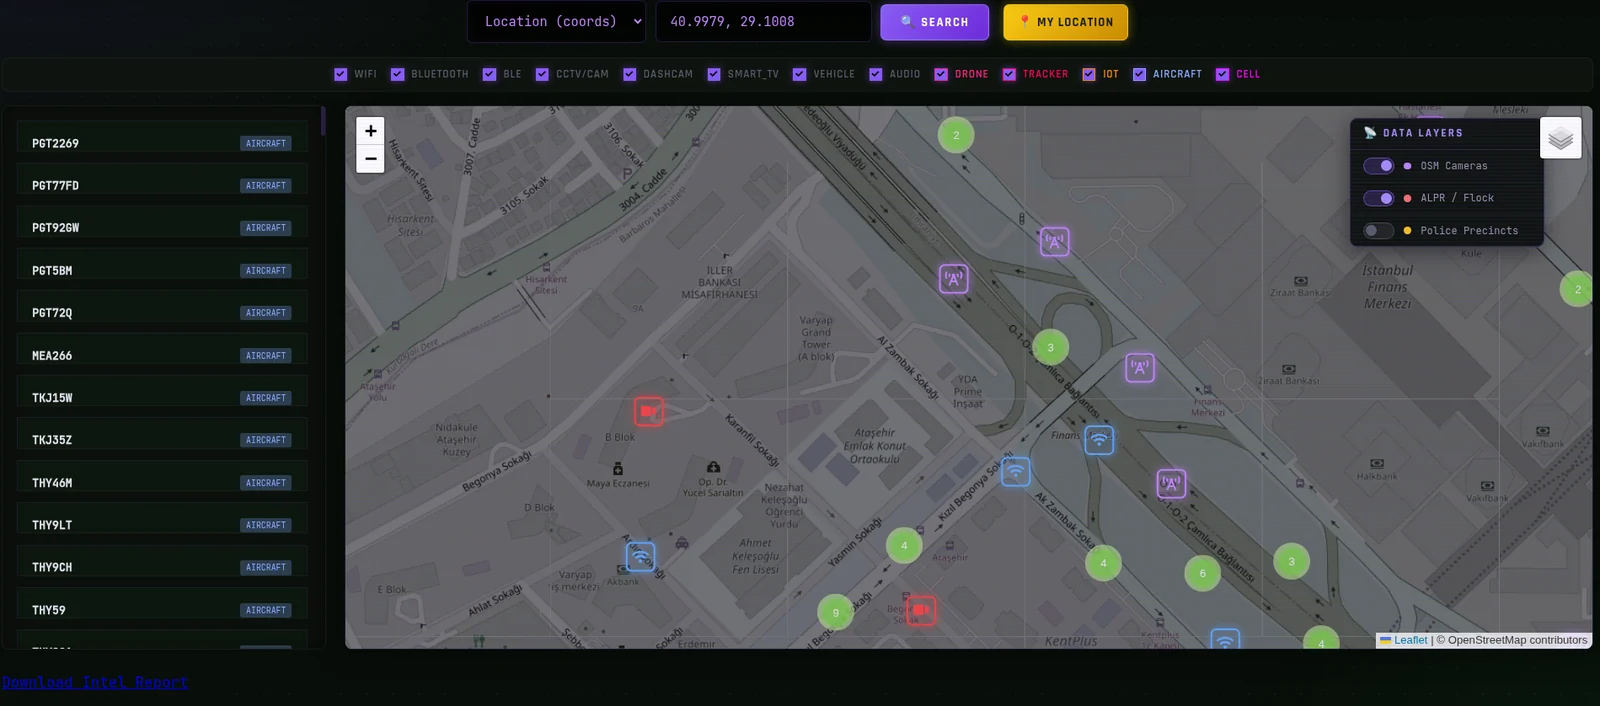 emrekybs/signalops
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…
 masjadaan/cve-2025-29338
Technical advisory and proof-of-concept for a stack-based buffer overflow (CWE-121) in the NXP moal.ko Wi-Fi kernel driver, enabling local kernel…
 nadafarafat/bd-alaris-firmware-analysis
Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…
 uthrasri/frameworks_opt_net_wifi_cve-2021-0390
Android Wi-Fi framework patch for CVE-2021-0390, addressing a remote code execution vulnerability in the Wi-Fi subsystem.
 t4e-3/cve-2025-63296
KERUI K259 5MP Wi-Fi (Tuya Smart Security Camera) contains a code execution vulnerability
 satheesh575555/external_wpa_supplicant_8_aosp10_r33_cve-2021-0516
Proof-of-concept exploit for CVE-2021-0516 in wpa_supplicant on AOSP 10, demonstrating a buffer overflow vulnerability in Wi-Fi authentication.
 shaikusaf/external_wpa_supplicant_8_aosp10_r33cve-2021-0326
Android Wi-Fi vulnerability research repository containing patched wpa_supplicant source for CVE-2021-0326, enabling analysis and testing of the…
 turretsec/u3000py
Python client for the Thinkware U3000 dashcam's local WiFi control protocol, reverse-engineered from the official Android app. PoC tooling behind…
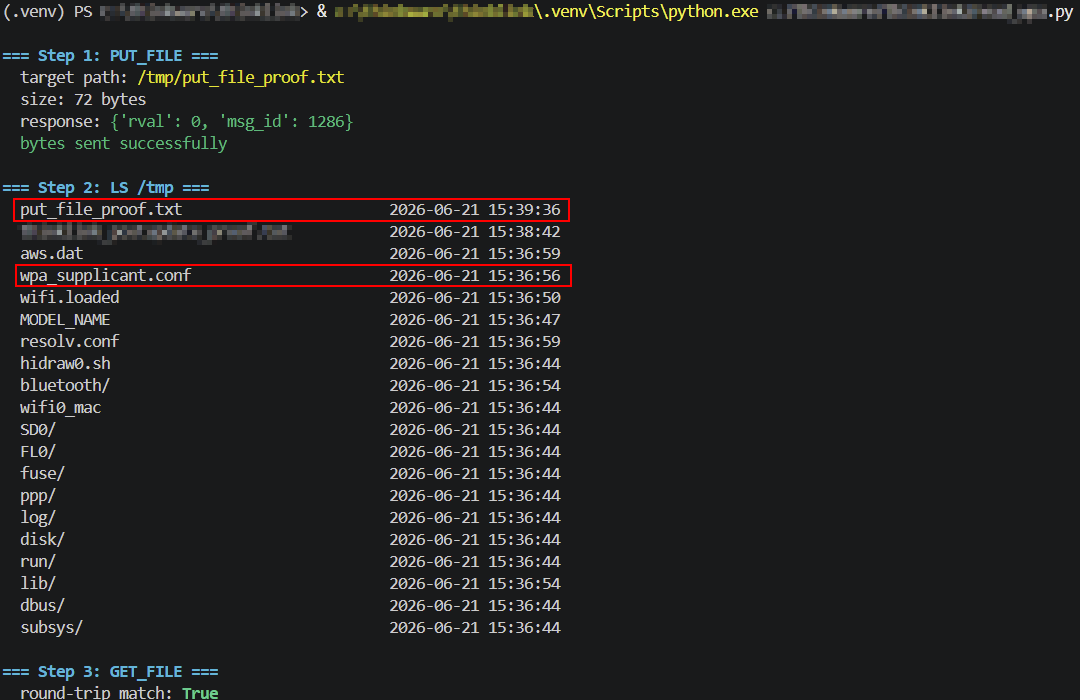 turretsec/disclosure-thinkware-u3000
Three unauthenticated vulnerabilities in the Thinkware U3000 dashcam's local WiFi control protocol: arbitrary file write, arbitrary file read, and…
 goultarde/remotemouse-3.008-rce
POC for CVE-2021-35448 based on https://www.exploit-db.com/exploits/49601
 nahueldsanchez/blogpost_cve-2018-19987-analysis
This repo has a blog post about my analysis for CVE-2018-19987 an authenticated OS command injection affecting multiple D-Link routers
 nanopathi/wpa_supplicant_8_cve-2021-0326.
Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.