
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
517 results
CVE-2024-22894 preview

CVE-2024-22894

GitHubjaarden/cve-2024-22894

Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…

cryptographyembedded-systems-securityexploitation+6
3
2 years ago
UEFI-Security-Research-Howyar-SysReturn-NetCopy preview

UEFI-Security-Research-Howyar-SysReturn-NetCopy

GitHubthemalwareguardian/uefi-security-research-howyar-sysreturn-netcopy

Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…

binary-analysisembedded-systems-securityexploitation+6
21 month ago
CVE-2022-24693 preview

CVE-2022-24693

GitHublukejenkins/cve-2022-24693

Documentation and reproduction steps for CVE-2022-24693: hardcoded credentials in Baicells Nova436Q and Neutrino 430 firmware, enabling remote SSH…
embedded-systems-securityexploitationfirmware-analysis+6
31 year ago
CVE-2026-1122-IoT-Firmware-Update-Signature-Bypass-via-Low-Order-Point-Injection preview

CVE-2026-1122-IoT-Firmware-Update-Signature-Bypass-via-Low-Order-Point-Injection

GitHubgeorge0papasotiriou/cve-2026-1122-iot-firmware-update-signature-bypass-via-low-order-point-injection

Demonstrates CVE-2026-1122 Ed25519 signature bypass via low-order point injection, forging malicious IoT firmware updates with Python and C verifier…
cryptographyembedded-systems-securityexploitation+4
3 months ago
CVE-2026-56718 preview

CVE-2026-56718

GitHubhellkkid/cve-2026-56718

AJCloud AJY IPC Firmware Path Traversal via jdbhttpd
embedded-systems-securityexploitationiot-security+3
2 months ago
CVE-2026-38577 preview

CVE-2026-38577

GitHubpoxsky/cve-2026-38577

Proof-of-concept demonstrating hardcoded root credentials (admin/system) in Tenda HG21 XPON modem firmware, enabling unauthorized root access via…
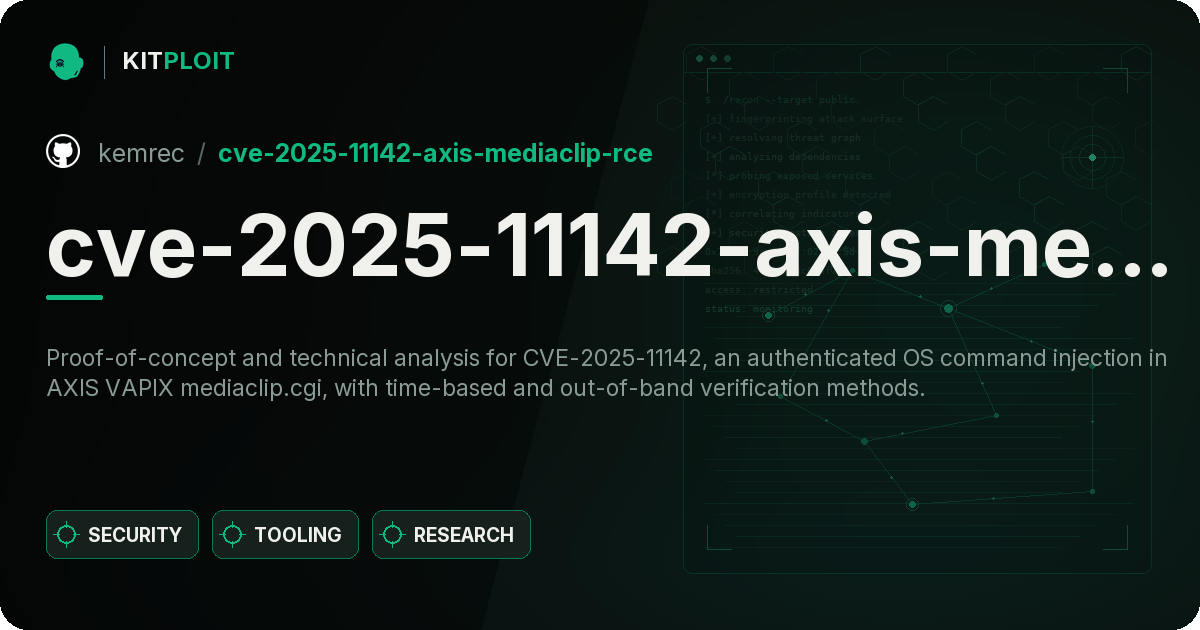
embedded-systems-securityexploitationfirmware-analysis+5
2 months ago
cve-2025-11142-axis-mediaclip-rce preview

cve-2025-11142-axis-mediaclip-rce

GitHubkemrec/cve-2025-11142-axis-mediaclip-rce

Proof-of-concept and technical analysis for CVE-2025-11142, an authenticated OS command injection in AXIS VAPIX mediaclip.cgi, with time-based and…
exploitationiot-securitypenetration-testing+2
2 months ago
CVE-2026-8888-Printer-Firmware-Unsigned-Update-via-HTTP preview

CVE-2026-8888-Printer-Firmware-Unsigned-Update-via-HTTP

GitHubgeorge0papasotiriou/cve-2026-8888-printer-firmware-unsigned-update-via-http

Demonstrates CVE-2026-8888, an unsigned printer firmware update over HTTP, including a malicious update server and vulnerable printer emulator for…
embedded-systems-securityexploitationfirmware-analysis+4
3 months ago
amthoneypot preview

amthoneypot

GitHubmlsebrell/amthoneypot

Honeypot for Intel's AMT Firmware Vulnerability CVE-2017-5689
defensive-toolsembedded-systems-securityiot-security+2
19 years ago
cve-2026-34473-unauthenticated-dos-zte-routers preview

cve-2026-34473-unauthenticated-dos-zte-routers

GitHubminanagehsalalma/cve-2026-34473-unauthenticated-dos-zte-routers

Technical breakdown of CVE-2026-34473, an unauthenticated denial of service affecting 17+ ZTE router models.
embedded-systems-securityexploitationfirmware-analysis+2
25 months ago
zyxel-wax650s-research-notebook-public preview

zyxel-wax650s-research-notebook-public

GitHubminanagehsalalma/zyxel-wax650s-research-notebook-public

Wiki-style research notebook for Zyxel WAX650S firmware emulation and vulnerability analysis
embedded-systems-securityfirmware-analysisreverse-engineering+2
26 months ago
cve-2026-86060 preview

cve-2026-86060

GitHubbahirul/cve-2026-86060

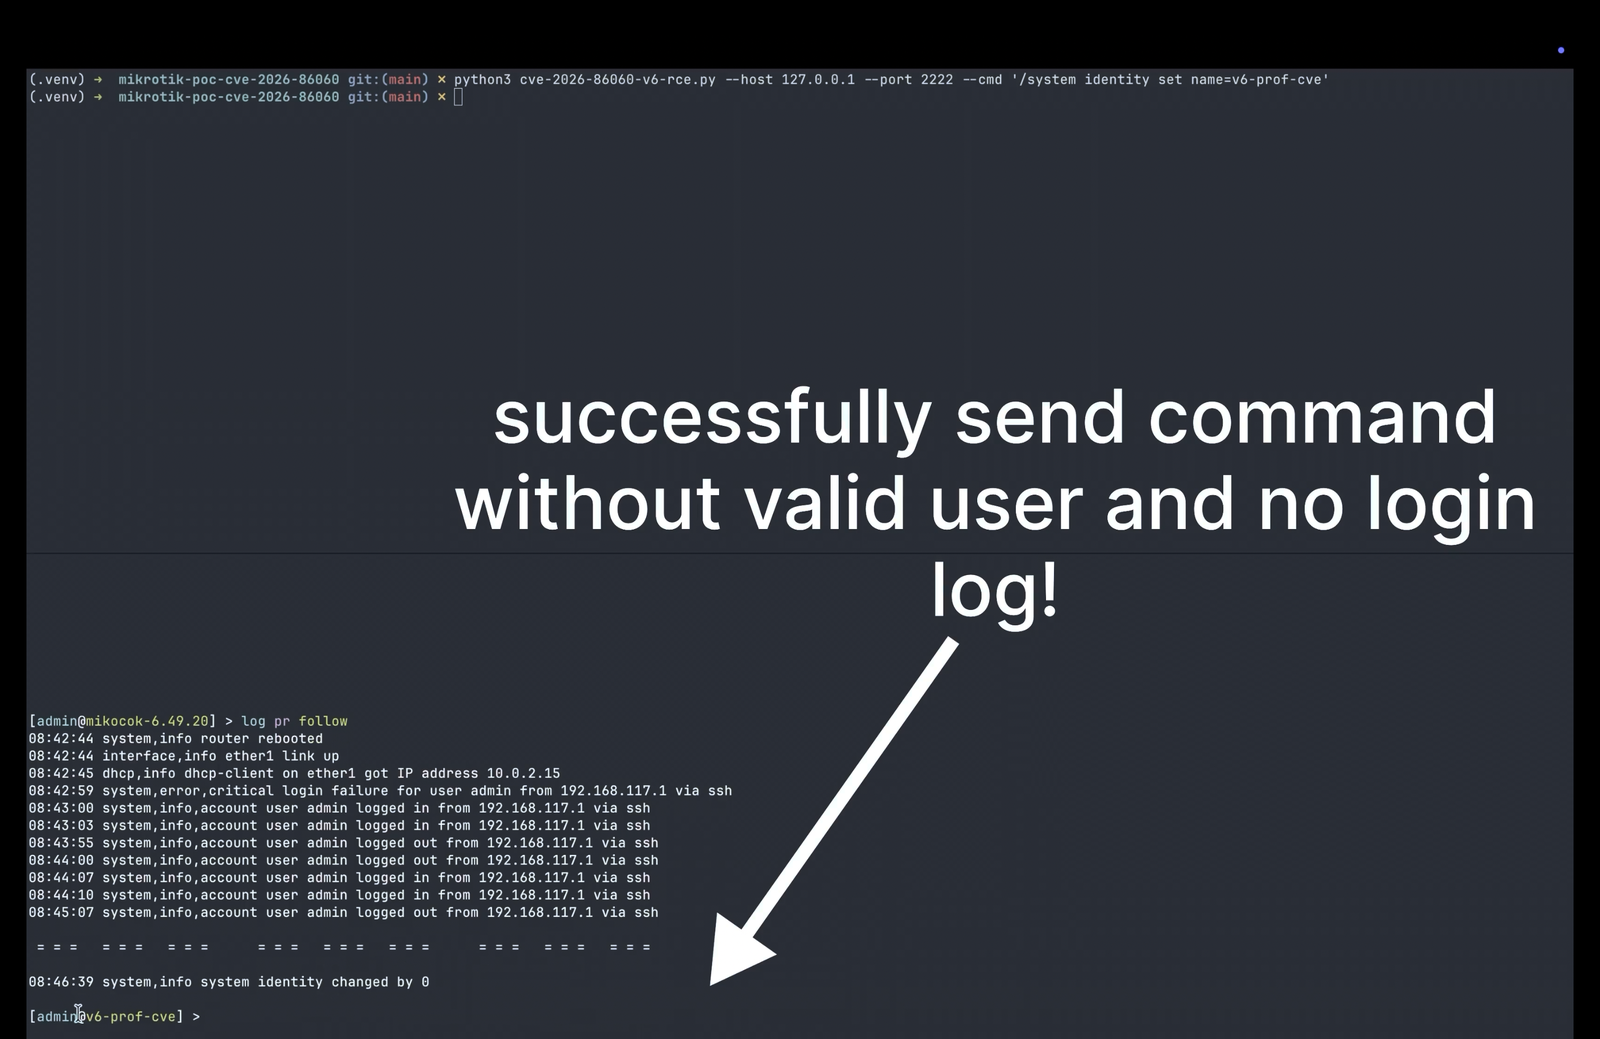
Advisory for CVE-2026-86060, a critical pre-auth privilege escalation in MikroTik RouterOS SSH, with impact analysis, detection guidance, and…
defensive-toolsembedded-systems-securityexploitation+4
11 month ago
CVE-2026-94095 preview

CVE-2026-94095

GitHubhackspeak/cve-2026-94095

PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.

embedded-systems-securityexploitationhardware-iot-security+5
11 month ago
CVE-2017-6206 preview

CVE-2017-6206

GitHubvarangamin/cve-2017-6206

The DGS-1510 Websmart switch series firmware has been found to have security vulneratiblies. The vulnerabilities include unauthenticated command…

exploitationiot-securitynetwork-security+3
26 years ago
CVE-2022-24654 preview

CVE-2022-24654

GitHubleonardobg/cve-2022-24654

Proof-of-concept exploit for authenticated stored cross-site scripting (XSS) vulnerability in INTELBRAS ATA 200 firmware 74.19.10.21, targeting the…
exploitationiot-securitypenetration-testing+2
24 years ago
CVE-2021-4045 preview

CVE-2021-4045

GitHubkaleth4/cve-2021-4045

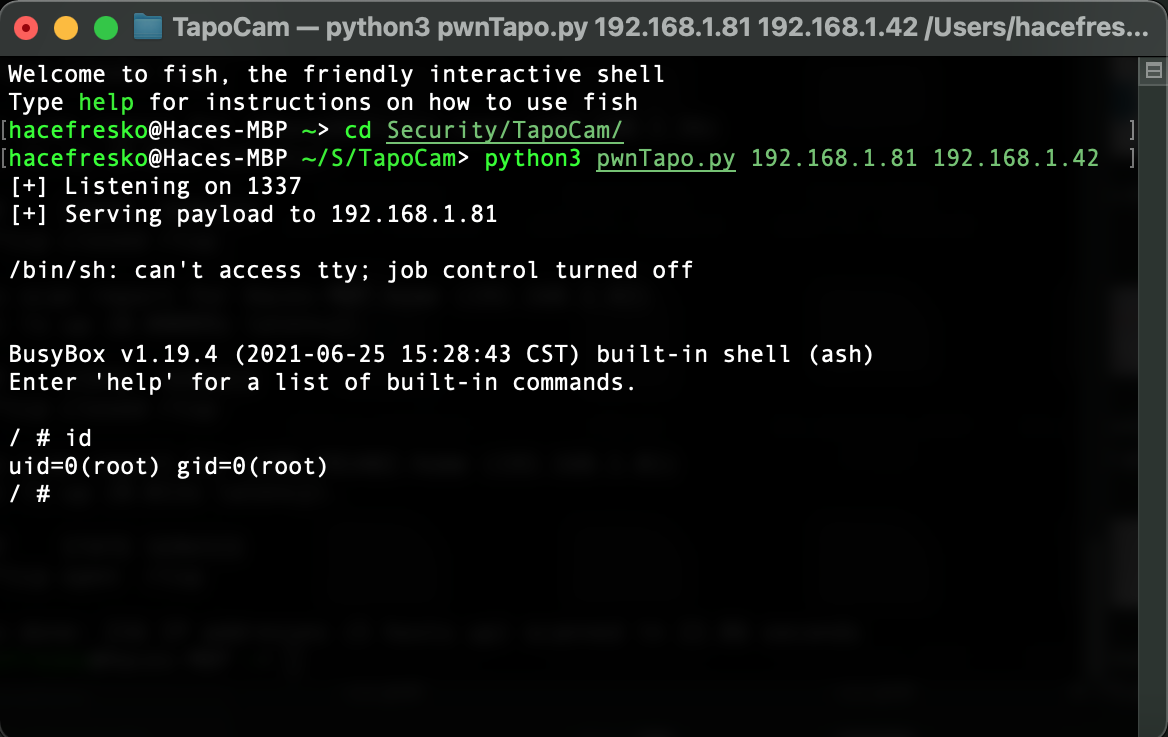
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
command-and-controlembedded-systems-securityexploitation+6
4 months ago
CVE-2021-4045 preview

CVE-2021-4045

GitHub234329a423853/cve-2021-4045

CVE-2021-4045 CVE-2021-4045 is a Command Injection vulnerability that allows Remote Code Execution in the TP-Link Tapo c200 IP camera. It affects all…
embedded-systems-securityexploitationfirmware-analysis+3
110 months ago
CVE-2026-56111 preview

CVE-2026-56111

GitHubchristbowel/cve-2026-56111

Proof-of-concept exploit for CVE-2026-56111, an out-of-bounds write in the M421 G-code handler of Marlin Firmware, demonstrating constrained memory…

binary-exploitationembedded-systems-securityexploitation+3
14 months ago
Previous1…345…29Next