
EXPLOIT-CVE-2021-44228
 joaovicdev/exploit-cve-2021-44228
Docker-based educational lab demonstrating Log4Shell (CVE-2021-44228) RCE exploitation with a vulnerable Java application, LDAP redirector, and…
educationexploitationlabs-practice+3
joaovicdev/exploit-cve-2021-44228Docker-based educational lab demonstrating Log4Shell (CVE-2021-44228) RCE exploitation with a vulnerable Java application, LDAP redirector, and…
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
 zemarkhos/cve-2026-44403-wingftp-v8.1.2-poc-exploit
CVE-2026-44403-WingFTP-v8.1.2-POC-Exploit
 0xs4n4tg/cve-2025-47812
CVE-2025-47812 Poc for wingdata HTB
 agilevatester/flaskcache_cve-2021-33026_poc
PoC exploit for CVE-2021-33026 that poisons Redis cache in Flask-Cache to achieve remote code execution via malicious pickle deserialization.
 kali-dass/cve-2021-44228-log4shell
Java-based proof-of-concept exploit for CVE-2021-44228 (Log4Shell) enabling remote command execution, OS information gathering, and arbitrary…
 dr4xp/pwnkit-helper
For CTF's and Safe Environments.... CVE-2021-4034 Local PrivEsc.
 chessredoffsec/cve-2023-26208
Python script with GUI for automated payload testing against login endpoints, designed for educational exploitation simulation and vulnerability…
 abiyeenzo/cve-2025-8671
PoC éducatif pour la vulnérabilité CVE-2025-8671 (DoS HTTP/2 sur lighttpd). À utiliser uniquement en laboratoire local.
 synfinner/cve-2023-35078
Easy and non-intrusive script to check for CVE-2023-35078
 rxerium/cve-2025-47812
Detection for CVE-2025-47812
 dkstar11q/blackash-cve-2025-47812
CVE-2025-47812
 chessredoffsec/cve-2023-26209
Python script with a Tkinter GUI for sending automated payloads of configurable size to a login endpoint, designed for educational testing of server…
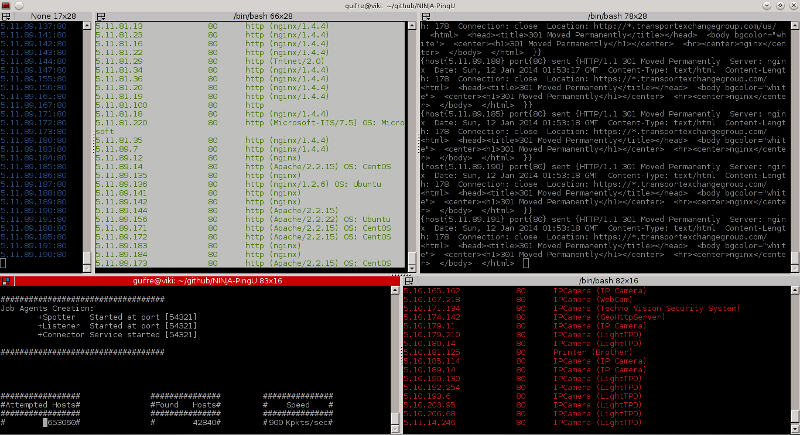 owasp/ninja-pingu
High-performance network scanner for large-scale IP and port scanning with service identification, embedded device detection, and vulnerability…