

Lab_Reportlab
 onion2203/lab_reportlab
This lab was set up to test CVE-2023-33733
educationexploitationlabs-practice+2
onion2203/lab_reportlabThis lab was set up to test CVE-2023-33733
 nxploited/cve-2025-2563
The User Registration & Membership WordPress plugin before 4.1.2 does not prevent users to set their account role when the Membership Addon is…
 abdullahmaqbool22/explosive-as-hell-mcs-qualifer-web-500
[First-Blood-XO] React Server Component endpoint vulnerable to CVE-2025-55182 (RCE) → enumerated SUID binaries → /usr/bin/perl had SUID set → used…
 rishipatidar/cve-2023-30212-poc-docker-file
This repository provides a Docker container for simulating the CVE-2023-30212 vulnerability, allowing you to practice and understand its impact. It…
 timtimxs/cve-2026-51947-advisory
Pivotal CRM's patch for an initial deserialization vulnerability was incomplete. The fix switched from BinaryFormatter to JSON.NET but left…
 alexs18/cve-2021-4773
Step-by-step tutorial demonstrating how to set up a vulnerable Apache 2.4.49 environment and exploit CVE-2021-41773 path traversal using Kali Linux…
 lixterclarixe/cve-2020-11019
In FreeRDP less than or equal to 2.0.0, when running with logger set to "WLOG_TRACE", a possible crash of application could occur due to a read of an…
 lorenzodegiorgi/setup-cve-2015-8562
Docker-compose to set up a test environment for exploiting CVE-2015-8562
 syntaxbearror/powershell-printnightmare
A collection of scripts to help set the appropriate registry keys for CVE-2021-34527
 swzhouu/cve-2020-26732
SKYWORTH GN542VF Hardware Version 2.0 and Software Version 2.0.0.16 does not set the Secure flag for the session cookie in an HTTPS session
 bombobombone/cve-2026-100381
Report and PoC for CVE-2026-100381, a DOM XSS in MediaWiki UploadWizard Flickr collection and set titles, with patch verification notes and a local…
 dafthack/mfasweep
A tool for checking if MFA is enabled on multiple Microsoft Services
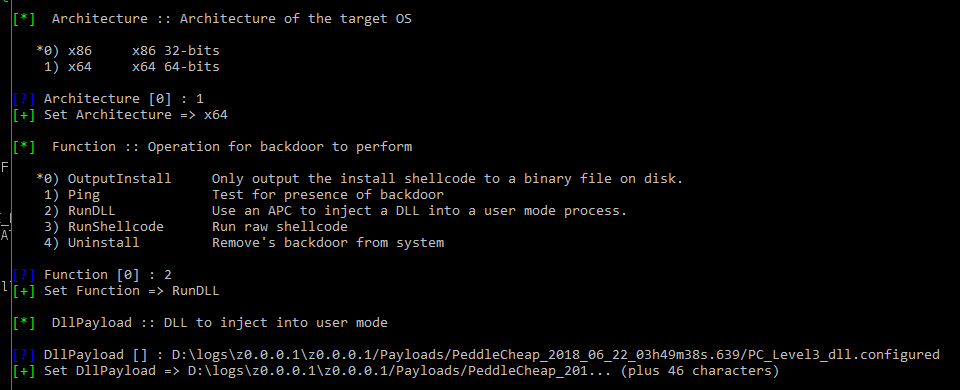 francisck/danderspritz_lab
A fully functional DanderSpritz lab in 2 commands
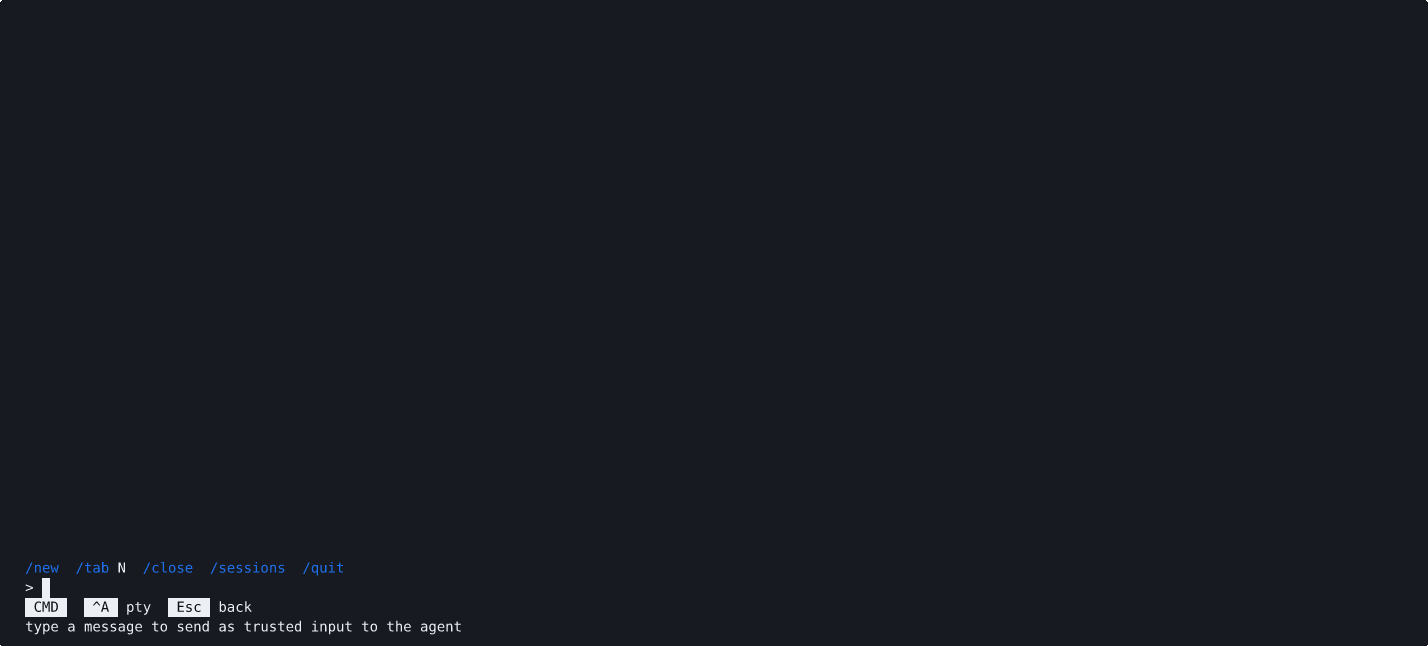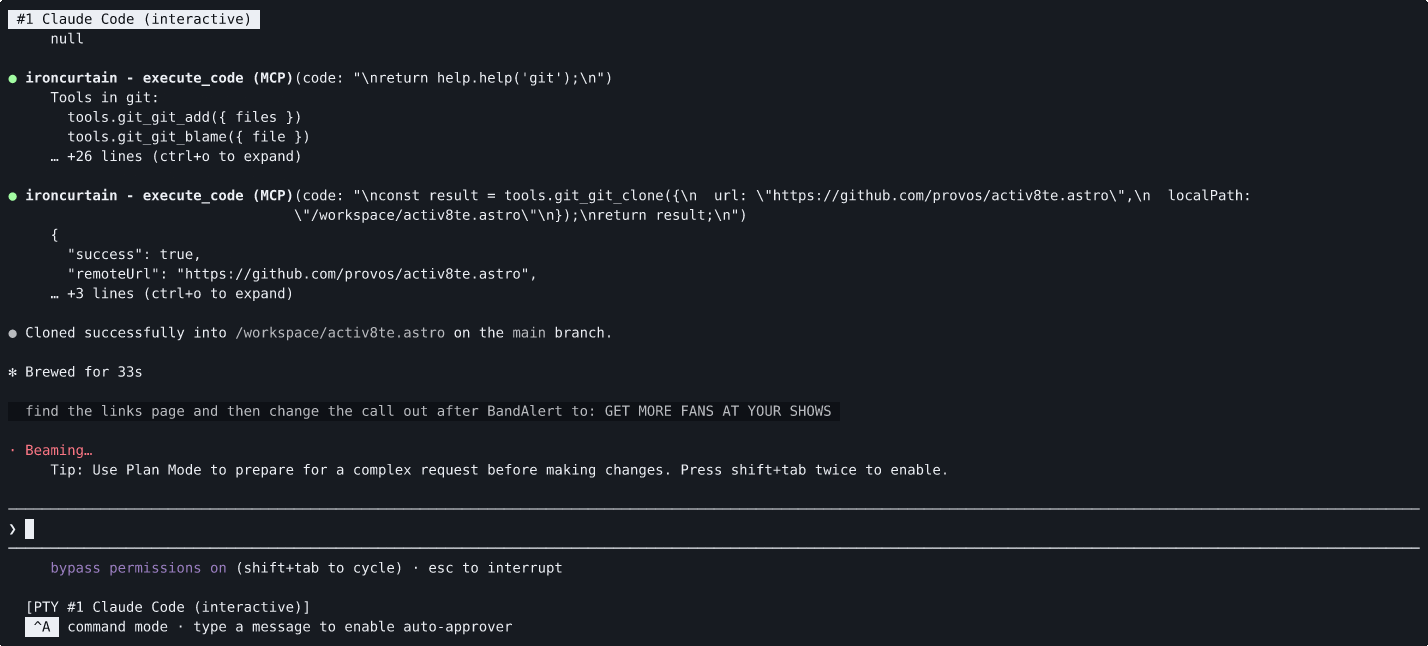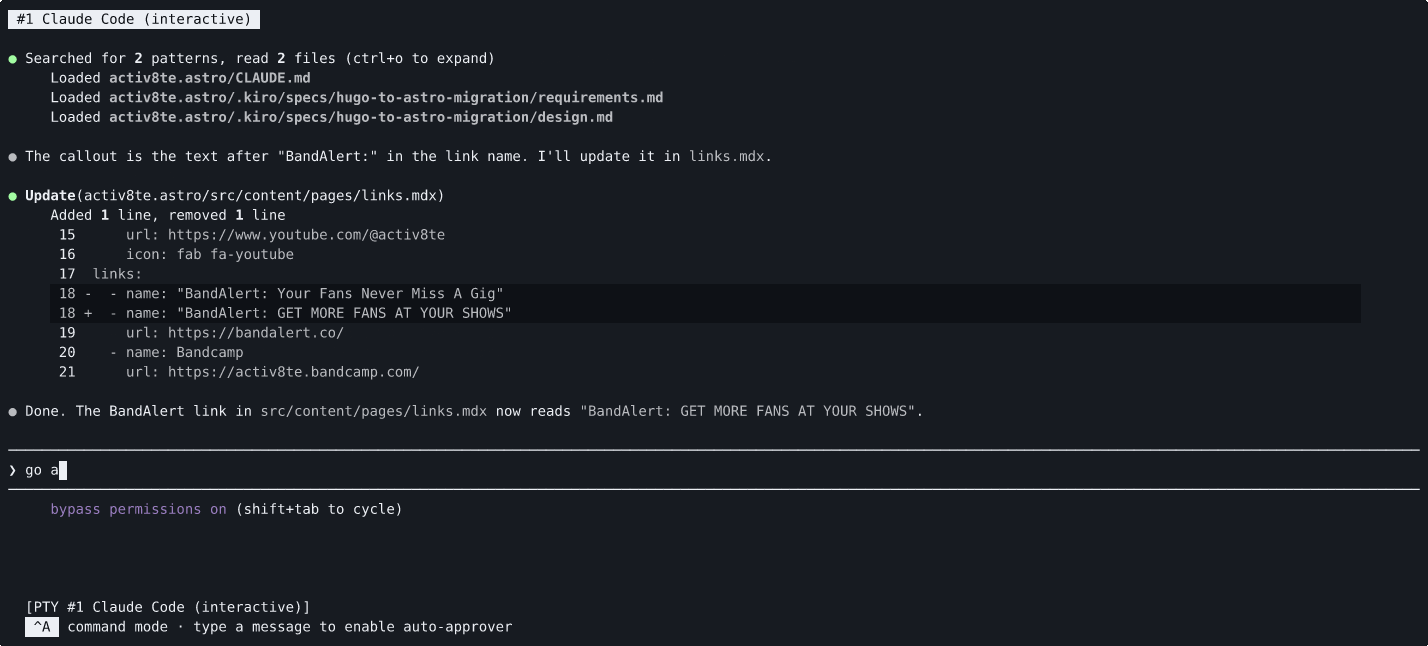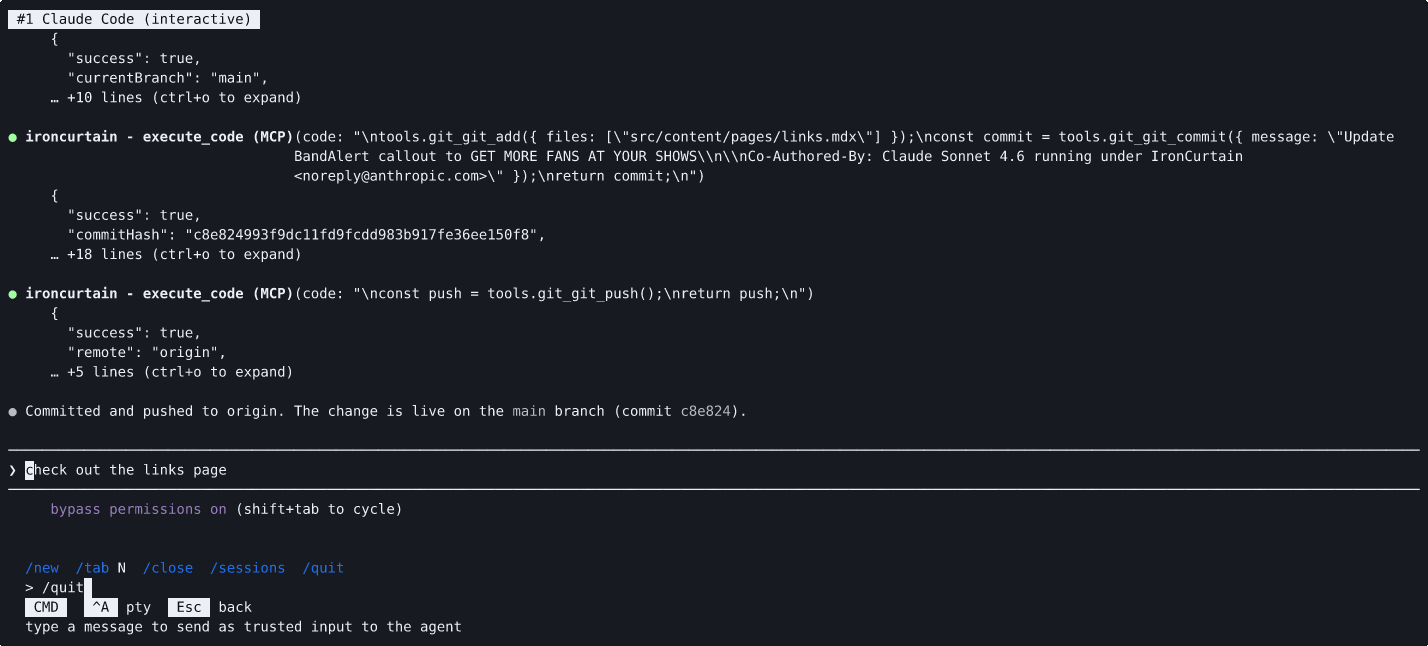 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)

 allanlw/svg-cheatsheet
A cheatsheet for exploiting server-side SVG processors.
 zierax/grafana-final-scanner
Grafana scanner with all public CVEs that I collected in one script to make grafana testing easier