

JAW
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
code-analysiscrawlerdatabase-security+5
soheilkhodayari/jawJAW: A Graph-based Security Analysis Framework for Client-side JavaScript
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
 owasp/riskassessmentframework
The Secure Coding Framework
 kai-one001/letta-cve-2025-51482-rce
Proof-of-concept exploit for CVE-2025-51482, demonstrating remote code execution via unsafe exec() usage and sandbox bypass in the Letta AI agent…
 mohammadnassiri/yaasa
Yet Another APK Static Analyzer
 trailofbits/test-fuzz
Rust macros and Cargo subcommand to automate fuzzing with afl.rs, including corpus generation and harness implementation, integrated with Rust's…
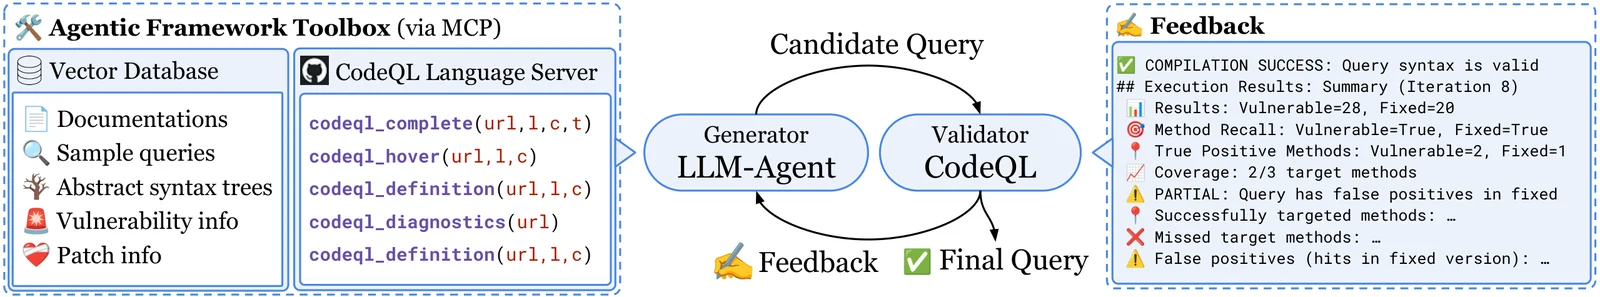 neuralprogram/qlcoder
Agentic Framework for Synthesizing CodeQL Queries
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
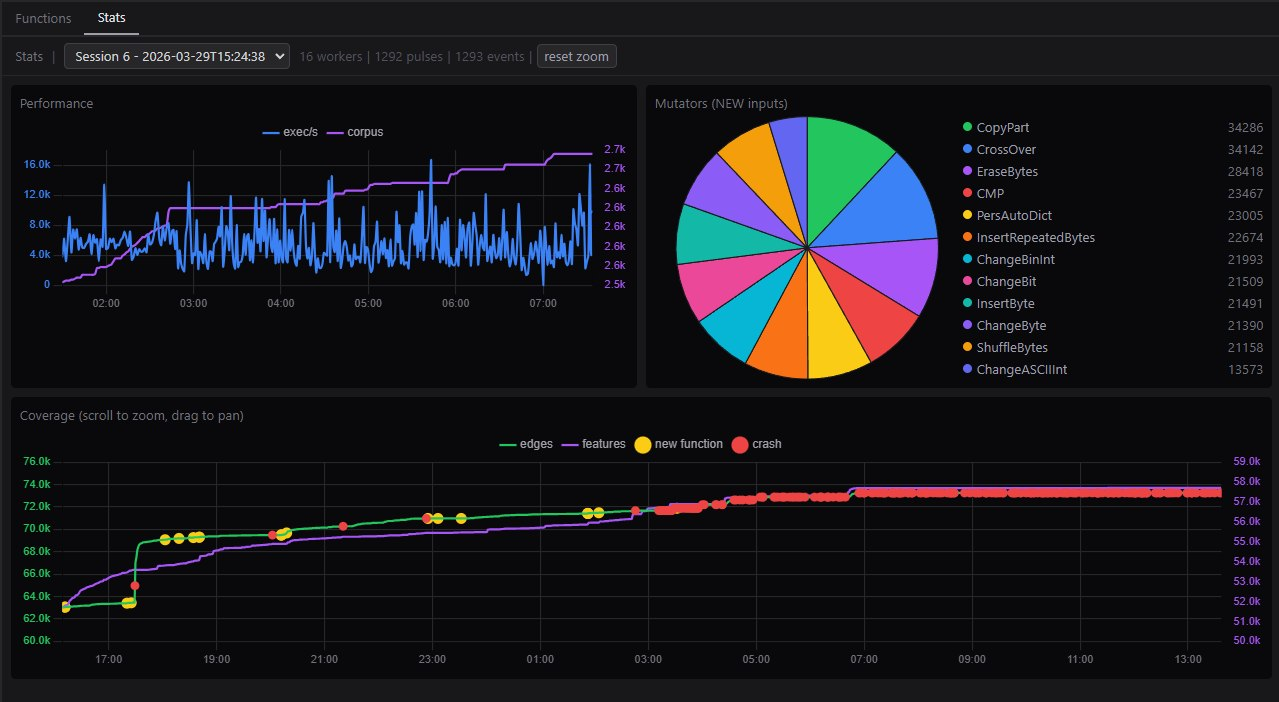 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 seanpesce/cve-2024-22243
Example exploitable scenarios for CVE-2024-22243 affecting the Spring framework (open redirect & SSRF).
 zr0n/react2shell
A complete framework for exploiting the vulnerability CVE-2025-55182
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 ak-cybe/cve-2025-68664-langgrinch-poc
A testing framework to identify and demonstrate deserialization vulnerabilities in LangChain Core (<0.3.81). Educational use only
 khidottrivi/cve-2022-22965
In-depth technical analysis of CVE-2022-22965 (Spring4Shell) with environment setup, debug walkthrough, and exploit chain breakdown for educational…
 meng-security/spring4shell-local-verification-lab
Spring Framework CVE-2022-22965 本地影响条件验证、版本升级修复与复测项目
 erroristotle/dvdr_llm
Ensemble framework for software vulnerability detection and repair using multiple large language models, with consensus analysis and evaluation tools…