
CVE-2018-13341
 rajchowdhury240/cve-2018-13341
This Tool Aims to Exploit the CVE-2018-13341
embedded-systems-securityexploitationhardware-iot-security+3
rajchowdhury240/cve-2018-13341This Tool Aims to Exploit the CVE-2018-13341
 robintrigon/cve-2023-36143
Maxprint Maxlink 1200G v3.4.11E has an OS command injection vulnerability in the "Diagnostic tool" functionality of the device.
 aliasrobotics/aztarna
aztarna, a footprinting tool for robots.
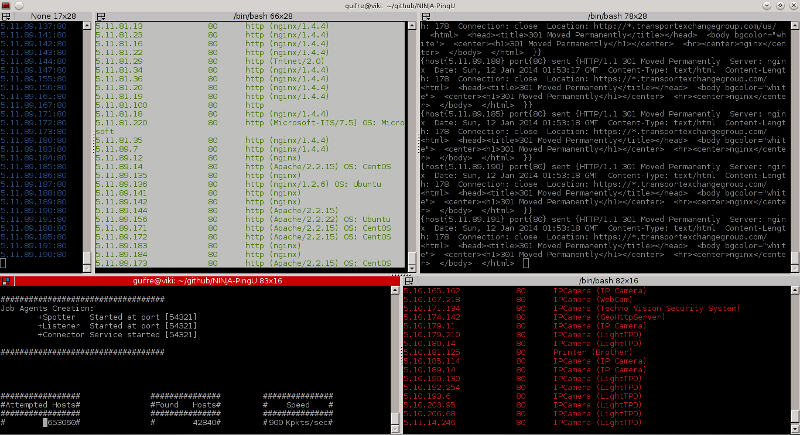 owasp/ninja-pingu
High-performance network scanner for large-scale IP and port scanning with service identification, embedded device detection, and vulnerability…
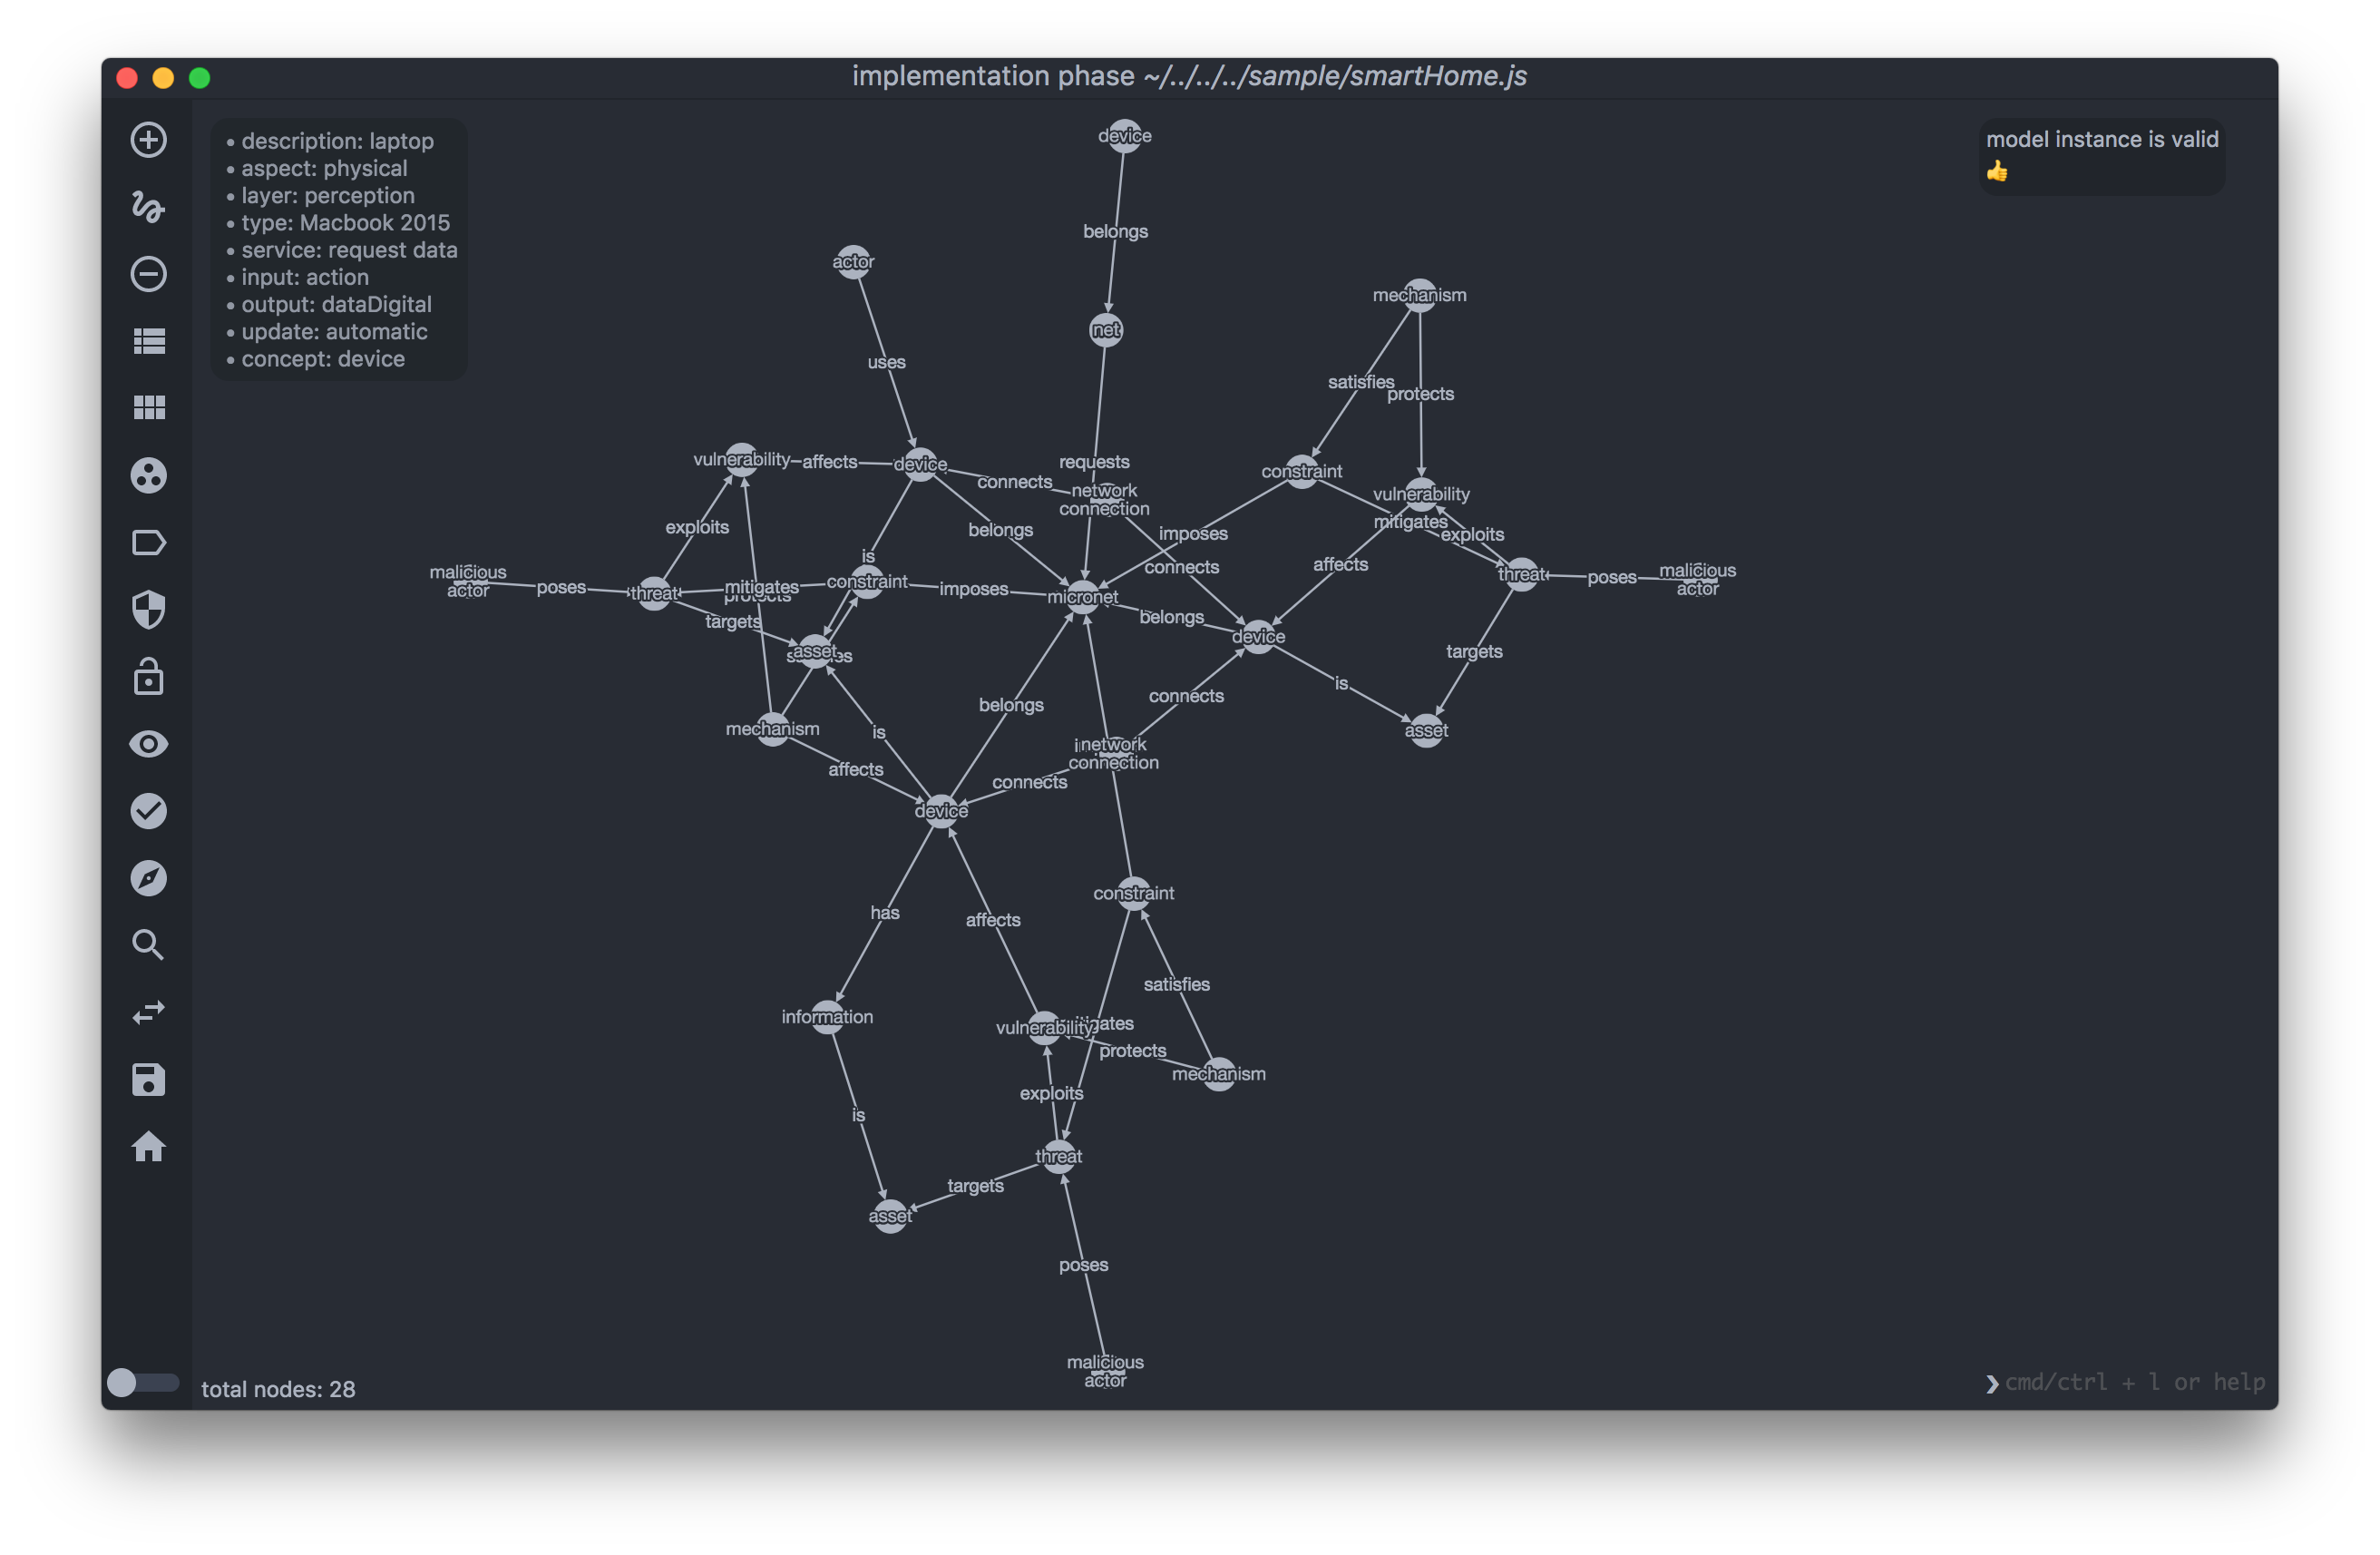 or3stis/apparatus
A graphical security analysis tool for IoT networks
 nccgroup/edidfuzzer
EDID (Enhanced Display Identification Data) Fuzzer
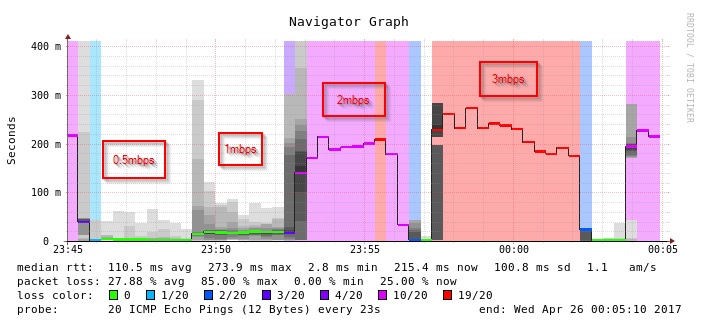 lunnova/puma6fail
CVE-2017-5693 Denial of service vulnerability in Puma 6 modems
 kosmokato/bad-dicom
Explotation framework for CVE-2019-11687
 f7p-h4nn1b4l/cve-2018-9995-dvr-credentials-extractor
This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.
 fwnavy/rmasmoke
RMASmoke main repo. CVE-2025-1122
 christopher-leese/cve-2015-1187-dir820l-firmware-reverse-engineering
Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…
 rehints/efixplorer
IDA plugin and loader for UEFI firmware analysis and reverse engineering automation
 d6fault/cve-2026-95675
Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…
 intel/intel-linux-processor-microcode-data-files
Official Intel microcode data files for updating processor firmware to mitigate security vulnerabilities and address functional issues on Linux…
 tothi/pwn-hisilicon-dvr
Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…
 binarly-io/fwhunt
The Binarly Firmware Hunt (FwHunt) rule format was designed to scan for known vulnerabilities in UEFI firmware.
 binarly-io/fwhunt-scan
Tools for analyzing UEFI firmware and checking UEFI modules with FwHunt rules