CVE-2026-26980-Ghost-CMS-Api

Go-based PoC for Ghost CMS Content API SQL injection (CVE-2026-26980). Verifies vulnerability, extracts admin credentials and API secrets, and…

Go-based PoC for Ghost CMS Content API SQL injection (CVE-2026-26980). Verifies vulnerability, extracts admin credentials and API secrets, and…

POC for CVE-2019-7616 / ESA-2019-09

Python PoC for CVE-2026-93399, an unauthenticated IDOR in Bookly <= 28.2 that leaks order tokens, exposes appointments, and rolls back bookings.

Sinilink XY-WFTX Wifi Remote Thermostat Module Temperature Controller

PoC Exploit CVE-2018-6389

Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…

Vulnerability & exploit intelligence — ExploitDB, NVD, Metasploit search with CVE→ATT&CK mapping and LogNorm/HuntForge integration | Part of Nebula…

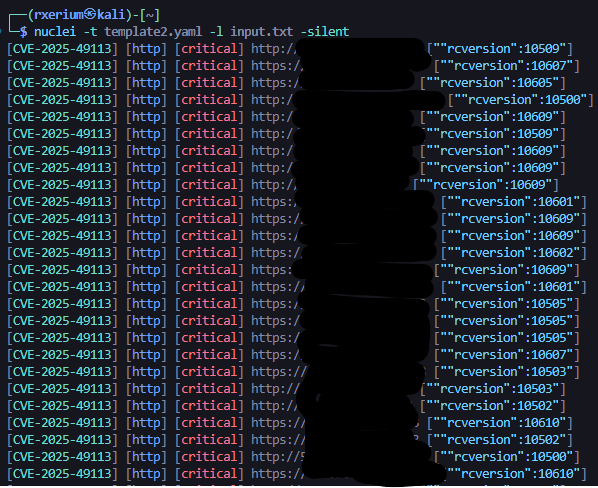
Detection for CVE-2025-49113

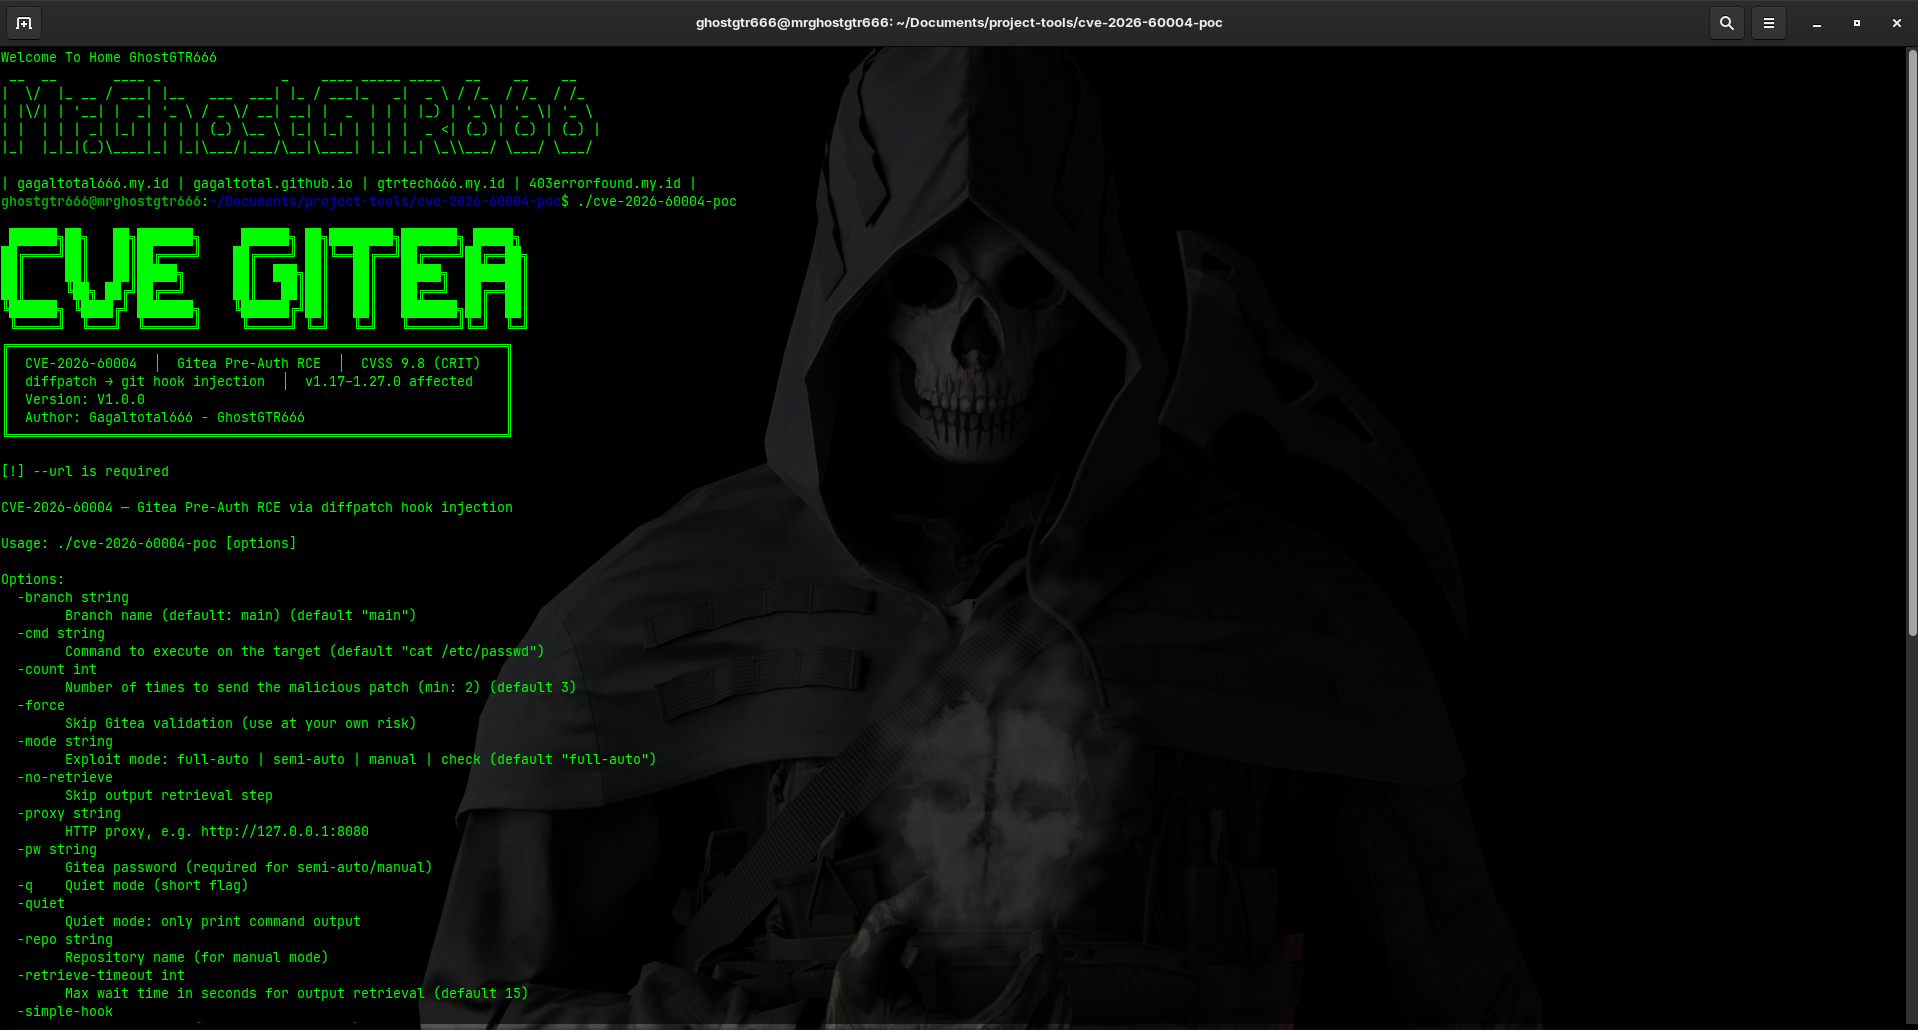
CVE-2026-60004 — Gitea Pre-Auth RCE via diffpatch hook injection

Proof of Concept: CVE-2026-21858 is vulnerability on n8n where unauthenticated remote attackers can access sensitive files.

Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…

wpsqli full SQLi extractor + dumper for CVE-2026-60137

SAML Single Sign On <= 5.4.4 - Unauthenticated Authentication Bypass via SAMLResponse Parameter

Proof-of-concept demonstrating a CMS AES-GCM short-tag authentication bypass in GnuPG's gpgsm (CVE-2026-57062). Forges a message that decrypts on…

CVE-2026-11961 — UserRegistration: WordPress User Registration <= 5.2.2 Privilege Escalation. Misconfigured Membership Roles → Unauthenticated Admin…

Extending of metasploit-framework

CVE-2026-6279

Security research disclosing CVE-2026-9794, an unauthenticated client ID enumeration flaw in Keycloak SAML ECP via faultstring oracle, fixed in…