
CVE-2020-3452_auto
 veids/cve-2020-3452_auto
Automated enumeration and file download tool exploiting CVE-2020-3452 in Cisco ASA devices, with Lua bytecode decompilation support.
exploitationinformation-gatheringpenetration-testing+2
veids/cve-2020-3452_autoAutomated enumeration and file download tool exploiting CVE-2020-3452 in Cisco ASA devices, with Lua bytecode decompilation support.
 vnyui/cve-2021-44228
Mass recognition tool for CVE-2021-44228
 ialejandrozalles/investigacionaplicacioncve-1999-0517
Research and exploitation tool targeting CVE-1999-0517, enabling vulnerability analysis and penetration testing for web-based security assessments.
 kkyehit/log4j_cve-2021-44228
Exploit tool for CVE-2021-44228 (Log4Shell) targeting vulnerable Log4j instances for remote code execution and security testing.
 nma-io/cve-2024-47176
A simple CVE-2024-47176 (cups_browsed) check tool written in go.
 trustcves/cve-2024-24398
Proof-of-concept or analysis tool for CVE-2024-24398, demonstrating exploitation of a specific vulnerability.
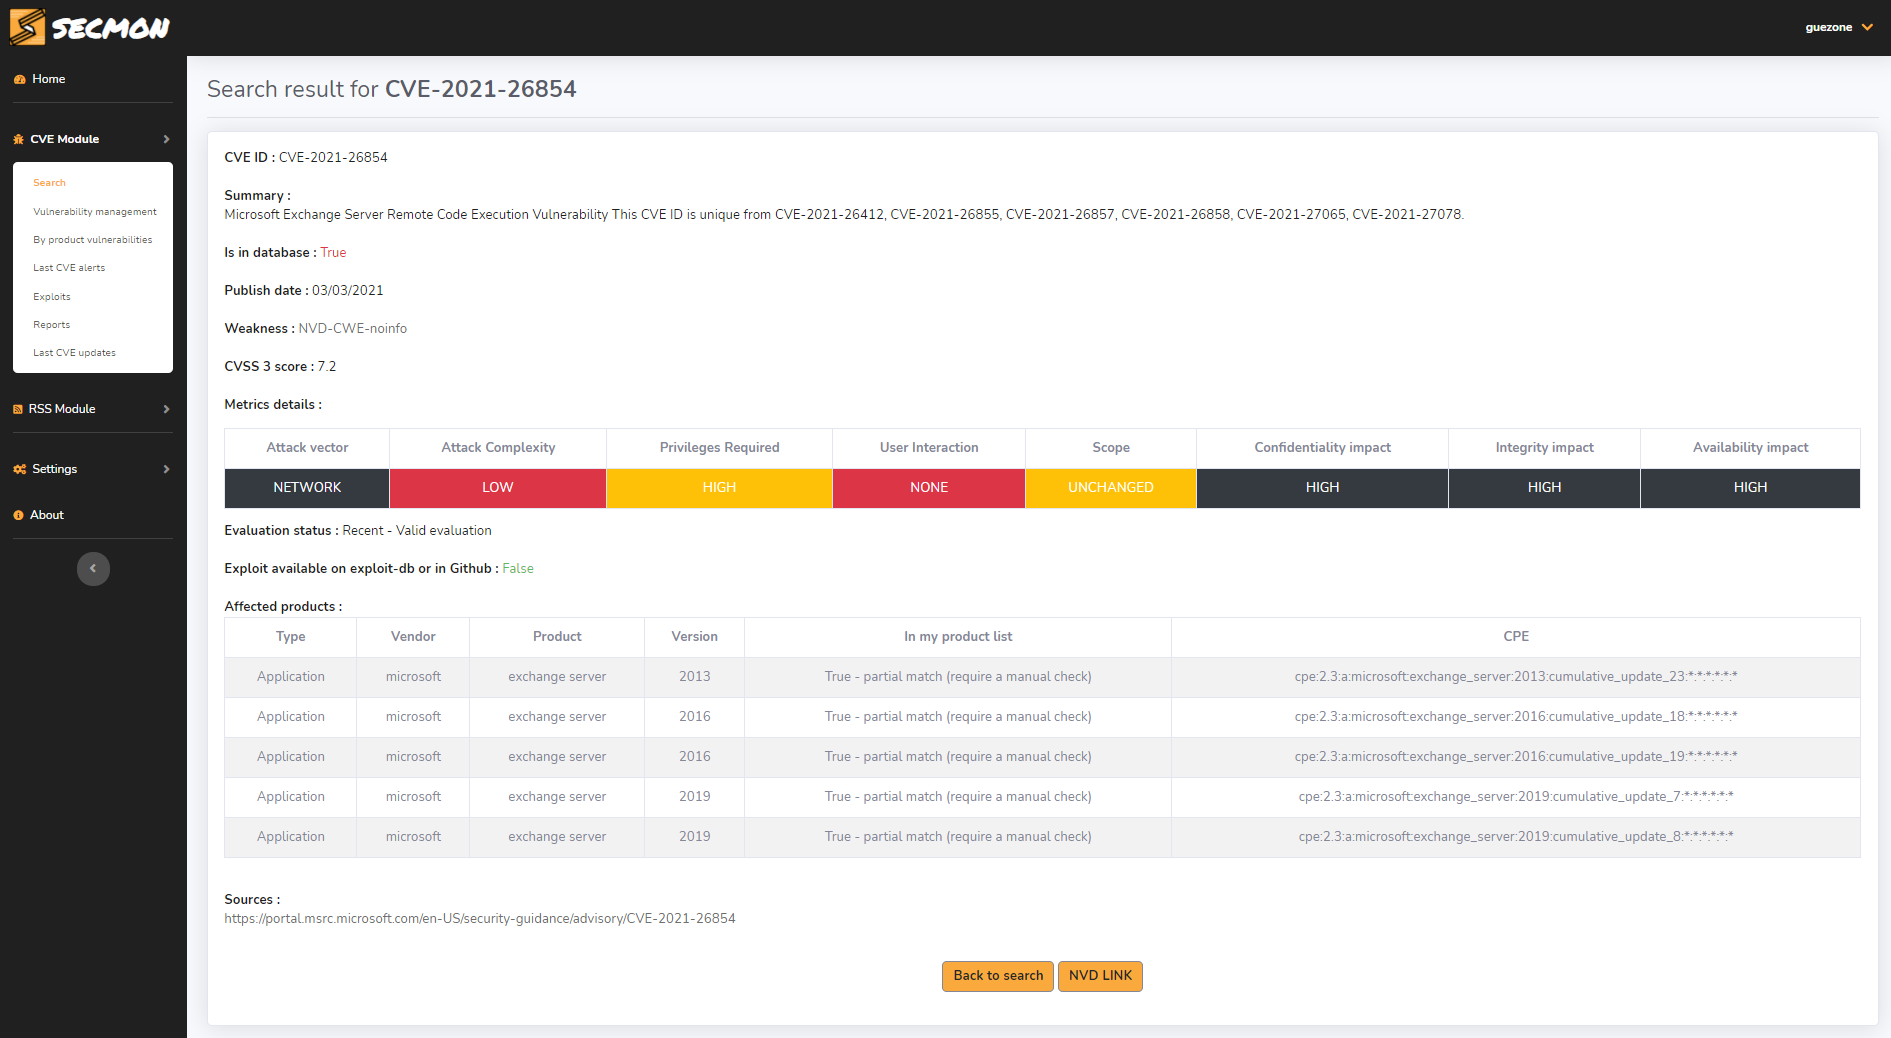 alb-uss/secmon
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.
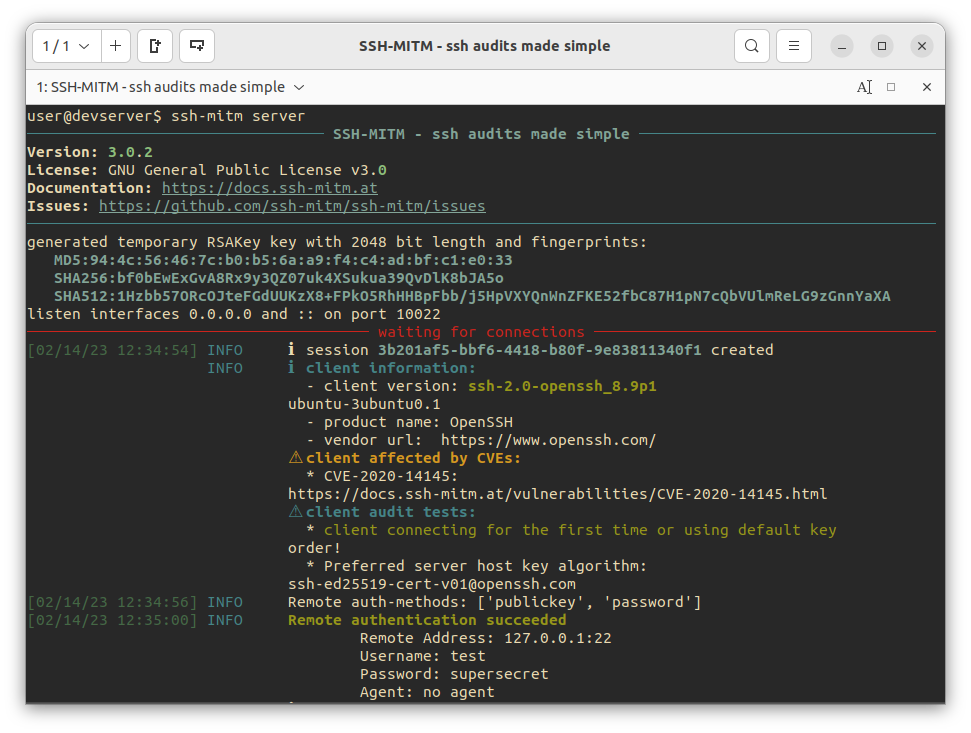 ssh-mitm/ssh-mitm
SSH-MITM - ssh audits made simple
 simsong/bulk_extractor
This is the development tree. Production downloads are at:

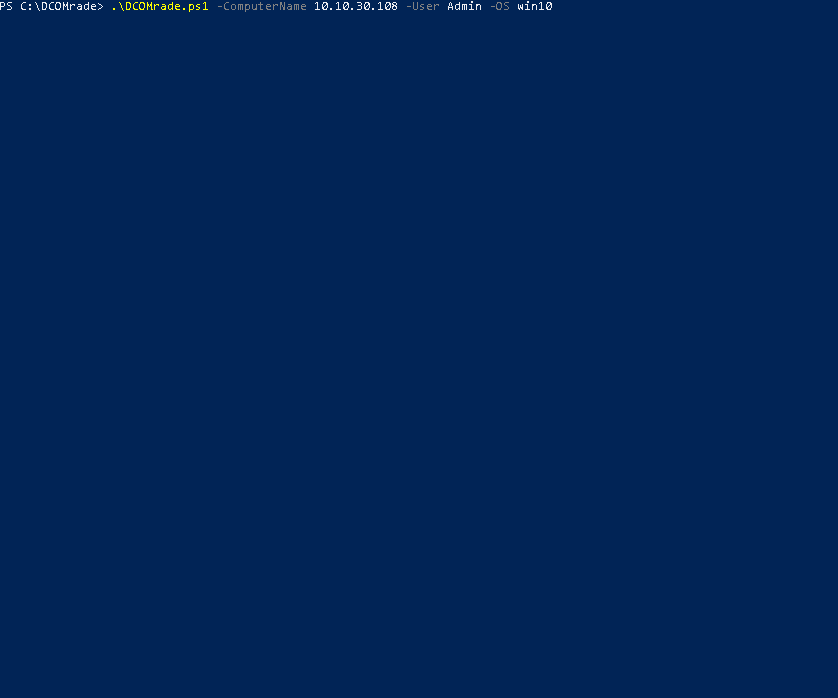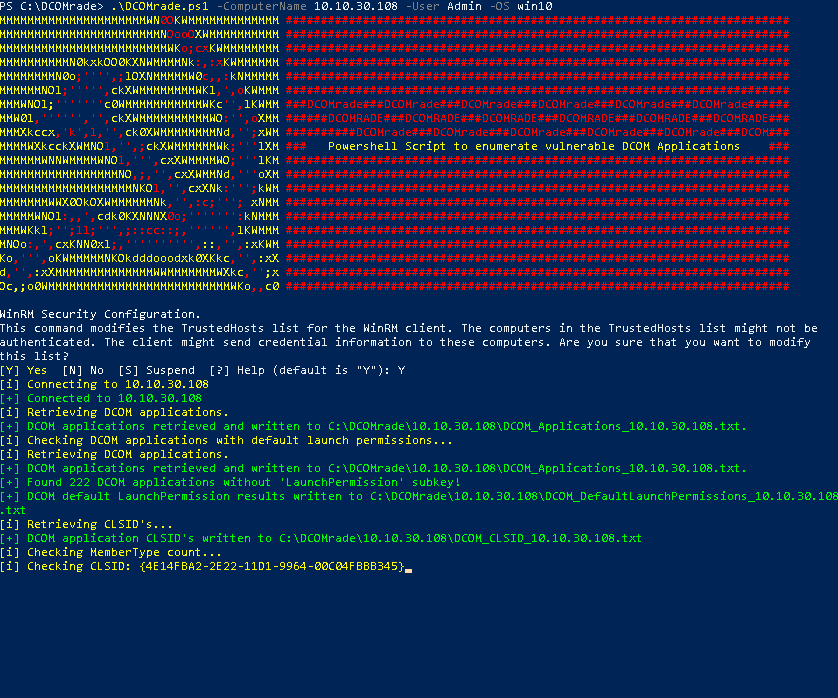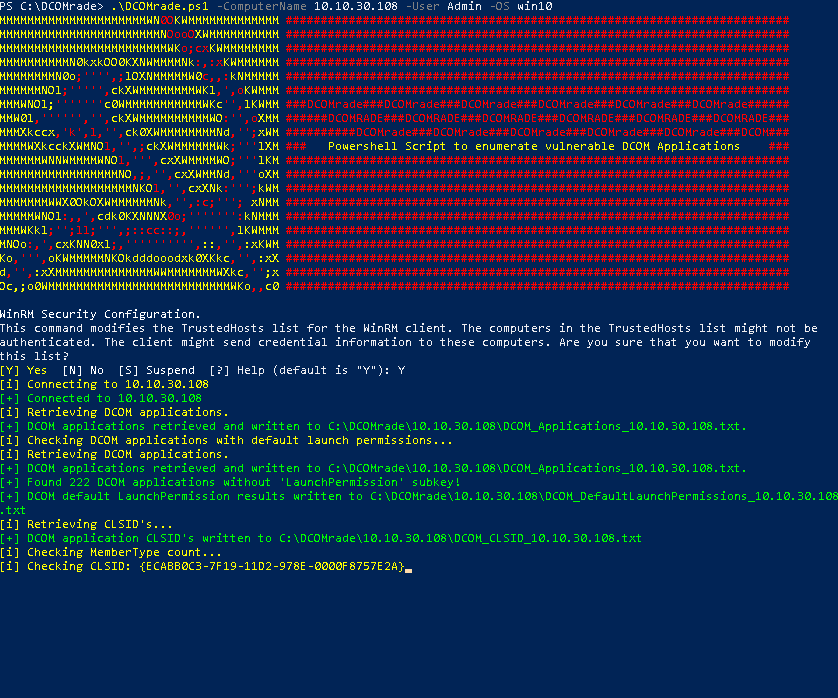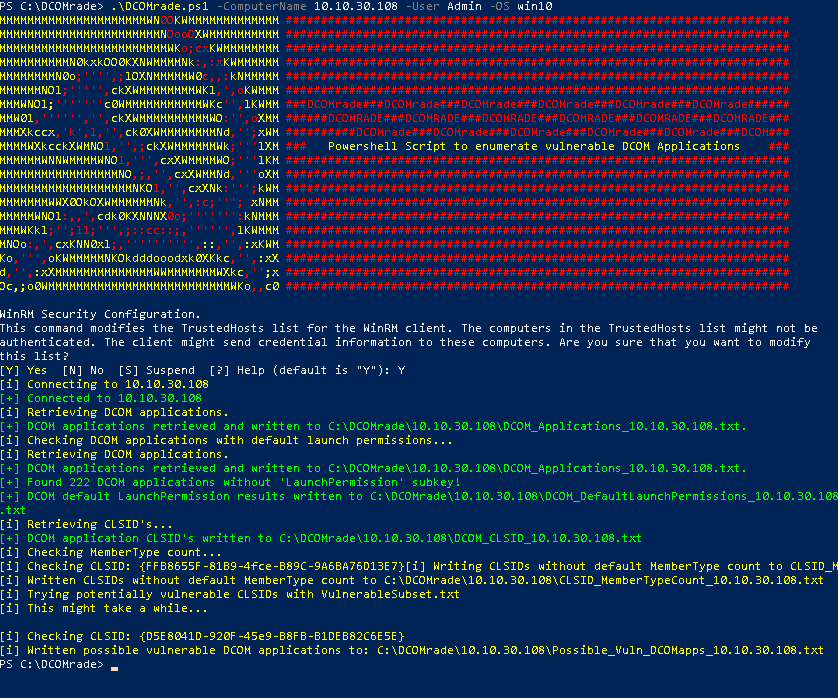 sud0woodo/dcomrade
Powershell script for enumerating vulnerable DCOM Applications
 netspi/ad-pathfinder
Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
 exploits-forsale/prefetch-tool
Windows KASLR bypass using prefetch side-channel
 h454nsec/cve-2023-42793
JetBrains TeamCity Authentication Bypass CVE-2023-42793 Exploit
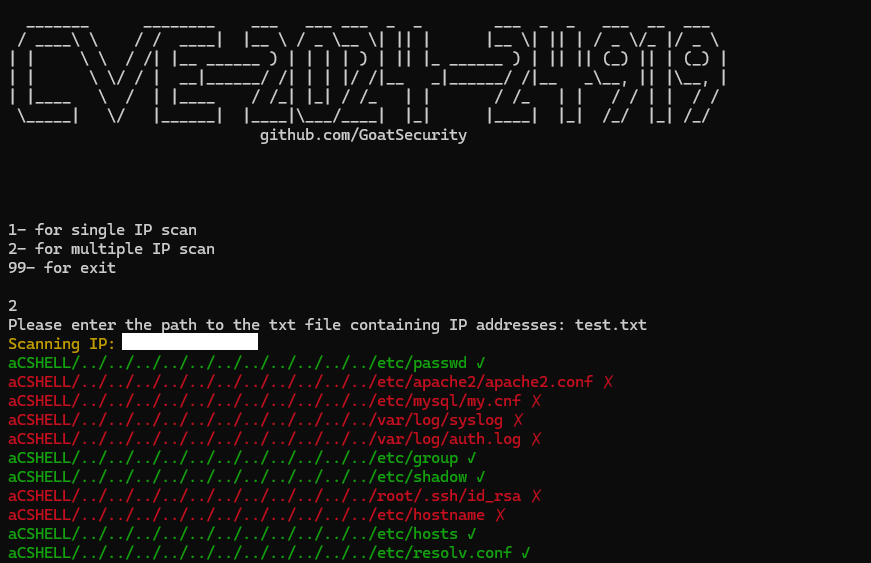 goatsecurity/cve-2024-24919
CVE-2024-24919 exploit
 ebrasha/abdal-anydesk-remote-ip-detector
CVE-2024-52940 - A zero-day vulnerability in AnyDesk's "Allow Direct Connections" feature, discovered and registered by Ebrahim Shafiei (EbraSha),…
 bughuntar/cve-2025-5777
CVE-2025-5777 Citrix NetScaler Memory Leak Exploit (CitrixBleed 2)
 p0dalirius/cve-2016-10956-mail-masta
MailMasta wordpress plugin Local File Inclusion vulnerability (CVE-2016-10956)