
CVE-2023-31606
 merbinr/cve-2023-31606
Documentation of CVE-2023-31606: a ReDoS vulnerability in Redcloth gem's sanitize_html function, with root cause analysis, CVSS 7.5 scoring, and…
educationpapers-researchstatic-code-analysis+2
2
merbinr/cve-2023-31606Documentation of CVE-2023-31606: a ReDoS vulnerability in Redcloth gem's sanitize_html function, with root cause analysis, CVSS 7.5 scoring, and…
 shoucheng3/esapi__esapi-java-legacy_cve-2022-24891_2-2-3-1
OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…
 nvisium-jack-mannino/owasp-goatdroid-project
*This project is no longer maintained* OWASP GoatDroid is a fully functional and self-contained training environment for educating developers and…
 scriptingxss/iotgoat
IoTGoat is a deliberately insecure firmware based on OpenWrt.
 wireghoul/lbmap
Advanced HTTP fingerprinting PoC
 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
 mseclab/pyjfuzz
PyJFuzz - Python JSON Fuzzer
 aws/http-desync-guardian
Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
 impact-i/x8-burp
Hidden parameters discovery suite
 emo-crab/slinger
An HTTP client specifically developed for security researchers
 raz0r/burp-radamsa
Radamsa fuzzer extension for Burp Suite
 projectdiscovery/collaborator
BurpSuite Standard/Private Collaborator Library
 infobyte/alexafaraday
Alexa skill example for Faraday API
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 ex-cal1bur/cve-2026-44596
YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
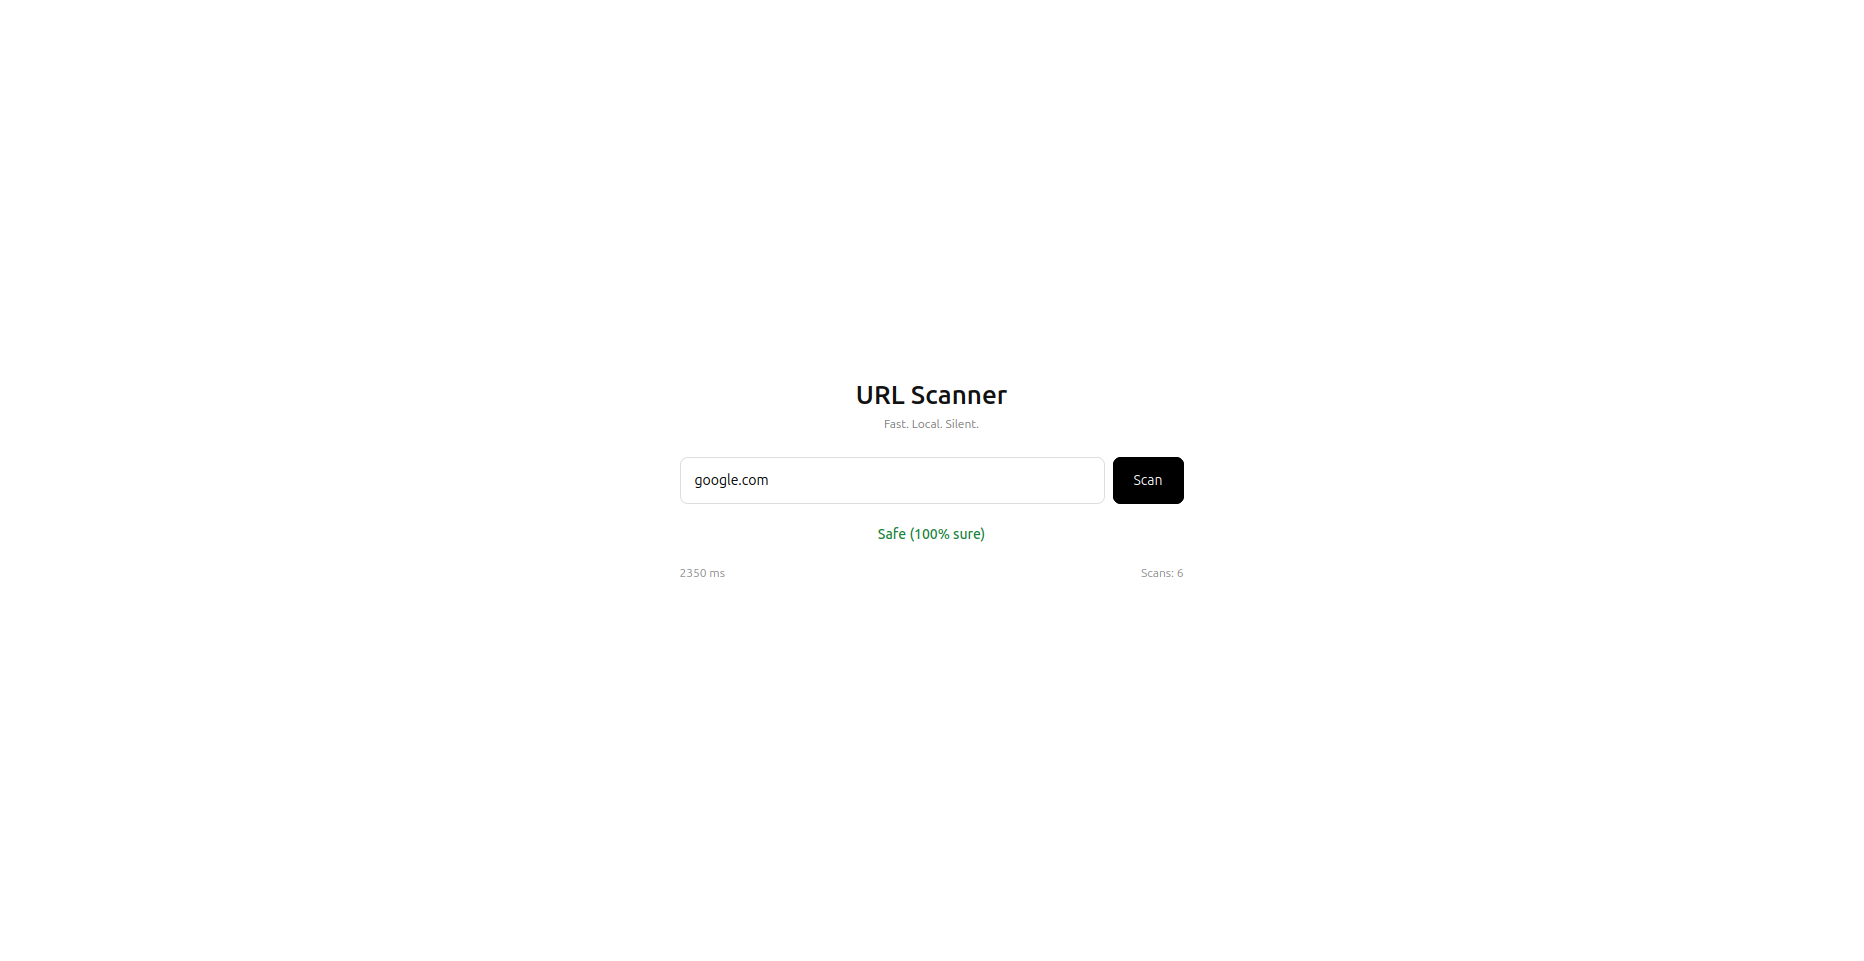 mannansainicyber/url_checker
Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…