Log4J-Log4Shell-CVE-2021-44228-Spring-Boot-Test-Service

Dockerized Spring Boot service intentionally vulnerable to Log4Shell (CVE-2021-44228) for testing detection tools, payloads, and exploit capabilities…

Dockerized Spring Boot service intentionally vulnerable to Log4Shell (CVE-2021-44228) for testing detection tools, payloads, and exploit capabilities…

Proof of concept of CVE-2017-1000117

🐺 Vulfy – Fast Rust based package version scanner

Automated exploit for CVE-2012-3153 / CVE-2012-3152

Fix for the CVE-2021-36934

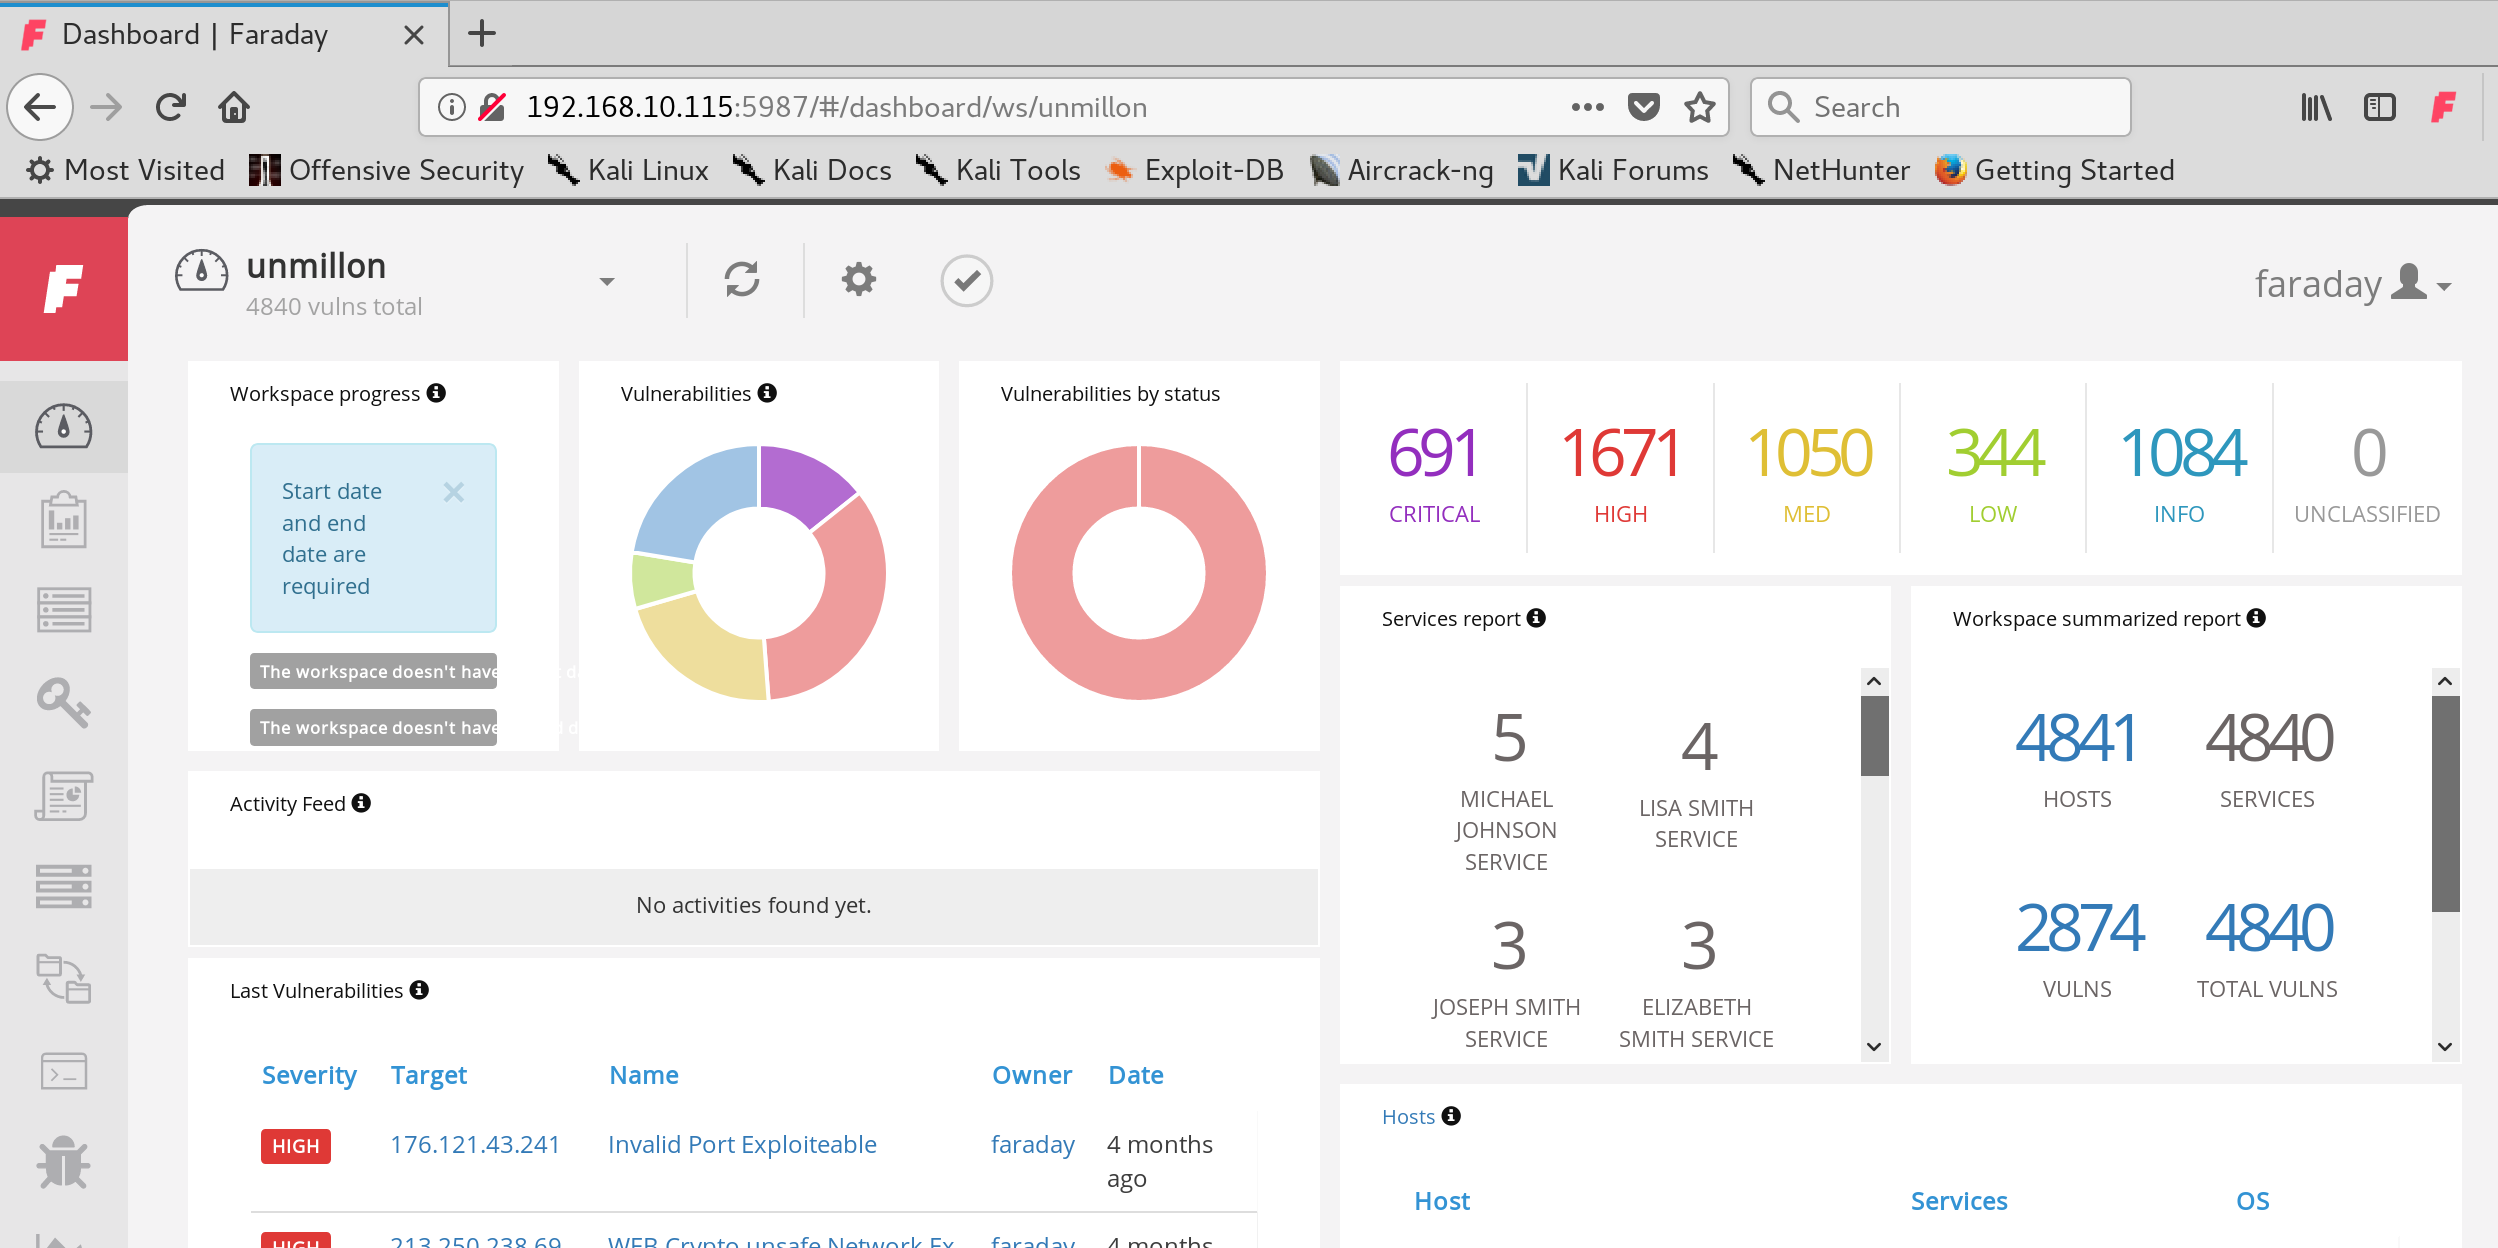
A browser extension for faradaysec platform https://faradaysec.com

Shitrix : CVE-2019-19781 - Remote Code Execution on Citrix ADC Netscaler exploit

Proof-of-concept exploit for Android privilege escalation vulnerability CVE-2015-6637, demonstrating memory corruption to gain elevated privileges.

CVE-2021-38647 POC for RCE

Exploit scanner for CVE-2022-26134 in Atlassian Confluence. Uses Shodan to find vulnerable hosts, then executes commands via the OGNL injection…

OpenSSH ProxyCommand RCE


Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.

Apply class remove process from ear/war/jar/zip archive, see https://logging.apache.org/log4j/2.x/

A fix for CVE-2019-11358 (prototype pollution in jquery)

Exploit script for Apache Tomcat RCE via deserialization (CVE-2020-9484), leveraging ysoserial payloads to achieve remote code execution.

Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…

Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…