
CVE-2019-13361
 lodi-g/cve-2019-13361
Smanos W100 1.0.0 devices have Insecure Permissions, exploitable by an attacker on the same Wi-Fi network.
exploitationiot-securitypenetration-testing+2
lodi-g/cve-2019-13361Smanos W100 1.0.0 devices have Insecure Permissions, exploitable by an attacker on the same Wi-Fi network.
 lequockhanh2k/tool_exploit_password_camera_cve-2018-9995
Exploit tool for CVE-2018-9995 that extracts credentials from vulnerable DVR devices via Google dorking and direct IP access.
 athos-zago/cve-2024-30973
POC VIDEO - https://youtu.be/hNzmkJj-ImM?si=NF0yoSL578rNy7wN
 exploitwritter/cve-2022-25064
This script exploits a remote command execution vulnerability in the TPLink WR840N router, using the configure function IPv6 protocol.
 yozarseef95/cve-2023-31594
IC Realtime ICIP-P2012T 2.420 is vulnerable to Incorrect Access Control
 cappricio-securities/cve-2024-5947
Deep Sea Electronics DSE855 - Authentication Bypass
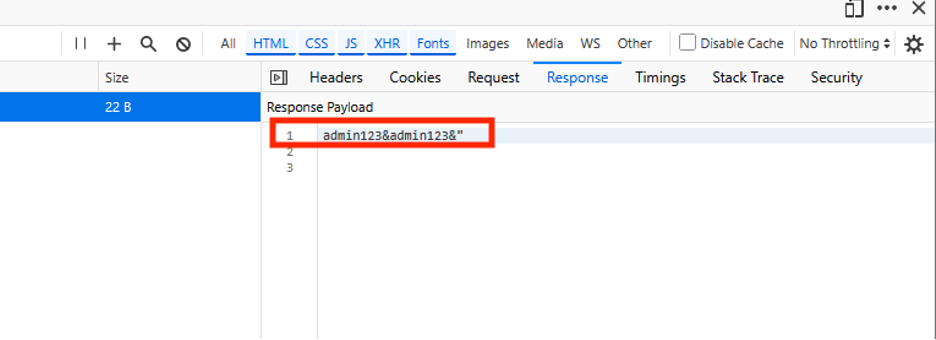 weedl/cve-2025-45620
Disclosure of client-side authentication bypass in AVer camera web interface exposing unencrypted credentials via network traffic monitoring.
 corelight/boa-detector
A vulnerable Boa web server detector.
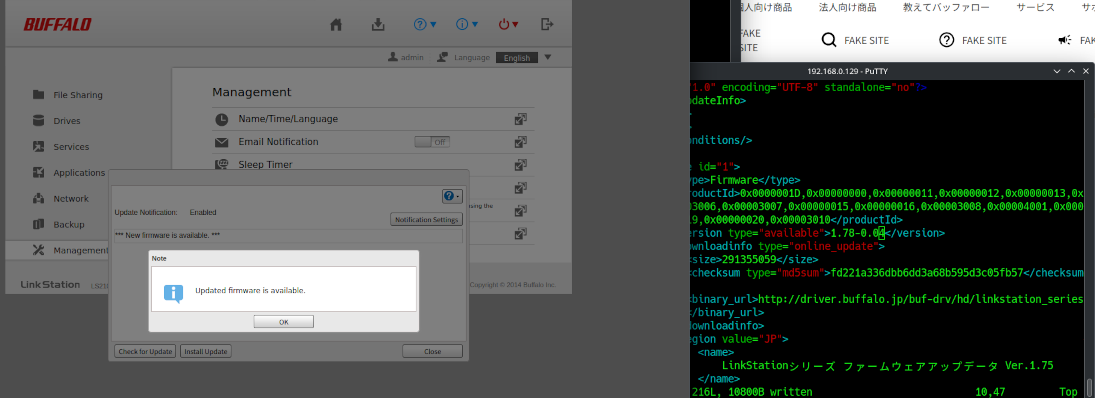 christopher-pace/cve-2023-51073
Firmware Update Server Verification Vulnerability on Buffalo LS210D Version 1.78-0.03
 dopheide-esnet/zeek-jetdirect
Zeek package to detect exploitation attempts of CVE-2017-2741 targeting HP JetDirect printers via network traffic analysis.
 kaisersource/cve-2021-3166
Proof-of-concept exploit for CVE-2021-3166 targeting ASUS DSL-N14U routers via malicious firmware upload, triggering a denial-of-service condition.
 lequockhanh2k/tool_camera_exploit_netwave_cve-2018-6479
Exploit tool for CVE-2018-6479, a denial-of-service vulnerability in Netwave IP cameras. Targets IoT devices to trigger temporary service disruption…
 c0nyy/iot_vuln
Proof-of-concept exploits for IoT device vulnerabilities, including TOTOLINK login bypass CVEs, with detailed technical analysis and reproduction…
 redfox-security/digisol-dg-gr1321-s-improper-access-control-cve-2024-4231
Exploit for CVE-2024-4231, an improper access control vulnerability in Digisol DG-GR1321 routers, allowing unauthorized access to sensitive…
 dearpan/cve-2018-9995
Exploit for CVE-2018-9995 targeting DVR devices. Sends a crafted Cookie header to retrieve plaintext admin credentials from the web control panel.
 str0ng4le/cve-2022-30114
Proof-of-concept exploit for CVE-2022-30114, a heap-based buffer overflow in Fastweb FastGate routers. Sends a crafted HTTP Authorization header to…
 exploitwritter/cve-2022-25062
This script exploits a vulnerability (IoF) in the TPLink WR840N router, using a field for injecting code in the module DNS.
 db44k/cve-2020-12124
Proof-of-concept exploit for CVE-2020-12124, a command injection vulnerability in Wavlink WN530H4 routers via the /cgi-bin/live_api.cgi endpoint,…