

toolbox
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
api-security-testingcrawlerdynamic-analysis-sandboxing+8
437 days ago
go-appsec/toolboxCollaborative application security testing between humans and agents via CLI and MCP
 straight-tamago/nocamerasound
CVE-2022-46689
 sec-tools/litefuzz
A multi-platform fuzzer for poking at userland binaries, network clients and servers
 deetl/cve-2023-24055
POC and Scanner for CVE-2023-24055
 jjensn/cve-2024-36877
Proof-of-concept exploit for CVE-2024-36877 targeting firmware vulnerabilities, with detailed write-up and binary exploitation techniques.
 isee857/cve-2025-0108-poc
Palo Alto Networks PAN-OS 身份验证绕过漏洞批量检测脚本(CVE-2025-0108)
 win3zz/cve-2023-43261
CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption
 s1lkys/cve-2020-15906
Writeup of CVE-2020-15906
 gnoxter/mountain_goat
A PoC demonstrating techniques exploiting CVE-2016-5696 Off-Path TCP Exploits: Global Rate Limit Considered Dangerous
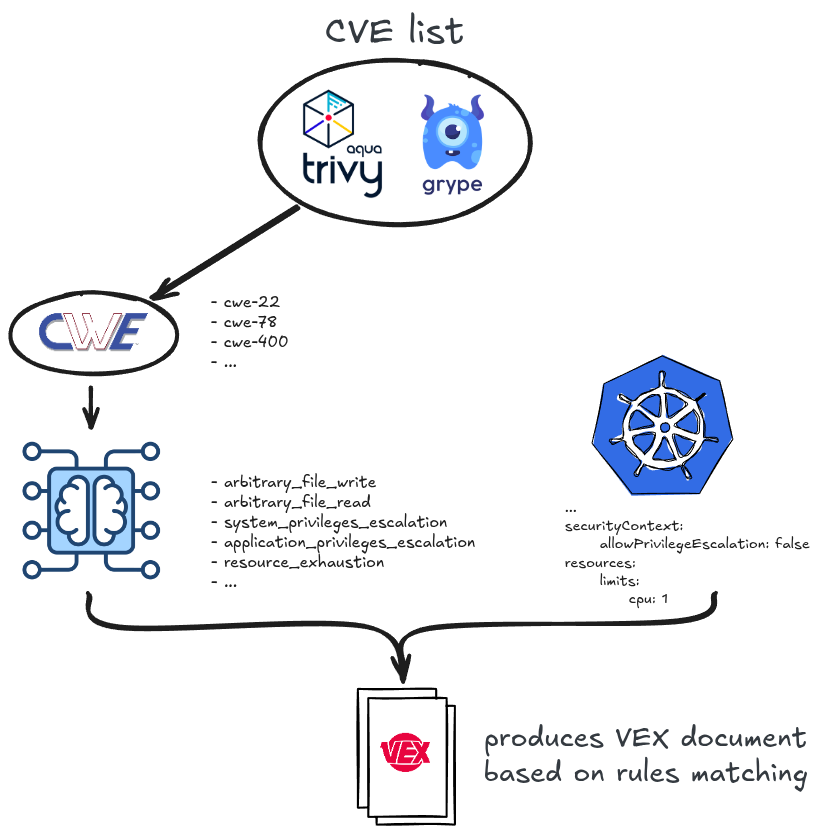 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 osmankandemir/web-wordlist-generator
Scans web applications to generate context-specific wordlists for security testing, asset discovery, and preliminary vulnerability analysis.
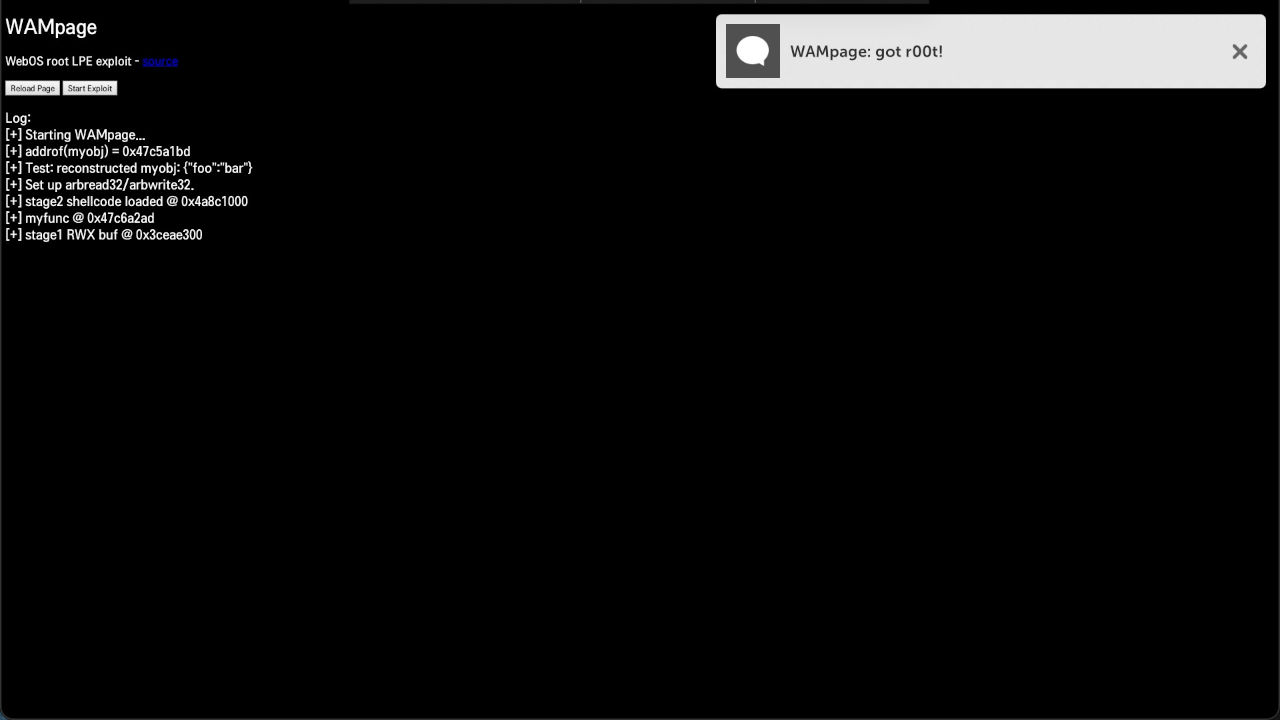 davidbuchanan314/wampage
WAMpage - A WebOS root LPE exploit chain (CVE-2022-23731)
 gensecaihq/cve-2024-3094-vulnerability-checker-fixer
Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…
 xmzyshypnc/cve-2021-30551
my exp for chrome V8 CVE-2021-30551
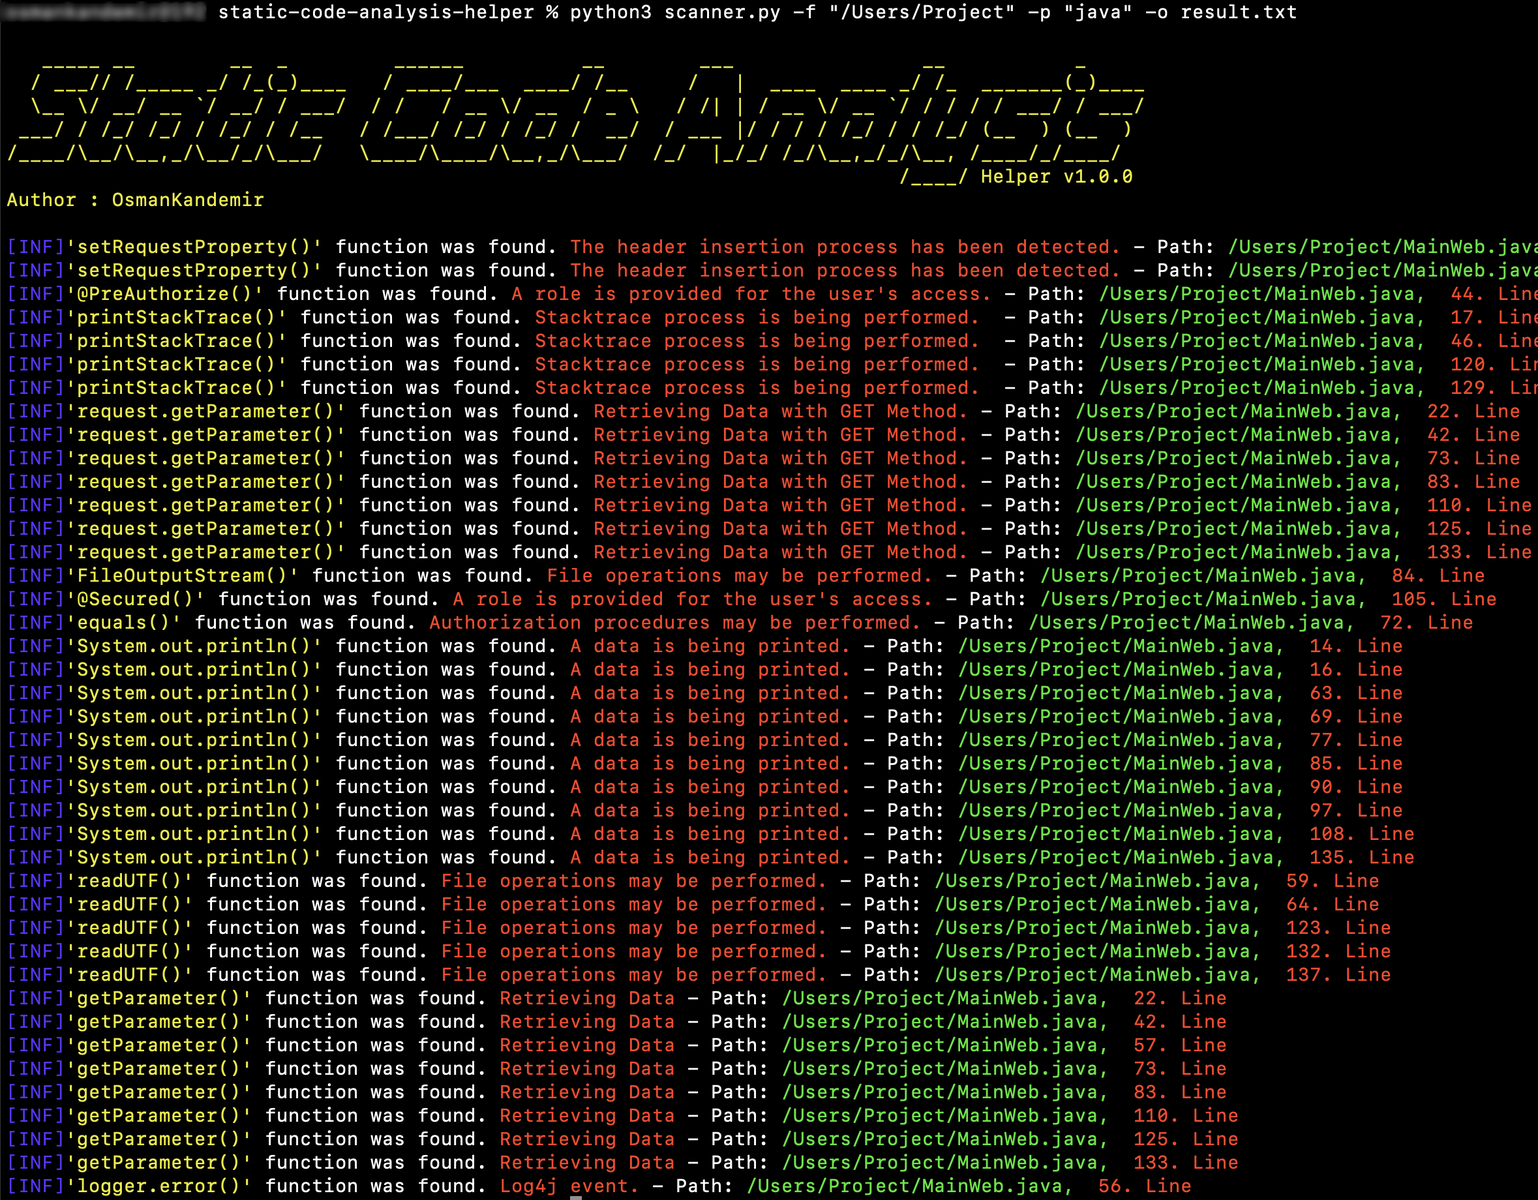 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 isee857/cve-2024-50379-poc
Batch detection script for Apache Tomcat CVE-2024-50379 race condition remote code execution vulnerability. Supports single and mass scanning via…
 timwr/cve-2013-6282
CVE-2013-6282 proof of concept for Android