
CVE-2023-36874
 wh04m1001/cve-2023-36874
Proof-of-concept exploit for CVE-2023-36874, a Windows elevation of privilege vulnerability. Demonstrates exploitation on vulnerable Windows clients…
binary-exploitationexploitationpenetration-testing+2
243
wh04m1001/cve-2023-36874Proof-of-concept exploit for CVE-2023-36874, a Windows elevation of privilege vulnerability. Demonstrates exploitation on vulnerable Windows clients…
 psecio/versionscan
A PHP version scanner for reporting possible vulnerabilities
 ioactive/laf
This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…
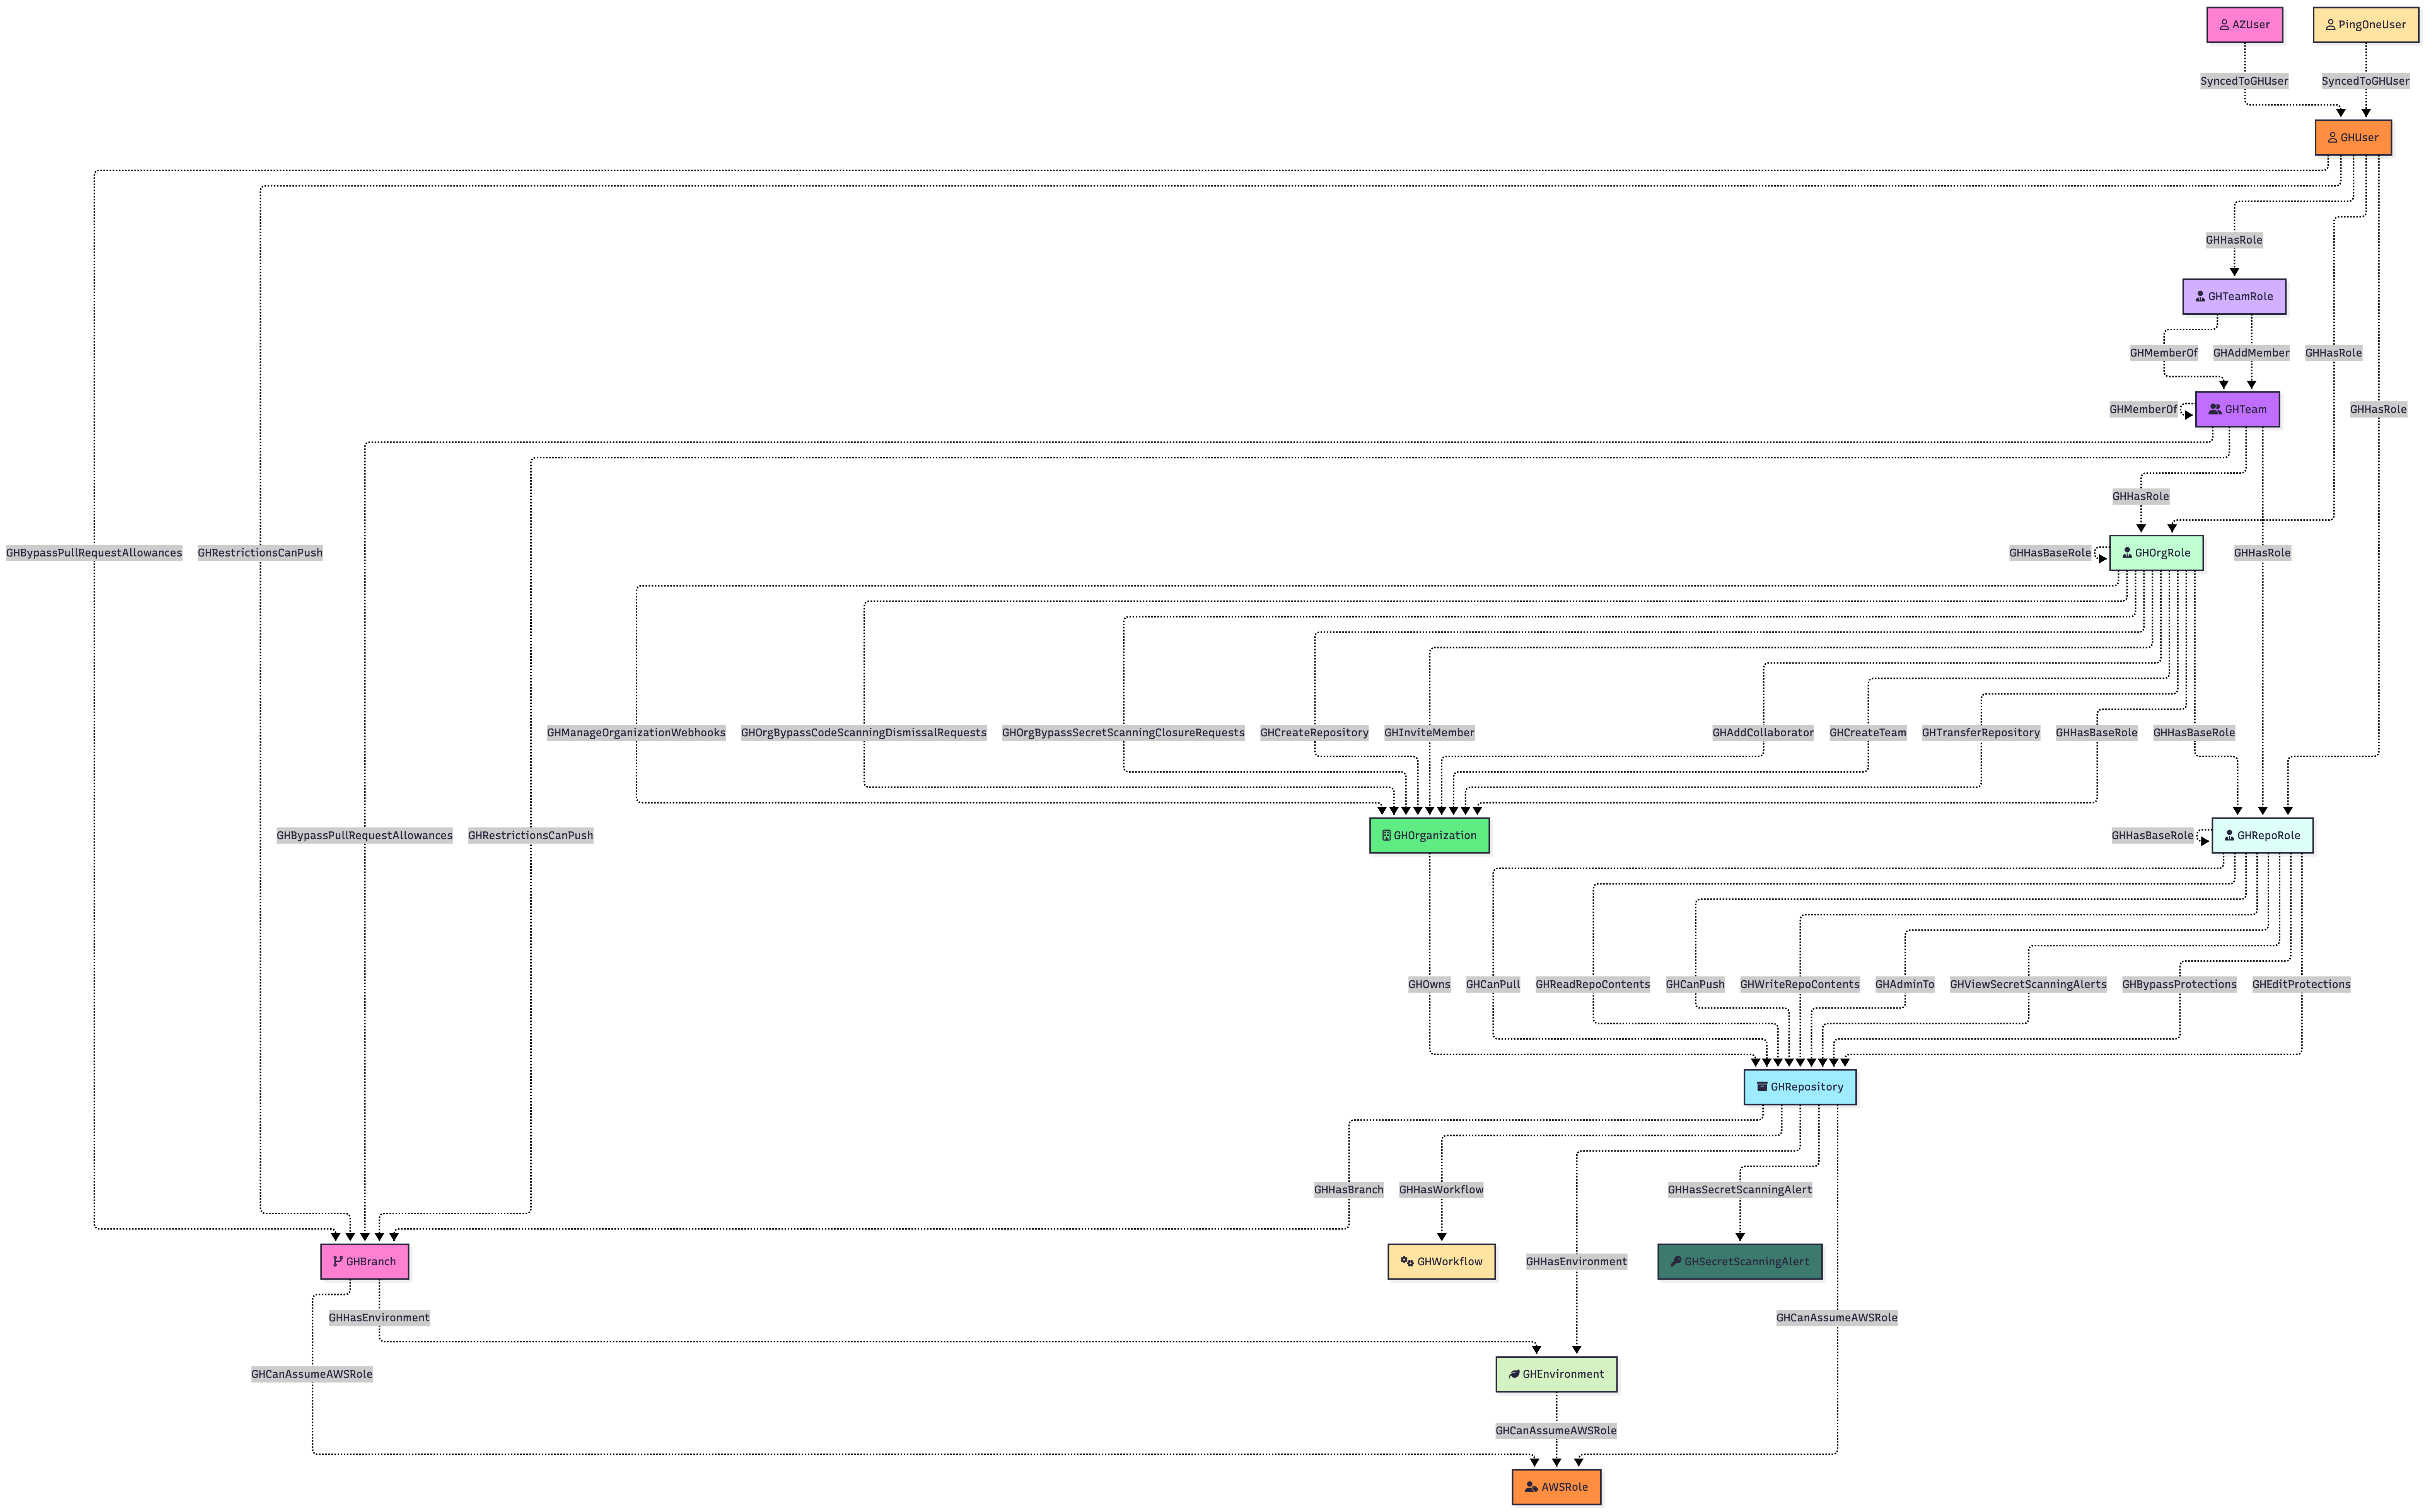 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
 oalabs/findyara-ida
IDA python plugin to scan binary with Yara rules

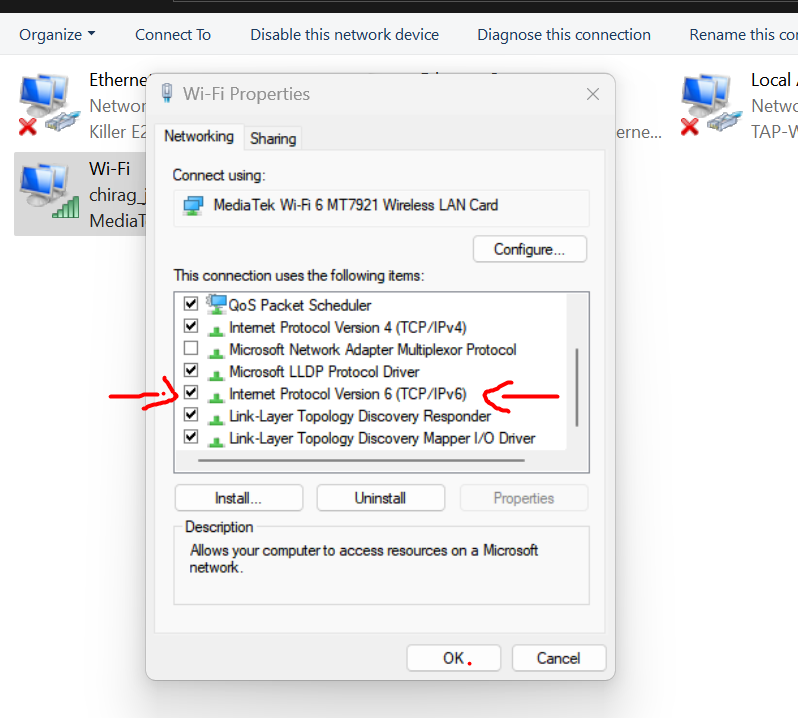 sachinart/cve-2024-38063-poc
Note: I am not responsible for any bad act. This is written by Chirag Artani to demonstrate the vulnerability.
 nccgroup/goatcasino
This is an intentionally vulnerable smart contract truffle deployment aimed at allowing those interested in smart contract security to exploit a wide…
 mouteee/autonomous-offensive-llm-handbook
A deterministic harness and handbook for autonomous offensive LLM agents, enforcing authorization, scope, and evidence gates to ensure reproducible…
 assetnote/jira-mobile-ssrf-exploit
Exploit code for Jira Mobile Rest Plugin SSRF (CVE-2022-26135)
 anasbousselham/fortiscan
A high performance FortiGate SSL-VPN vulnerability scanning and exploitation tool.
 realtalk/cve-2013-2094
original cve-2013-2094 exploit and a rewritten version for educational purposes
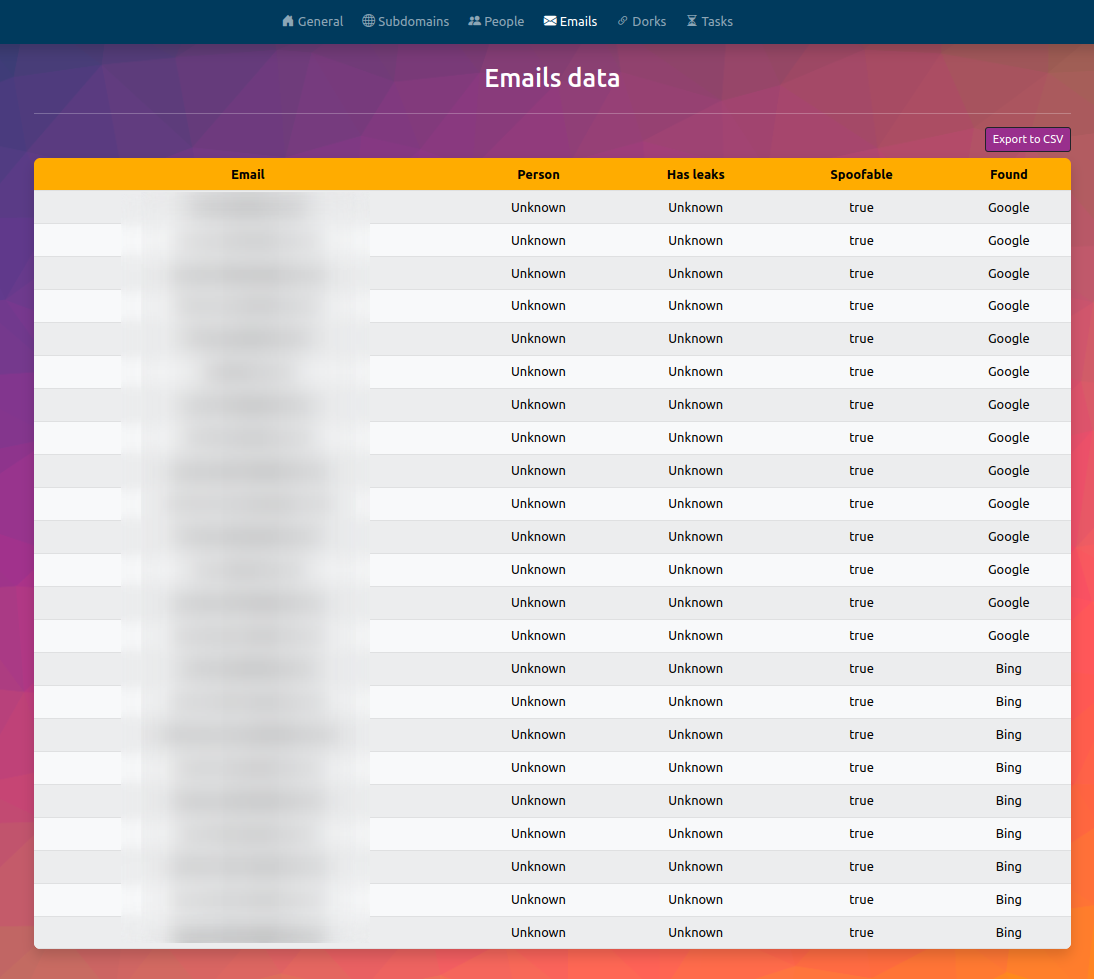 fundacio-i2cat/infohound
InfoHound is an OSINT to extract a large amount of data given a web domain name.
 watchtowrlabs/fortijump-exploit-cve-2024-47575
Fortinet Fortimanager Unauthenticated Remote Code Execution AKA FortiJump CVE-2024-47575
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
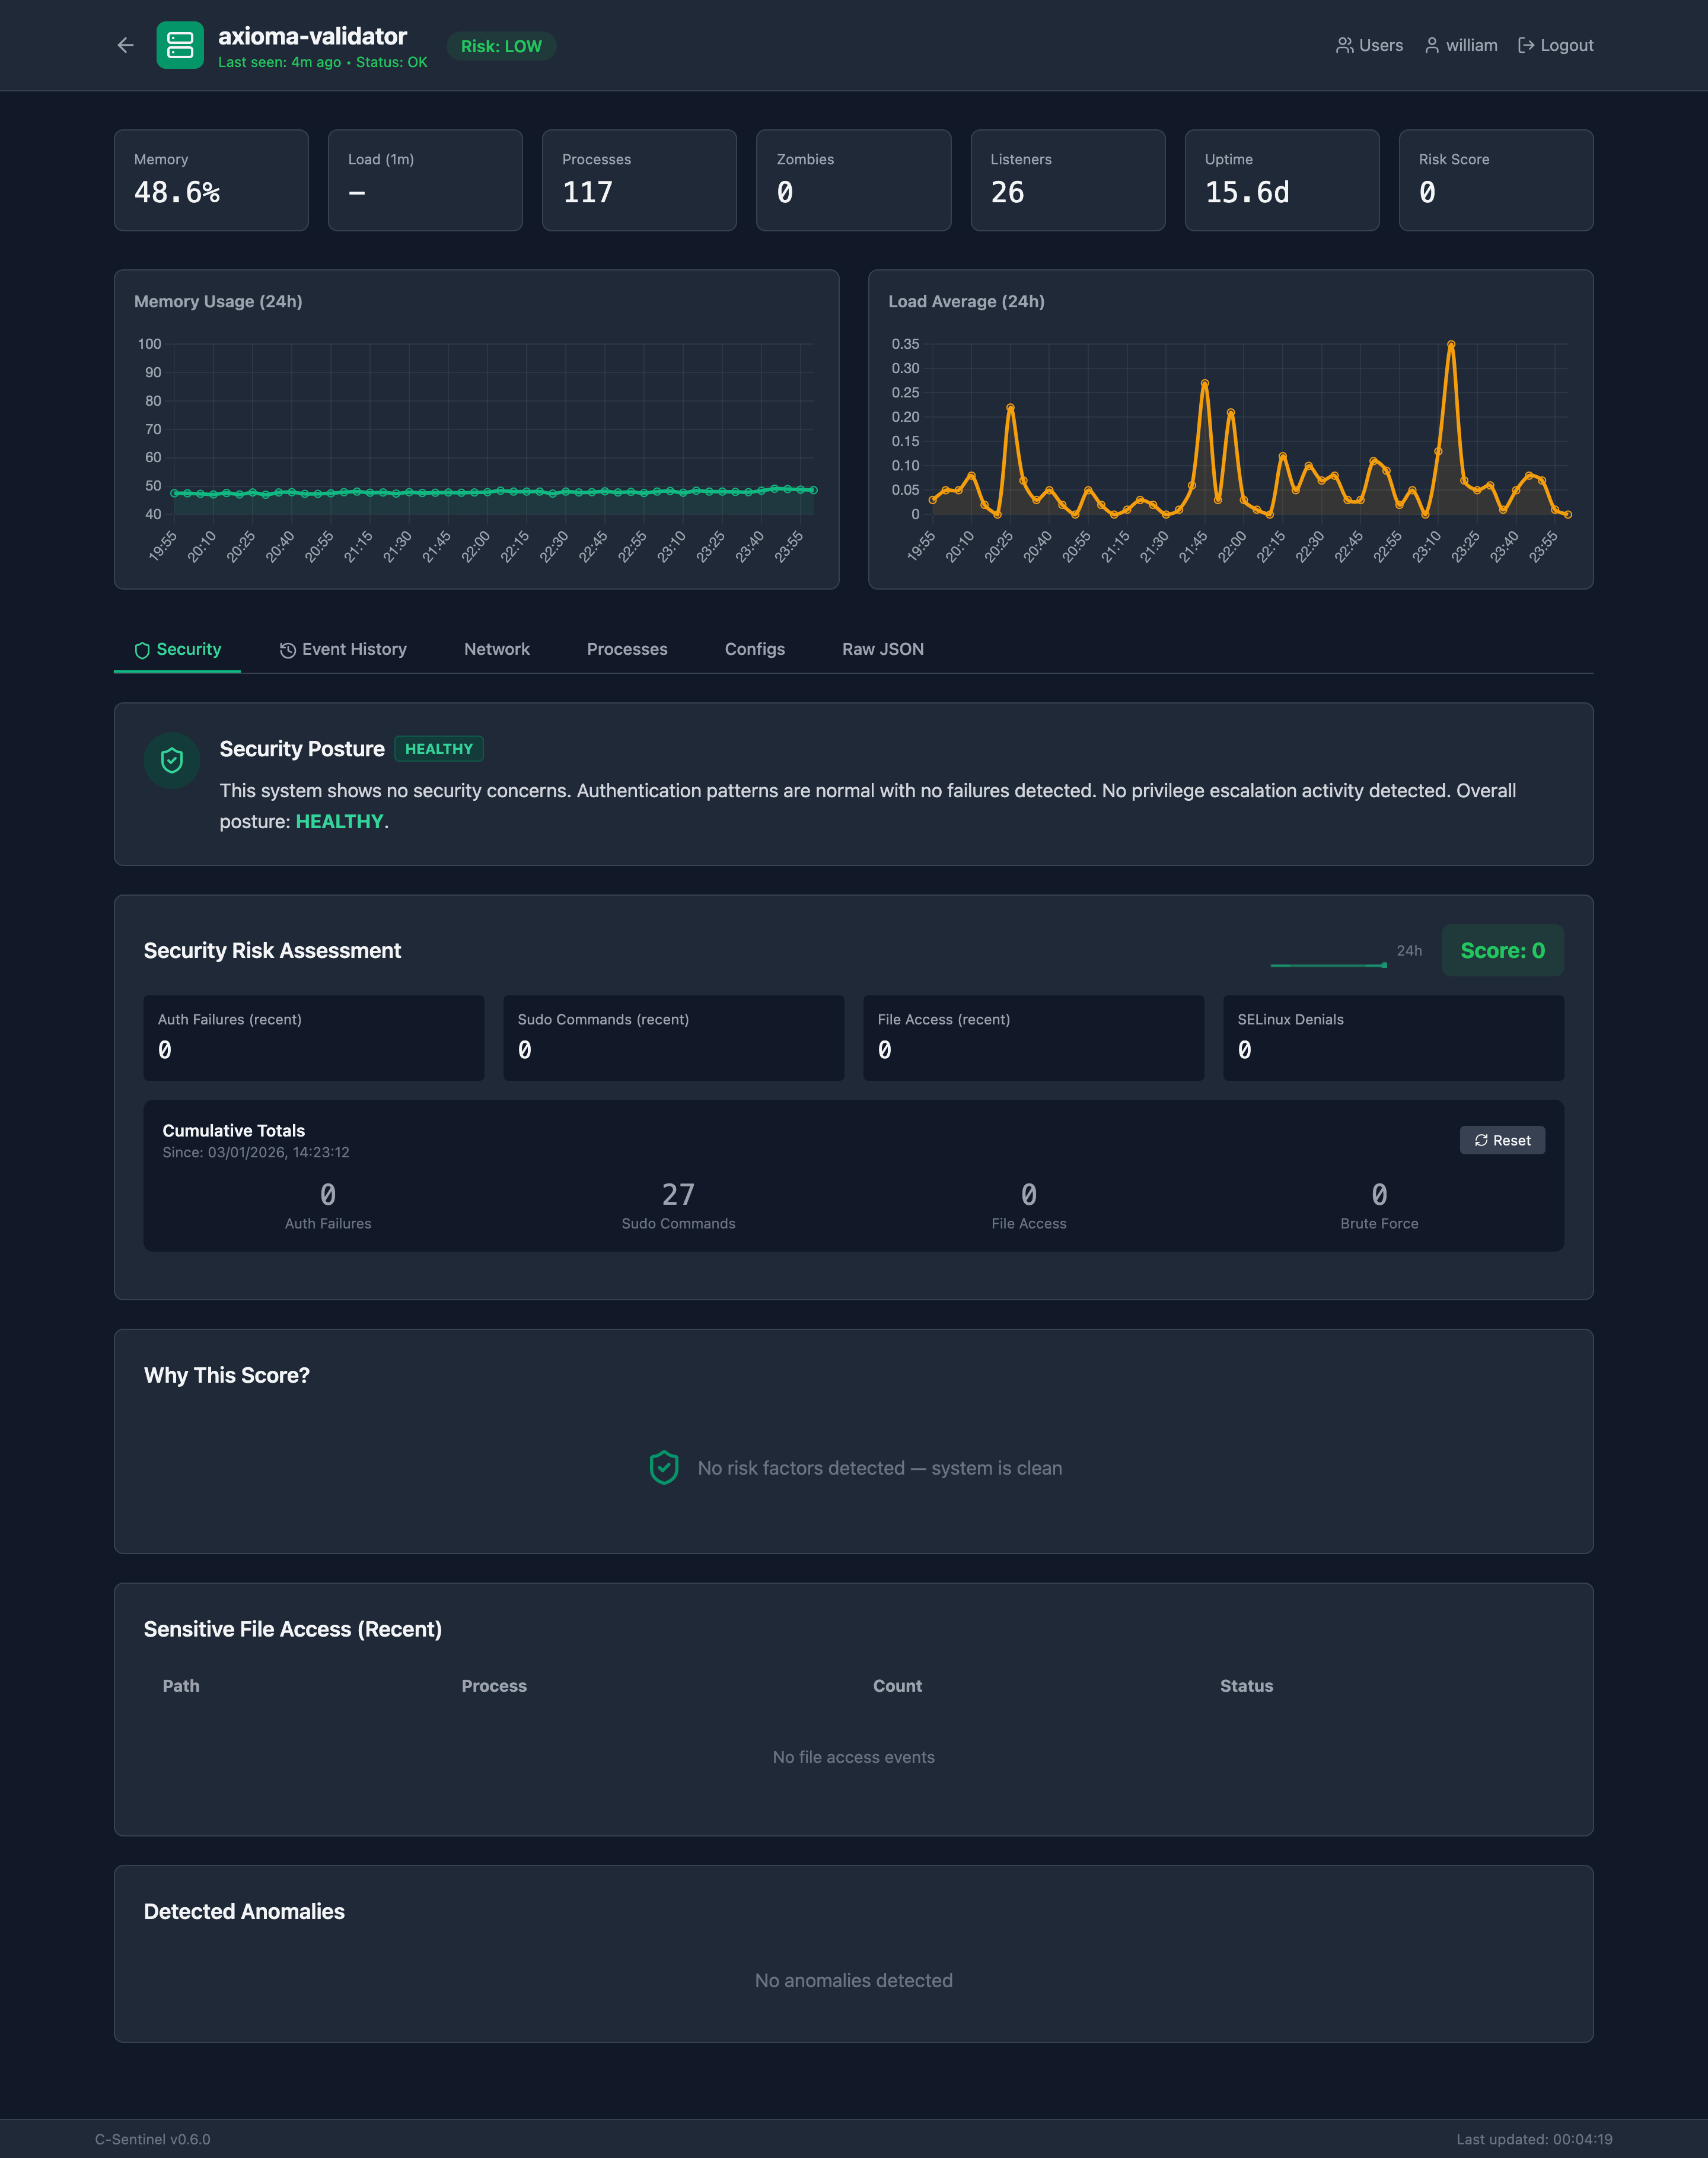 speytech/c-sentinel
Semantic Observability for UNIX Systems - A lightweight C-based system prober with AI-powered analysis
 horizon3ai/h3-cli
CLI tool for the Horizon3.ai API