
fracture
 elvira-alec/fracture
FragAttacks WiFi penetration framework — CVE-2020-24586/87/88
dns-analysisexploitationinformation-gathering+7
elvira-alec/fractureFragAttacks WiFi penetration framework — CVE-2020-24586/87/88
 wh02m1/cve-2026-78306
Proof-of-concept exploiting DJI drone Bluetooth DUML command injection, sending unauthenticated commands to read credentials, alter Wi-Fi config, and…
 turretsec/u3000py
Python client for the Thinkware U3000 dashcam's local WiFi control protocol, reverse-engineered from the official Android app. PoC tooling behind…
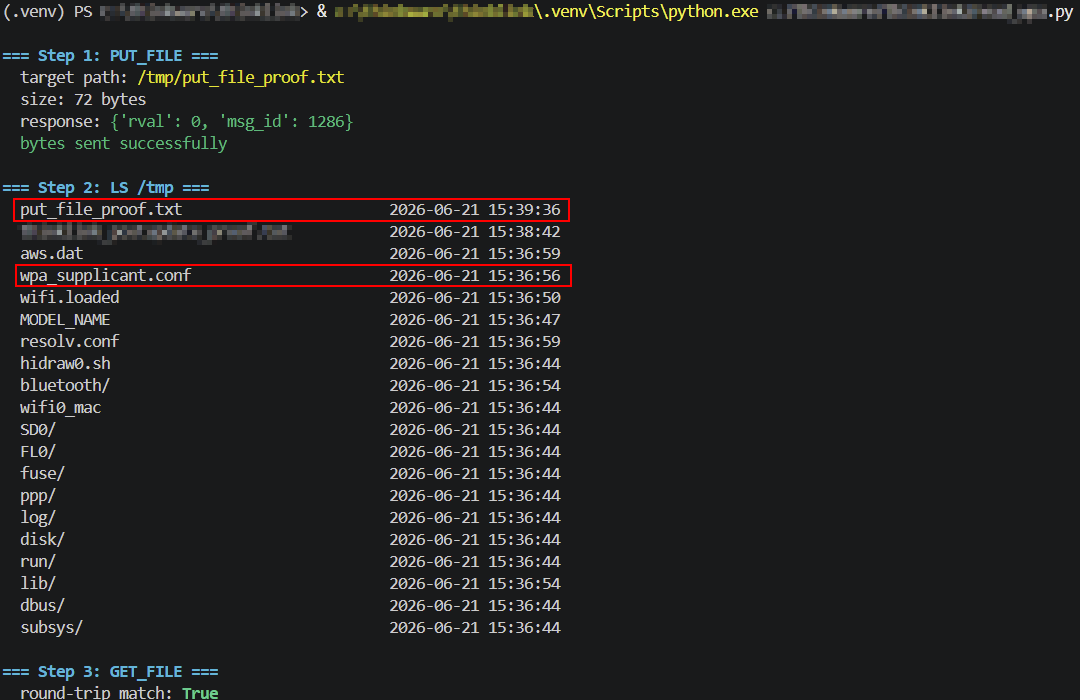 turretsec/disclosure-thinkware-u3000
Three unauthenticated vulnerabilities in the Thinkware U3000 dashcam's local WiFi control protocol: arbitrary file write, arbitrary file read, and…
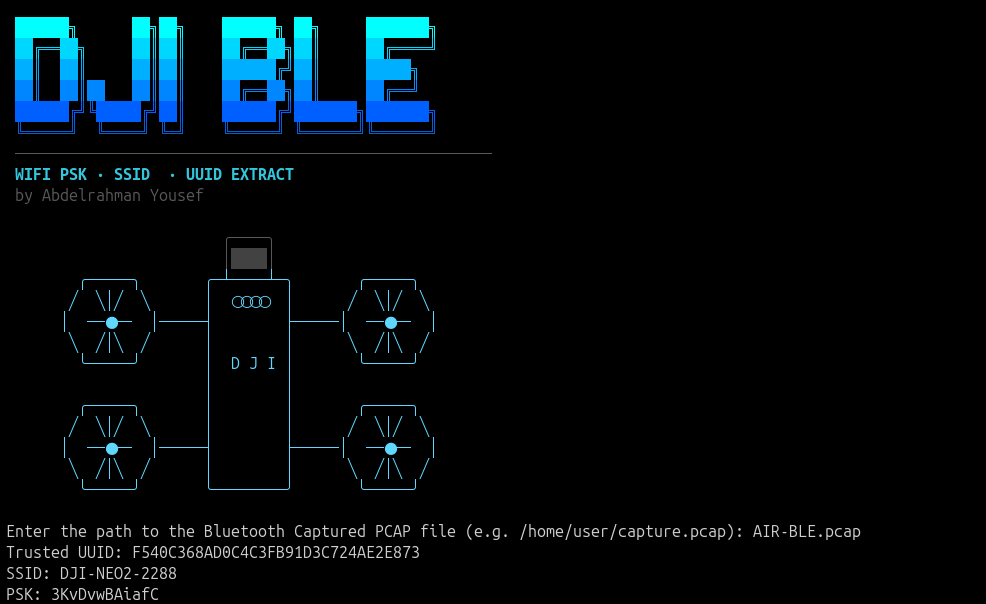 wh02m1/cve-2026-77812
Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…
 mermehr/mouseserver-1.7.8.5-rce
PoC exploit for CVE-2022-3218 targeting WiFi Mouse Server 1.7.8.5, achieving RCE via keystroke injection and in-memory PowerShell payload delivery…
 dingo97/cve-2026-20516
Write-up and ADB proof of concept for CVE-2026-20516, a confused deputy flaw in MediaTek Android TV MiracastService allowing local Wi-Fi Direct state…
 george0papasotiriou/cve-2026-11117-wpa2-4-way-handshake-reinstallation-krack-sim-
Python simulation of CVE-2026-11117 demonstrating WPA2 4-way handshake PTK reinstallation and nonce reuse to illustrate the KRACK attack.
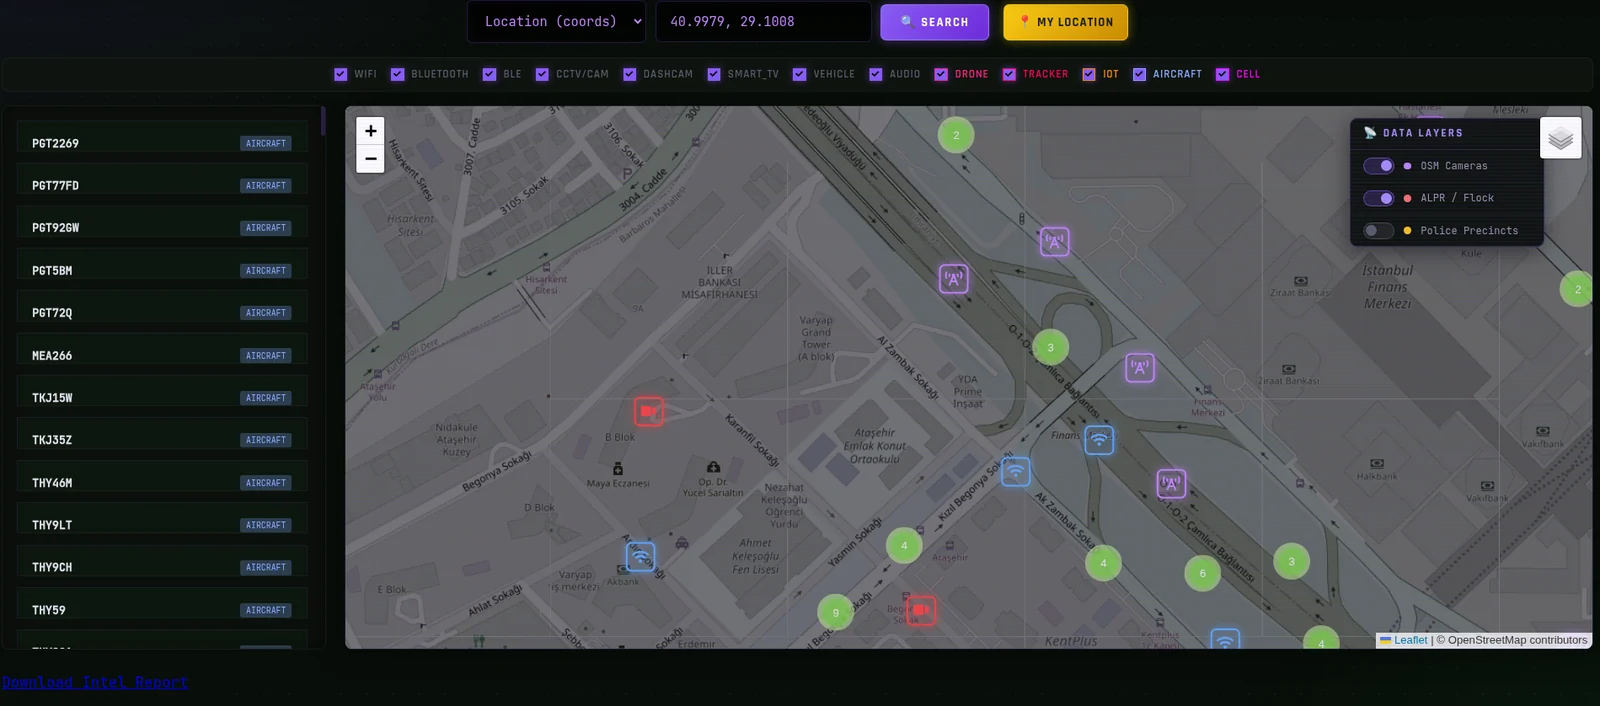 emrekybs/signalops
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…
 luismirandaacebedo/security_articles
Technical articles detailing IoT vulnerability research, including WiFi communication flaws and firmware update weaknesses in connected devices, with…
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
 goultarde/remotemouse-3.008-rce
POC for CVE-2021-35448 based on https://www.exploit-db.com/exploits/49601
 efchatz/wpaxfuzz
A full-featured open-source Wi-Fi fuzzer
 nadafarafat/bd-alaris-firmware-analysis
Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…
 ottoyrocky/phantom-brain
Red portatil de reconocimiento inteligente con IA offline
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
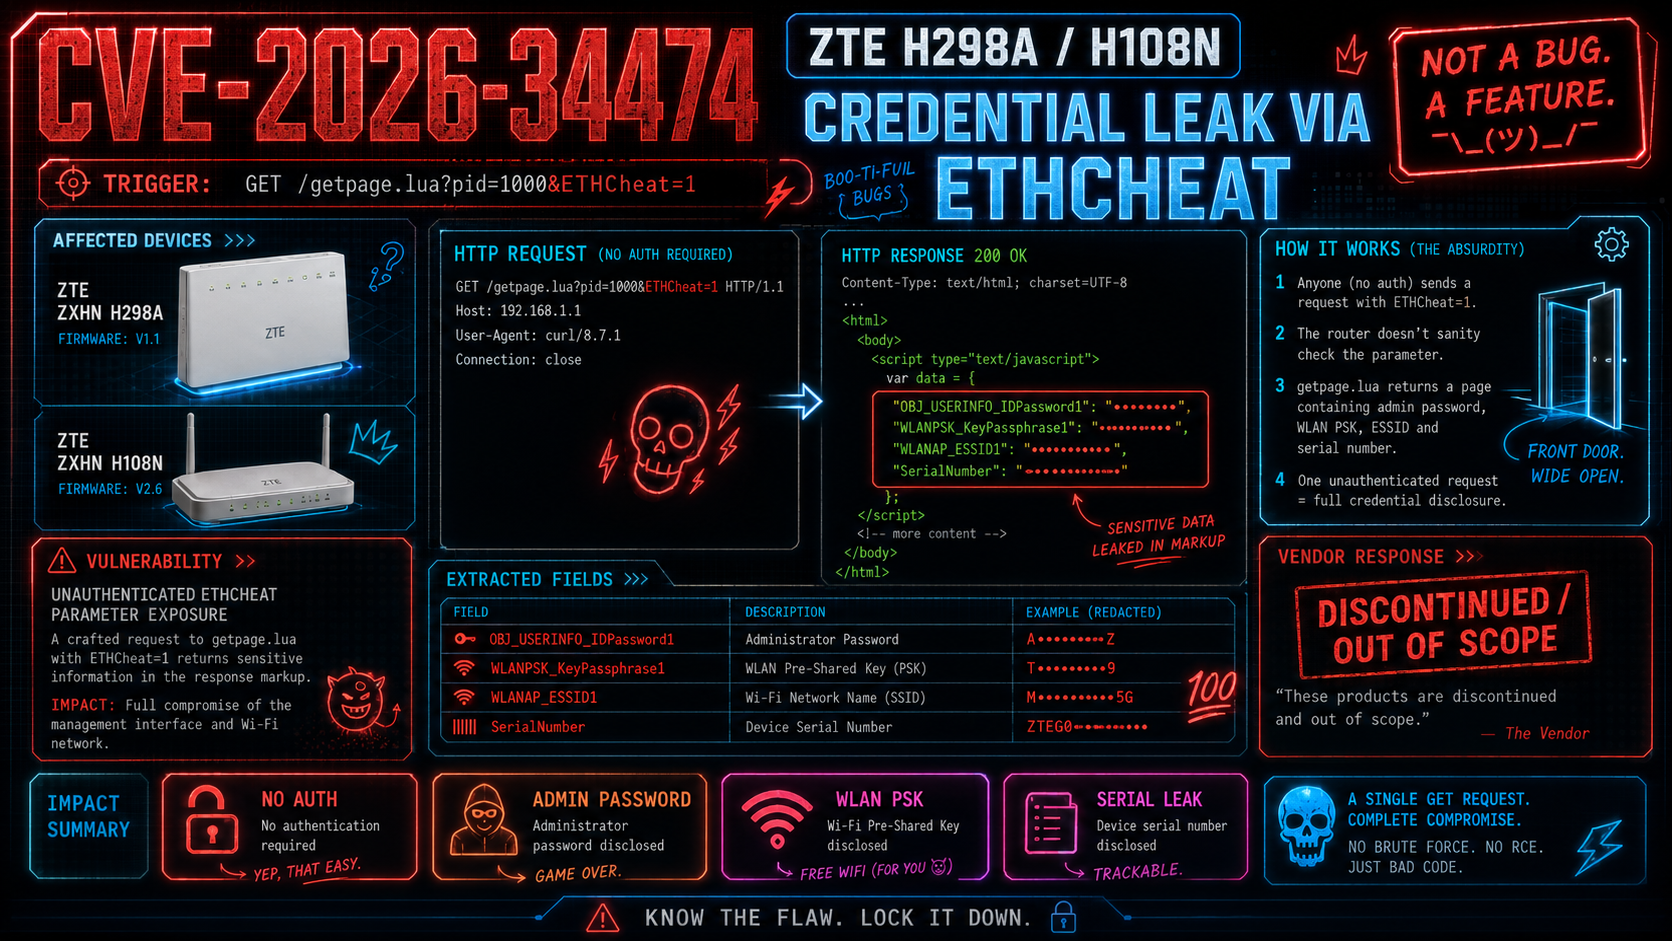 minanagehsalalma/cve-2026-34474-zte-h298a-h108n-sensitive-data-exposure
CVE-2026-34474: unauthenticated ETHCheat=1 requests leak the admin password and Wi-Fi PSK from ZTE H298A/H108N routers.
 masjadaan/cve-2025-29338
Technical advisory and proof-of-concept for a stack-based buffer overflow (CWE-121) in the NXP moal.ko Wi-Fi kernel driver, enabling local kernel…