

PurpleLlama
 meta-llama/purplellama
Set of tools to assess and improve LLM security.
adversarial-attackai-securitycode-analysis+4
4.5k22h 6m ago
meta-llama/purplellamaSet of tools to assess and improve LLM security.
 zarcolio/sitedorks
Search Google/Bing/Ecosia/DuckDuckGo/Yandex/Yahoo for a search term (dork) with a default set of websites, bug bounty programs or custom collection.
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…
 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.
 zierax/grafana-final-scanner
Grafana scanner with all public CVEs that I collected in one script to make grafana testing easier
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
 dungsocool/cve-2025-7384
Exploit PoC and root-cause analysis for a critical unauthenticated PHP object injection in WordPress Database for Contact Form 7, leading to RCE via…
 abstractclass/cloudprivs
Determine privileges from cloud credentials via brute-force testing.
 martinclauss/exim-rce-cve-2018-6789
This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.
 deepwoodssec/cve-2026-36522
Proof-of-concept exploit for CVE-2026-36522: unauthenticated NaN injection via MAVLink PARAM_SET in ArduPilot ArduPlane, causing DoS or silent…
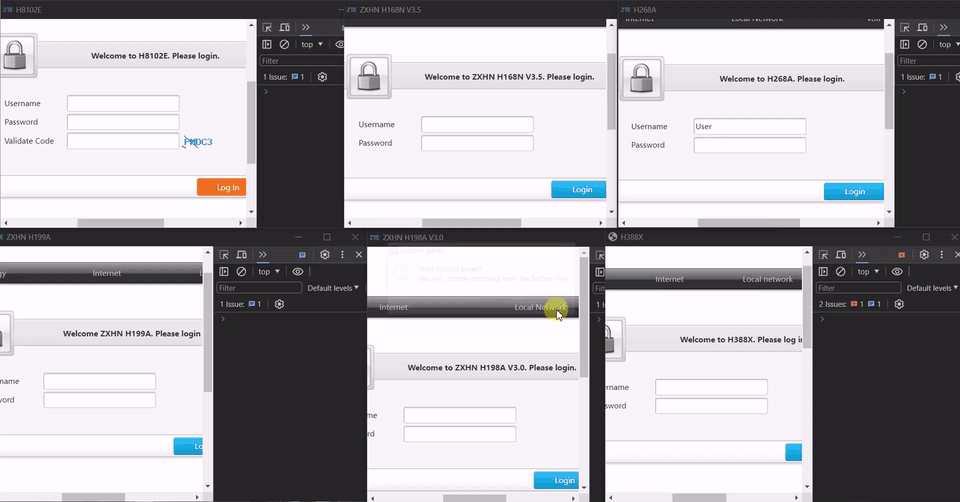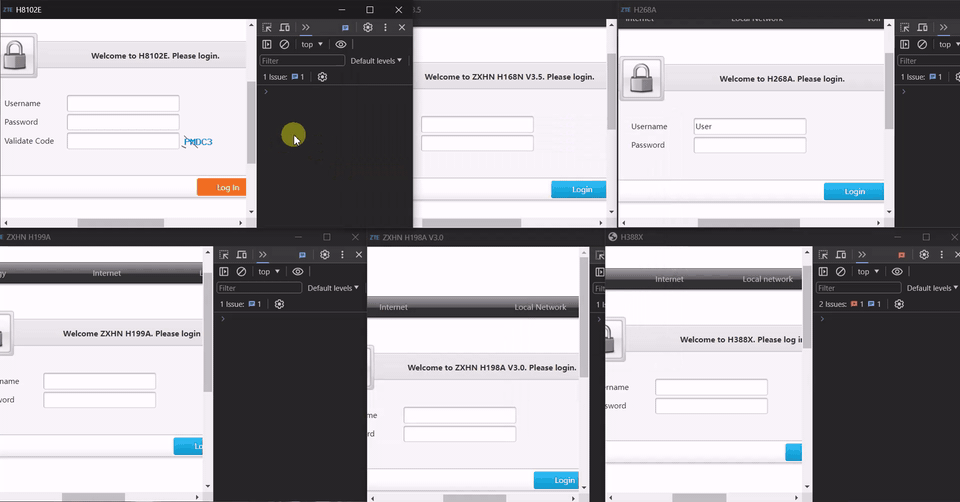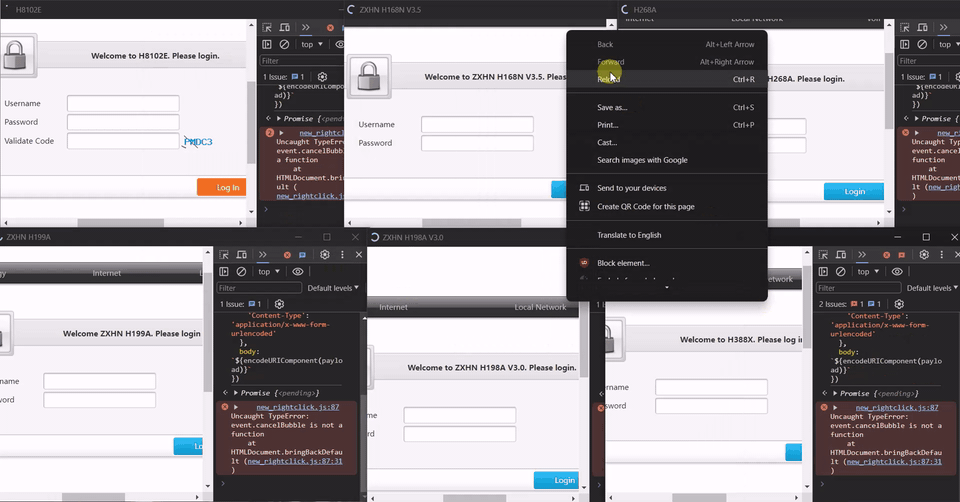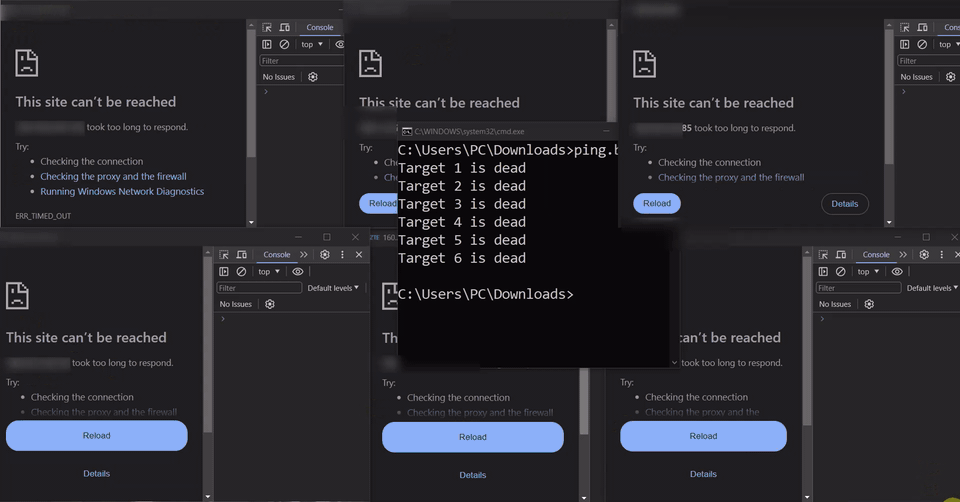 minanagehsalalma/cve-2026-34473-unauthenticated-dos-zte-routers
Technical breakdown of CVE-2026-34473, an unauthenticated denial of service affecting 17+ ZTE router models.
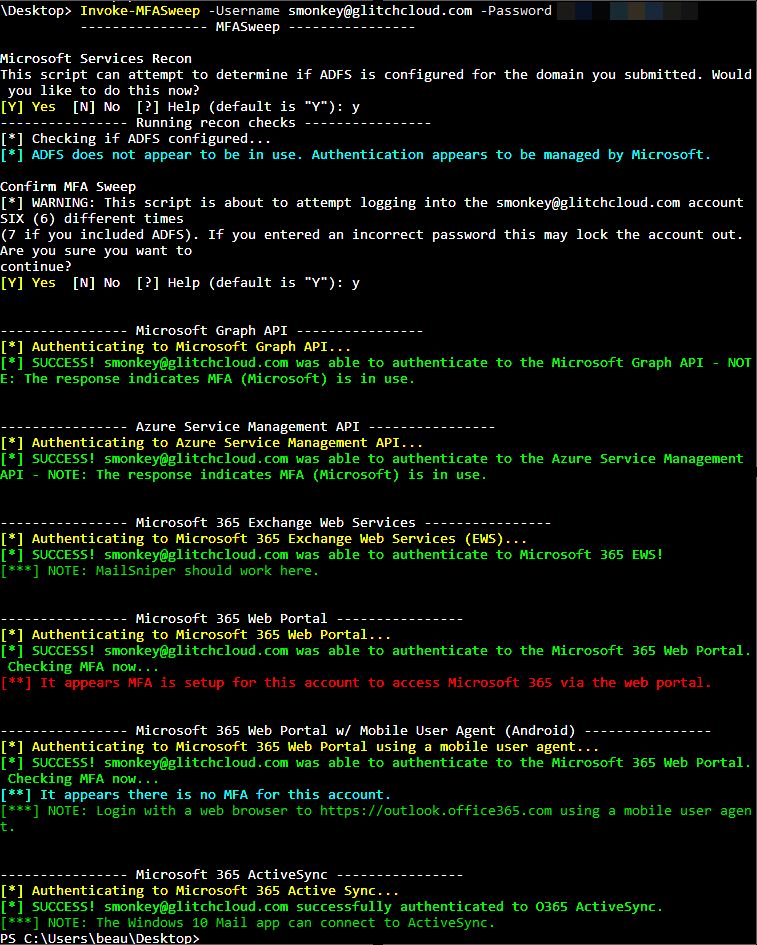 dafthack/mfasweep
A tool for checking if MFA is enabled on multiple Microsoft Services
 backline-playground/gogs
Fork of gogs/gogs for reachability benchmark testing (CVE-2024-45337)
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 localh0ste/cve-2025-4138
Tarfile module directory traversal vulnerability ( with overflow crossed Directory ) --> Lead to Privilege escalation
 azurit/crsprober
Remote detection tool for OWASP Core Rule Set version and paranoia level on ModSecurity WAFs, aiding security posture assessment.
 80ottanta80/cve-2024-32019-poc
Bash script for Privilege Escalation via "ndsudo" (Netdata Local Exploit)