

fleet
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
cloud-securityconfiguration-auditingdefensive-tools+4
7.0k
fleetdm/fleetOpen-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 owasp/secure-headers-project
OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.
 mein-0/knockgiga
Proof-of-concept local privilege escalation exploiting Gigabyte gdrv3.sys IOCTLs to write the SYSTEM token into a user process via an unchecked…
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 owasp/opencre
Interactive platform linking security standards and guidelines for designing, developing, testing, and procuring secure software. Provides a unified…
 horkimhab/cve-2026
Educational collection of CVE proof-of-concept resources and vulnerability research material for authorized lab testing, defensive study, and secure…
 ksnnd32/redis_exploit
🔍 Explore and test the CVE-2025-49844 (RediShell) vulnerability in Redis with this practical lab environment for secure education and research.
 yozarseef95/cve-2023-31594
IC Realtime ICIP-P2012T 2.420 is vulnerable to Incorrect Access Control
 google/silifuzz
Fuzzes CPU implementations by generating test inputs from software proxies, then executes them on real hardware to detect microarchitecture defects…
 chipsec/chipsec
Platform Security Assessment Framework
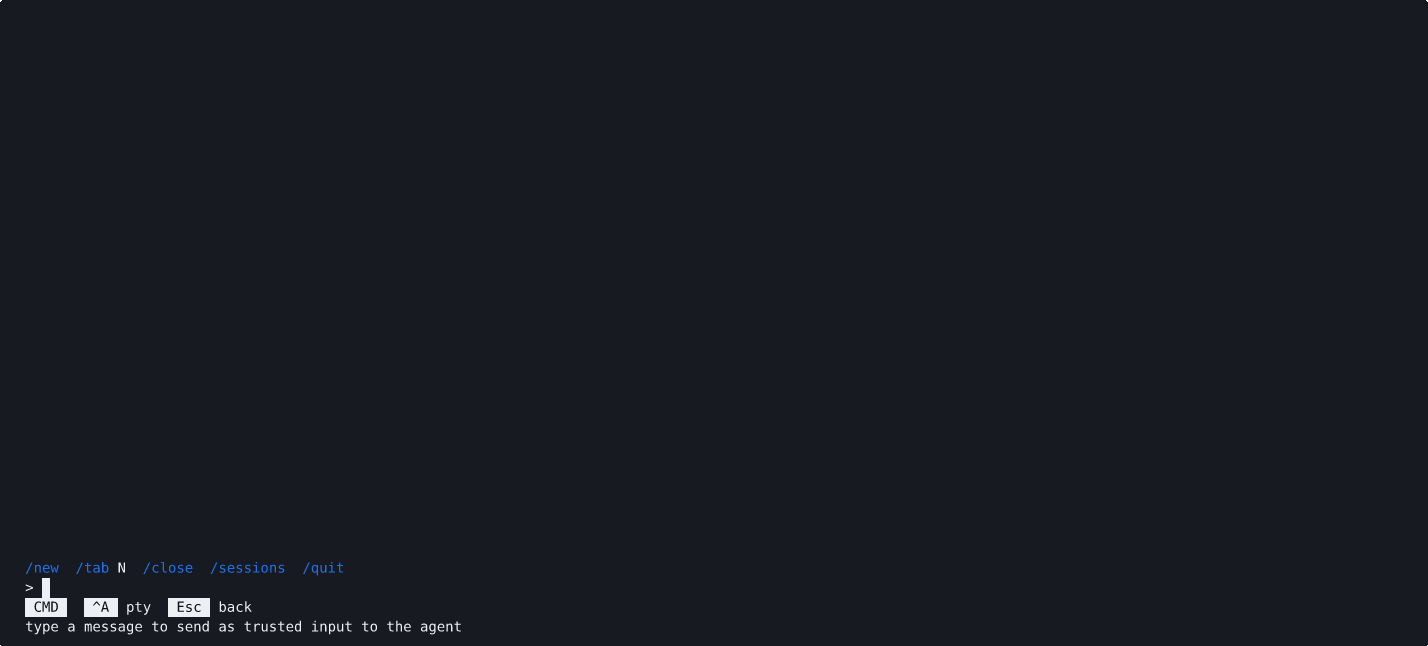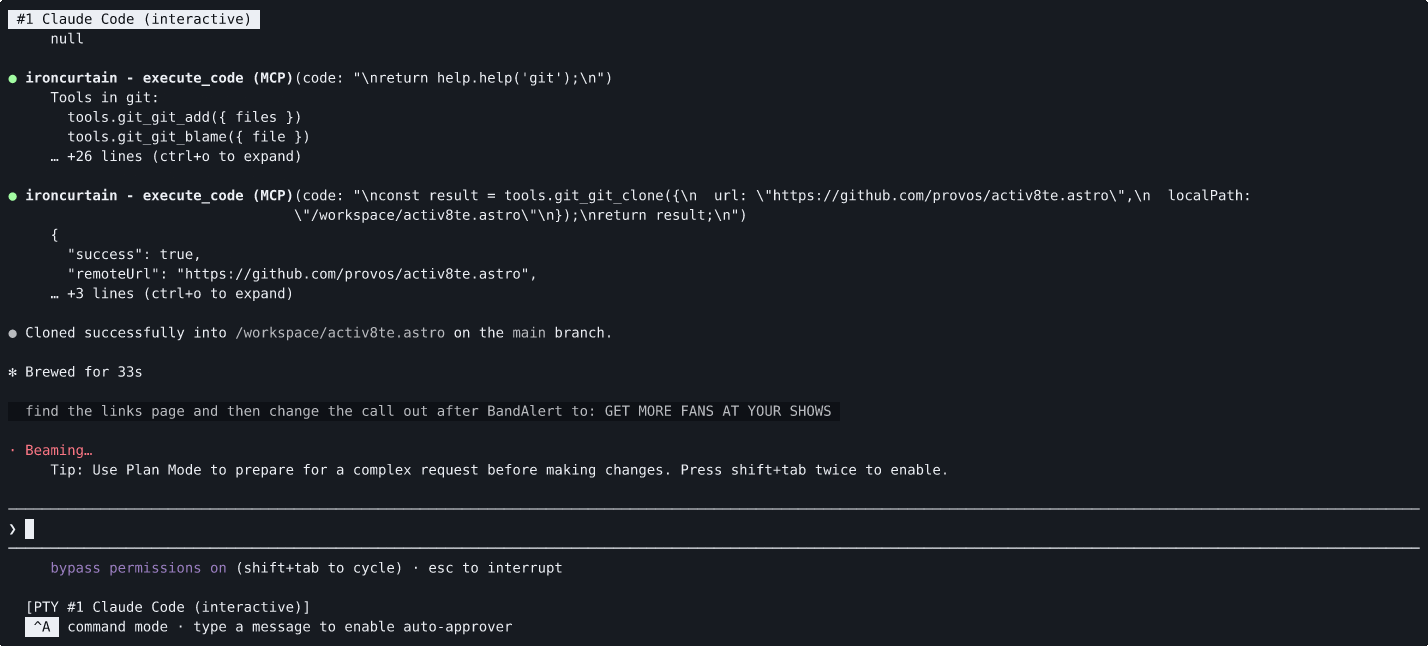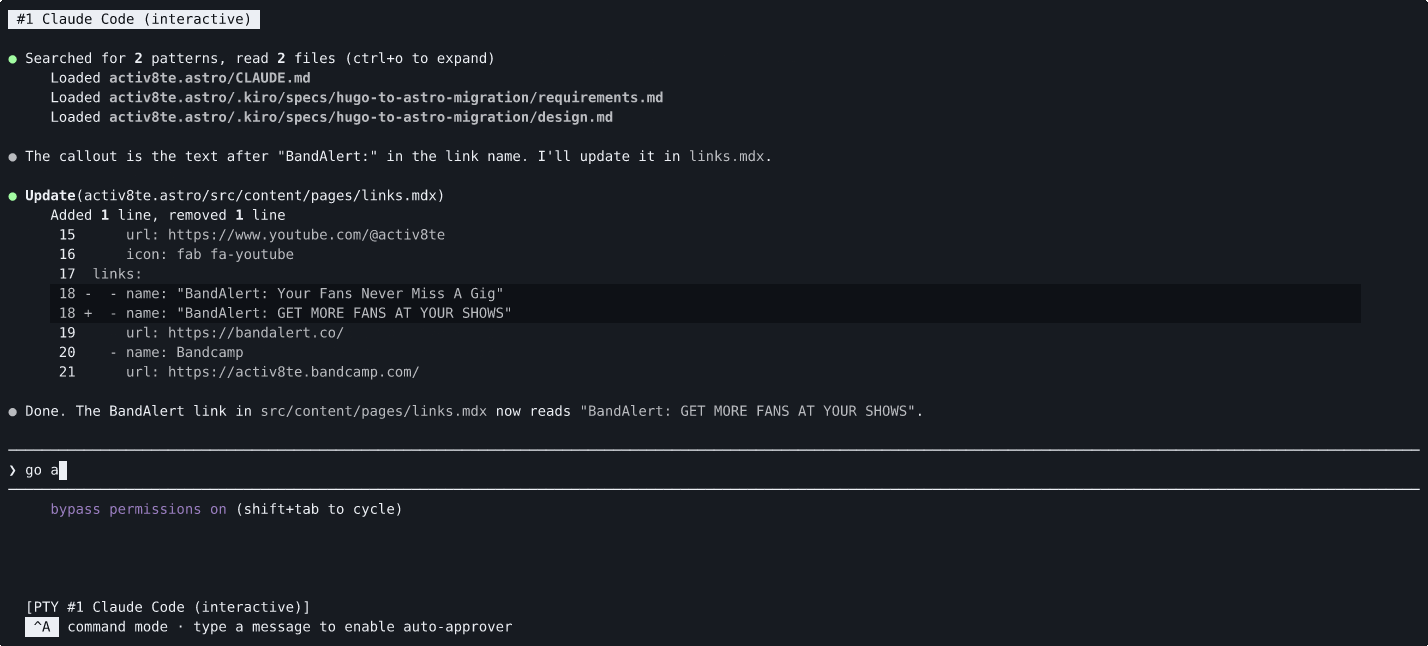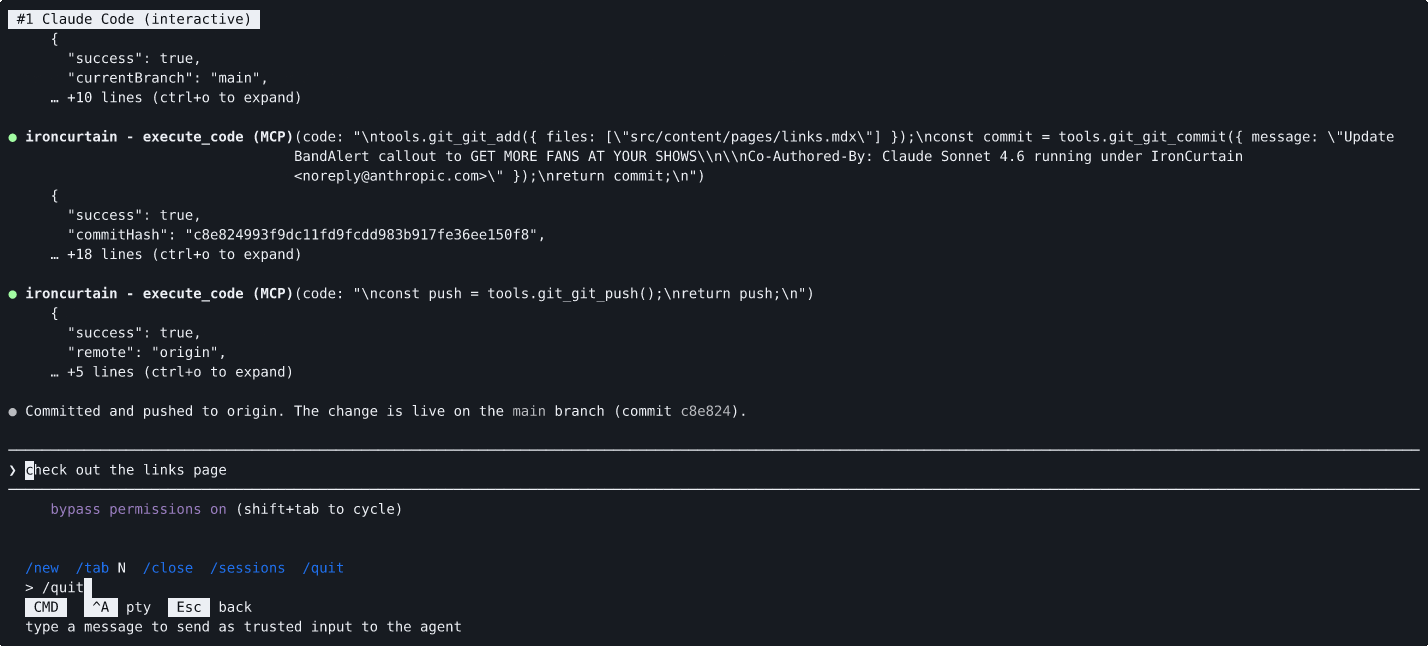 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)
 viralmaniar/vulnvault
Developer-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…
 vusec/btr
Artifacts for the Branch Target Reuse (BTR) Spectre-v2 attack research, including microarchitecture experiments, attack-surface analysis of JIT…
 ihebski/defaultcreds-cheat-sheet
One place for all the default credentials to assist the Blue/Red teamers identifying devices with default password 🛡️
 mein-0/gvcidrv64
Proof-of-concept exploit for Gigabyte's GVCIDrv64.sys kernel driver, achieving local privilege escalation via arbitrary physical memory and I/O port…
 owasp/ocsd
OWASP Certified Secure-Software Developer
 owasp/android-security-masterclass
OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…
 rushikesh-a-bhujbal/cve-2011-2523
From-scratch exploit development in Python. No Metasploit. No frameworks. Raw socket-level implementation of real CVEs against authorized lab targets.