
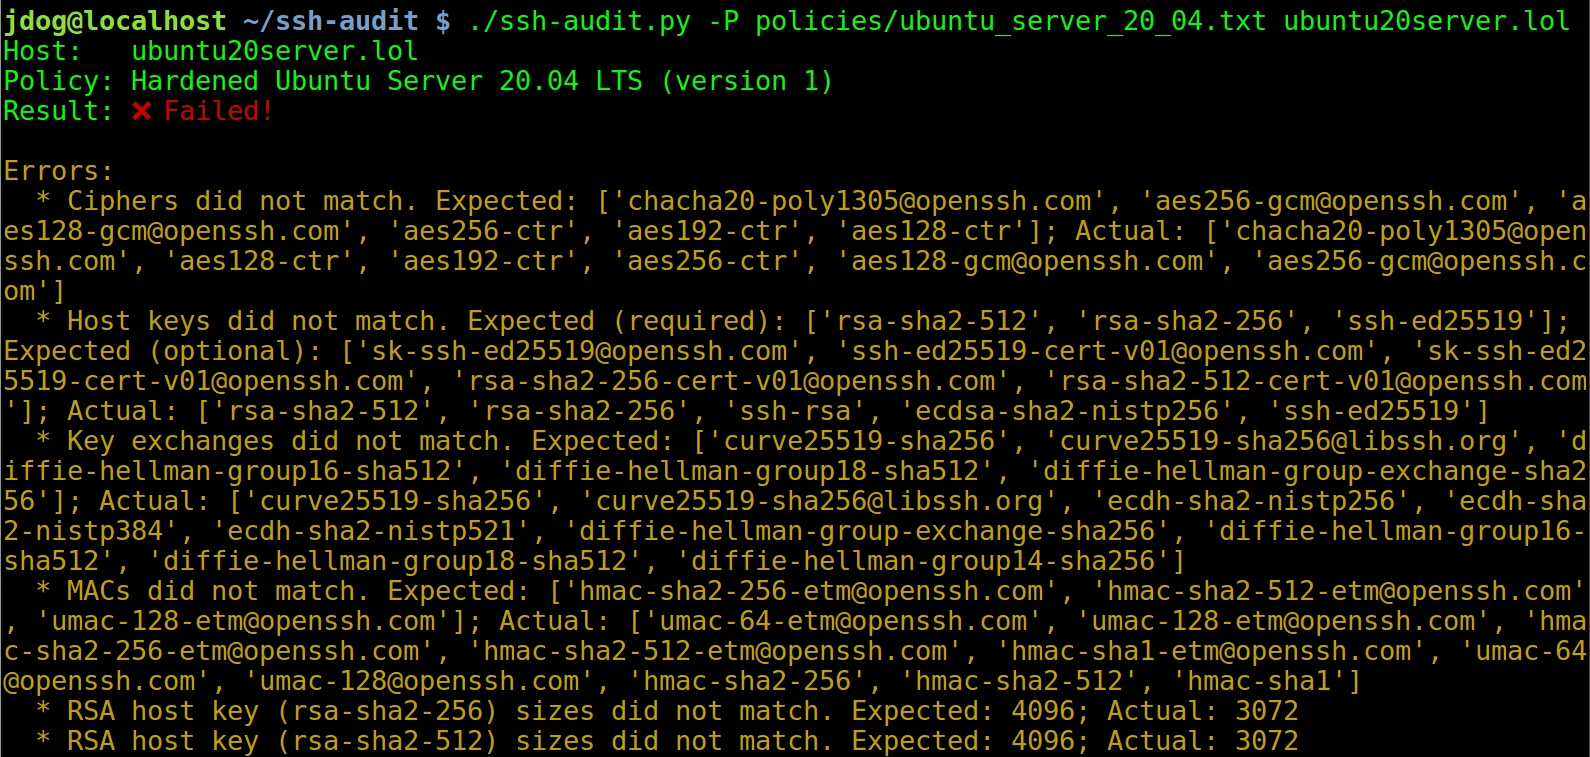
ssh-audit
 jtesta/ssh-audit
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
configuration-auditingcryptographyinformation-gathering+6
4.3k
jtesta/ssh-auditSSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
 alexb616/weblate-cve-2026-24126
Proof-of-concept exploit for CVE-2026-24126, an arbitrary file read in Weblate via SSH host argument injection, allowing authenticated admins to read…
 damnkrishna/cve-2025-32433-lab
A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
 liam-worsley/cve-2025-32433-poc-analysis
This is an analysis for CVE-2025-32433 (Erlang OTP SSH Vulnerability). I did not write any of the code, I only wrote comments describing what the…
 dheatattack/dheater
Proof-of-concept denial-of-service tool that enforces Diffie-Hellman ephemeral key exchange over TLS and SSH to saturate server CPU, implementing…
 gabrielha12/termix-research
CVE-2026-45746, CVE-2026-45750, CVE-2026-53547 — three critical vulnerabilities in Termix: cross-tenant session hijacking, OS command injection, and…
 acidboonrs/cve-2025-26466-openssh-poc
CVE-2025-26466 OpenSSH SSH2_MSG_PING DoS PoC
 razureink/cve-2025-32433-erlang_ssh_rce_reproduction
Reproduction of cve-2025-32433-erlang_ssh_rce_reproduction
 dampedcoast/exploiting-a-vulnerability-using-reverse-shell
This project simulates a real-world attack-and-defend scenario across two virtual machines. You will exploit a critical pre-authentication RCE…
 0x7556/cve-2025-32433
CVE-2025-32433 Erlang/OTP SSH RCE Exploit SSH远程代码执行漏洞EXP
 hazavvip/cve-2025-30208
Exploit scanner for CVE-2025-30208 (Vite arbitrary file read) with multi-variant bypass detection, credential harvesting, SSH key extraction, and…
 hackerhouse-opensource/cve-2018-10933
Docker-based CVE-2018-10933 libssh authentication bypass exploit with patched client for testing SSH server vulnerabilities and unauthorized access…
 shubtheone/cve-2021-36260-hikvision
Python exploit for CVE-2021-36260 command injection in Hikvision web servers. Supports safe/unsafe vulnerability verification, remote command…
 cybervinner/tp-link-tl-wr820n-cve-2025-14175
Responsible disclosure write-up for CVE-2025-14175 involving weak cryptographic algorithm support in the SSH server of TP-Link TL-WR820N.
 soltanali0/cve-2025-32433-eploit
Erlang/OTP SSH Vulnerable to Pre-Authentication RCE
 rxerium/cve-2025-26465
MitM attack allowing a malicious interloper to impersonate a legitimate server when a client attempts to connect to it
 rxerium/cve-2025-26466
The OpenSSH client and server are vulnerable to a pre-authentication DoS attack between versions 9.5p1 to 9.9p1 (inclusive) that causes memory and…
 dollarboysushil/cve-2025-32433-erlang-otp-ssh-unauthenticated-rce
PoC showing unauthenticated remote code execution in Erlang/OTP SSH server. By exploiting a flaw in SSH protocol message handling, an attacker can…