
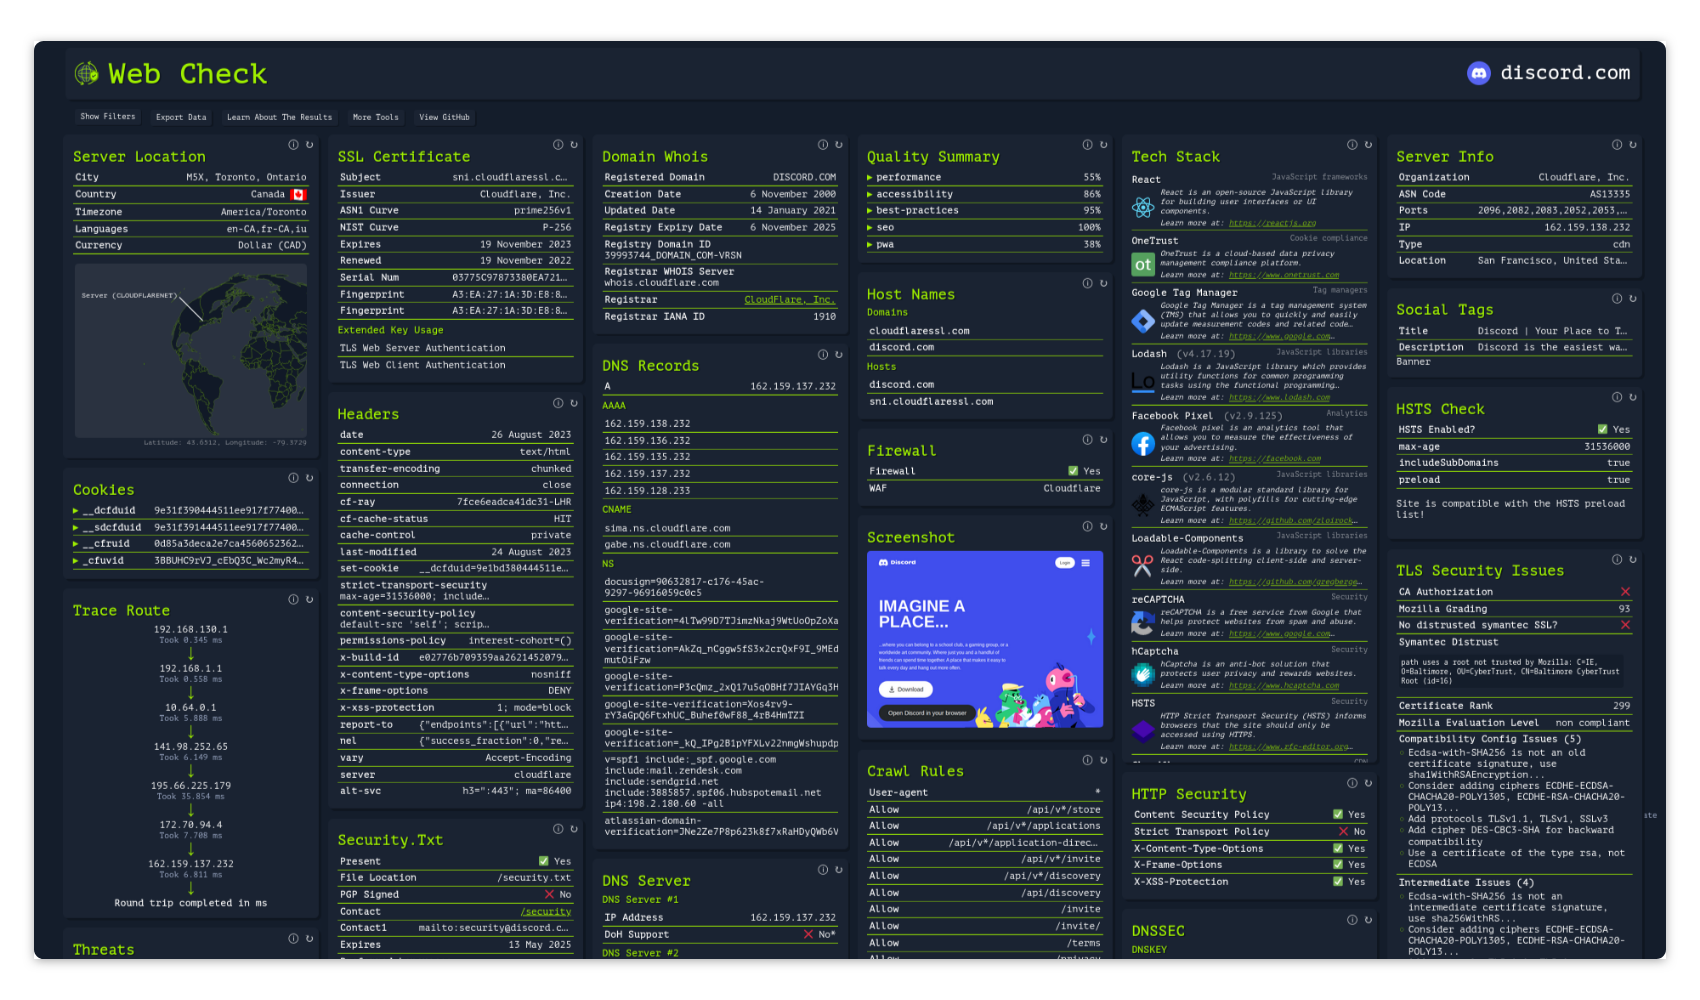
web-check
 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
dns-analysisemail-harvestinginformation-gathering+10
lissy93/web-check🕵️♂️ All-in-one OSINT tool for analysing any website
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
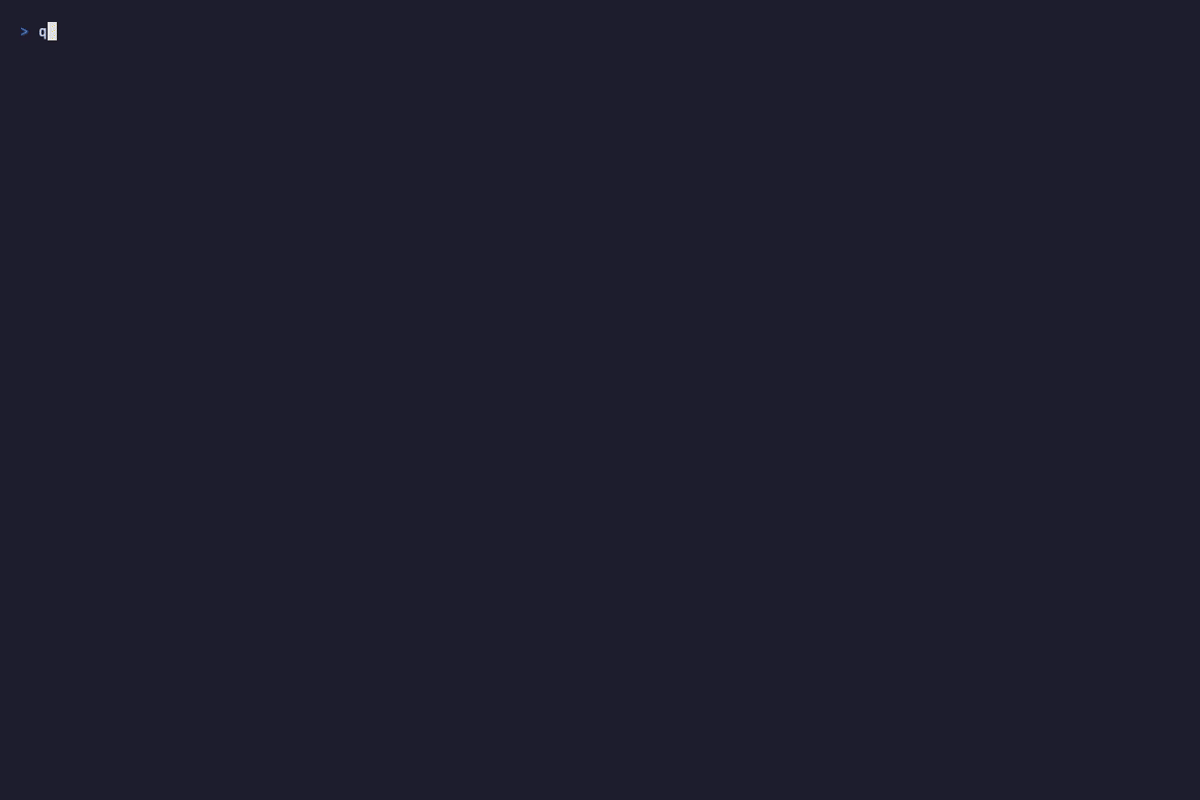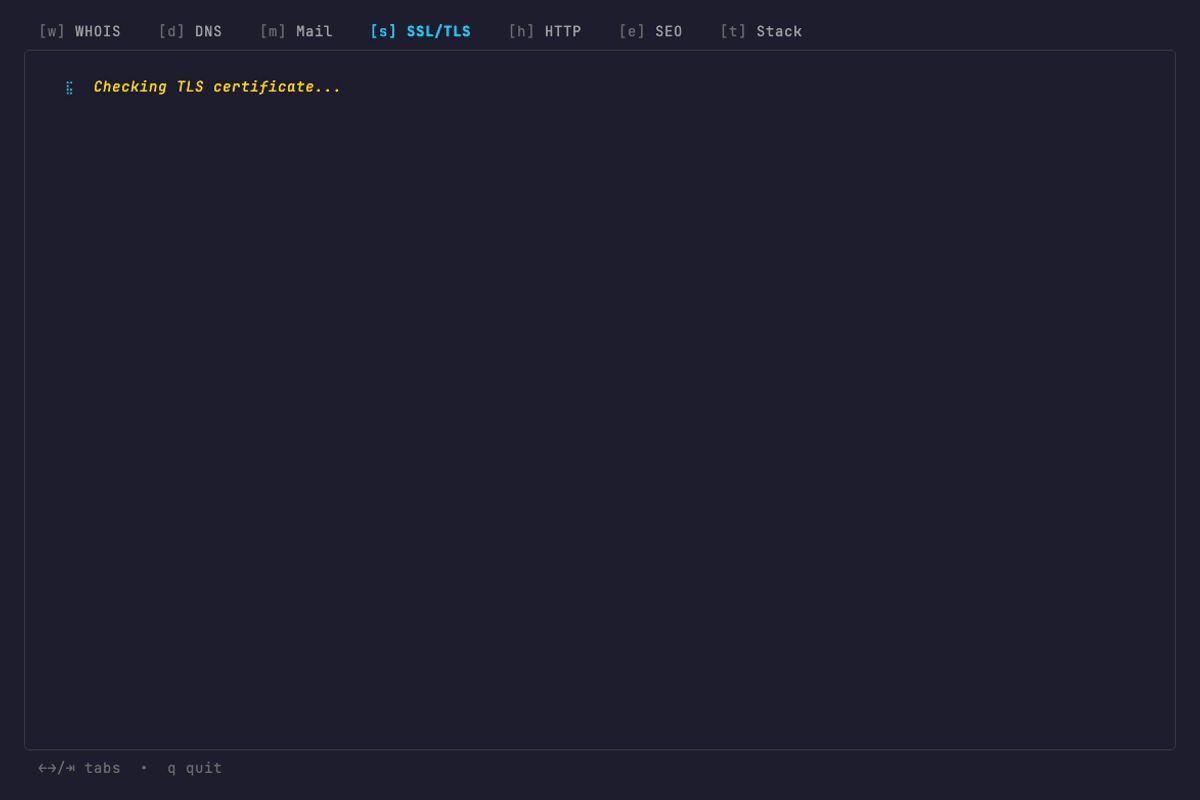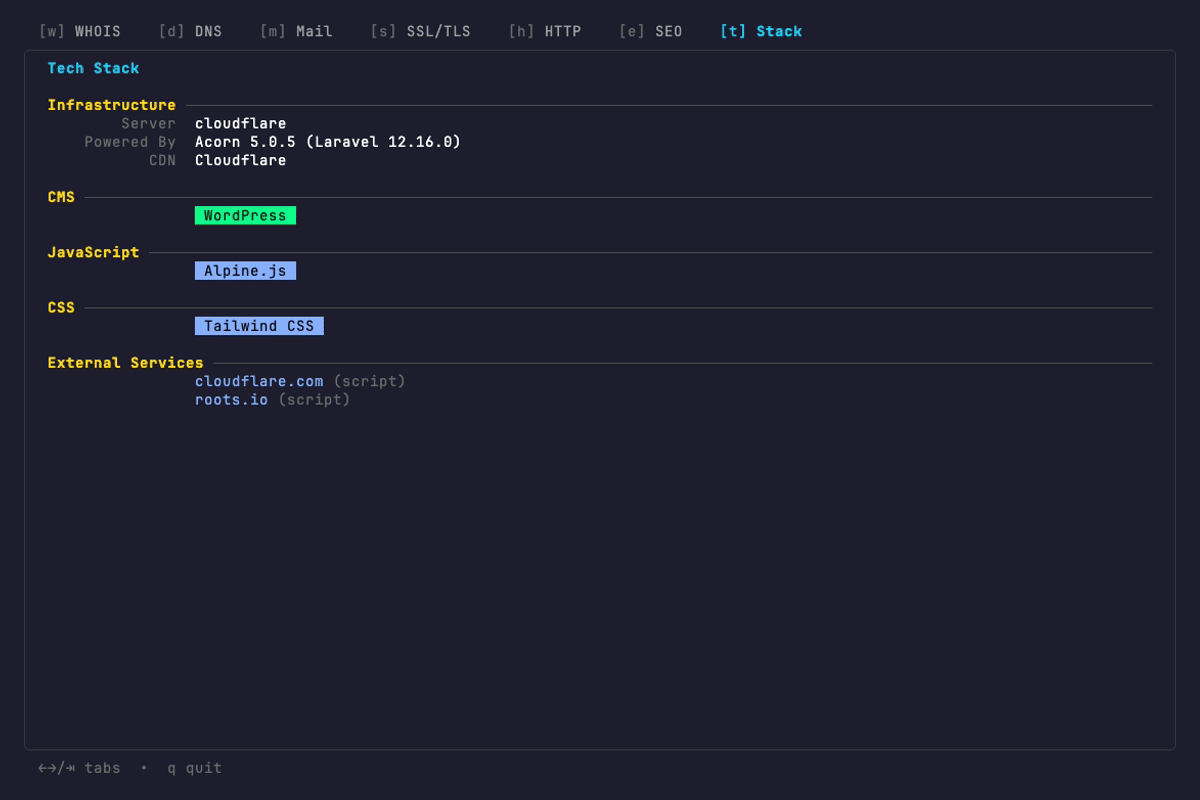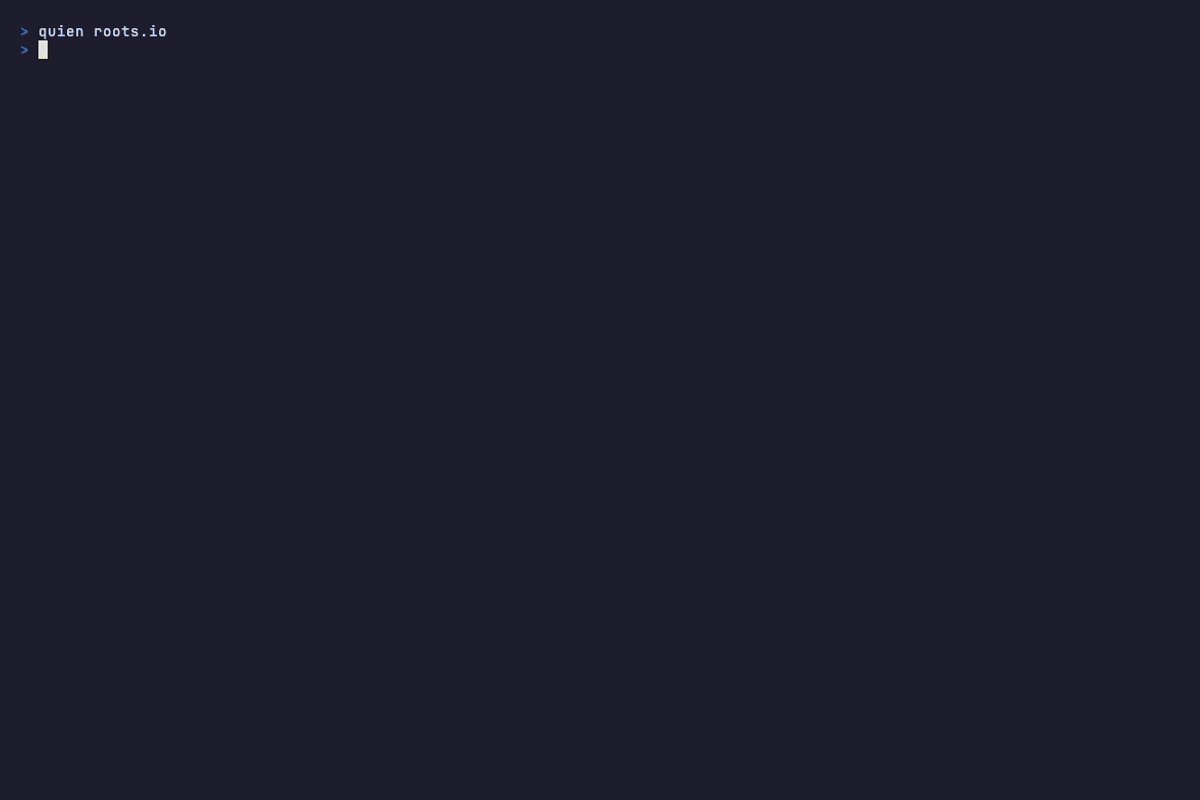 retlehs/quien
A better whois and domain intelligence toolkit
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
 romain-deperne/cve-2026-33715
Proof-of-concept exploit for unauthenticated SSRF and open email relay in Chamilo LMS via install.ajax.php, allowing internal network probing and…
 blue-chocolates/cve-2016-10033
Exploit for CVE-2016-10033, a remote code execution vulnerability in PHPMailer, enabling unauthenticated attackers to execute arbitrary code via…
 shinthink/cve-2026-54390
CVE-2026-54390 — JTL Shop Smarty SSTI RCE | Pre-Auth Template Injection via fetch('string:' . ) | 5.2.0-5.7.1
 wh4l3x/cve-2026-xxxx-atlassian-email-enumeration
CVE-2026-XXXX: Atlassian GraphQL Email Enumeration Oracle (CWE-204, CVSS 5.3 MEDIUM)
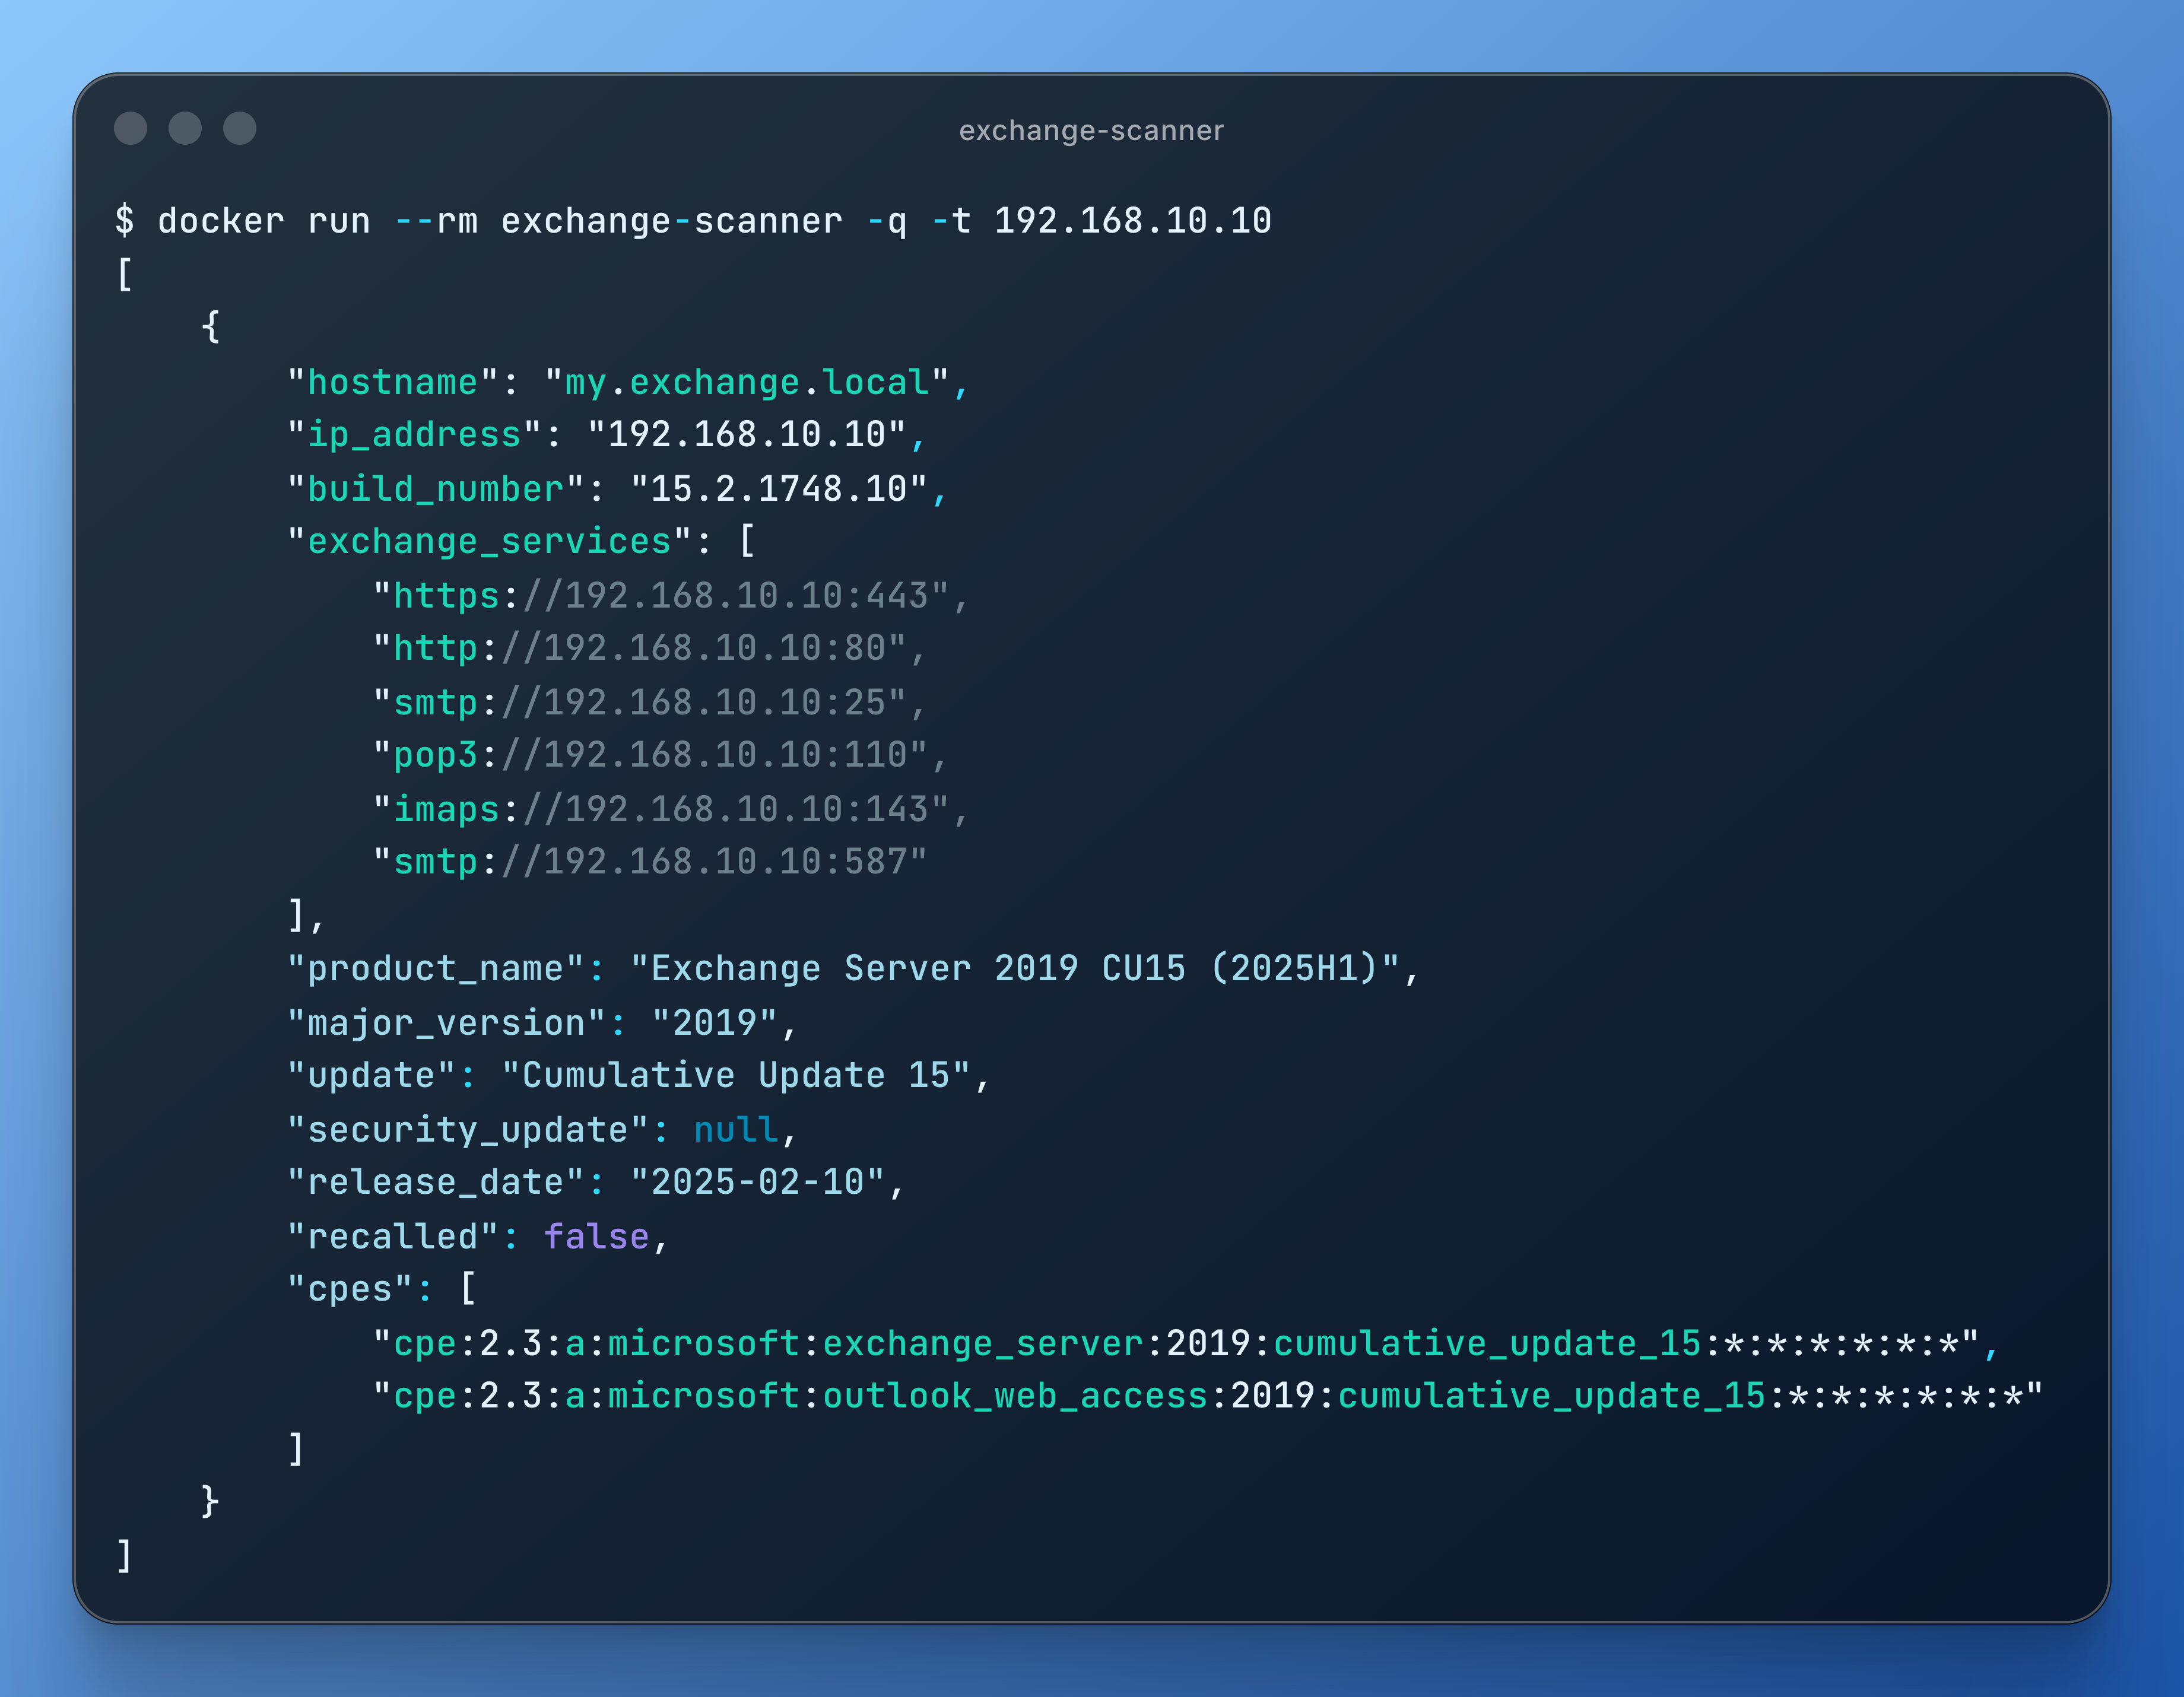 bishopfox/exchange-scanner
Identify public-facing Microsoft Exchange servers and determine their software versions
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 te-k/harpoon
CLI tool for open source and threat intelligence
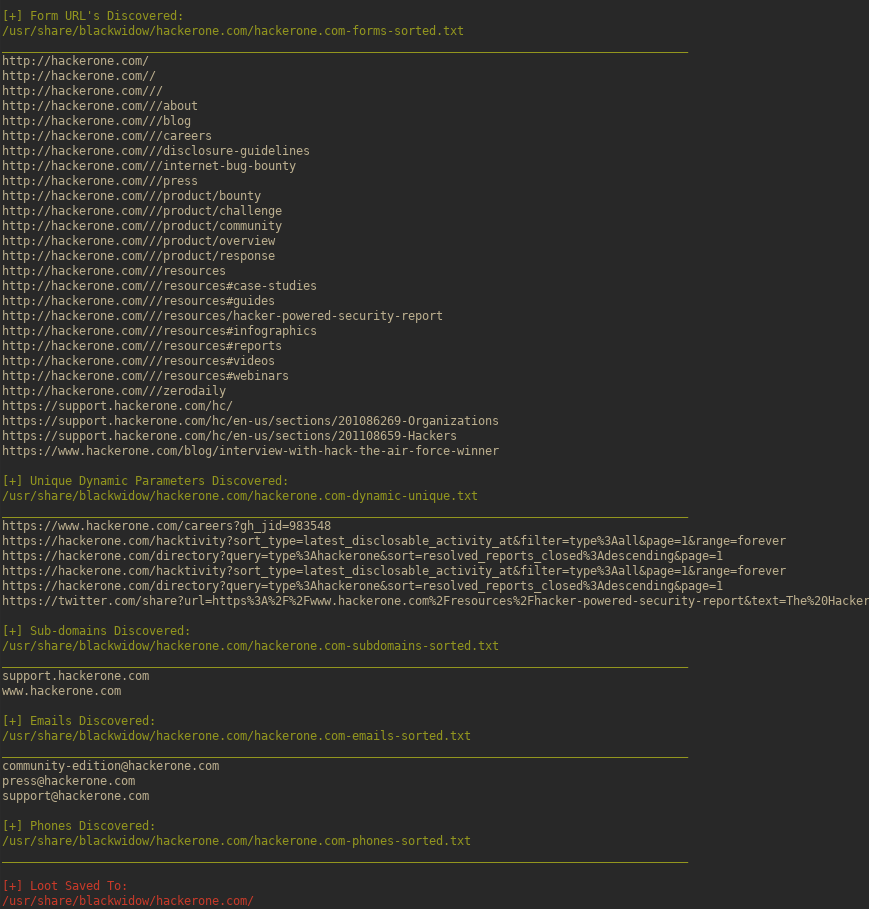 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
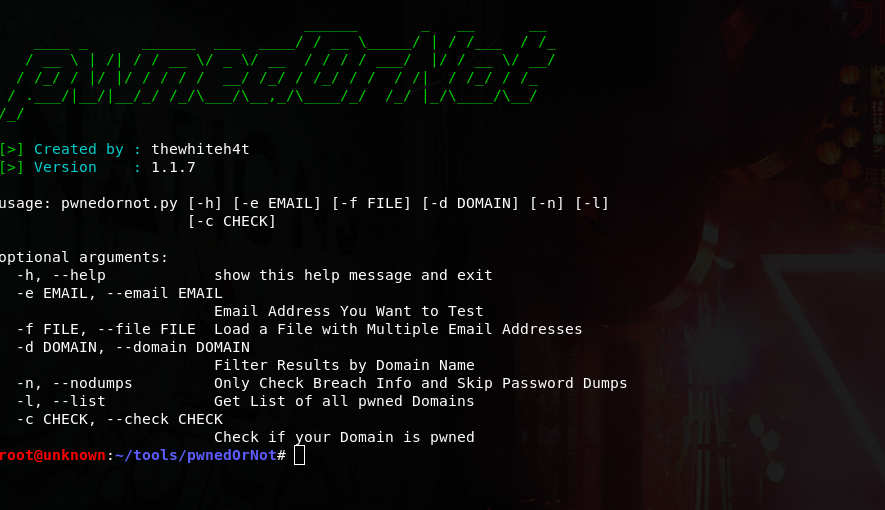 thewhiteh4t/pwnedornot
OSINT Tool for Finding Passwords of Compromised Email Addresses
 edu0x01/sr-71
An easy-to-use Python tool for performing subdomain enumeration, endpoint recognition, and more
 thewoodenbench/cve-2025-66956
Insecure Access Control in Contact Plan, E-Mail, SMS and Fax components in Asseco SEE Live 2.0 allows remote attackers to access and execute…
 redpack-kr/blackash-cve-2025-20393
CVE-2025-20393
 thewoodenbench/cve-2025-66955
Local File Inclusion in Contact Plan, E-Mail, SMS and Fax components in Asseco SEE Live 2.0 allows remote authenticated users to access files on the…
 7h30th3r0n3/cve-2025-51586-prestashop-poc
PrestaShop AdminLogin Email Enumeration PoC - CVE-2025-51586. This repository provides an ethical Proof-of-Concept (PoC) for the PrestaShop…