

systeminformer
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
15.6k
winsiderss/systeminformerReal-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
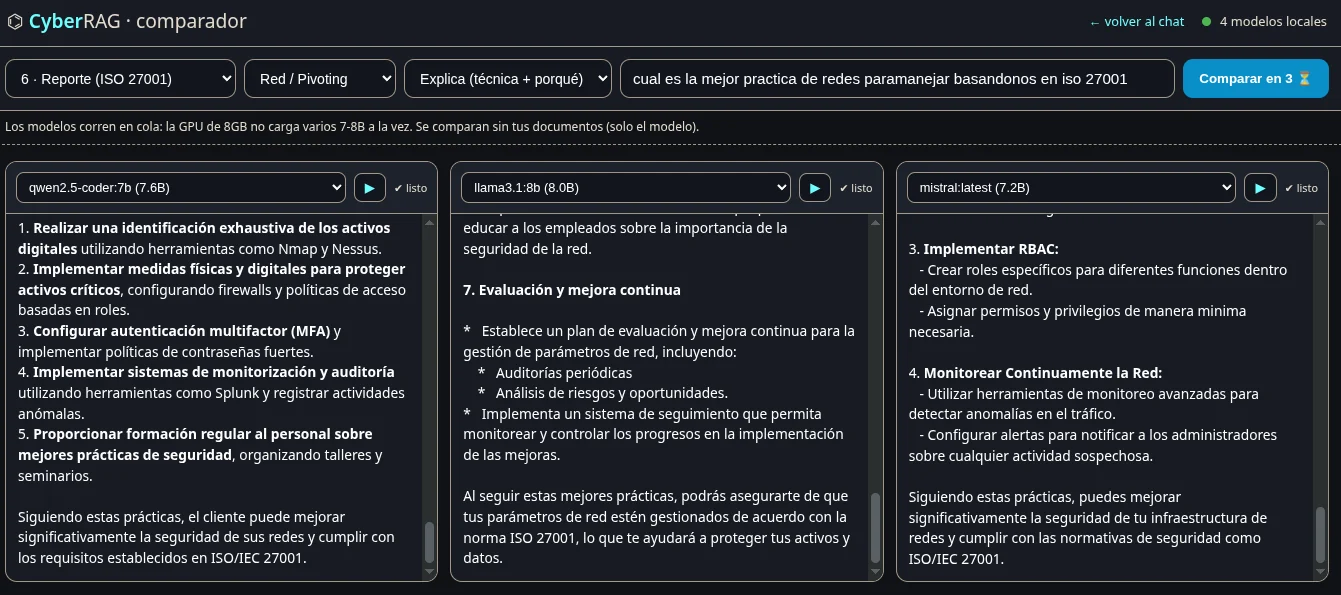
 rdelasierra-uy/rag-seguridad
CyberRAG — RAG 100% local (Ollama) sobre apuntes y libros de ciberseguridad: recuperación híbrida, respuestas con citas, asistente de pentest por…
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 glen-testing/low-int-cert-monitor
Monitor Certificate Transparency logs for certificates with trivially small EC private keys (the eMudhra weak-key class). P-256/384/521.
 thalesgroup-cert/watcher
AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…
 asvorg/cve-2026-105030-poc
A python3 PoC for CVE-2026-105030 Kener 4.0.0 before 4.1.6 Hidden Monitor Data Disclosure via Dashboard API
 bardlaudian/cve-2018-9276
CVE-2018-9276 — PRTG Network Monitor < 18.2.39 Authenticated RCE. For educational purposes and authorized penetration testing only.
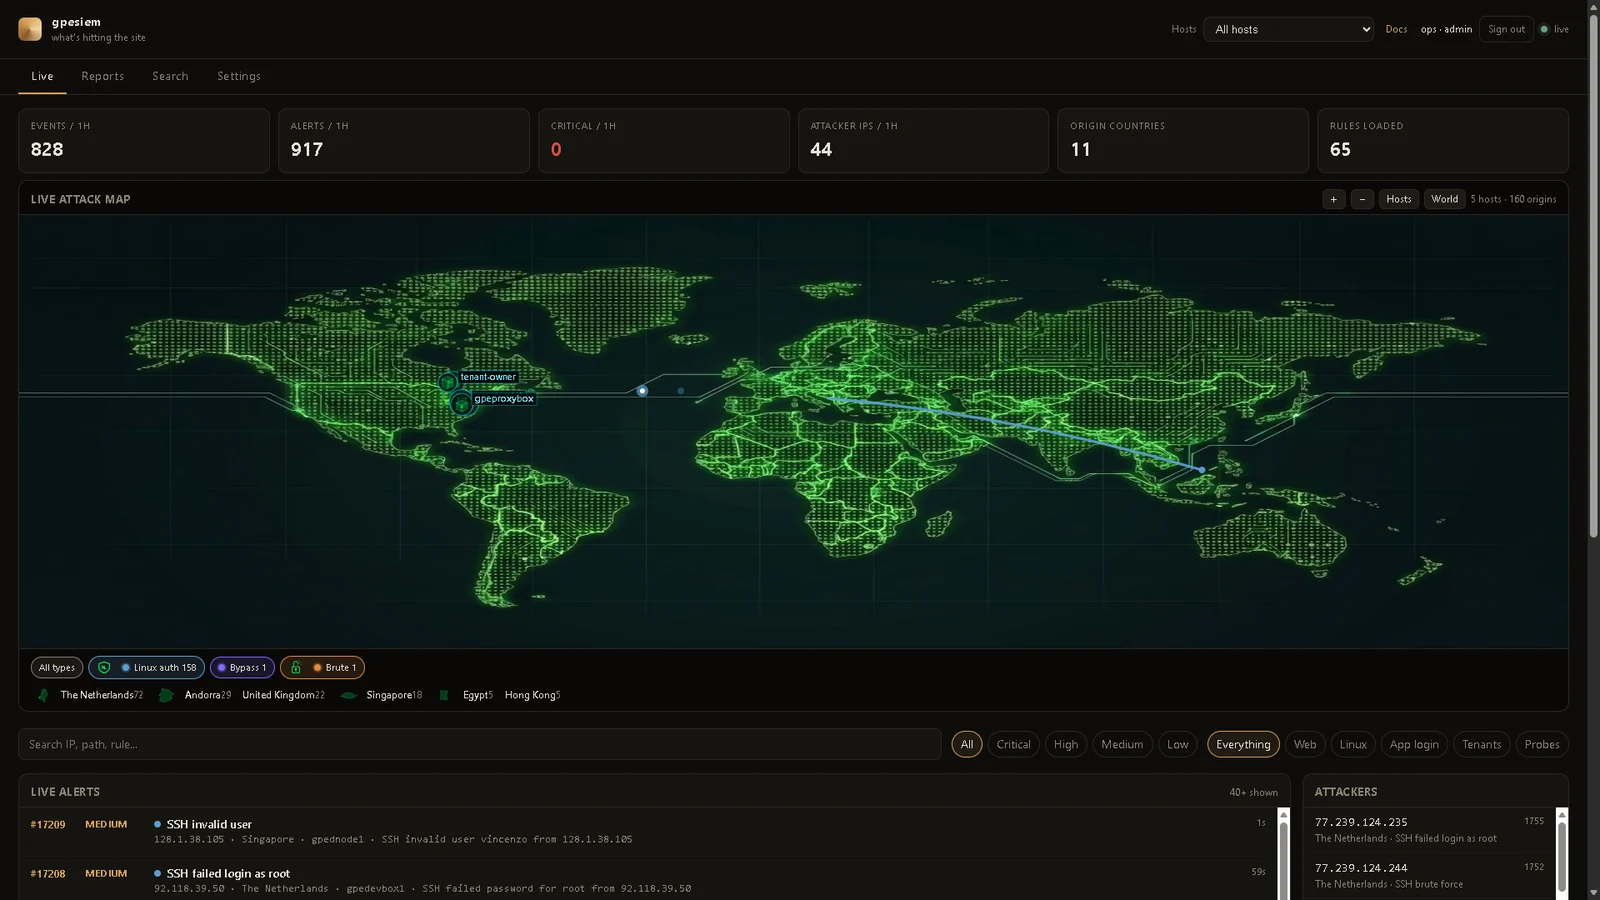 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 cves-labs/cve-2026-21877
Dockerized vulnerable lab environment with a Python-based network monitor and dedicated exploit script, enabling hands-on exploitation, privilege…
 idoka/awesome-canbus
:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…
 khalilu020/offensive-security-adversary-emulation
Simulated a real-world attack (CVE-2011-2523) against a vulnerable host, then cross-checked detection coverage against an existing…
 mr-r3b00t/cve-2026-0300
Deceptive honeypot designed to simulate and monitor exploitation attempts targeting CVE-2026-0300, capturing attacker behavior for analysis and…
 rippsec/cve-2025-27591-meta-below-lpe
CVE-2025-27591 – Meta below symlink following local privilege escalation (HackTheBox CTF)
 d7ead/cve-2025-61156
Insecure access control in ThreatFire System Monitor's TfSysMon.sys driver allows unprivileged process termination with kernel privileges, enabling…
 fxrstor/throttlestoppoc
CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
 jcarabantes/cve-2024-54820
Proof-of-concept for an unauthenticated SQL injection vulnerability in XOne Web Monitor that allows credential dumping and data extraction via…
 ma111e/melody
Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.
 griisemine/cve-2024-56331
Proof-of-concept exploit for CVE-2024-56331, demonstrating Local File Inclusion in Uptime Kuma via improper URL handling in the real-browser monitor.…