
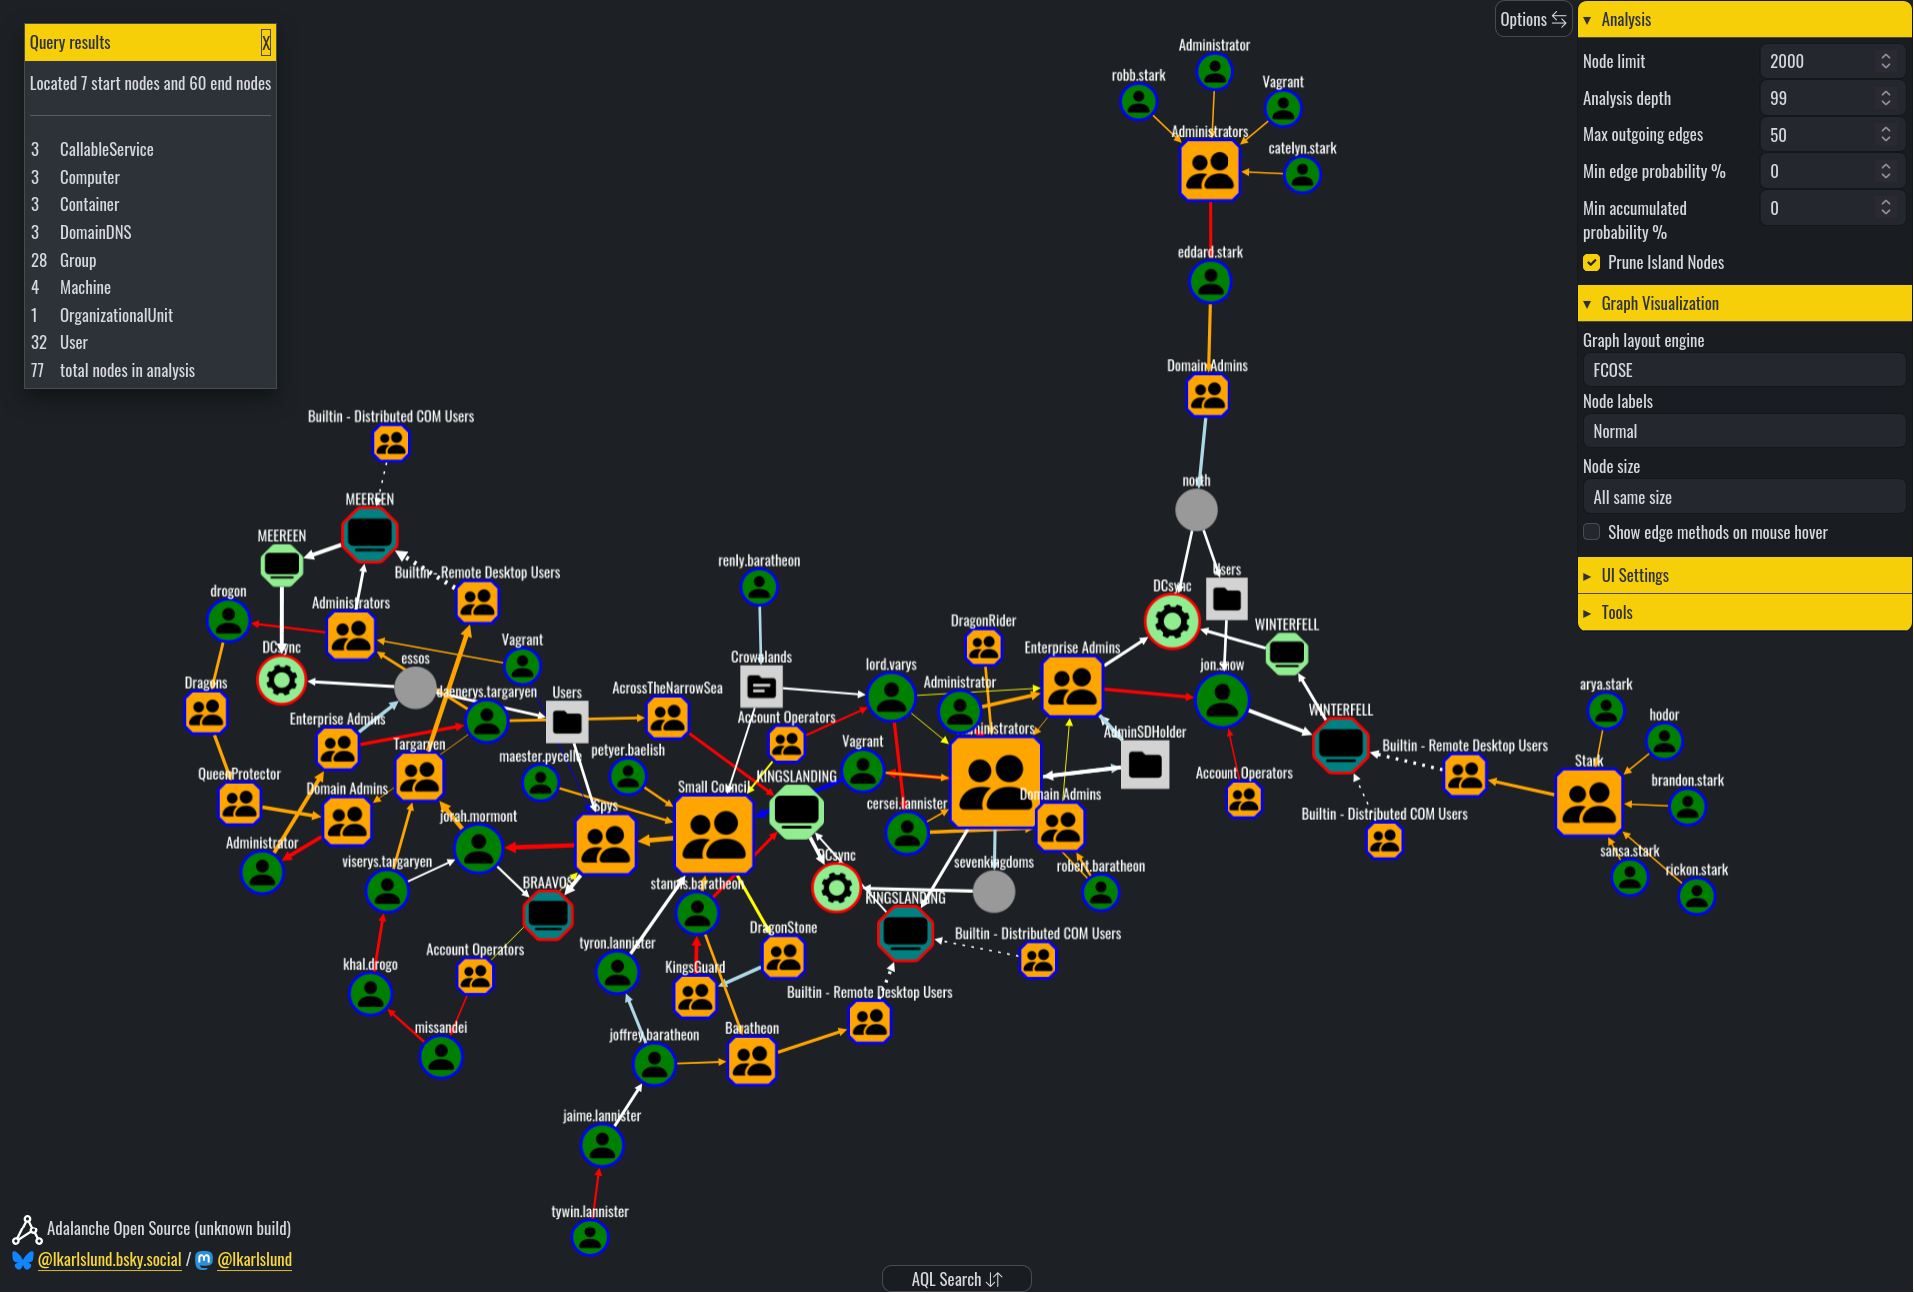
Adalanche
 lkarlslund/adalanche
Attack Graph Visualizer and Explorer (Active Directory) ...Who's *really* Domain Admin?
penetration-testingreconnaissancered-teaming+1
2.2k2 days ago
lkarlslund/adalancheAttack Graph Visualizer and Explorer (Active Directory) ...Who's *really* Domain Admin?
 murrez/cve-2026-89055
Python check/exploit PoC for CVE-2026-89055, an unauthenticated authorization bypass in Customer Reviews for WooCommerce that lets attackers link…
 candisexterior171/cve-2026-57827
Demonstrate the unauthenticated remote code execution vulnerability in the RSFiles! Joomla component through an arbitrary file upload.

 murrez/cve-2026-88854
Python 3 PoC scanner and exploit for CVE-2026-88854, an unauthenticated SQL injection in OrdaSoft Joomla Gallery, with mass check and EXTRACTVALUE…
 murrez/cve-2026-84434
Python PoC scanner and exploit for CVE-2026-84434, an unauthenticated arbitrary file upload in Gravity Forms <=3.1.0.4 via hidden File Upload fields.…
 fishjojo1/devin-cve48384-1789318364-1162143-parent
Authorized reachability probe for CVE-2025-48384, used to verify whether a target is exposed to the vulnerability in a controlled testing context.
 sebastianmautner/nuclei-cve-2025-24813
University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…
 l0lsec/openfire-ssrf-cve-2019-18394
PoC for CVE-2019-18394: unauthenticated full-read SSRF in Openfire <= 4.4.2 FaviconServlet
 romain-deperne/cve-2026-34160
Unauthenticated SSRF in the Chamilo LMS PENS plugin — CVE-2026-34160 / CVSS 8.6
 romain-deperne/cve-2026-33715
Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
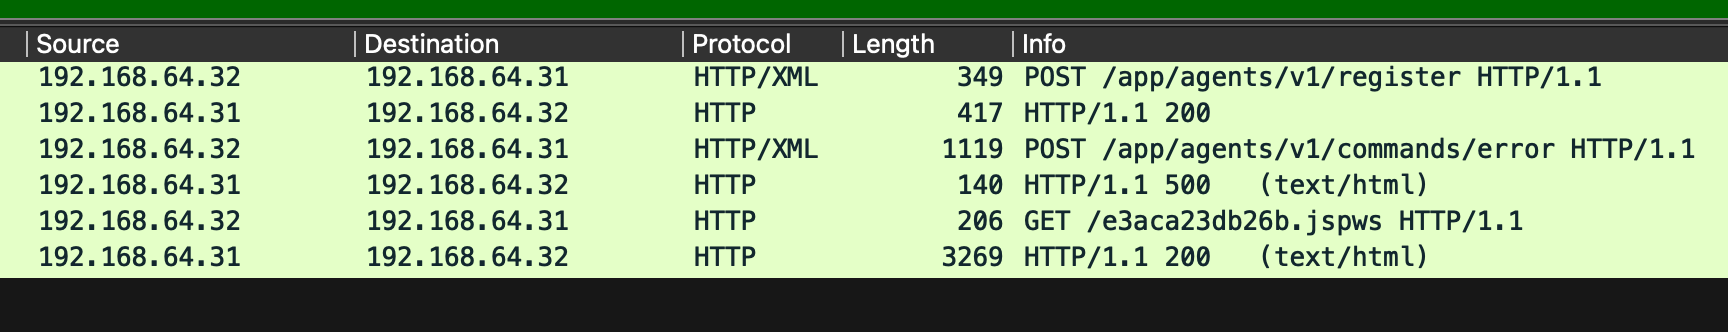 boredhackerblog/teamcity-cve-2026-63077-pcap
teamcity teamcity-CVE-2026-63077 exploitation pcap
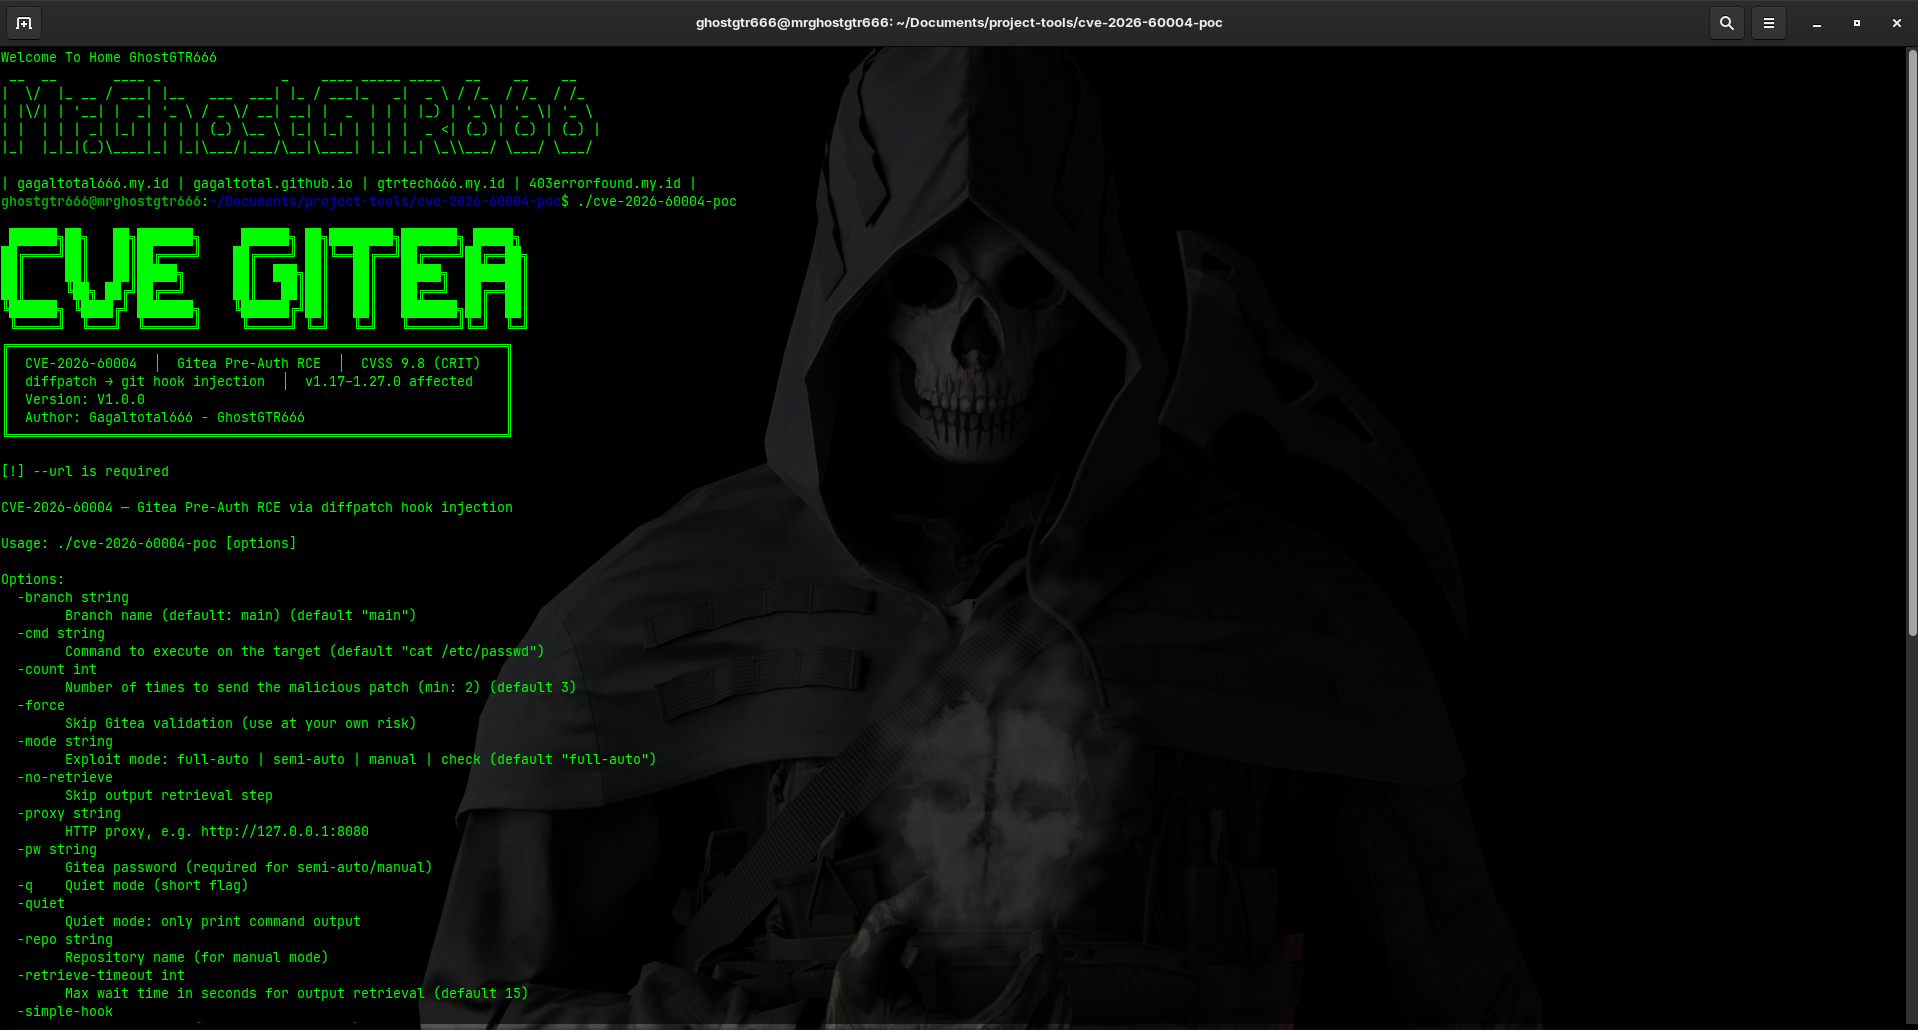 gagaltotal/cve-2026-60004-poc-gitea
CVE-2026-60004 — Gitea Pre-Auth RCE via diffpatch hook injection
 ridhinva/ghe-push-option-rce-scanner
Scanner: CVE-2026-3854 GitHub Enterprise Server Pre-auth RCE via Push Option Injection — Python checker (CISA KEV)
 johnlodan/wp2shell-rce
WordPress CVE-2026-63030 and CVE-2026-60137 security tool for detecting exposure to the WP2Shell pre-authentication RCE chain.
 shinthink/cve-2026-66066
CVE-2026-66066 — KindaRails2Shell: Rails Active Storage/libvips Arbitrary File Read → RCE. MATLAB/HDF5 dual-identity file → SECRET_KEY_BASE theft →…
 zephrfish/cve-2021-22986_check
CVE-2021-22986 Checker Script in Python3