
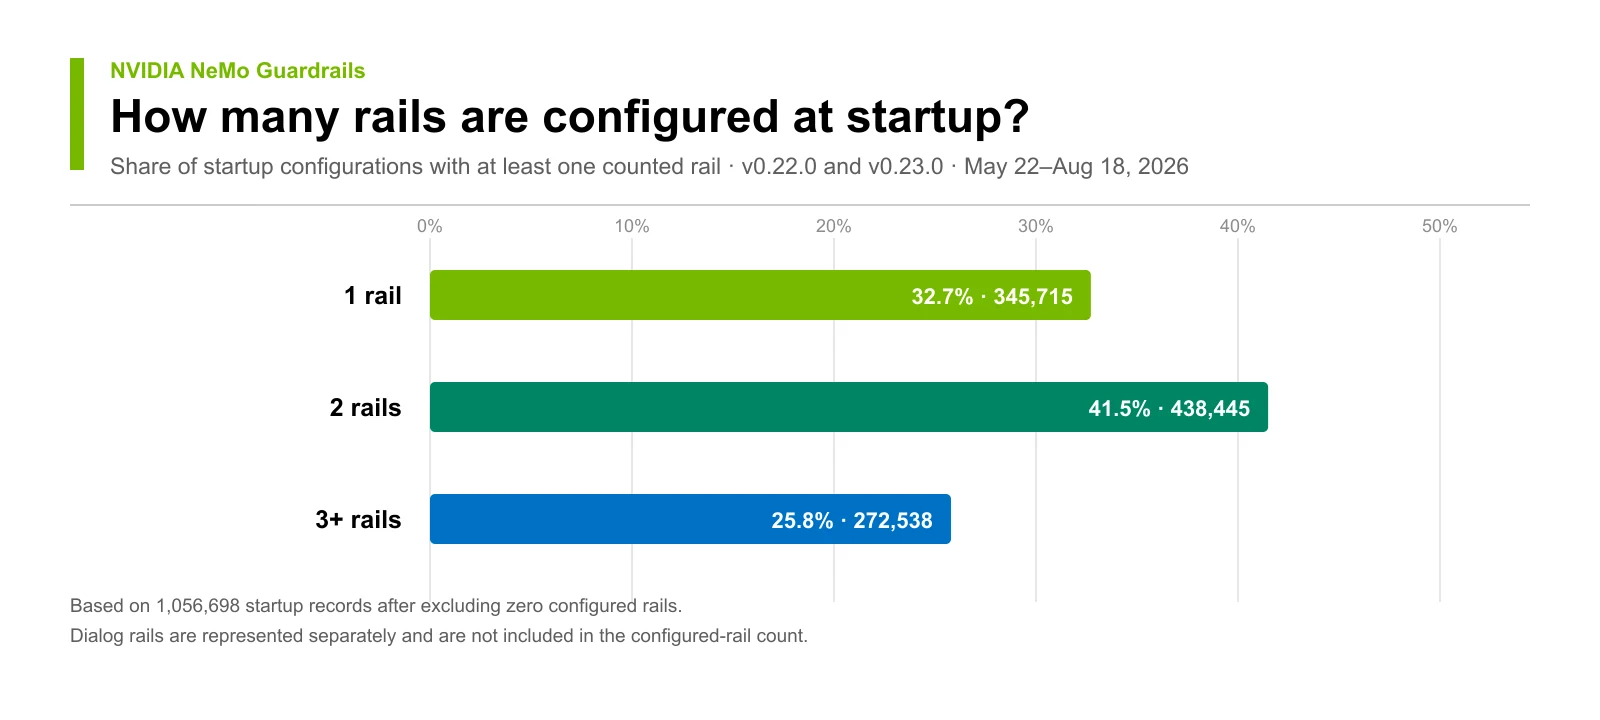
Guardrails
 nvidia-nemo/guardrails
Programmable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask…
ai-securityanomaly-detectiondefensive-tools+3
7.2k
nvidia-nemo/guardrailsProgrammable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask…
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 murrez/cve-2026-19658
Python 3 checker and exploit helper for CVE-2026-19658, a WordPress Give Tributes PHP object injection flaw, with FOFA target discovery and legacy…
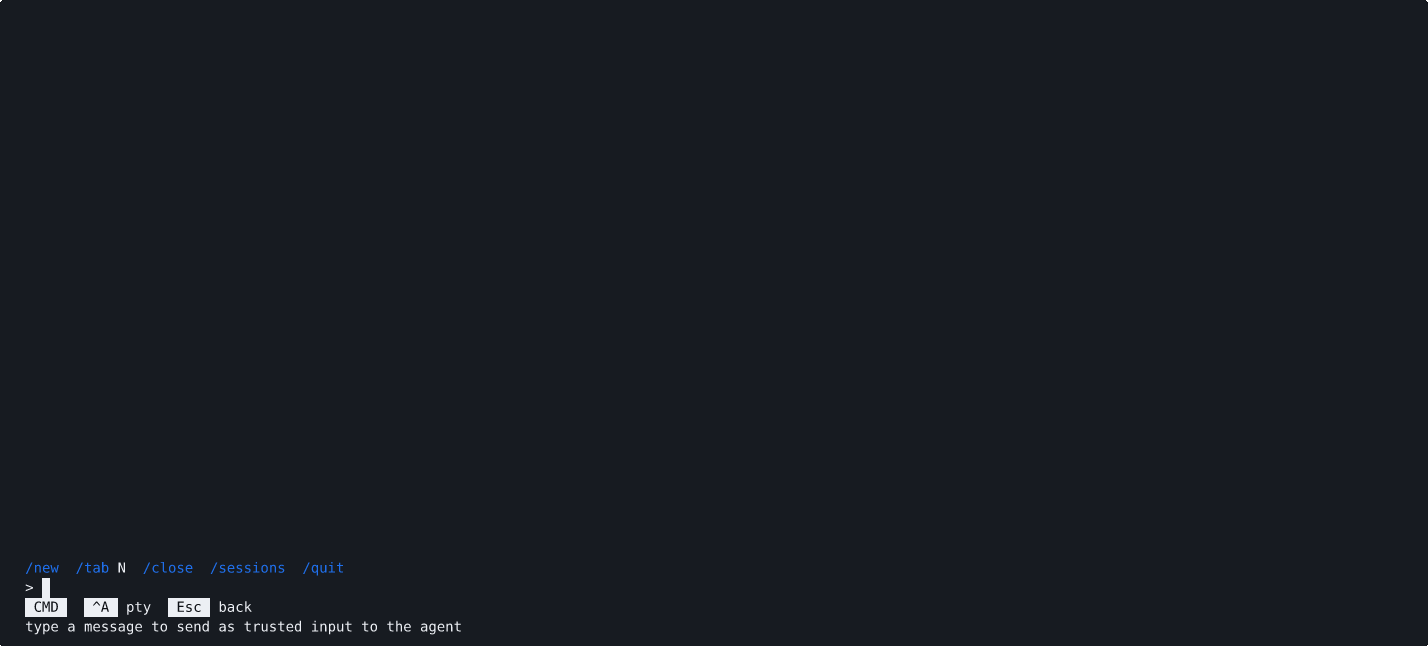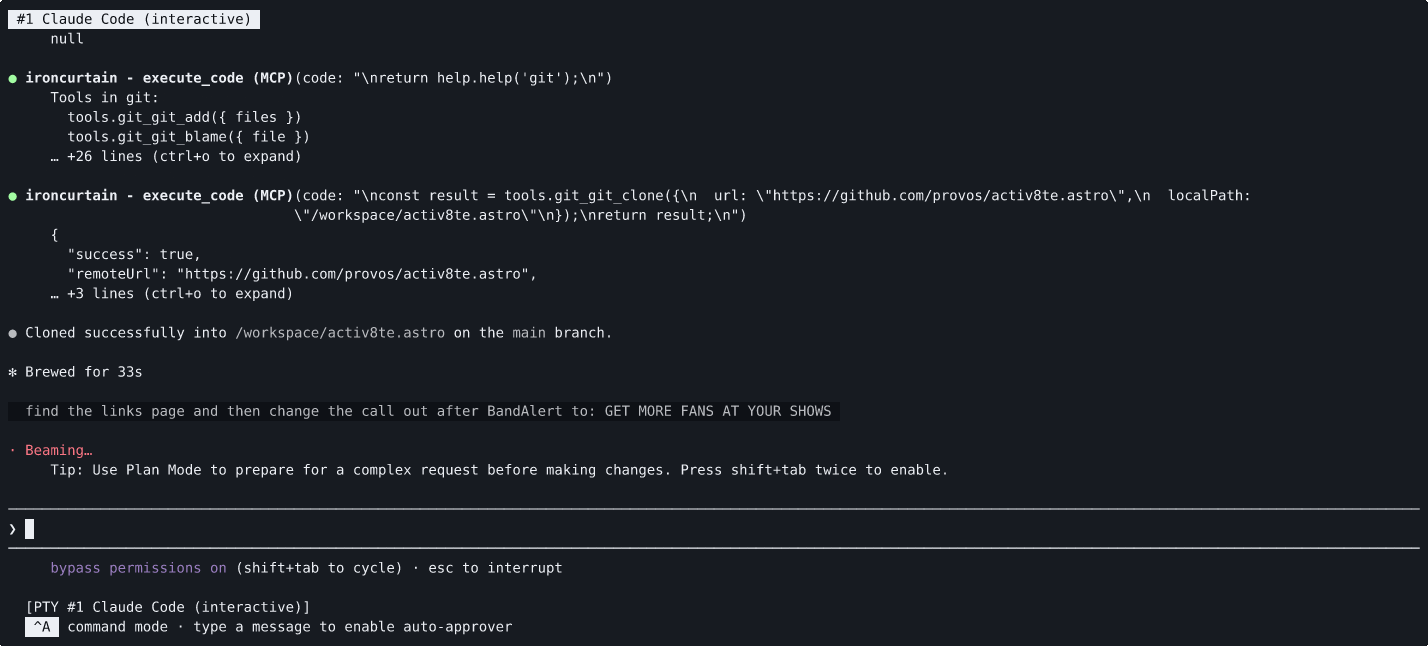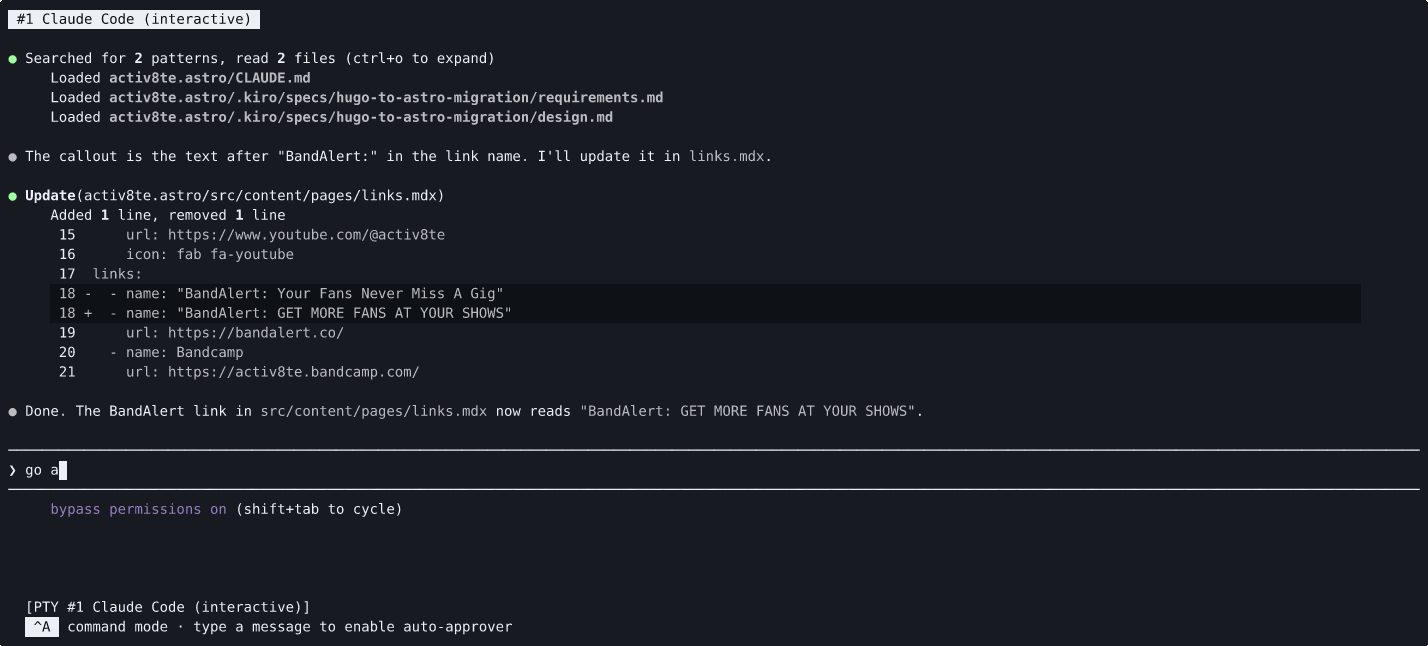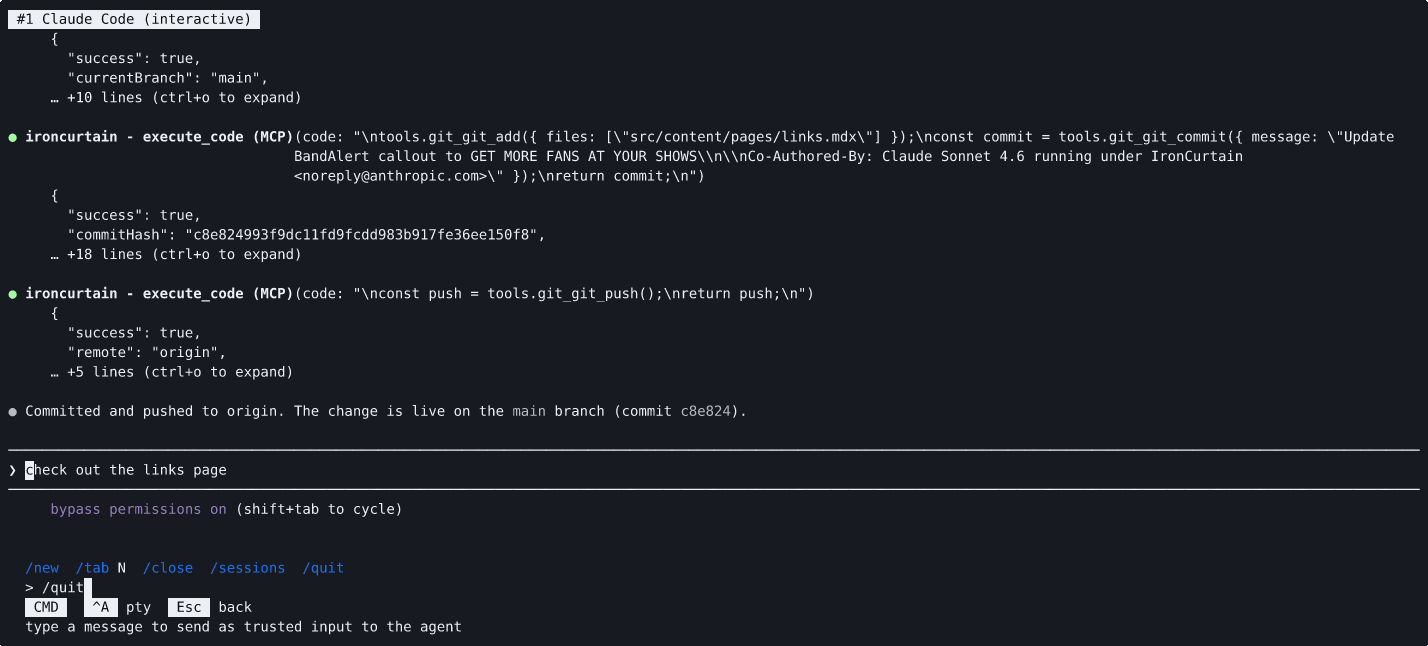 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)
 minh3102011/cve-2026-18963_analyst
Docker-based lab for reproducing Keycloak CVE-2026-18963, including vulnerable version setup, realm seeding, and source-level workflow analysis with…
 0xcyberstan/cve-2026-31694-poc
Linux kernel FUSE readdir cache out-of-bounds write (CVE-2026-31694): a malicious FUSE server overflows a page-cache page by 24 bytes. PoC plus an…
 brainbob/cve-2026-76578
Proof-of-concept exploit for CVE-2026-76578 and CVE-2026-76560, chaining anonymous LDAP ADD with a 389-ds SELFDN bypass to gain FreeIPA domain admin…
 tarpeg007/cve-2026-74586
Unprivileged proof-of-concept for CVE-2026-74586, a Linux kernel SCTP ASCONF use-after-free. Provides a raw-packet trigger, reliability metrics, and…
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
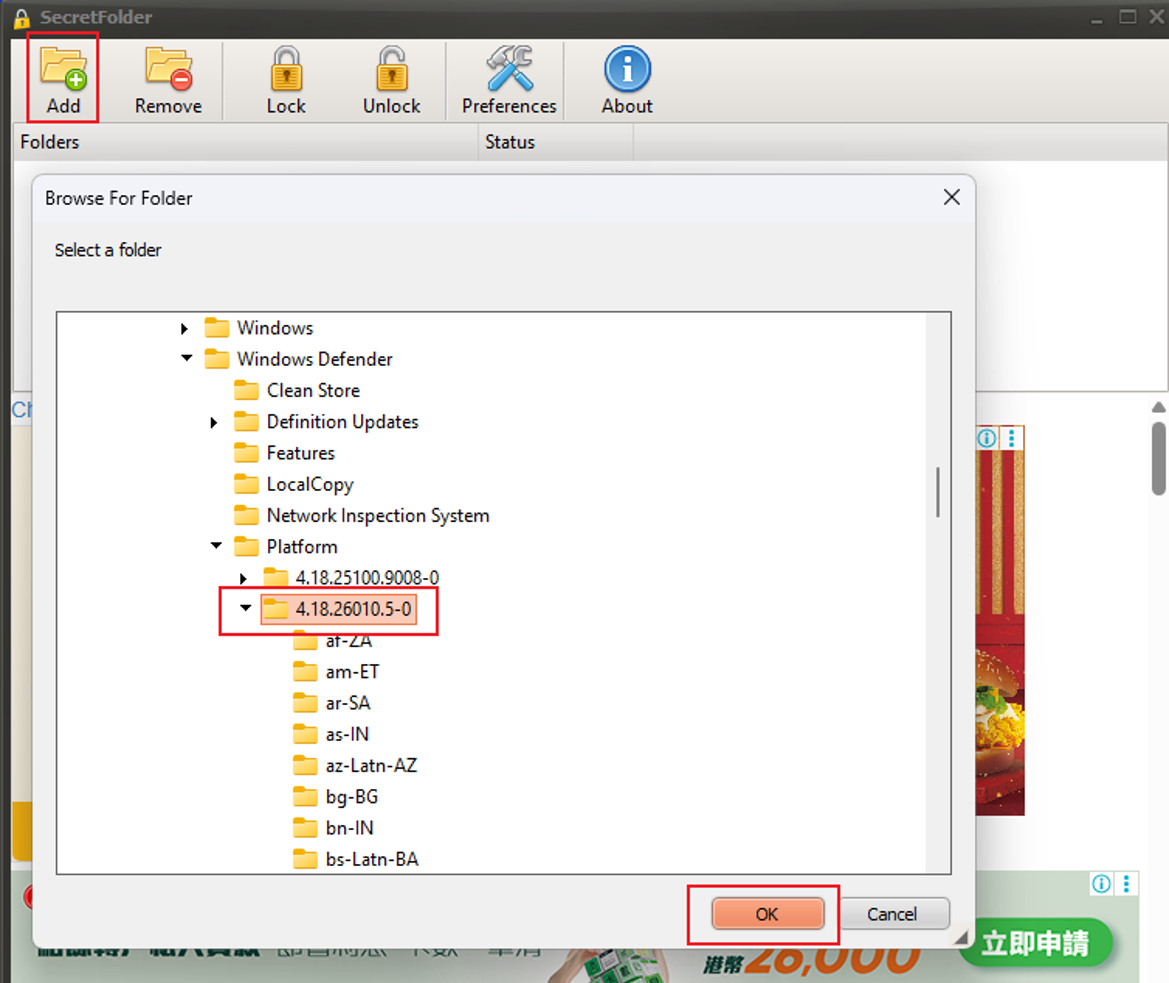 cwjchoi01/cve-2026-36130
Proof-of-concept demonstrating a vulnerability that disables Microsoft Defender (MsMpEng.exe) by locking a folder and rebooting, with screenshots…
 jmg0929/cve-2021-40346
PoC exploit for CVE-2021-40346: HAProxy integer overflow enabling HTTP request smuggling and ACL bypass. Includes analysis, reproduction steps, and…
 abdugafforov-bobur/cve-2026-54415-poc
PoC for CVE-2026-54415 — Azuriom CMS (<1.2.11) Broken Access Control → account takeover
 ctn-qvo/cve-2026-0073-android-adbd-bypass-poc_zh_cn
CVE-2026-0073-Android-ADBD-bypass-POC汉化版
 pinperepette/macpersistencechecker
macOS persistence mechanism scanner with code signature verification and timeline tracking.
 fredevsec/cve-2026-0073
0-Click RCE Android Adb TLS Wireless Debugging
 1neptune/fragnesia
Add go CVE-2026-46300 (Fragnesia) local privilege escalation exploit
 1neptune/dirtyfrag
Add go CVE-2026-43284 / CVE-2026-43500 (dirtyfrag) local privilege escalation exploit
 m00ddy/cve-2026-0073-android-client-tls-auth-bypass
translating original python exploit to C